
CVE-2026-49060-Lab
 rootdirective-sec/cve-2026-49060-lab
Docker-based lab for reproducing CVE-2026-49060, an unauthenticated privilege escalation in the Hippoo Mobile App for WooCommerce WordPress plugin.…
educationlabs-practicepenetration-testing+3
rootdirective-sec/cve-2026-49060-labDocker-based lab for reproducing CVE-2026-49060, an unauthenticated privilege escalation in the Hippoo Mobile App for WooCommerce WordPress plugin.…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 dedsecteam-blackhat/cve-2025-68860
Exploit script for CVE-2025-68860 targeting WordPress Mobile Builder plugin. Generates forged JWT tokens using a hardcoded secret to authenticate as…
 assetnote/jira-mobile-ssrf-exploit
Exploit code for Jira Mobile Rest Plugin SSRF (CVE-2022-26135)
 horkimhab/cve-2026-73570
Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…
 horkimhab/cve-2026-109618-619
Proof-of-concept code for CVE-2026-109618 and CVE-2026-109619 (php2shell bypass), packaged for authorized lab reproduction and vulnerability research.
 horkimhab/cve-2026-59265
Proof-of-concept and research material for CVE-2026-59265, a LibreOffice and OpenOffice vulnerability, intended for authorized lab testing and…
 horkimhab/cve-2026-wordpress
Educational CVE proof-of-concept collection targeting WordPress vulnerabilities, with setup scripts and lab guidance for authorized security research…
 horkimhab/cve-2026-13181-cve-2026-13182-cve-2026-13183-cve-2026-13184
Educational proof-of-concept for Telerik padding oracle vulnerabilities (CVE-2026-13181-184) with scripts for authorized security testing and…
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 horkimhab/cve-2026-19975
Proof-of-concept and research repository for CVE-2026-19975 in Azuriom, with setup instructions and a linked technical writeup for authorized…
 horkimhab/cve-2023-27350-cve-2023-27351
Educational proof-of-concept for PaperCut pre-auth RCE chain (CVE-2023-27350, CVE-2023-27351) with setup scripts and authorized testing guidance.
 d0gukank/cve-2019-1218
Proof-of-concept exploit for a cross-site scripting (XSS) vulnerability in Microsoft Outlook for iOS, enabling email-based spoofing attacks and…
 mozilla/firefox-devtools-mcp
Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi
 census/whatsapp-mitd-mitm
PoC and tools for exploiting CVE-2020-6516 (Chrome) and CVE-2021-24027 (WhatsApp)
 reverseclabs/cve-2021-25374_samsung-account-access
This script can be used to gain access to a victim's Samsung Account if they have a specific version of Samsung Members installed on their Samsung…
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
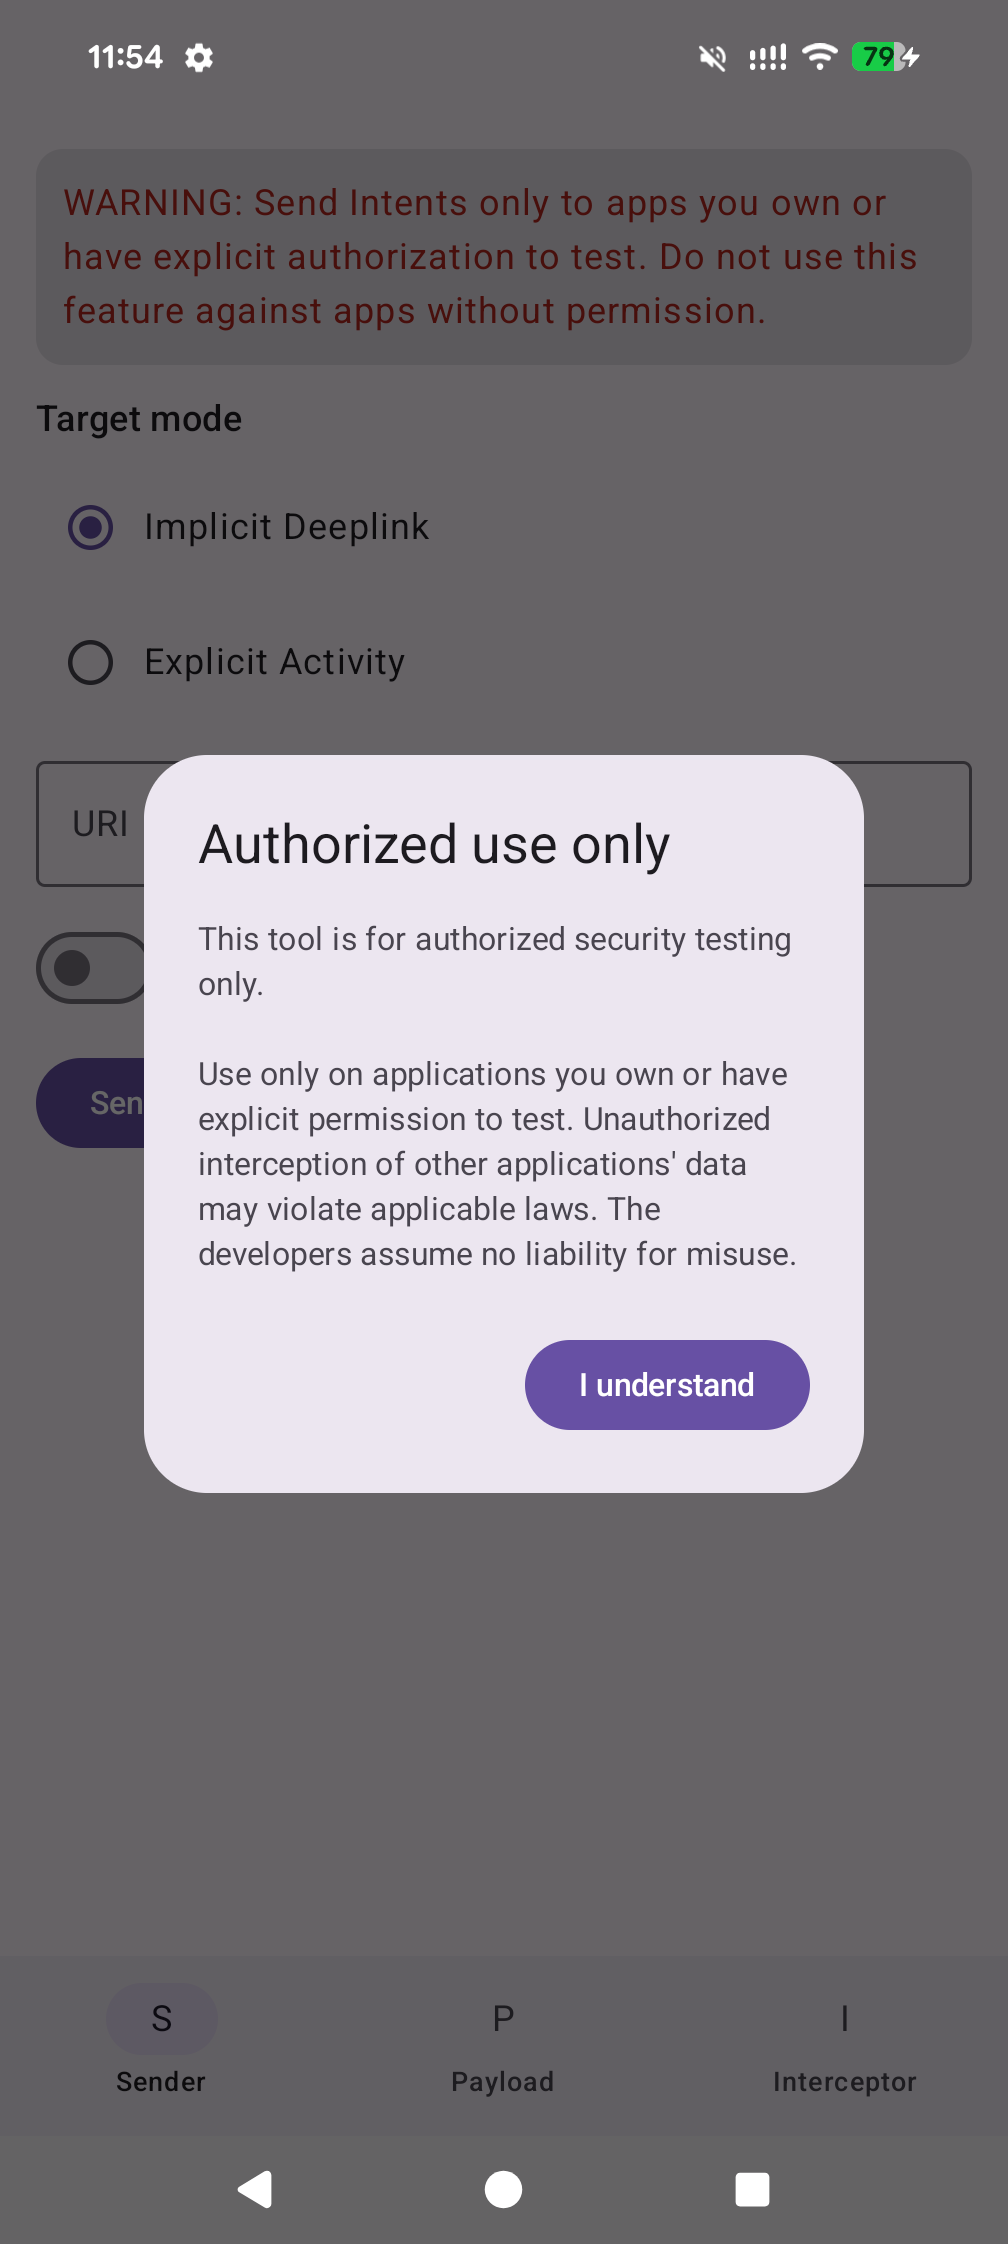 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking