
CVE-2026-67401
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
exploitationpayload-developmentpenetration-testing+2
2
axedos/cve-2026-67401Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 redshift-cybersecurity/cve-2024-41628
Python exploit script for CVE-2024-41628, a Local File Inclusion vulnerability in ClusterControl CMON API (ports 9500/9501). Retrieves arbitrary…
 shubtheone/cve-2021-36260-hikvision
Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…
 mbadanoiu/mal-008
Case Study: SSHtranger Things (CVE-2019-6111, CVE-2019-6110) in Cisco SD-WAN
 b374k/b374k
PHP Webshell with handy features
 mbadanoiu/cve-2025-31644
CVE-2025-31644: Command Injection in Appliance mode in F5 BIG-IP
 doyensec/malicious-devfile-registry
CVE-2024-0402 exploit for GitLab Workspaces using a malicious Devfile Registry with path-traversal archive to overwrite authorized_keys and gain SSH…
 gabrielha12/termix-research
CVE-2026-45746, CVE-2026-45750, CVE-2026-53547 — three critical vulnerabilities in Termix: cross-tenant session hijacking, OS command injection, and…
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
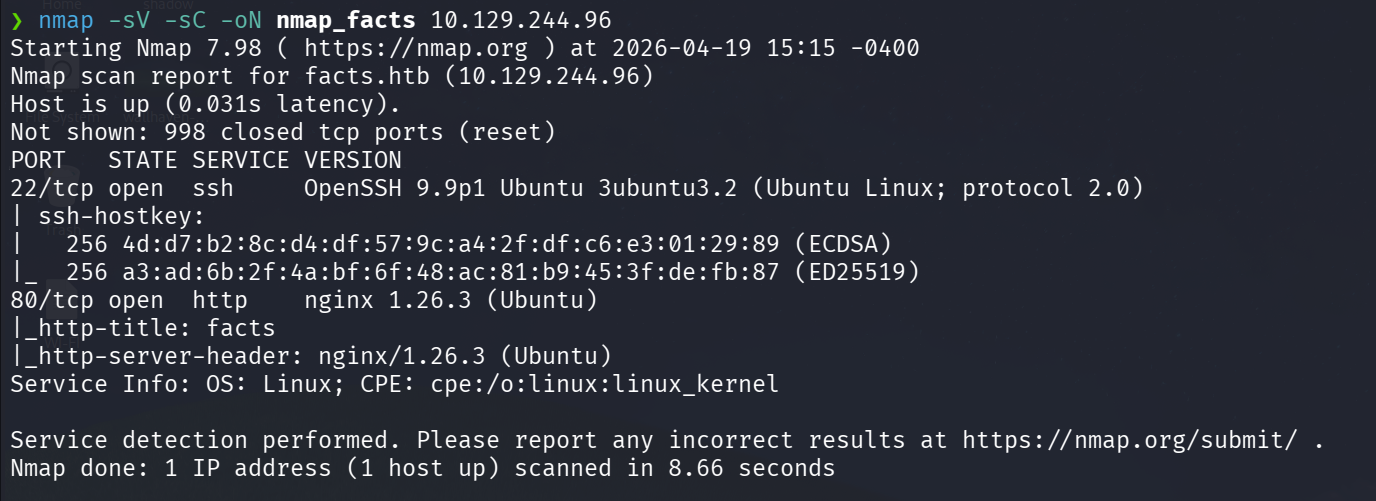 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 philippedixon/cve-2018-15473
Python-based exploit for CVE-2018-15473, enabling SSH user enumeration via OpenSSH username validation timing attack. Updated from Python 2 to 3 for…
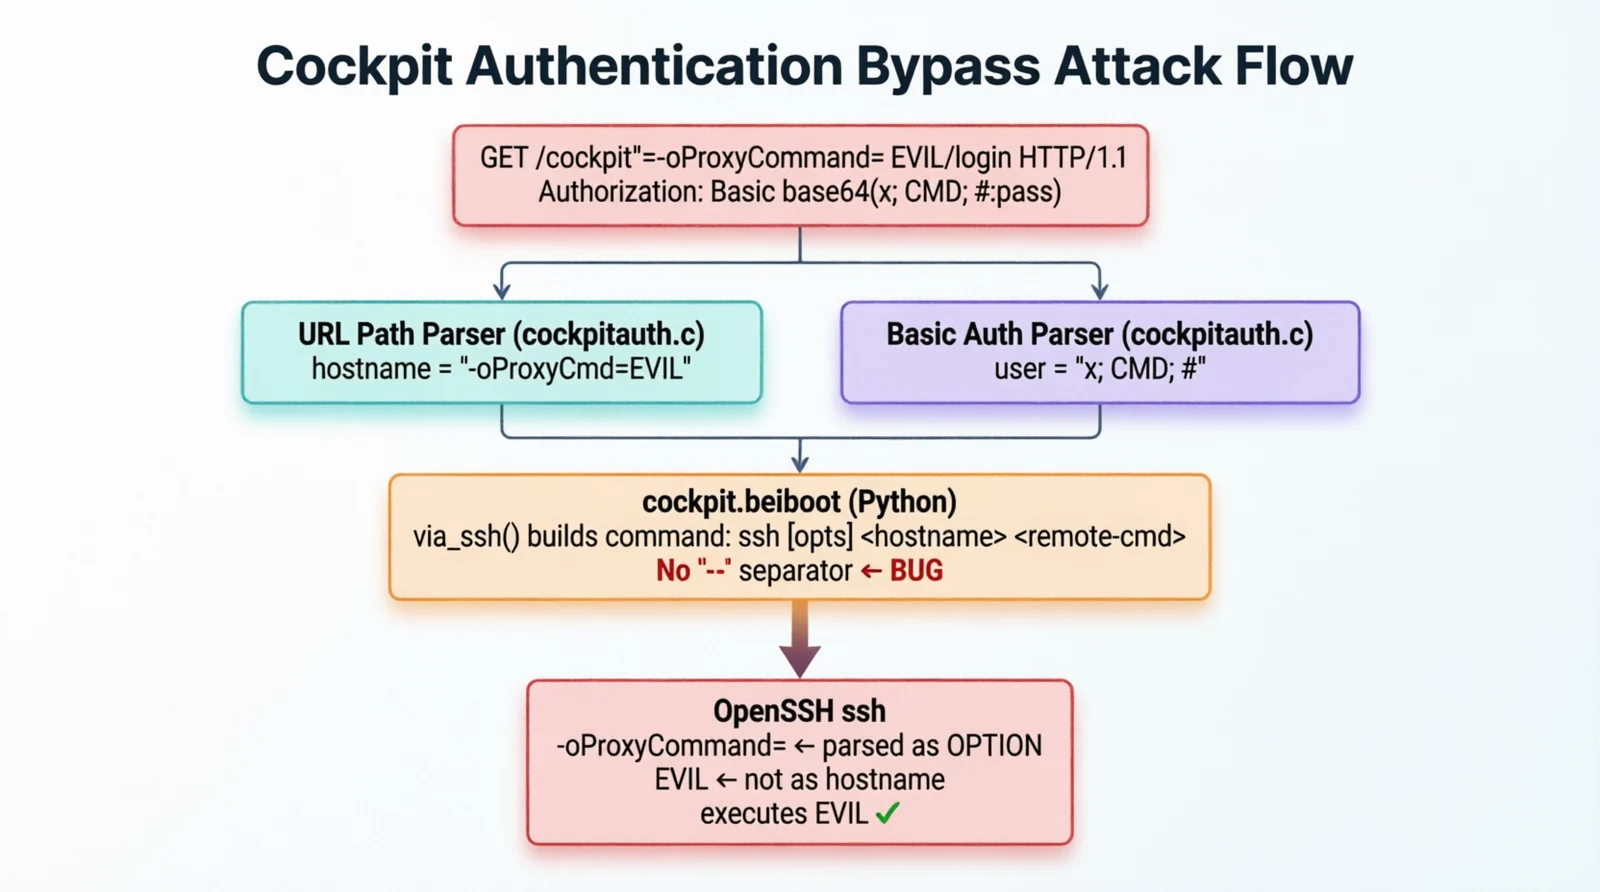 cyberheartmi9/cve-2026-4631-cockpit-rce
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
 qingsiweisan/cve-2022-40684
Python exploit for CVE-2022-40684 targeting FortiGate devices. Supports single and batch execution with custom SSH public key injection for…
 unix13/metasploitable2
PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 danilo-dellorco/cve-2026-6815
Authenticated path traversal and arbitrary file write PoC exploit for Casdoor <3.54.1, enabling RCE via SSH key injection, web shell upload, or…