
Archived
nginxpwner
 stark0de/nginxpwner
Nginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.
information-gatheringmisconfigurationpenetration-testing+3
1.6k
stark0de/nginxpwnerNginxpwner is a simple tool to look for common Nginx misconfigurations and vulnerabilities.
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 imancybersecurity/cve-2023-27350-poc
Proof-of-concept exploit for CVE-2023-27350 targeting authentication bypass in PaperCut MF/NG print management software. Includes Shodan dorks for…
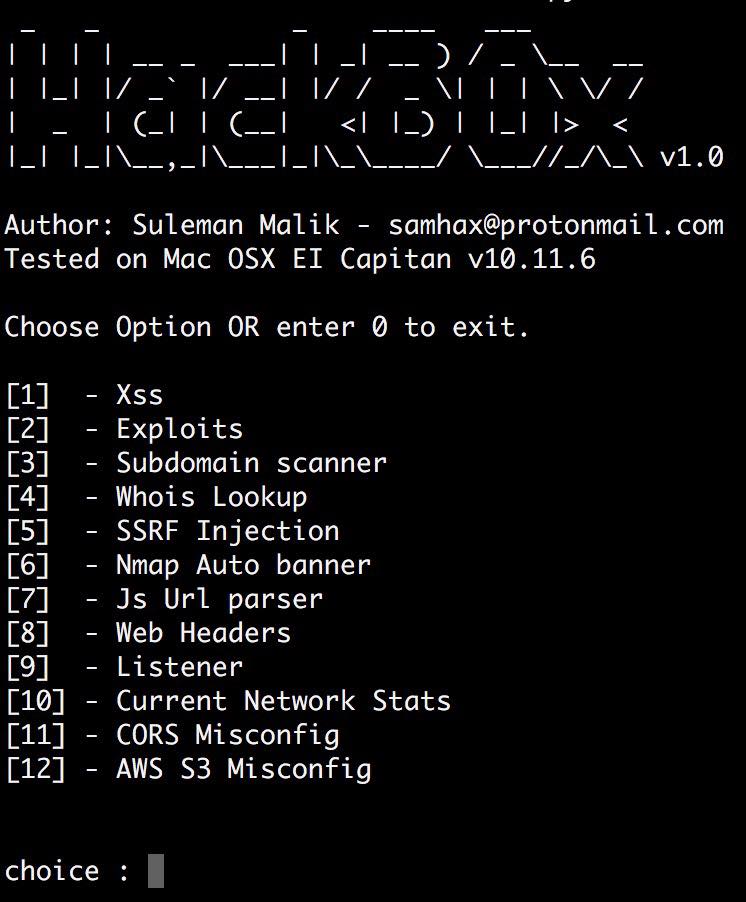 samhaxr/hackbox
HackBox is a powerful and comprehensive tool that combines a variety of techniques for web application and network security assessments, including…
 abrewer251/cve-2020-1938_ghostcat-poc
Apache Tomcat AJP Ghostcat (CVE-2020-1938) exploit tool for file disclosure with multi-target scanning, custom wordlists, and upload point detection…
 benso-io/posta
Browser extension for tracking, inspecting, and exploiting cross-document postMessage vulnerabilities with replay and cross-origin exploit simulation…
 nyakki-labs-0x420/myesve
CVE-2024-38475 exploitation & scanning tool with Mullvad VPN rotation
 mr-kasim-mehar/cve-2024-24919-exploit
Java-based scanner that checks IP addresses for CVE-2024-24919 vulnerability, with interactive options to print response data and change target file…
 xiw1ll/cve-2024-22198_checker
Identify Nginx-ui version and check if it's vulnerable to CVE-2024-22198
 xn2/glpwn
GLPI automatic exploitation tool for CVE-2020-15175
 zer0yu/cve-2021-41277
Go-based exploit tool for CVE-2021-41277, a Metabase sensitive information disclosure vulnerability enabling local file inclusion and environment…
 cybertechajju/cve-2026-23869-exploit
Automated exploit tool for CVE-2026-23869, a remote DoS in React Server Components. Includes PoC, Nuclei template, and scanning scripts for detection…
 gibran-abdillah/cve-2023-32315
Automated exploit tool for CVE-2023-32315 authentication bypass vulnerability. Scans single or bulk targets with multiprocessing and automatic login…
 cerberusmrxi/fortiweb-cve-2025-64446-rce-exploit
Security research tool for FortiWeb CVE-2025-64446 vulnerability. Automated exploitation framework with advanced logging, real-time metrics, proxy…
 sxyrxyy/aiohttp-exploit-cve-2024-23334-certstream
Automated exploit tool for CVE-2024-23334 that collects domains from certstream, checks for vulnerable Python aiohttp servers, and sends successful…
 hxlxmj/mass-exploit-cve-2022-29464
Mass exploitation tool for CVE-2022-29464 targeting WSO2 Carbon Server. Automates pre-auth RCE scanning via Shodan/ZoomEye, uploads webshells and…
 charlesjson/cve-2023-20198
Python-based exploit tool for CVE-2023-20198 targeting Cisco IOS XE routers. Provides automated exploitation and post-exploitation capabilities for…
 amit-pathak009/cve-2022-29464-mass
Mass exploit tool for CVE-2022-29464, a pre-auth RCE in WSO2 Carbon Server, with single-target and batch scanning via file input and search dorks.