
Athanasius
 shyam999/athanasius
Framework for penetration testing. The software can identify everything from cross-site scripting to SQL injection. Developers can also use this…
password-attackspenetration-testingvulnerability-scanners+1
19
shyam999/athanasiusFramework for penetration testing. The software can identify everything from cross-site scripting to SQL injection. Developers can also use this…
 groppoxx/cve-2025-25198-poc
PoC for CVE-2025-25198: automated Host header poisoning test for Mailcow - HTTPS listener, automatic cookie/CSRF handling, captures first reset link.
 dinhbaouit/cve-2021-36394
Proof-of-concept exploit for CVE-2021-36394 in Moodle, enabling admin password takeover and remote code execution via custom PHP functions.
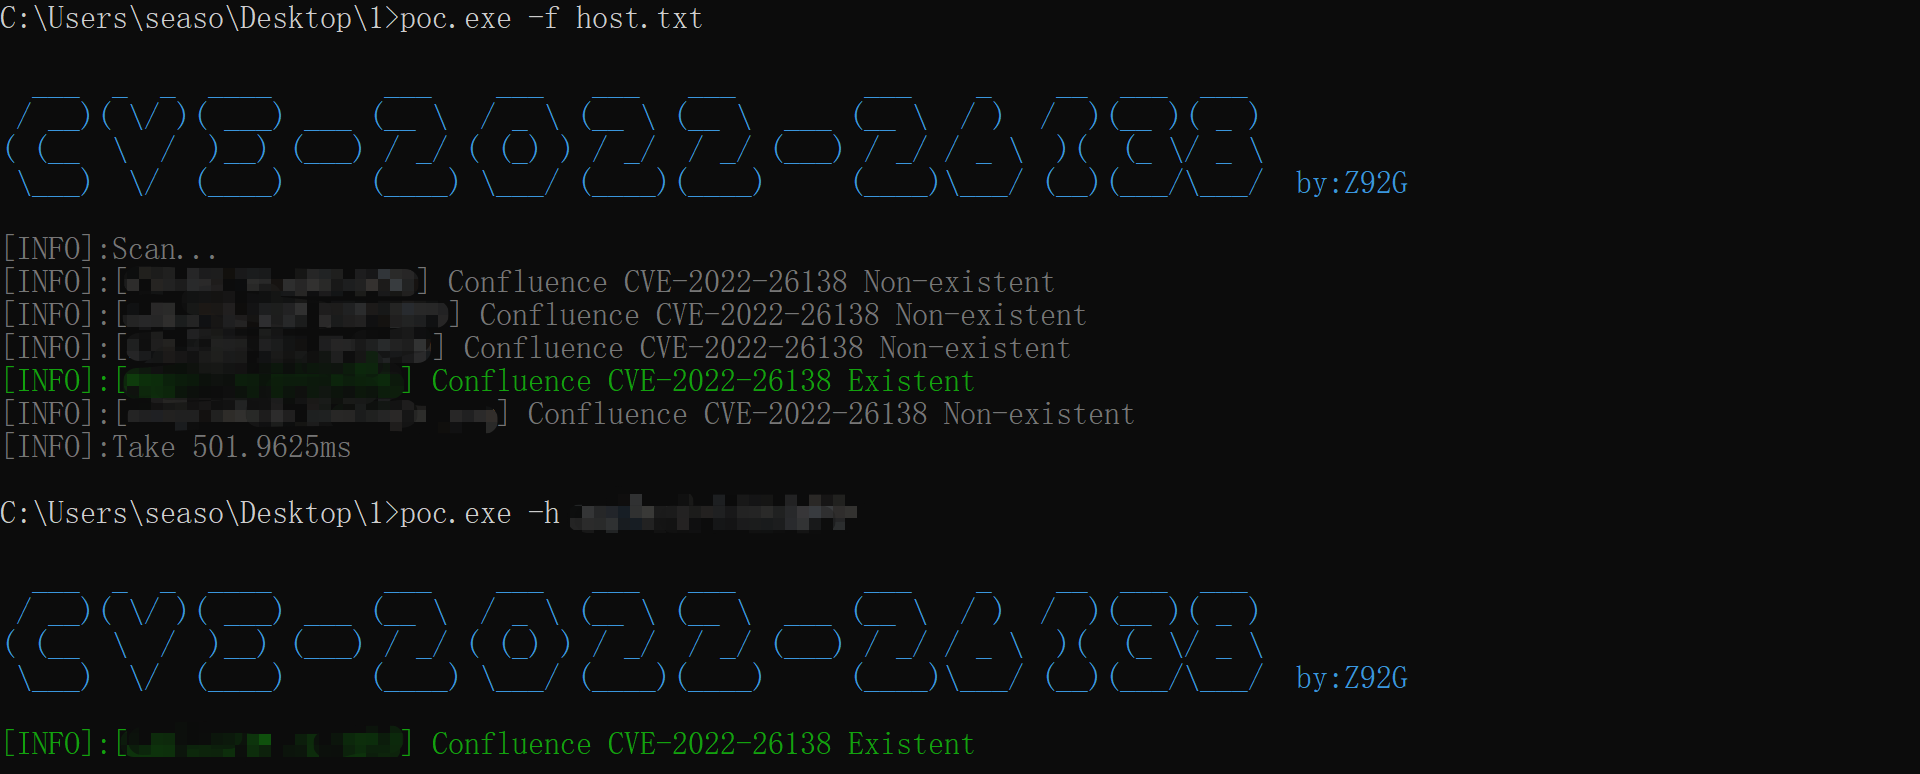 z92g/cve-2022-26138
Confluence Hardcoded Password POC
 e-renna/cve-2019-9053
CVE-2019-9053 Exploit for Python 3
 imthoe/cve-2019-14314
Python exploit for CVE-2019-14314: authenticated SQL injection in NextGEN Gallery 3.2.10 WordPress plugin, extracting password hashes from the…
 h4md153v63n/cve-2022-40032_simple-task-managing-system-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)
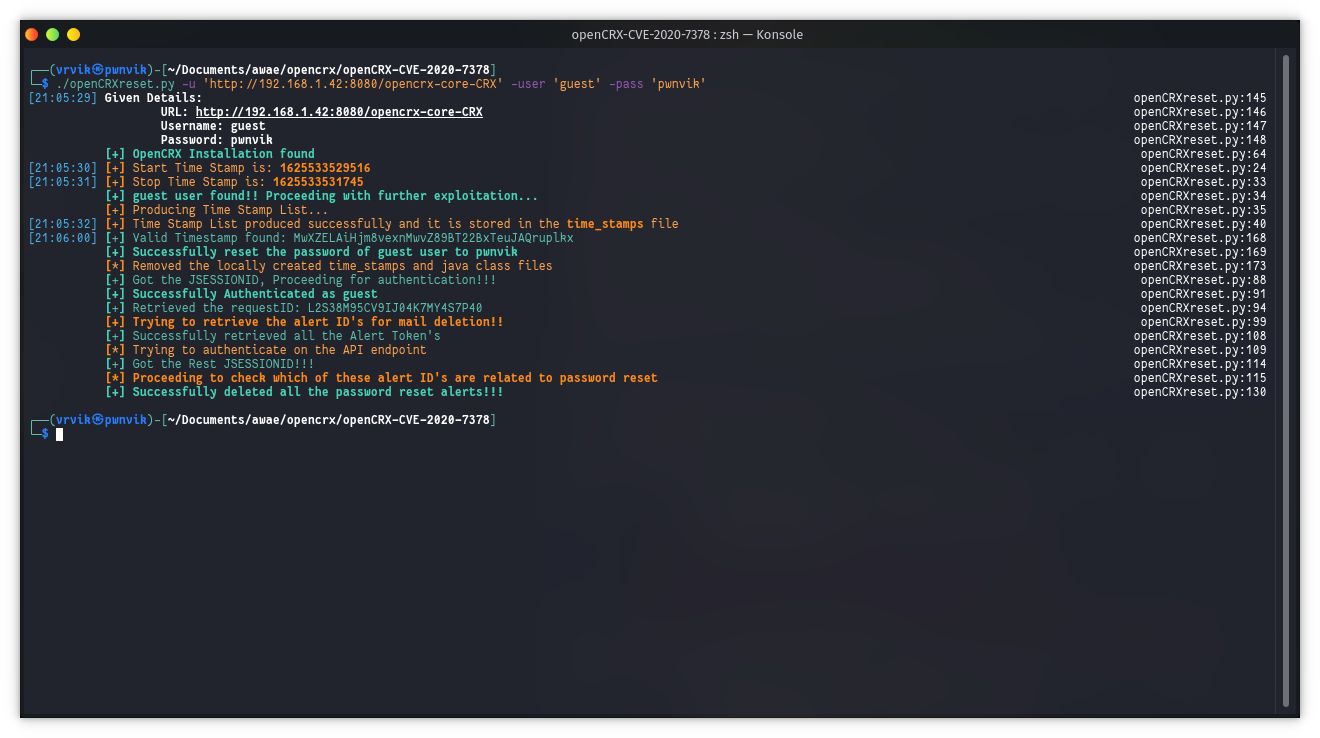 ruthvikvegunta/opencrx-cve-2020-7378
Exploits Password Reset Vulnerability in OpenCRX, CVE-2020-7378. Also maintains Stealth by deleting all the password reset mails created by the script
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 greenwolf/cve-2022-1162
Exploit for CVE-2022-1162: hardcoded password bypass in GitLab CE/EE OmniAuth accounts, enabling unauthorized login with a known credential.
 unix13/metasploitable2
PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
 duy-31/cve-2023-7028
An issue has been discovered in GitLab CE/EE affecting all versions from 16.1 prior to 16.1.6, 16.2 prior to 16.2.9, 16.3 prior to 16.3.7, 16.4 prior…
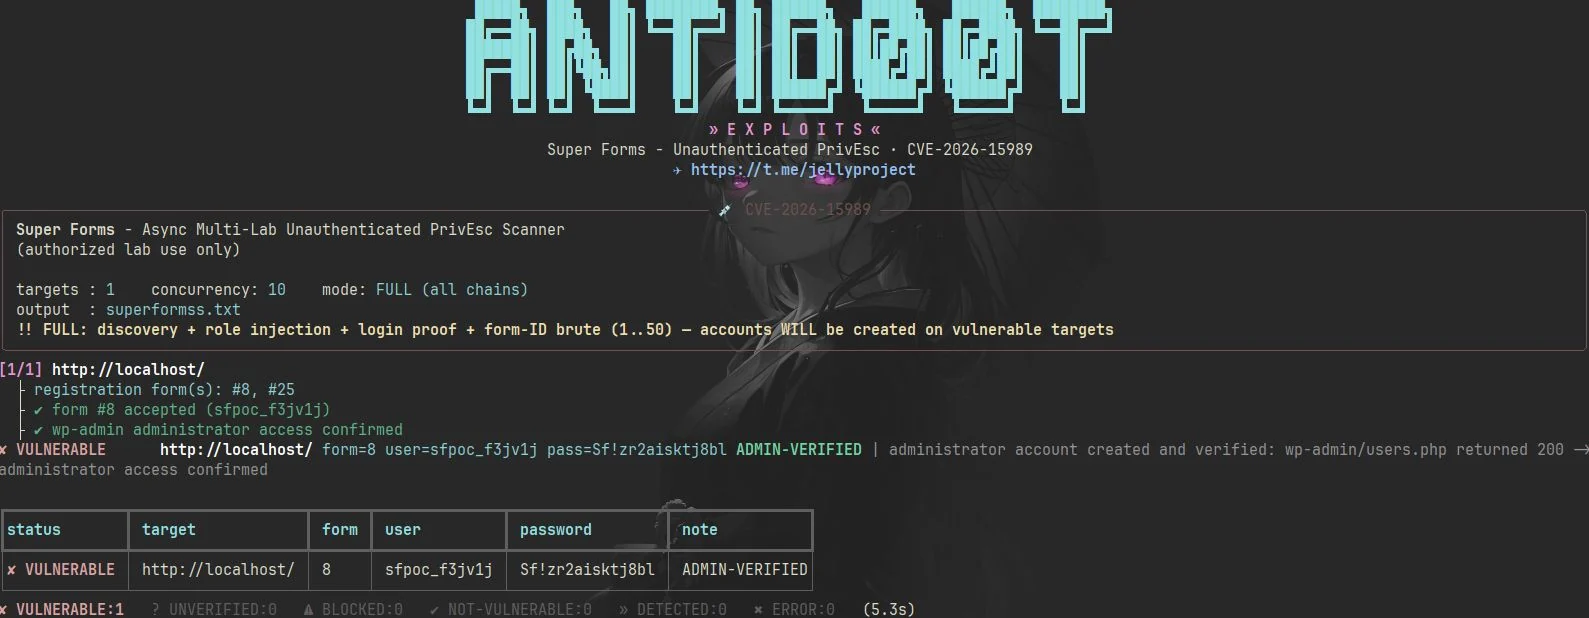 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
 randomrobbiebf/redash-reset
Exploit the Redash weak secret key vulnerability (GHSA-g8xr-f424-h2rv) to generate password reset links for any user, enabling account takeover…
 faceless0x7/cve-2026-93453
Python PoC for CVE-2026-93453, a SOGo password reset link poisoning flaw via attacker-controlled Origin header that enables reset token interception…
 nxploited/cve-2026-12416-cve-2026-12417
Unauthenticated Account Takeover via Weak Password Reset Validation via 'reset_user_id' Parameter | Unauthenticated Privilege Escalation via Weak…
 boonjune/poc-cve-2022-30600
A proof of concept for CVE-2022-30600