CVE-2026-13181-CVE-2026-13182-CVE-2026-13183-CVE-2026-13184

Educational proof-of-concept for Telerik padding oracle vulnerabilities (CVE-2026-13181-184) with scripts for authorized security testing and…

Educational proof-of-concept for Telerik padding oracle vulnerabilities (CVE-2026-13181-184) with scripts for authorized security testing and…

Curated vulnerability research repository with in-depth writeups, PoC scripts, and IOC detection tools for real-world security incidents like…

Programmatically create hunting rules for deserialization exploitation with multiple keywords, gadget chains, object types, encodings, and rule types

A deep look at some recon methodologies and web-application vulnerabilities of my interest where I will merge all my notes gathered from books,…

Curated collection of open redirect payloads sourced from bug bounty reports, with a shell script to substitute a target whitelisted domain for…

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…

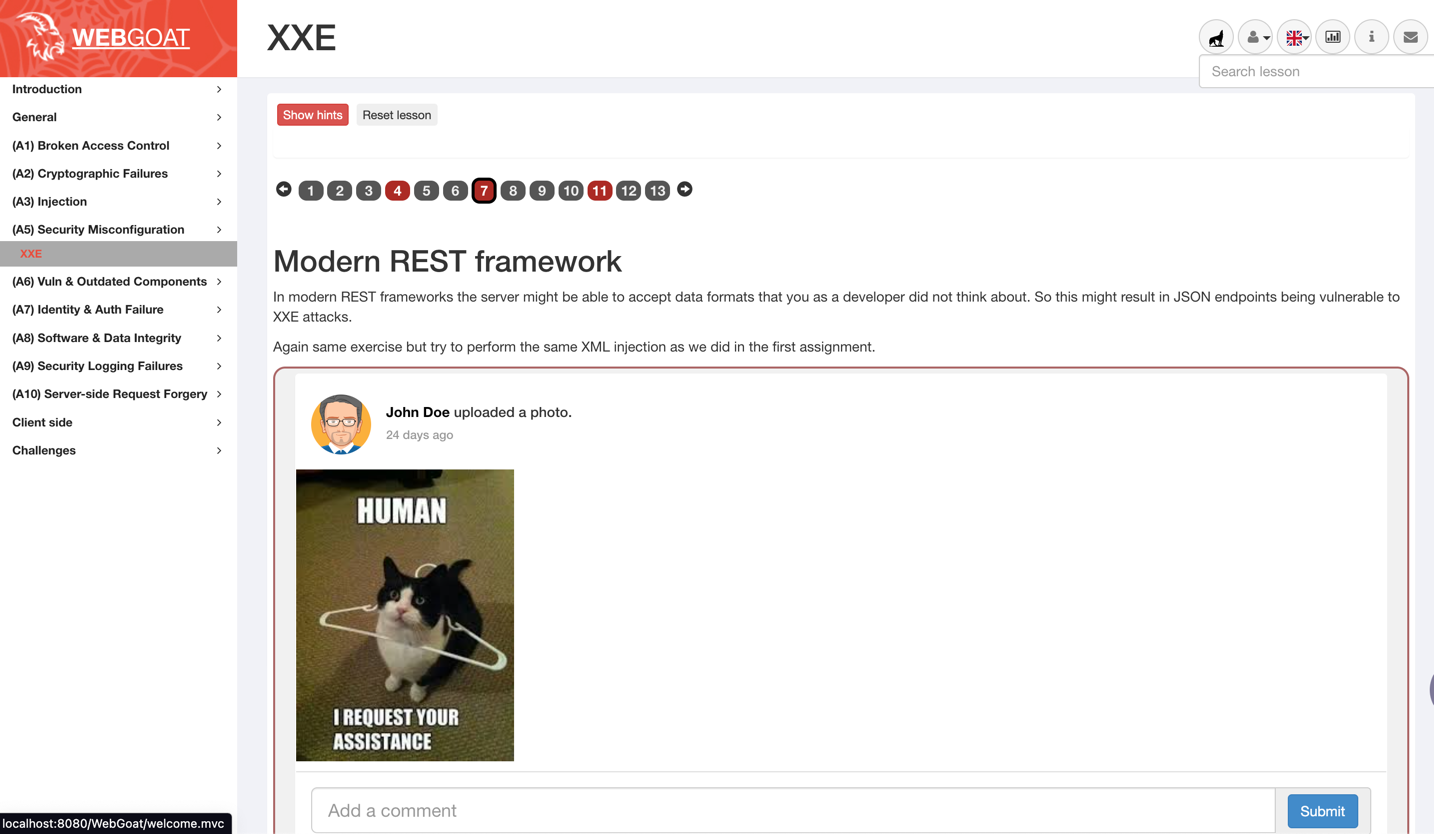
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…

Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…

Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…

Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…

PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…

Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…