

SneeitScanner-CVE-2025-6389
 itsismarcos/sneeitscanner-cve-2025-6389
SneeitScanner - PoC & Scanner para RCE não autenticada no Sneeit Framework (CVE-2025-6389)
command-and-controlexploitationpayload-generation+3
1
itsismarcos/sneeitscanner-cve-2025-6389SneeitScanner - PoC & Scanner para RCE não autenticada no Sneeit Framework (CVE-2025-6389)
 chiefyoru/cve-2026-21628_poc
Unauthenticated Remote Code Execution in Astroid Framework 2.0.0 - 3.3.10 for Joomla
 mrowkoob/cve-2023-33538-msf
CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework
 trevorputbrese/cve-2024-38819-lab
Hands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…
 r00t4dm/cve-2018-14667
about CVE-2018-14667 from RichFaces Framework 3.3.4
 mylo-2001/ghoststrike
Fully automated Spring4Shell (CVE-2022-22965) + GitLab RCE framework
 snip3r69/spring-shell-vuln
Spring has Confirmed the RCE in Spring Framework. The team has just published the statement along with the mitigation guides for the issue. Now, this…
 cj-0107/cve-2022-26134
PoC for CVE-2022-26134, a Confluence Server OGNL injection vulnerability, built on the pocsuite3 framework for authorized security testing.
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 opsecramdan/react2shell-cve-2025-55182
Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…
 mcorybillington/cve-2025-64328_freepbx-framework-command-injection
CVE-2025-64328 FreePBX Authenticated Command Injection in the framework module.
 valeriocassoni/csv-injection-in-instant-developer-foundation-25.0-poc
This repository contains a Proof of Concept (PoC) for a CSV Injection (Formula Injection) vulnerability (CVE-2025-60852) affecting applications built…
 nxploited/cve-2025-6389
Sneeit Framework <= 8.3 - Unauthenticated Remote Code Execution in sneeit_articles_pagination_callback
 kre80r/cve-2021-3007-vulnerable
CVE-2021-3007 Vulnerable Test Environment - Laminas/Zend Framework Deserialization RCE
 boroeurnprach/cve-2025-59057-poc
A XSS vulnerability exists in in React Router's meta()/<Meta> APIs in Framework Mode when generating script:ld+json tags which could allow arbitrary…
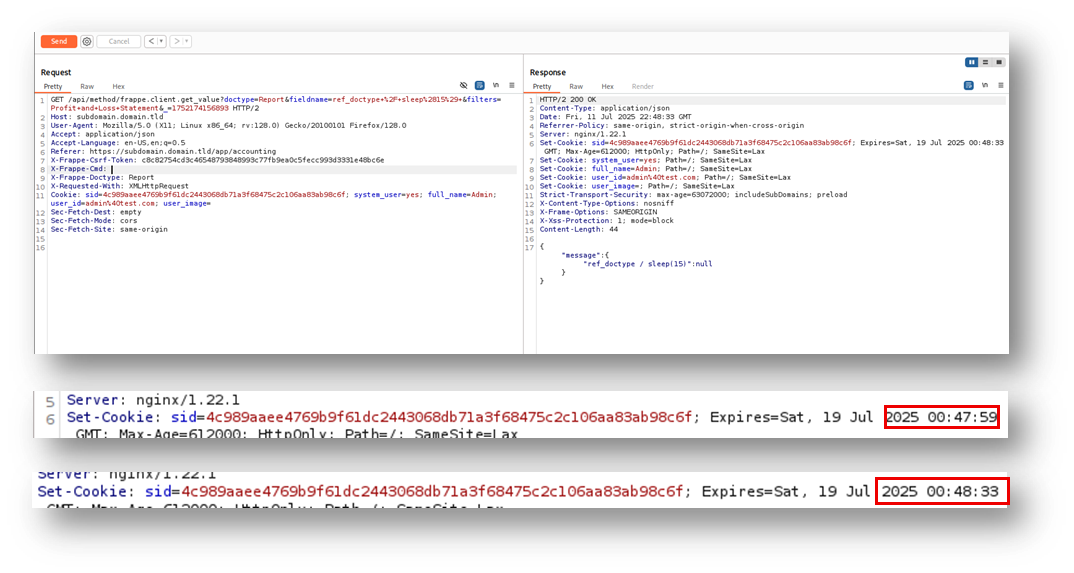 moalali/cve-2025-56380
Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…
 cved-sources/cve-2018-7600
Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…