

cve-2026-26114-poc
 huynambka/cve-2026-26114-poc
Proof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
command-and-controlexploitationexploit-frameworks+5
huynambka/cve-2026-26114-pocProof-of-concept exploit for CVE-2026-26114, a remote code execution vulnerability in Microsoft SharePoint, with a Python PoC and Metasploit module…
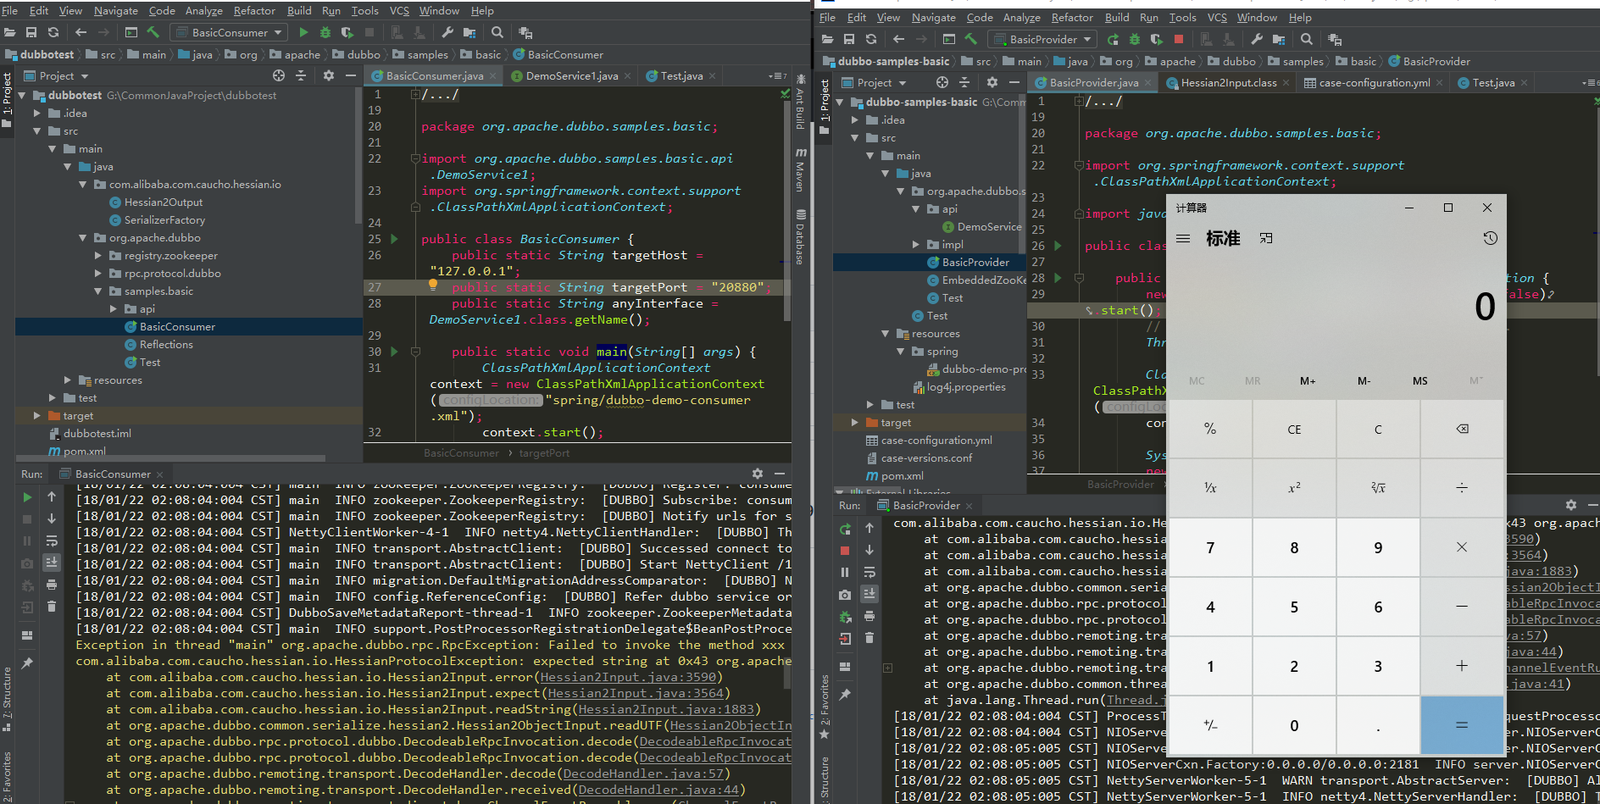 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 kagura-maru/cve-2021-40444-poc
An attempt to reproduce Microsoft MSHTML Remote Code Execution (RCE) Vulnerability and using Metasploit Framework.
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
 p0dalirius/awesome-rce-techniques
Awesome list of step by step techniques to achieve Remote Code Execution on various apps!
 taroballzchen/cve-2021-36260-metasploit
the metasploit script(POC) about CVE-2021-36260
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 xfox64x/cve-2016-5640
Crestron AirMedia AM-100 RCE (CVE-2016-5640) Metasploit Module
 sneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box
Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
 mefulton/cve-2018-11510
Just a couple exploits for CVE-2018-11510
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 im-hanzou/cve-2025-56399
CVE-2025-56399 – Remote Code Execution in laravel-file-manager v3.3.1. Exploits misconfigured config in Laravel File Manager to upload and verify a…
 alihzsec/cve-2025-55182
Critical RCE vulnerability scanner for React Server Components (CVE-2025-55182). Automated exploitation framework with multi-payload support, proxy…
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 shinthink/solrradar
☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
 projectdiscovery/katana
A next-generation crawling and spidering framework.
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…