
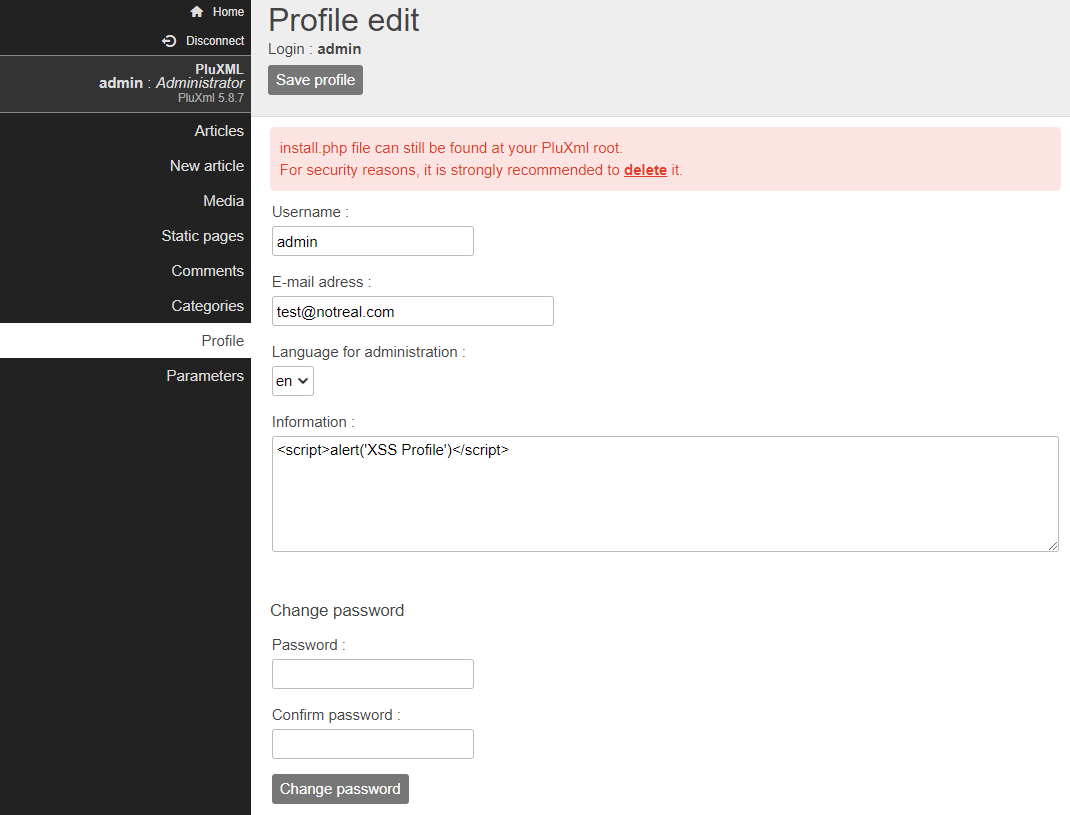
CVE-2021-38603
 kielvaughn/cve-2021-38603
Proof-of-concept for CVE-2021-38603: stored cross-site scripting (XSS) vulnerability in PluXML's profile edit page. Demonstrates injection via the…
exploitationpenetration-testingvulnerability-analysis+2
1
kielvaughn/cve-2021-38603Proof-of-concept for CVE-2021-38603: stored cross-site scripting (XSS) vulnerability in PluXML's profile edit page. Demonstrates injection via the…
 0xdtc/xwiki-platform-rce-cve-2025-24893
Bash exploit for CVE-2025-24893, unauthenticated RCE in XWiki Platform, using template injection in the SolrSearch macro to execute arbitrary system…
 th-secforge/cve-2025-30208
CVE‑2025‑30208 is a medium-severity arbitrary file read vulnerability in the Vite development server (a popular frontend build tool)
 0xqrx/cve-2024-6333
Authenticated Remote Code Execution vulnerability in Xerox WorkCentre printers via the Network Troubleshooting Log feature.
 dezso-dfield/cve-2023-27350
PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…
 simoesctt/sctt-2026-33-0004-forticloud-sso-identity-singularity
While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…
 dedsecteam-blackhat/cve-2025-68860
Exploit script for CVE-2025-68860 targeting WordPress Mobile Builder plugin. Generates forged JWT tokens using a hardcoded secret to authenticate as…
 grejh0t/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 (React2Shell), a critical unauthenticated RCE in React Server Components via unsafe deserialization in…
 rrespxwnss/cve-2025-63572
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…
 ranjithxploit/cve-2024-25600
Modified the CVE-2024-25600
 simoesctt/ctt-enhanced-vmware-vcenter
Looking at current high-impact vulnerabilities, let's use the VMware vCenter Server CVE-2021-21972 (CVSS 9.8) as our base. This is a publicly known…
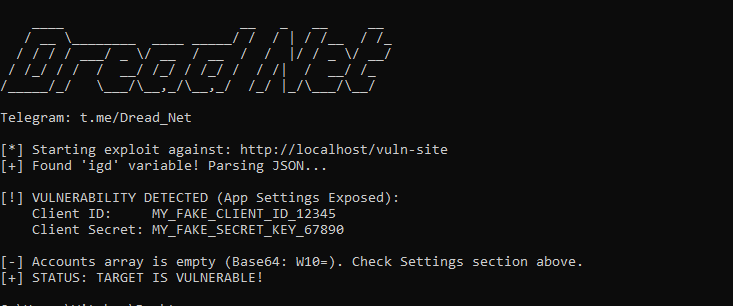 galaxy-sc/cve-2025-12139-wordpress-integrate-google-drive-exploit
Golang PoC exploit for CVE-2025-12139 targeting the Integrate Google Drive WordPress plugin. Extracts sensitive OAuth credentials (Client ID, Secret,…
 jfriedli/cve-2025-11973
Proof-of-concept exploit for CVE-2025-11973 demonstrating local file inclusion (LFI) in WordPress via file:// protocol, with automated exfiltration…
 code42cate/nexts-cve-2025-66478-exploit
Exploit for CVE-2025-66478 targeting Next.js applications. Provides proof-of-concept code to demonstrate and test the vulnerability in web…
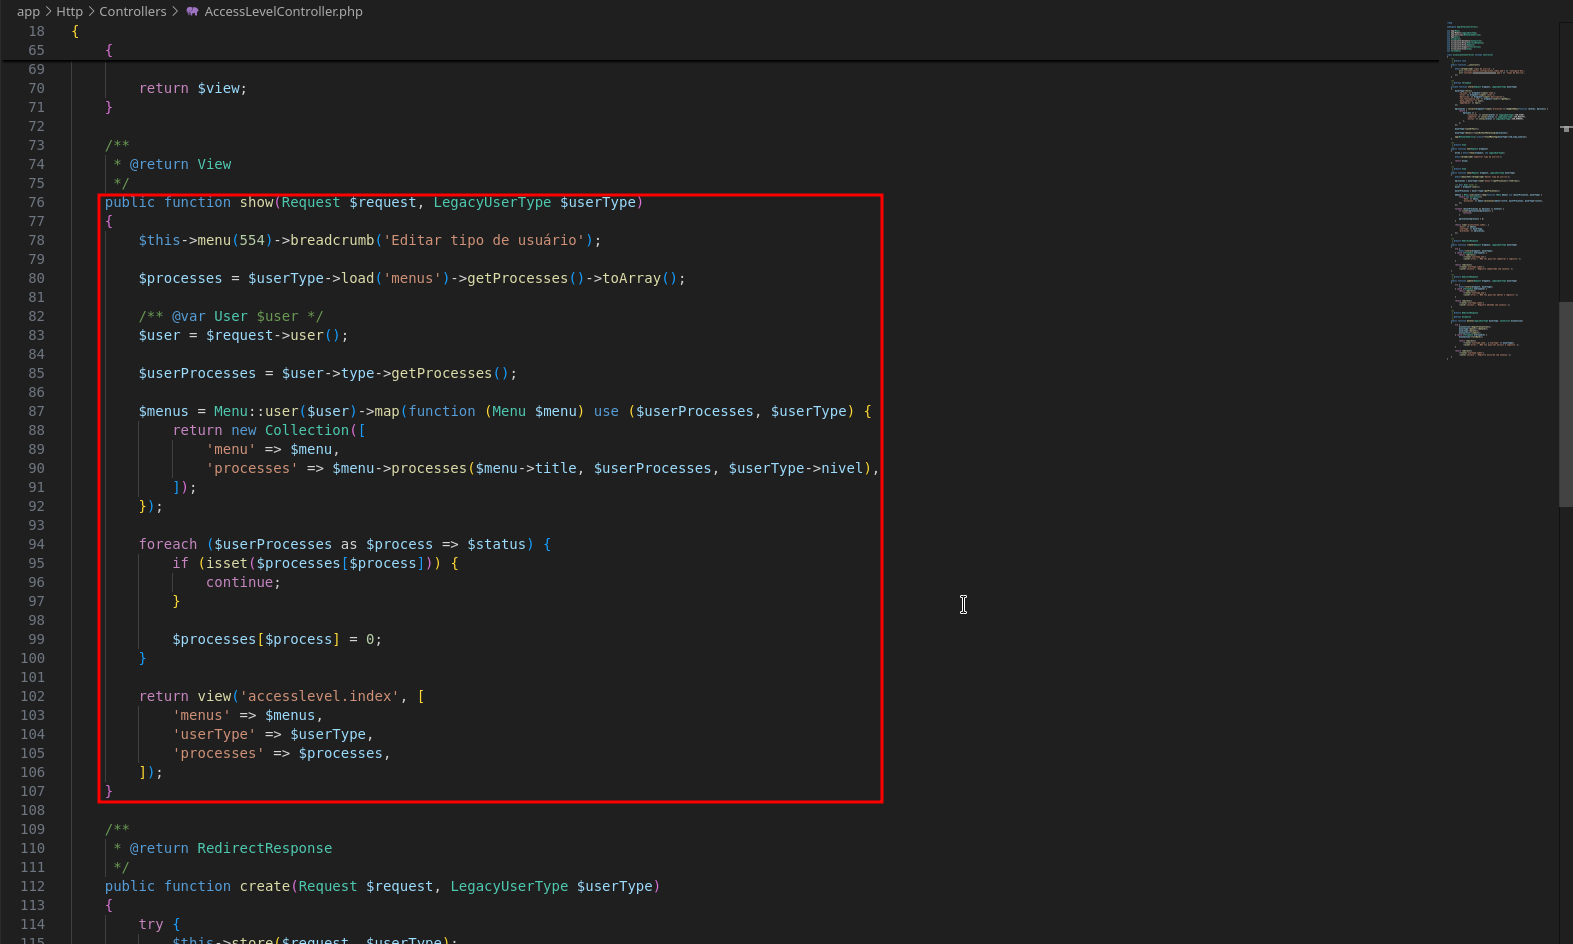 m3m0o/portabilis-ieducar-user-type-privilege-escalation
Proof of concept for exploitation of the vulnerability described in CVE-2025-11554, which concerns the possibility of a privilege escalation through…
 mbanyamer/cve-2026-25130-cybersecurity-ai-cai-framework-0.5.10
Proof-of-concept demonstrating argument injection leading to OS command injection in the CAI framework's find_file utility, enabling arbitrary…
 teteco/cve-2025-67070-intelbras-cftv-mfa-bypass
A critical vulnerability in the Intelbras NVD 9032 R Ftd IP CFTV device allows an attacker to bypass the multi-factor authentication during password…
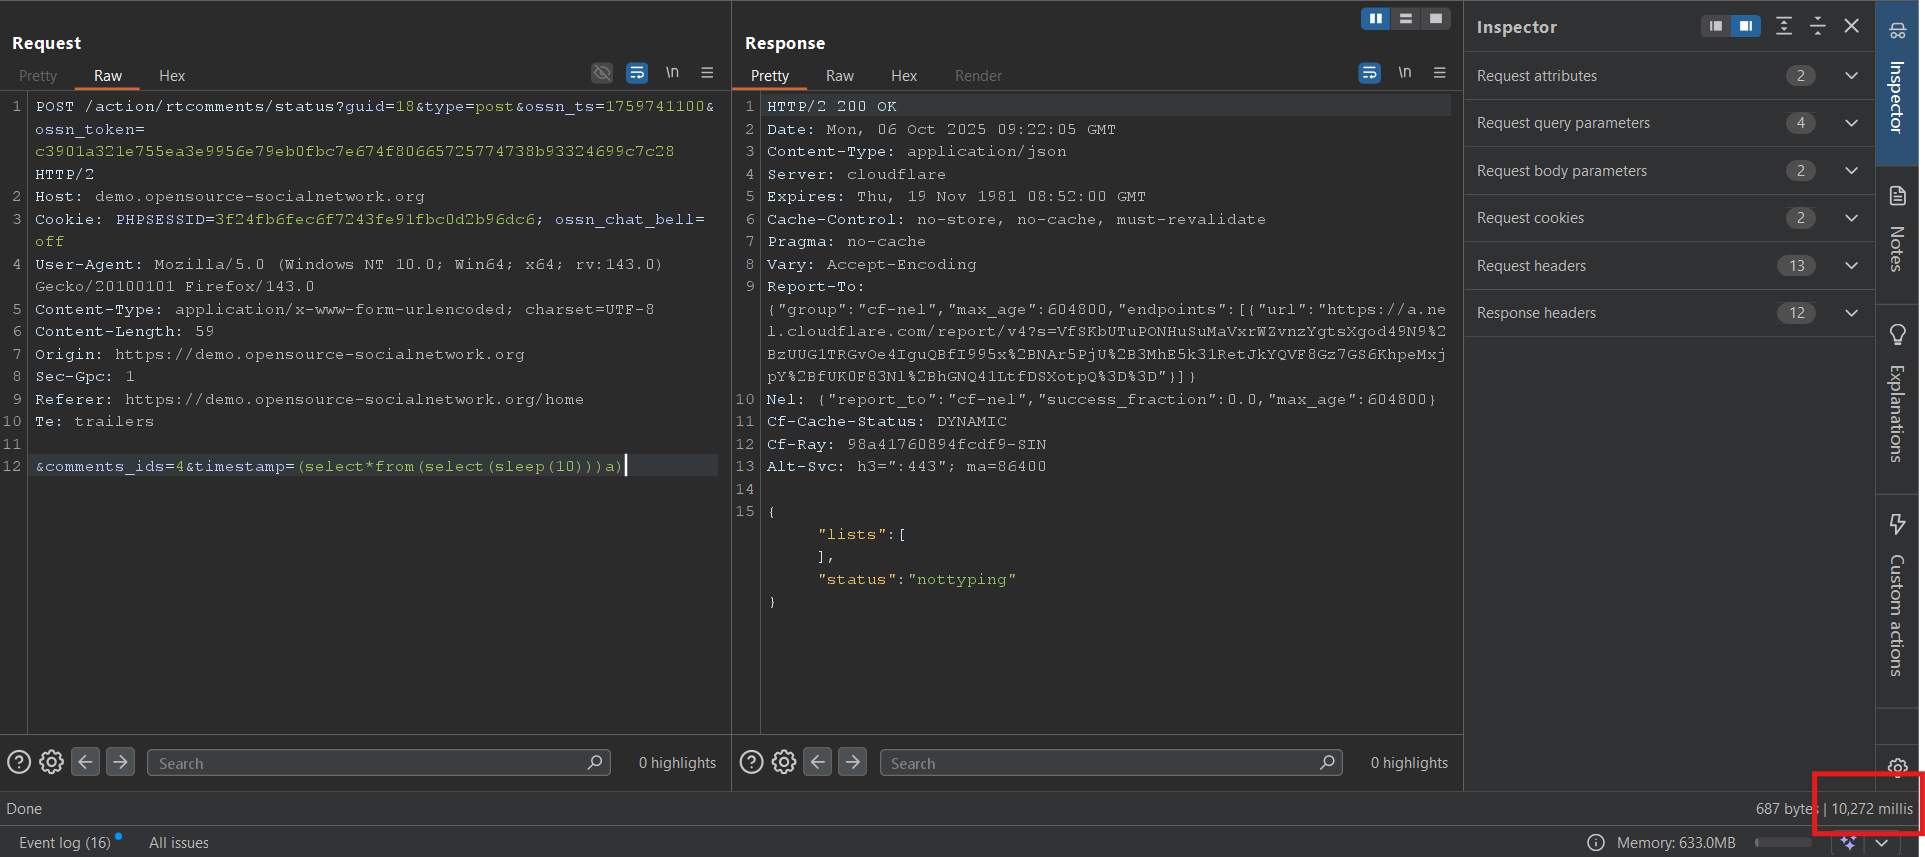 kgan0509/cve-2025-63585
Proof-of-concept for a blind time-based SQL injection vulnerability in OSSN's /action/rtcomments/status endpoint, demonstrating arbitrary SQL…