
CVE-2024-38819
 ghosts3c/cve-2024-38819
CVE-2024-38819 nuclei template
exploitationpenetration-testingvulnerability-analysis+2
31 year ago
ghosts3c/cve-2024-38819CVE-2024-38819 nuclei template
 soliux/cve-2021-41773
On the 11/11/21 the apache 2.4.49-2.4.50 remote command execution POC has been published online and this is a loader so that you can mass exploit…
 btamburi/strutszeiro
Telegram Bot to manage botnets created with struts vulnerability(CVE-2017-5638)
 0xgh057r3c0n/cve-2026-3844
WordPress - Breeze Cache <= 2.4.4 - Unauthenticated Arbitrary File Upload
 nullcult/cve-2025-31324-file-upload
A totally unauthenticated file-upload endpoint in Visual Composer lets anyone drop arbitrary files (e.g., a JSP web-shell) onto the server.
 mingyisecurity-lab/cve-2025-55182-tools
A Comprehensive CVE-2025-55182 Detection and Security Assessment Tool
 r4p3c4/cve-2024-24919-exploit-poc-checkpoint-firewall-vpn
Herramienta de explotación para explotar la vulnerabilidad CVE-2024-24919 en las VPN de Checkpoint Firewall
 randomrobbiebf/cve-2020-12077
MapPress Maps Pro < 2.53.9 - Remote Code Execution (RCE) due to Incorrect Access Control in AJAX Actions
 vulnmachines/confluence-cve-2023-22515
Confluence Broken Access Control
 ianxtianxt/proxysqlmap
From Proxy to SqlMapApi
 whiteov3rflow/cve-2026-41472-poc
CyberPanel v2.4.3 XSS Chain to RCE CVE-2026-41472
 im-hanzou/cve-2026-3844
Breeze Cache WordPress <=2.4.4 allows unauthenticated file upload via fetch_gravatar_from_remote when local gravatar hosting is enabled.
 cappricio-securities/cve-2018-8033
Apache OFBiz 16.11.04 is susceptible to XML external entity injection (XXE injection)
 1beelze/cve-2026-11387
Exploits unauthenticated privilege escalation in SMS Alert WooCommerce plugin (CVE-2026-11387) via OTP bypass and arbitrary password reset, with…
 jenderal92/wp-cve-2023-2732
Python 2.7
 polosss/by-poloss..-..cve-2026-12432-poc
WP Full Stripe Free <= 8.4.3 - Missing Authorization
 emanueldosreis/nmap-cve-2023-35078-exploit
Nmap script to exploit CVE-2023-35078 - Mobile Iron Core
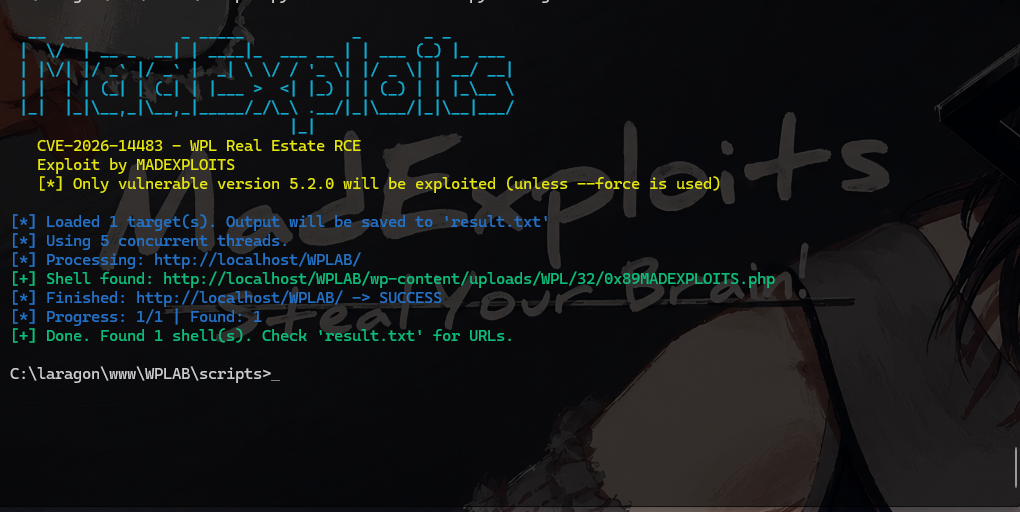 madexploits/cve-2026-14483
CVE-2026-14483 POC EXPLOIT BY MADEXPLOITS