
CVE-2026-41940-PoC
 zerodayevil/cve-2026-41940-poc
Proof-of-concept code demonstrating CVE-2026-41940, providing a reproducible test case for vulnerability verification and security research.
exploitationpenetration-testingvulnerability-analysis+1
28
zerodayevil/cve-2026-41940-pocProof-of-concept code demonstrating CVE-2026-41940, providing a reproducible test case for vulnerability verification and security research.
 zerodayevil/cve-2026-41096-poc
Proof-of-concept exploit for CVE-2026-41096, demonstrating the vulnerability and providing a reproducible test case for security researchers and…
 boreas37/cve-2026-56705
PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.
 cyb3rk0ala/cve-2022-35914-rce
PoC exploit for CVE-2022-35914 — GLPI v.10.0.2 htmLawed command injection, command execution, and reverse shell support.
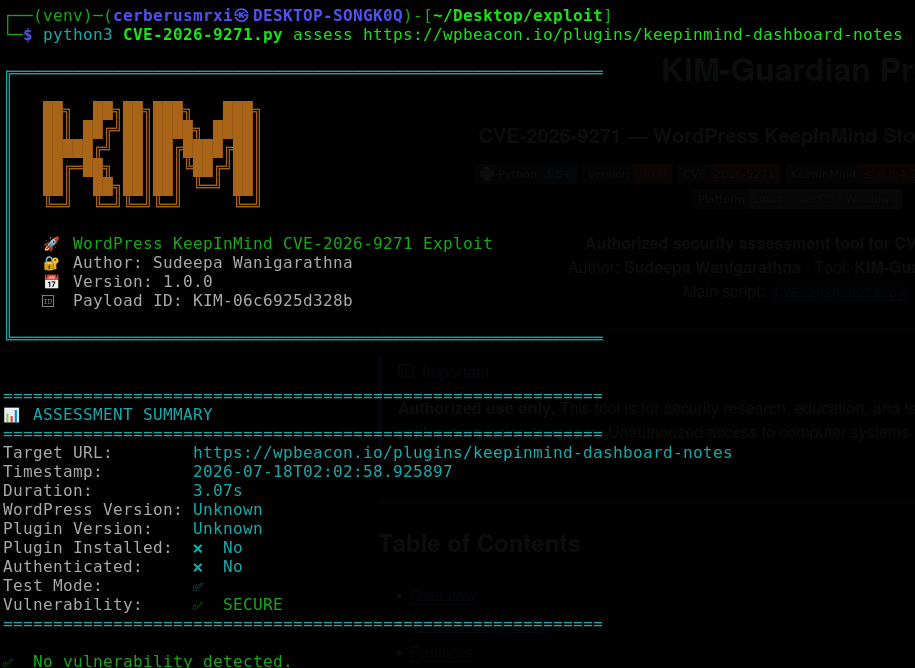 cerberusmrxi/wordpress-keepinmind-cve-2026-9271-exploit
Authorized stored XSS assessment tool for CVE-2026-9271 in WordPress KeepInMind plugin. Detects vulnerable versions, injects safe test payloads, and…
 synacktiv/nounours
Nounours is a tool designed to test APP_KEYs at scale on Laravel applications.
 funixone/exploit-cve-2026-8832
Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…
 funixone/exploit-cve-2026-8832-
Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…
 xitexploiter96-dot/cve-2025-23419
Python-based TLS session reuse exploit tester that checks for authentication bypass vulnerabilities in misconfigured servers requiring client…
 carlosaruy/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…
 sorrence/cve-2021-44228
A simple Log4j PoC written in Go
 tdawg506/cve-2025-31161
Scans target to see if its vulnerable to CVE-2025-31161
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
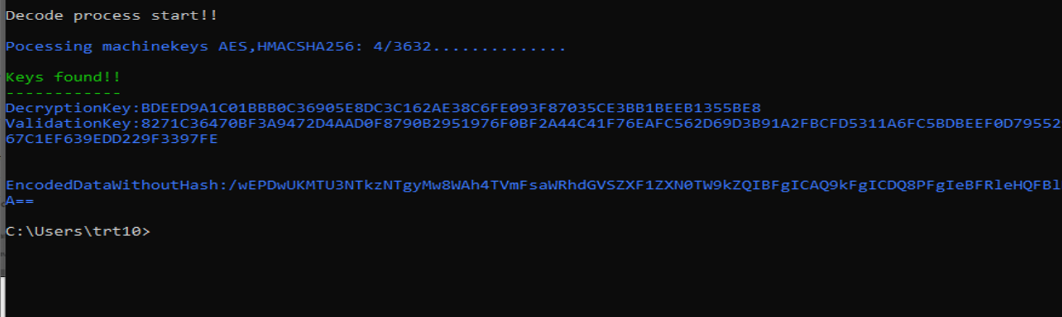 orwagodfather/aspdotnetwrapper-edited-
This Tool To Test Machine Keys In View State
 dzonerzy/gowapt
Go Web Application Penetration Test
 zyx2440/apache-http-server-2.4.50-rce
Apache-HTTP-Server-2.4.50-RCE This tool is designed to test Apache servers for the CVE-2021-41773 / CVE-2021-42013 vulnerability. It is intended for…
 geniuszly/cve-2022-44149
Python script to test CVE-2022-44149 router vulnerability via authenticated payload delivery to the web interface, with logging for security…
 b-abderrahmane/cve-2021-44228-playground
Docker-based lab to validate CVE-2021-44228 (Log4Shell) in Java apps, test mitigations, and simulate RCE via LDAP and HTTP payloads.