
prismsec
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
dns-subdomain-enumerationpenetration-testingpenetration-testing-frameworks+7
azmisyahrul/prismsecSecure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 baktistr/cve-2026-23550-poc
Bash-based proof-of-concept tester for CVE-2026-23550. Checks WordPress modular connector login endpoints for admin cookie issuance and verifies…
 nu11secur1ty/g0burpsqlmapi
CLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…
 1beelze/cve-2026-23550
Root-cause analysis, PoC, and detection guidance for CVE-2026-23550, a critical unauthenticated admin session takeover in the WordPress plugin…
 sangsenimanwartefak/cve-2026-23550
Bash exploit for CVE-2026-23550 that triggers unauthenticated WordPress admin login via crafted REST API request to Modular Connector's…
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…
 dedsecteam-blackhat/cve-2026-23550
Bash script for WordPress user enumeration and automated admin account creation, exploiting CVE-2026-23550 to bypass authentication and achieve…
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 xeloxa/cve-2024-28397-js2py-rce-exploit
Professional exploit for CVE-2024-28397: Js2Py Sandbox Escape leading to Remote Code Execution (RCE). Includes modular payload generation.
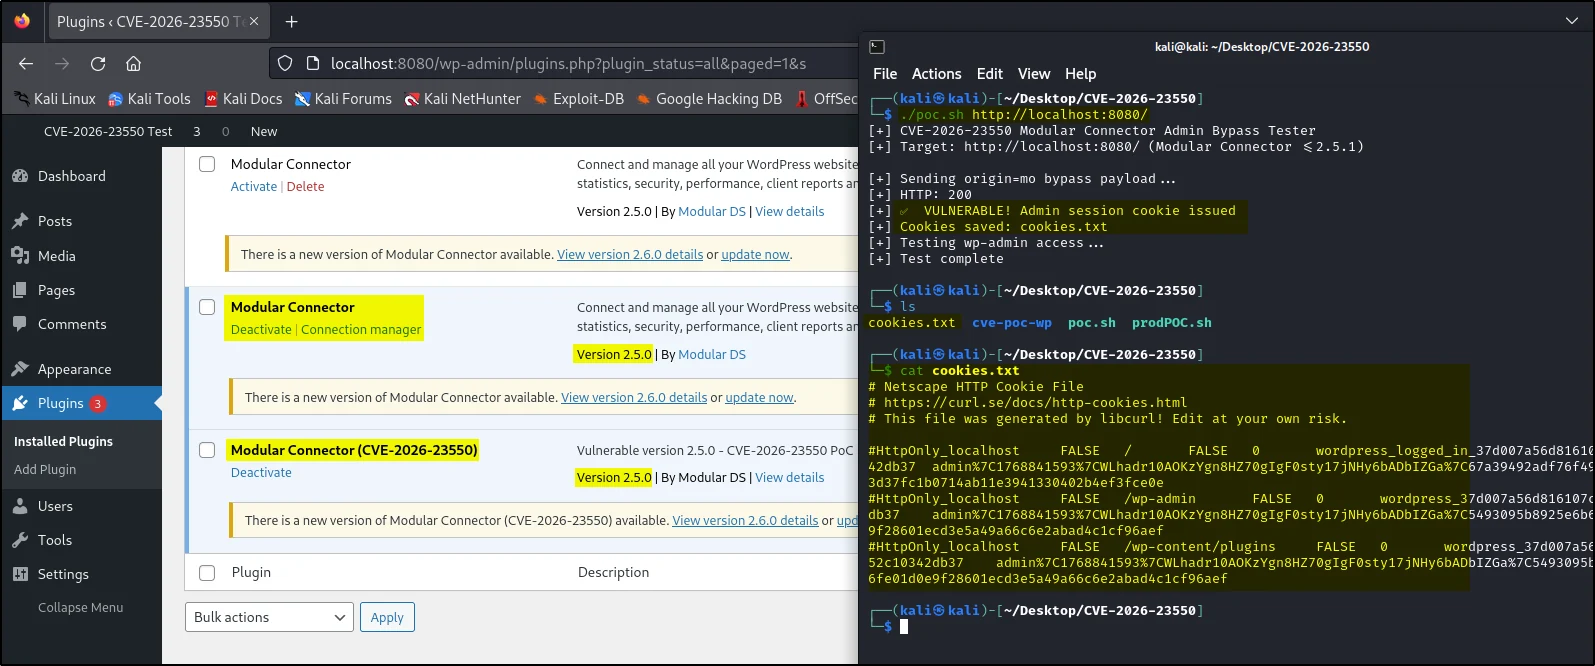 thetorjancaptain/cve-2026-23550-poc
CVE-2026-23550 - Modular DS WordPress Plugin **Unauthenticated Admin Access**
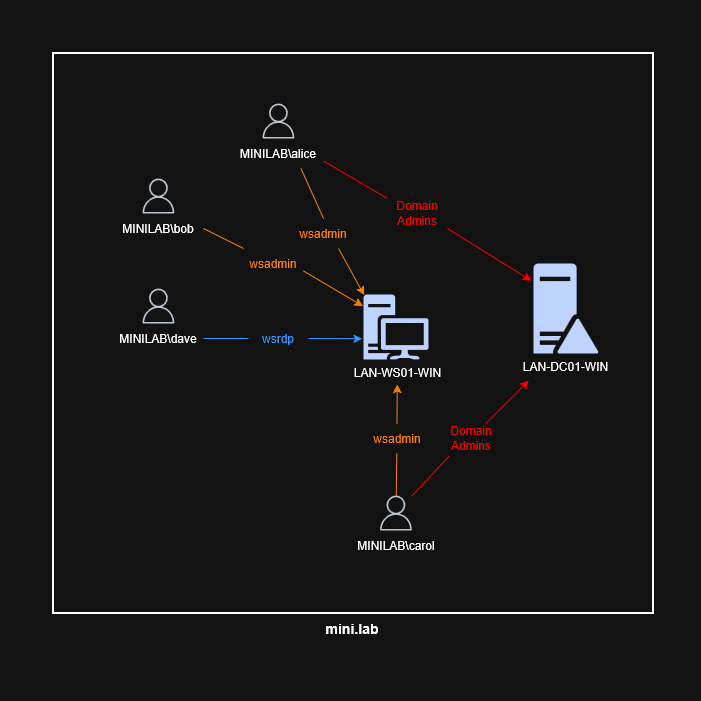 0xmr007/lab4purplesec
Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
 mylo-2001/ghoststrike
Fully automated Spring4Shell (CVE-2022-22965) + GitLab RCE framework
 thestingr/cve-2024-36991-tool
This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…
 dannz1337/deep-reaver
AI-enhanced vulnerability assessment and exploitation toolkit for modular scanning of web applications, detecting SQLi, XSS, RCE, CSRF, and more with…