
Panoptic
 lightos/panoptic
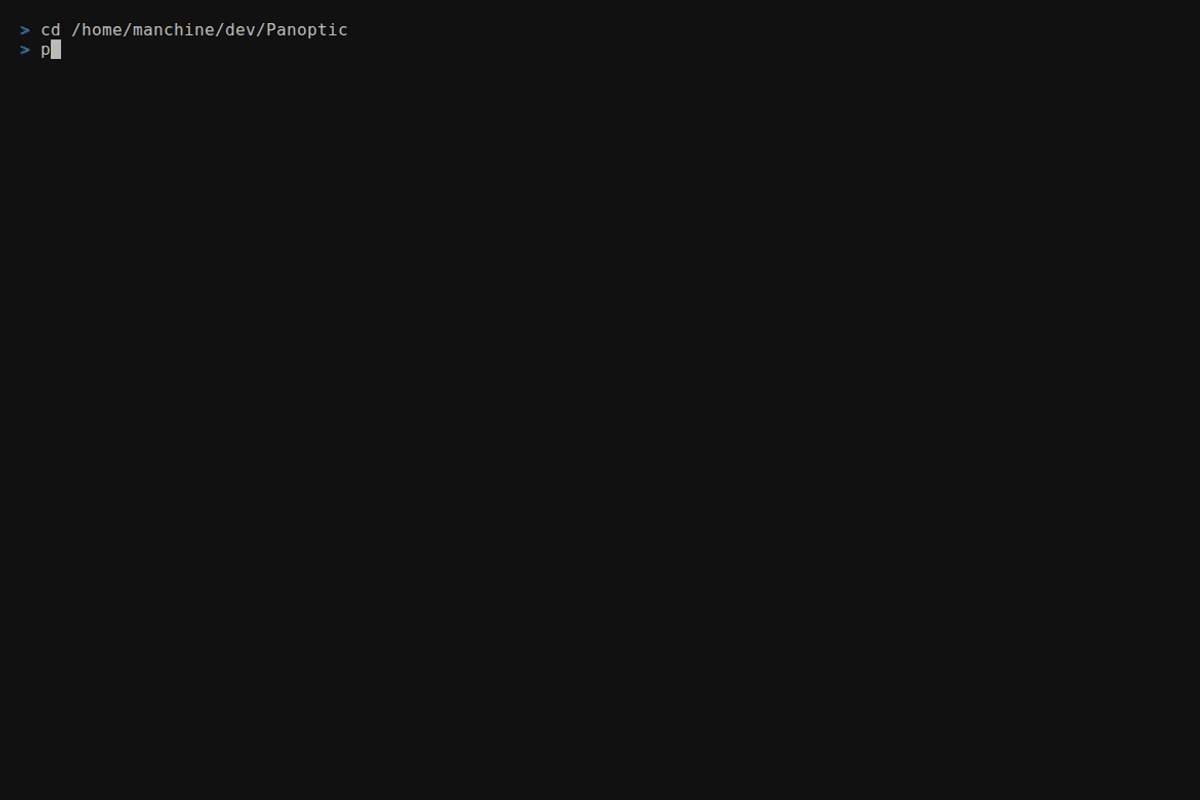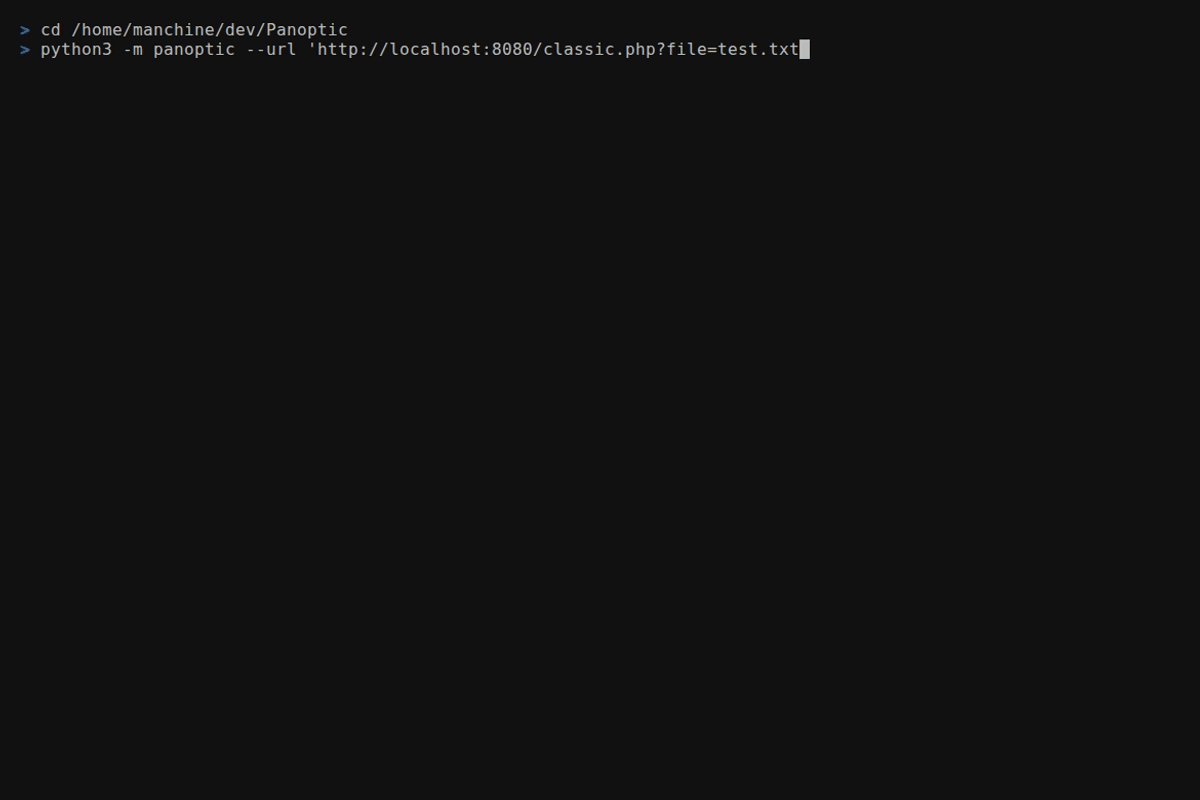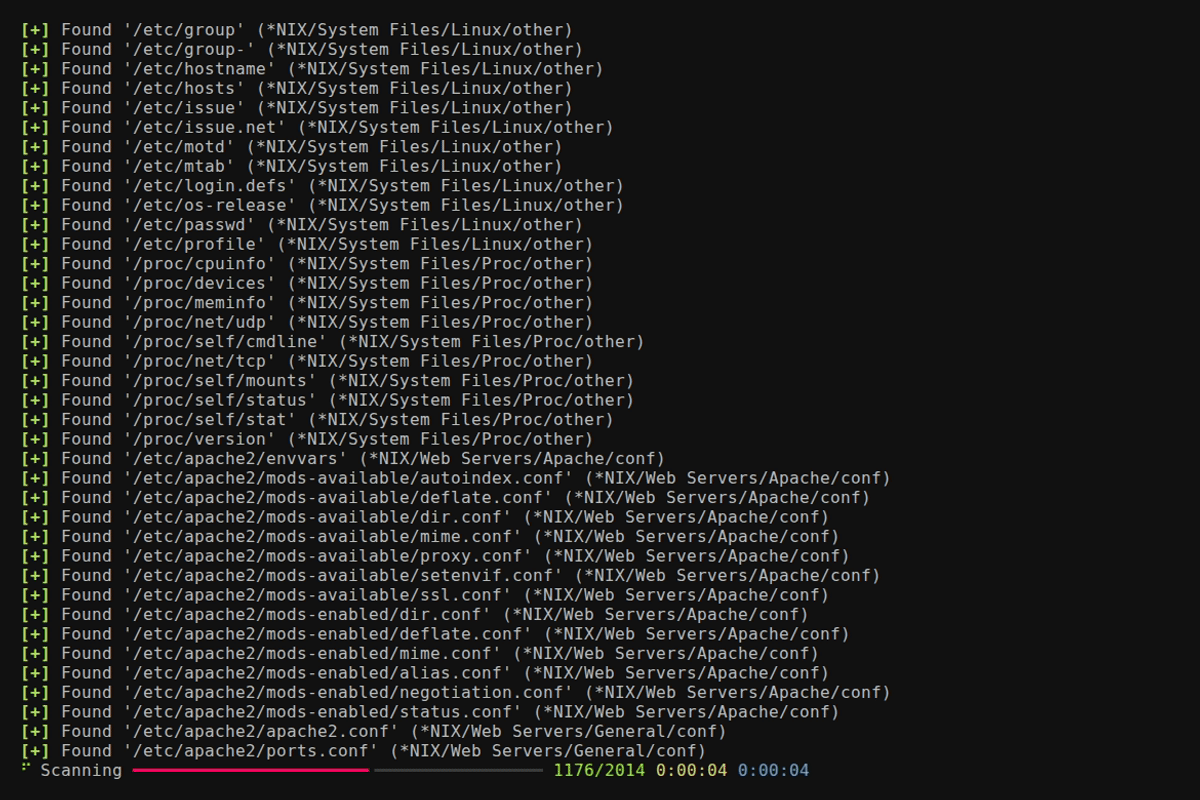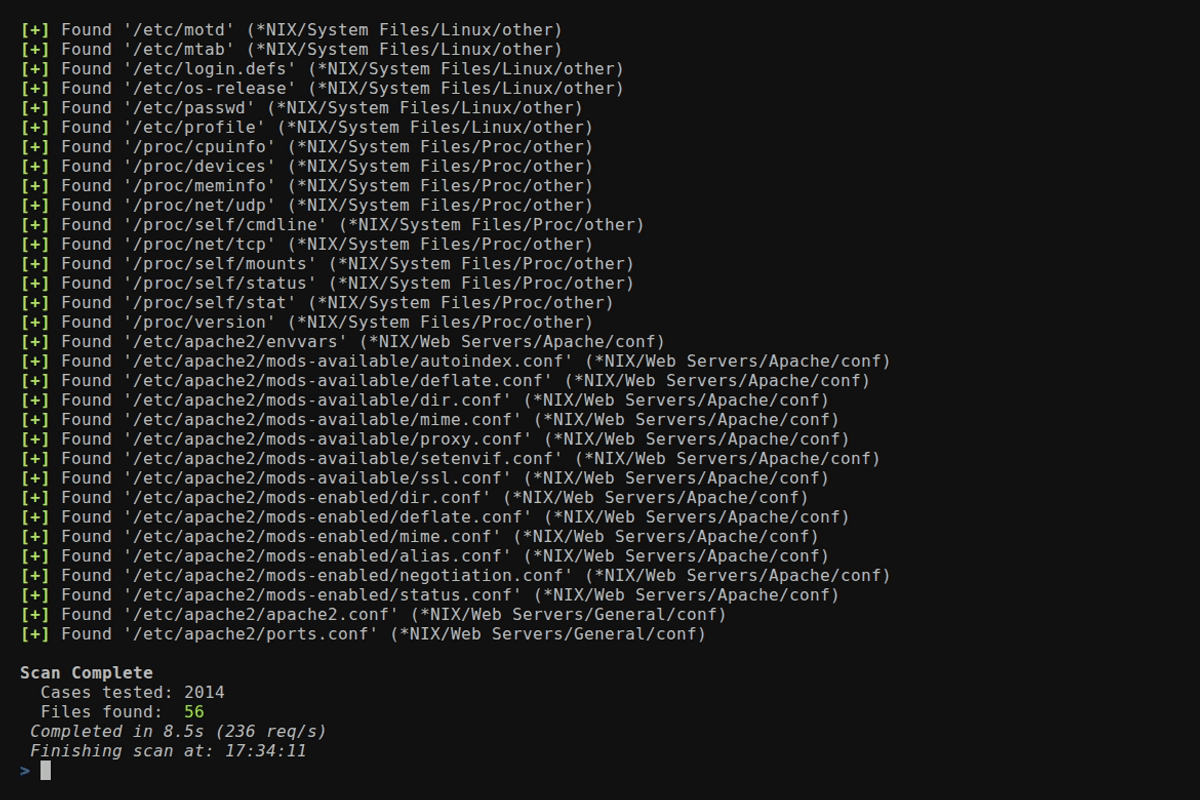
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…
information-gatheringpenetration-testingreconnaissance+2
325
lightos/panopticPanoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…
 juanpoch/cve-2026-73570
Zimbra Collaboration Suite RCE — SMTP log poisoning → swatchdog → OS Command Injection (CVSS 8.9, CISA KEV)
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 skraft9/cve-2025-29471
Stored XSS in Nagios Log Server 2024R1.3.1
 biutrap/cve-2026-59310
Proof-of-concept exploit for CVE-2026-59310, demonstrating remote path traversal via crafted syslog messages to write arbitrary log files on VMware…
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…
 giangdurian/cve-2021-3129
Python exploit script for Laravel Ignition CVE-2021-3129 RCE, using log poisoning and phar deserialization to execute commands on vulnerable web apps.
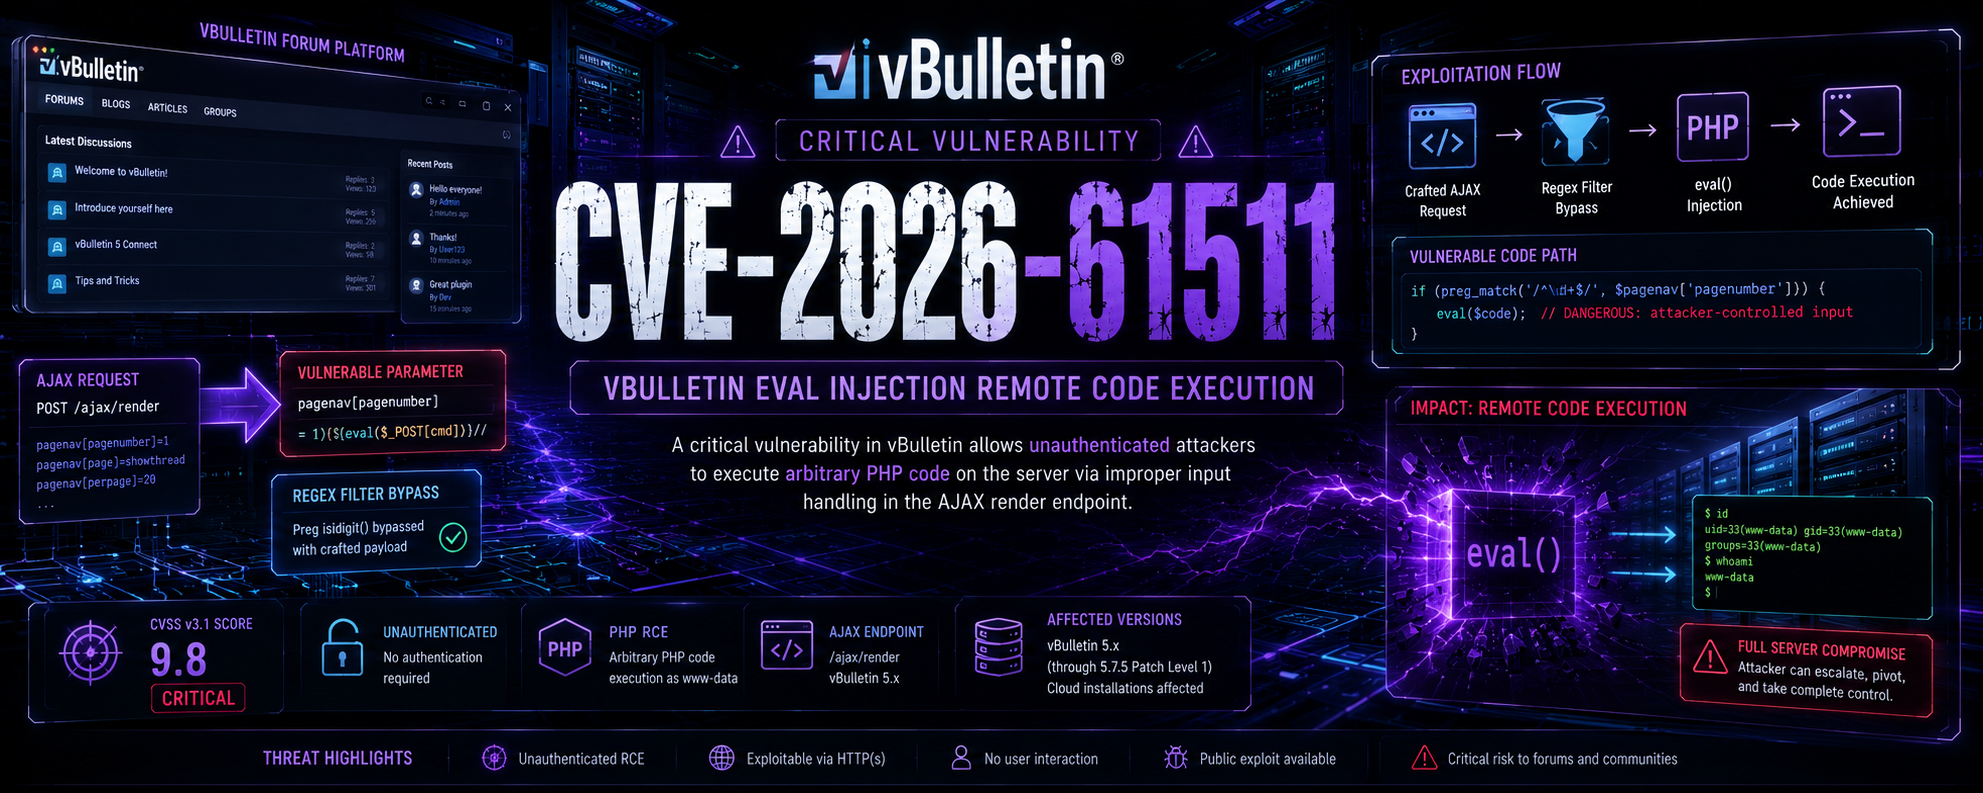 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 george0papasotiriou/cve-2026-21011-log4j-style-jndi-injection-in-custom-logger-simulated-
Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…
 shinthink/cve-2026-58025
CVE-2026-58025 — MediaWiki Deserialization RCE via Log Entry Import. LogEntryBase::extractParams() unserialize() user-controlled log_params. CVSS 9.8…
 5kr1pt/glpi-logbleed
PoC for CVE-2026-53629, blind SQL injection in the GLPI history log filter
 l0lsec/cve-2021-26837
CVE-2021-26837 - SQL Injection in the SearchTextbox parameter of HelpSystems/Fortra DeliverNow. Payloads, annotated requests, and evidence. Fixed in…
 jtmh37/apache-tomcat-cve-2025-24813-lab
ICT279 Vulnerability Detection and Mitigation Project using CVE-2025-24813 in an Internet Banking Environment
 bp2008/dahualoginbypass
Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.
 lyccyc/cve-2023-41892_poc
Proof-of-concept scripts and Docker lab for reproducing CVE-2023-41892, a pre-authenticated remote code execution vulnerability in Craft CMS.…
 polosss/by-poloss..-..cve-2026-39938
Proof-of-concept exploit for CVE-2026-39938: unauthenticated local file inclusion in Cacti <= 1.2.30, enabling arbitrary file read and remote code…
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…