

Project-CVE-2026-33017
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
command-and-controlexploitationpayload-development+6
1
e4zyy/project-cve-2026-33017CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 nu11secur1ty/g0burpsqlmapi
CLI tool for generating SQL injection PoC requests, automating sqlmap attacks, and managing modular exploit scripts with interactive menu and…
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 pysectools/cve-2026-3629
WordPress Privilege Escalation Checker
 rix4uni/cve-2025-55182
A command-line tool for detecting CVE-2025-55182 and CVE-2025-66478 in Next.js applications using React Server Components.
 orwagodfather/react2shell-scanner
RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 assetnote/react2shell-scanner
High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 alessiodos/react2shell-scanner
CVE-2025-55182 & CVE-2025-66478 Detection Tool for Next.js RSC RCE
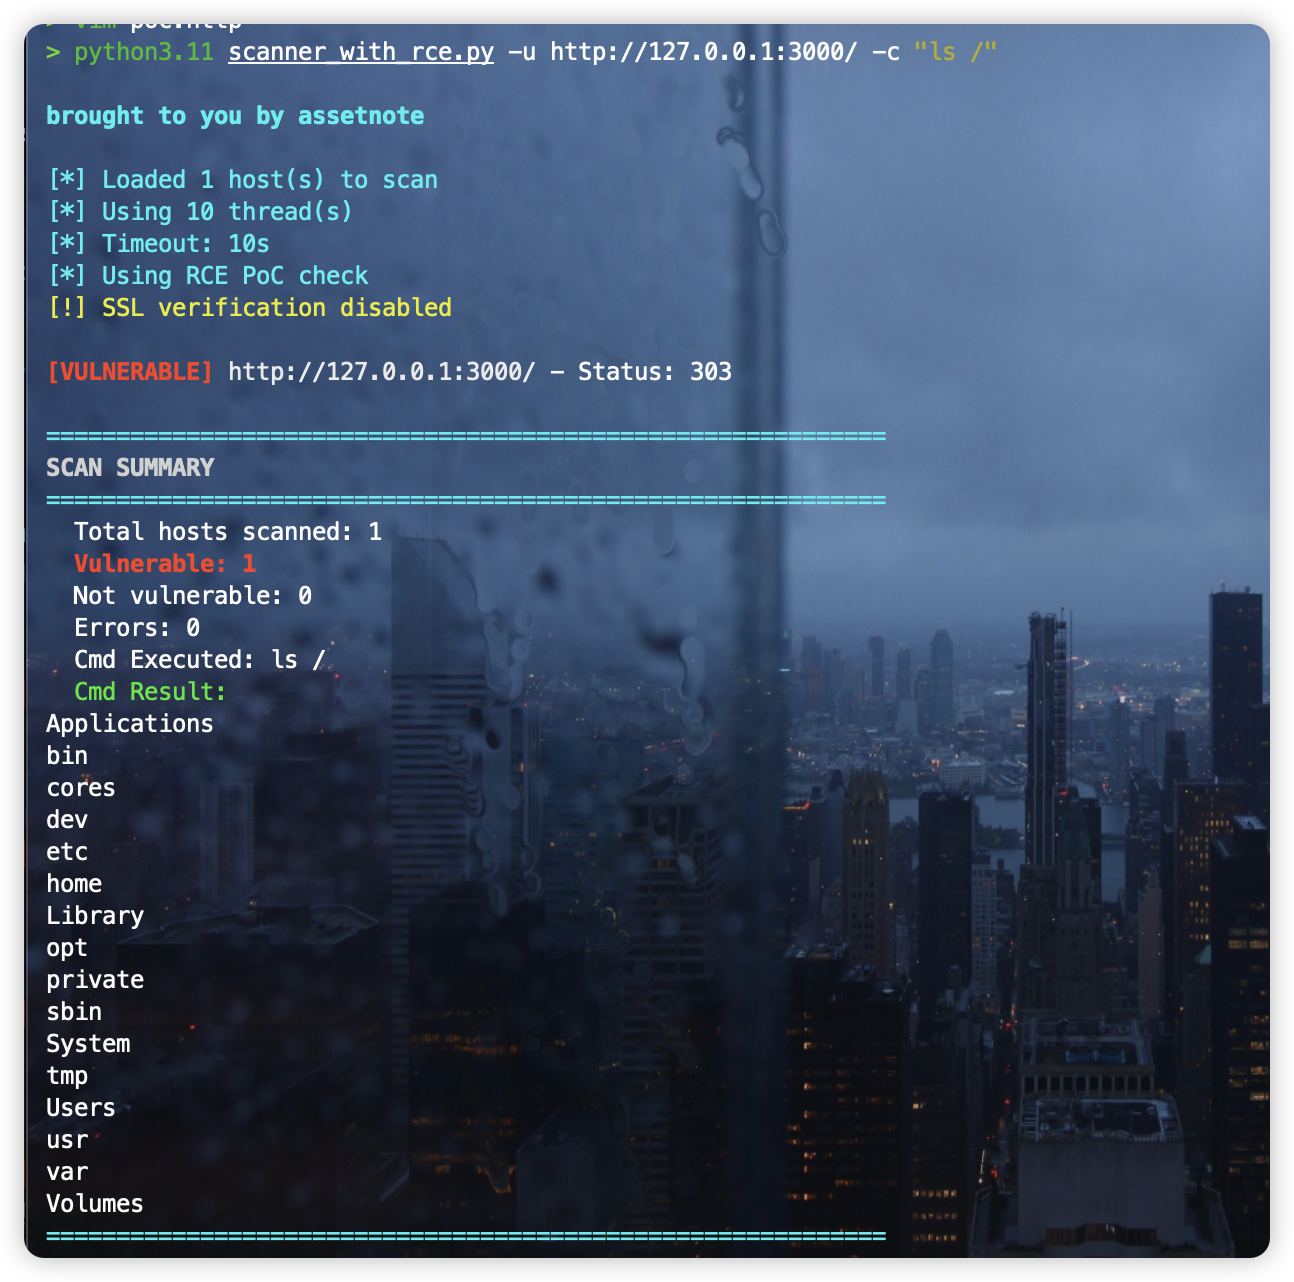 zzhorc/cve-2025-55182
CVE-2025-55182复现环境及RCE回显poc
 ambionics/phpggc
PHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
 anonkryptiquz/nextsploit
NextSploit is a command-line tool designed to detect and exploit CVE-2025-29927, a security flaw in Next.js
 pixilated730/nextjs-exploit-
CVE-2025-29927
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
 iqzer0/vulnknox
A Go-based wrapper for the KNOXSS API to automate XSS vulnerability testing.
 abbarhissarh/follinaxploit
A Command Line based python tool for exploit Zero-Day vulnerability in MSDT (Microsoft Support Diagnostic Tool) also know as 'Follina' CVE-2022-30190.
 hrishikesh7665/follina_exploiter_cli
Exploit Microsoft Zero-Day Vulnerability Follina (CVE-2022-30190)
 farjaalahmad/cve-2019-16759
Interactive-Like Command-Line Console for CVE-2019-16759