Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
POC_SQL_injection_in_Parse_Server_prior_6.5.7_-_7.1.0 preview

POC_SQL_injection_in_Parse_Server_prior_6.5.7_-_7.1.0

GitHubheavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0

Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…

database-securityexploitationinformation-gathering+3
1
8 days ago
CVE-2023-40028 preview

CVE-2023-40028

GitHubgodylockz/cve-2023-40028

POC for CVE-2023-40028: Ghost CMS Arbitrary File Read

data-exfiltrationexploitationinformation-gathering+3
21 month ago
CVE-2026-26980 preview

CVE-2026-26980

GitHubyym8538/cve-2026-26980

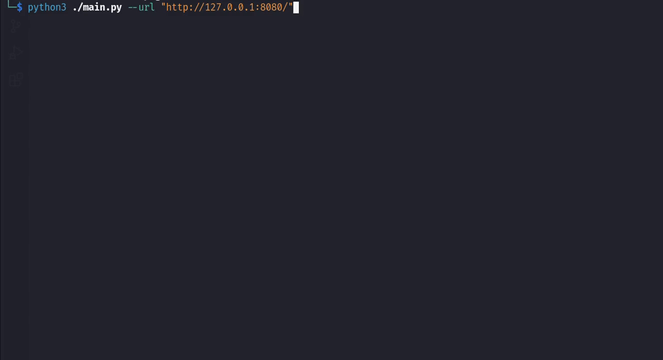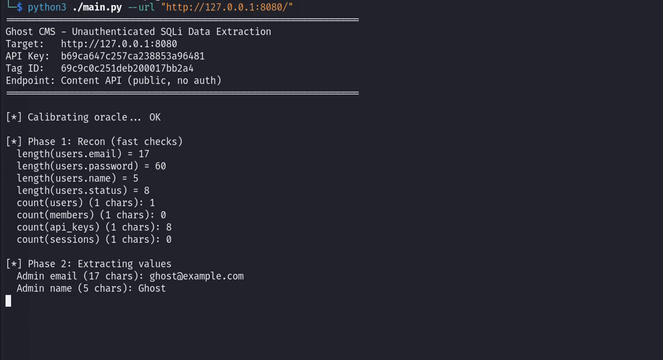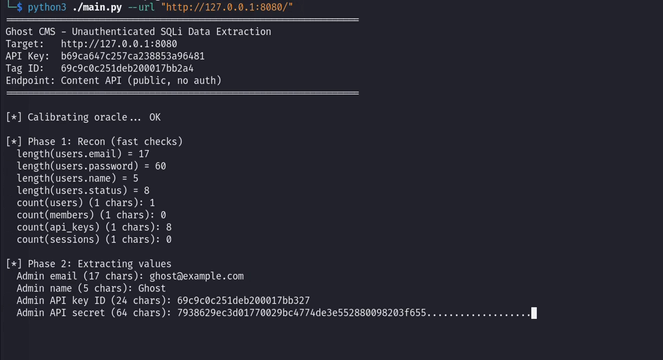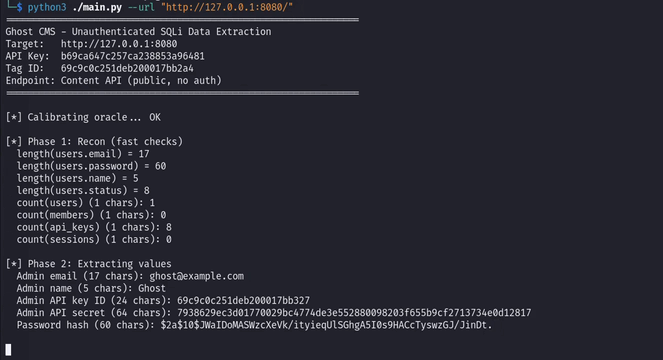
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…

database-securityeducationexploitation+5
12 months ago
CVE-2026-26980 preview

CVE-2026-26980

GitHubvognik/cve-2026-26980

Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…

database-securitydata-exfiltrationexploitation+4
102 months ago
CVE-2026-26980-PoC preview

CVE-2026-26980-PoC

GitHubn0bitaemon/cve-2026-26980-poc

Ghost CMS Content API Blind SQL Injection

database-securityexploitationinformation-gathering+4
14 months ago
CVE-2026-26980-Ghost-CMS-Api preview

CVE-2026-26980-Ghost-CMS-Api

GitHubgagaltotal/cve-2026-26980-ghost-cms-api

Go-based PoC for Ghost CMS Content API SQL injection (CVE-2026-26980). Verifies vulnerability, extracts admin credentials and API secrets, and…

exploitationinformation-gatheringpenetration-testing+2
114 months ago
CVE-2026-26980 preview

CVE-2026-26980

GitHubeqstlab/cve-2026-26980

Ghost Content API SQL Injection

educationexploitationlabs-practice+3
35 months ago
CVE-2026-29053 preview

CVE-2026-29053

GitHubac8999/cve-2026-29053

(RCE) vulnerability discovered in Ghost CMS (specifically affecting versions 0.7.2 through 6.19.0)

exploitationpayload-developmentpenetration-testing+2
16 months ago
ghost-cve-2026-26980 preview

ghost-cve-2026-26980

GitHubdinosn/ghost-cve-2026-26980

CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)

database-securityeducationexploitation+5
196 months ago
CVE-2025-66849 preview

CVE-2025-66849

GitHubwojtekchwala/cve-2025-66849

Ghost CMS Privilege Escalation PoC

exploitationpayload-developmentpenetration-testing+3
6 months ago
CVE-2026-29053 preview

CVE-2026-29053

GitHubrootxran/cve-2026-29053

Proof-of-concept exploit for Ghost CMS remote code execution via prototype pollution in jsonpath and static-eval, with a vulnerable environment setup…

exploitationpayload-developmentpenetration-testing+2
17 months ago
CVE-2023-40028 preview

CVE-2023-40028

GitHubstp1t/cve-2023-40028

Python exploit for CVE-2023-40028 enabling authenticated arbitrary file read on Ghost CMS, designed for educational use and HTB machines.

educationexploitationpenetration-testing+2
19 months ago
CVE-2023-40028 preview

CVE-2023-40028

GitHubbuutt3rf1y/cve-2023-40028

POC for CVE-2023-40028: Ghost CMS Arbitrary File Read

exploitationinformation-gatheringpenetration-testing+2
1 year ago
CVE-2023-40028 preview

CVE-2023-40028

GitHubsyogod/cve-2023-40028

CVE-2023-40028 is a security vulnerability affecting Ghost CMS versions prior to 5.59.1.

educationexploitationpenetration-testing+2
1 year ago
Ghost-CMS-Exploit preview

Ghost-CMS-Exploit

GitHubgl1tch0x1/ghost-cms-exploit

Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…

exploitationpassword-attackspayload-generation+4
1 year ago
CVE-2023-40028 preview

CVE-2023-40028

GitHubrehan6658/cve-2023-40028

Python exploit for CVE-2023-40028 in Ghost CMS, enabling arbitrary file read via symlink abuse in ZIP uploads. Includes automated cleanup.

educationexploitationpenetration-testing+2
1 year ago
CVE-2024-23724 preview

CVE-2024-23724

GitHubyoussefdds/cve-2024-23724

Proof-of-concept exploit for CVE-2024-23724 in Ghost CMS, demonstrating privilege escalation via malicious SVG profile image upload.

ctfeducationexploitation+3
1 year ago
Ghost-5.58-Arbitrary-File-Read-CVE-2023-40028 preview

Ghost-5.58-Arbitrary-File-Read-CVE-2023-40028

GitHub0xdtc/ghost-5.58-arbitrary-file-read-cve-2023-40028

CVE-2023-40028 affects Ghost, an open source content management system, where versions prior to 5.59.1 allow authenticated users to upload files that…

educationexploitationpenetration-testing+3
131 year ago
Previous12Next