
CVE-2011-2523
 rushikesh-a-bhujbal/cve-2011-2523
From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.
educationexploitationlabs-practice+4
rushikesh-a-bhujbal/cve-2011-2523From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.
 0xs4n4tg/cve-2025-47812
CVE-2025-47812 Poc for wingdata HTB
 zemarkhos/cve-2026-44403-wingftp-v8.1.2-poc-exploit
CVE-2026-44403-WingFTP-v8.1.2-POC-Exploit
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 0xjuarez/cve-2025-47812
Exploit and scanner for CVE-2025-47812 targeting Wing FTP Server unauthenticated remote code execution, supporting single-target, mass scanning,…
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3
 d3vn0mi/cve-2025-471812-poc
Python PoC for CVE-2025-47812, unauthenticated RCE in Wing FTP Server <= 7.4.3 via NULL-byte Lua injection into session files
 shisones/cve-2025-31161
A proof of concept for CVE-2025-31161, using mangled HTTP header to perform unauthenticated impersonation of any user in Crush FTP server.
 estebanzarate/cve-2025-47812-wing-ftp-server-7.4.3-unauthenticated-rce-poc
Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…
 shadowgit30/cve-2025-47812
CVE-2025-47812 POC
 havbay/cve-2025-47812-poc
Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…
 matesz44/cve-2025-47812
CVE-2025-47812: Wing FTP Server 7.4.3 UnauthN RCE in sh
 kre80r/cve-2025-34299-lab
Docker test environment for CVE-2025-34299 - Monsta FTP Pre-Auth RCE vulnerability
 rxerium/cve-2025-34299
Detection for CVE-2025-34299
 donmedfor/cve-2015-3306
Python PoC exploit for CVE-2015-3306 ProFTPD directory traversal. Copies files and drops a PHP backdoor into webroot for remote command execution via…
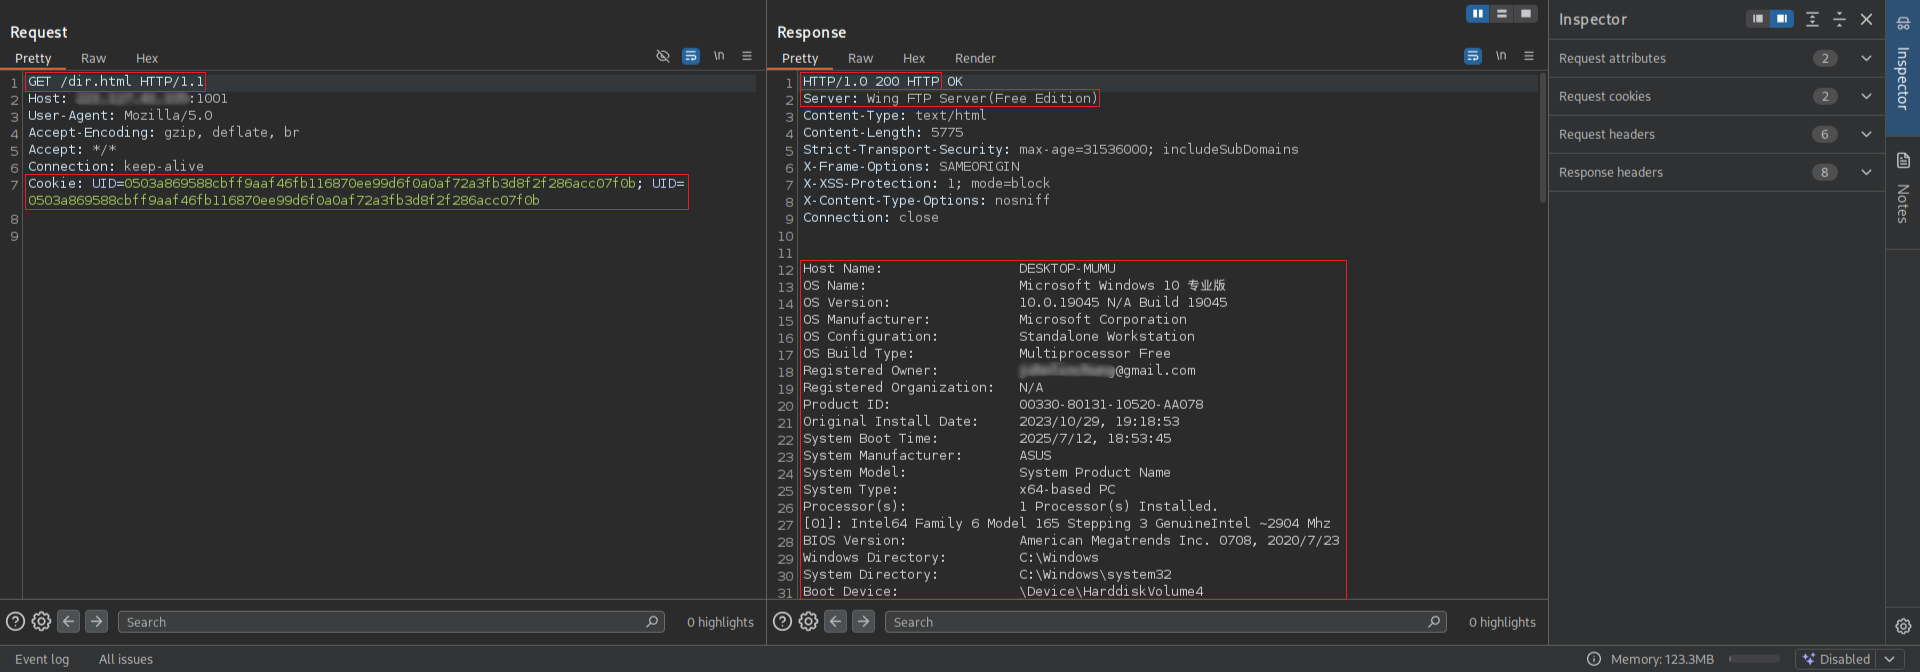 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 dkstar11q/blackash-cve-2025-47812
CVE-2025-47812
 blindma1den/cve-2025-47812
Unauthenticated remote code execution exploit for Wing FTP Server < 7.4.4, enabling command execution and reverse shells via Lua injection in session…