
CVE-2026-16348
 slagzz/cve-2026-16348
TP-Link Archer BE800 V1 — VPN Key Injection RCE
exploitationpenetration-testingred-teaming+2
slagzz/cve-2026-16348TP-Link Archer BE800 V1 — VPN Key Injection RCE
 slagzz/cve-2026-9254
TP-Link Archer BE800 V1 — Parental Control LAN RCE
 totekuh/cve-2026-75616
Proof-of-concept exploit for authenticated OS command injection in TP-Link Archer C20 v6 web management interface, executing root commands via BPA…
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 rhestcorp/tp-l-nk-sizma-explo-t
TP-Link Router Authenticated RCE Exploit (CVE-2022-30075) Bu araç, TP-Link Archer AX50 ve bazı diğer TP-Link router modellerinde bulunan…
 nastycrow/cve-2025-27893
Detailed disclosure of CVE-2025-27893: an authenticated web parameter manipulation vulnerability in Archer Platform 6.x allowing unauthorized…
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection
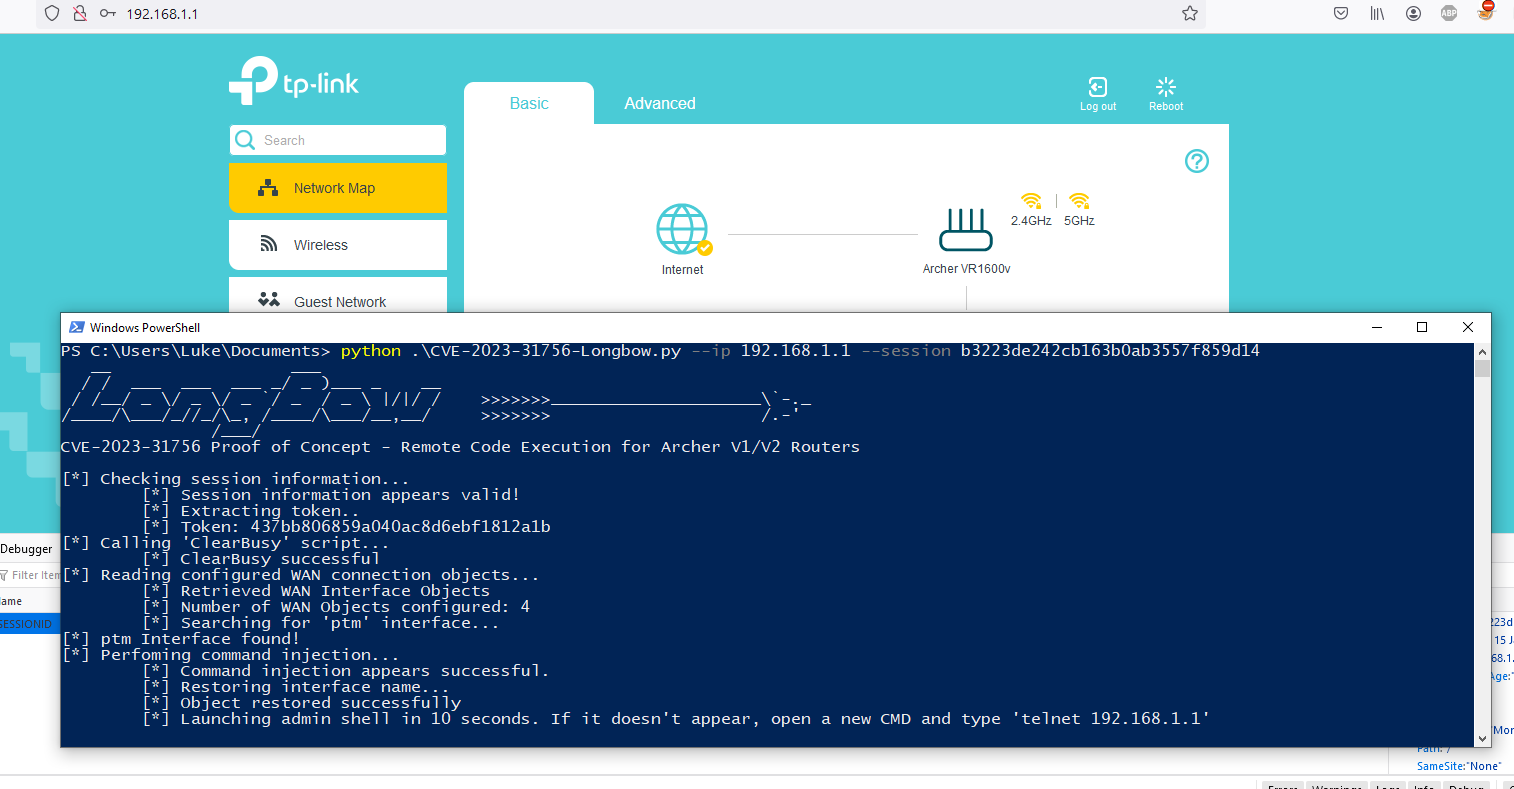 stanleyjobsonau/longbow
CVE-2023-31756 Proof of Concept - Remote Code Execution for Archer V1/V2 Routers
 werwolfz/cve-2023-1389
TP-Link Archer AX21 - Unauthenticated Command Injection [Loader]
 voyag3r-security/cve-2023-1389
Proof-of-concept scripts for CVE-2023-1389, an unauthenticated command injection in TP-Link Archer AX21, providing file transfer and reverse shell…
 aaronsvk/cve-2022-30075
Tp-Link Archer AX50 Authenticated RCE (CVE-2022-30075)
 full-disclosure/cve-2021-44827
Proof-of-concept exploit for authenticated remote code execution (CVE-2021-44827) targeting TP-Link Archer C20i routers. Provides post-exploitation…
 jackdoan/tp-link-archerc5-rce
CVE-2018-19537
 vakzz/tplink-cve-2017-11519
POC for TP-Link Archer C9 - Admin Password Reset and RCE (CVE-2017-11519)
 ayushman4/tp-link-archer-cr-700-xss-exploit
Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)