CVE-2026-66749-Unchecked-Room-Lookup-Leads-to-Server-Crash-Let-s-Chat-

Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)

Security Advisory: Unchecked Room Lookup Leads to Server Crash (Let's Chat)

This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…

The minor methodology for room: https://tryhackme.com/room/n8ncve202568613

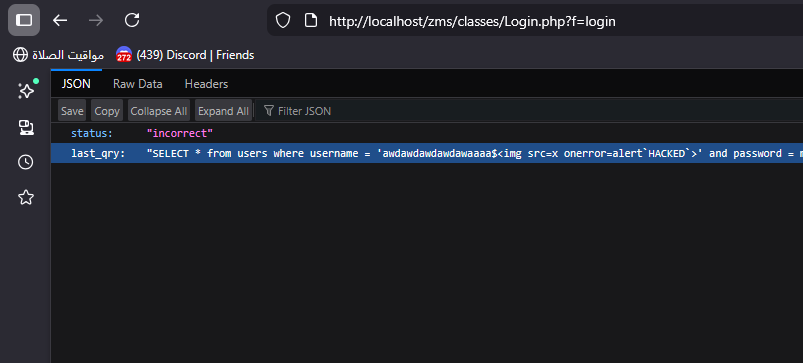
Sourcecodester Zoo Management System v1.0 is vulnerable to Cross Site Scripting (XSS) in /classes/Login.php Due to invalid Content-Type

Time-Based Blind SQL Injection tool for MySQL - CVE-2019-9053

Practice POC scripting in Tryhackme’s intro poc scripting room (For Linux)

Python-based exploit for Hotel Druid 3.0.3 Remote Code Execution (CVE-2022-22909). Injects PHP payloads via room names to achieve command execution…

Proof-of-concept exploit for CVE-2024-23742 in Loom for macOS. Validates vulnerability and injects arbitrary code via RunAsNode settings to gain a…

Proof-of-concept demonstrating incorrect access control in Unifiedtransform v2.0, allowing teachers to modify section details. Includes step-by-step…

Zoo Management System 1.0 - Stored Cross-Site-Scripting (XSS)

Zoo Management System 1.0 - Reflected Cross-Site-Scripting (XSS)

Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…

Proof-of-concept demonstrating stored cross-site scripting (XSS) in Minical 1.0.0 via the Room Status edit note feature, with step-by-step…

Detailed writeup of CVE-2021-41773 Apache path traversal and RCE exploitation, with step-by-step commands and root cause analysis from a TryHackMe…

This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…

Exploits CVE-2012-2982 in Webmin with a Rust PoC that delivers a configurable TCP reverse shell and optional Netcat listener.

TryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification

A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig