

blindxss-lite
 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
command-and-controldata-exfiltrationinformation-gathering+7
3
yuyudhn/blindxss-liteA lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 ch35h1r3c47/cve-2026-23723-poc
This is a lightweight Python helper script designed to automate the generation of sqlmap-compatible PoC files for the authenticated error-based SQL…
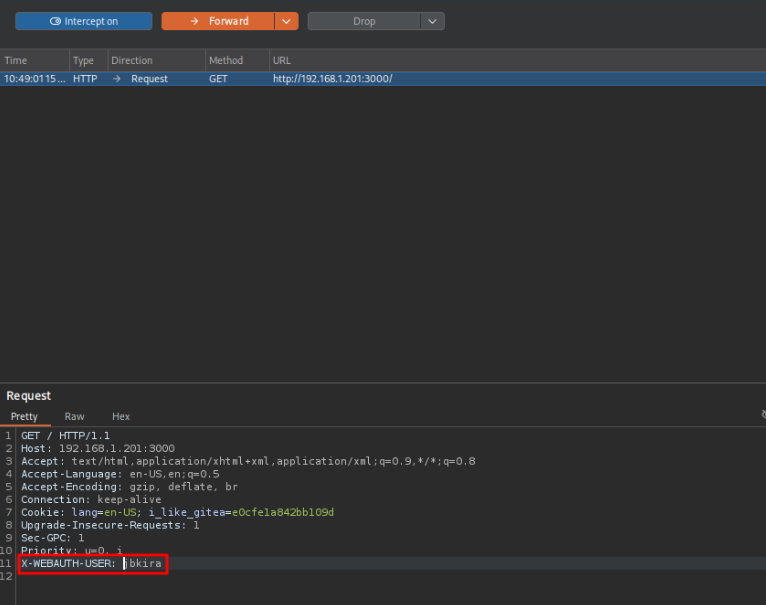 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 jenderal92/zimbra-valid-login-checker
Lightweight Python script to test username/password combinations against Zimbra webmail login pages for security assessments and password auditing.
 r4j3sh-com/cve-2025-55182
Lightweight Go toolkit plus a Dockerized Next.js lab to explore and triage CVE-2025-55182.
 sangleshubham/react-security-cve-2025-55182-exploit
NodeJS-based exploit script and scanner for the React Server Components "React2Shell" vulnerability (CVE-2025-55182).
 j4ck3lsyn-gen2/cve-2026-63030-wp2r00t
A fully red-team(offensive security) weaponized variant of wp2shell, built for authorized penetration testing & educational purposes.
 mrsol0/cve-2025-55182-terminal
This is a POC for testing your projects that are vulnerable to CVE-2025-55182 with a terminal and ability to scan a list
 z3usx01/cve-2025-0054
Lightweight Python scanner for detecting stored XSS (CVE-2025-0054) in SAP NetWeaver Java. Submits customizable payloads and checks for script…
 furkankayapinar/reactnext2shell
CVE-2025-55182 and CVE-2025-66478
 edsonjt81/cve-2023-22515-scan.
Lightweight scanner for CVE-2023-22515 that detects vulnerable Atlassian Confluence instances by probing the /server-info.action endpoint and…
 grp-ops/react2shell
Lightweight scanner and Nuclei templates for identifying React and Next.js deserialization RCEs (CVE-2025-55182 / CVE-2025-66478).
 dinosn/cve-2021-2109
Lightweight Python scanner for CVE-2021-2109 that checks target URLs for the specific vulnerability with minimal dependencies.
 fufu-byte/cve-2024-46506
Standalone Python exploit for CVE-2024-46506, providing a lightweight, portable remote code execution module without requiring the Metasploit…
 epicosy/ratpack-1
Lightweight Java toolkit for building high-performance web applications, with a focus on exploiting CVE-2019-17513 for security testing and…
 deathvu/cve-2024-9474
Proof-of-concept exploit for CVE-2024-9474 targeting Palo Alto PAN-OS. Lightweight Python script for testing vulnerability against specified URLs.
 cybersecplayground/cve-2024-48887-fortiswitch-exploit
a lightweight JavaScript snippet showcasing how unauthorized password changes can be triggered on vulnerable Fortinet FortiSwitch GUI endpoints.