
cve-2026-85706
 0xenesbayram/cve-2026-85706
Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via parser…
educationexploitationlabs-practice+4
0xenesbayram/cve-2026-85706Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via parser…
 shirouuu/gitea-template-sync-path-traversal-privilege-escalation-cve-2026-38526-
PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 tori-tech/mandating-honeypots-project
This repository conducts security audits on digital identity verification systems, identifies vulnerabilities through whitepapers and technical POCs,…
 shijx1024/cve-2024-31666
Documents CVE-2024-31666, a remote code execution vulnerability in Flusity-CMS v2.33 via the edit_addon_post.php component, including impact and…
 brigadeops32/cve-2026-85706
Python PoC exploiting CVE-2026-85706, an unauthenticated path traversal and arbitrary file read in GitLab CE/EE via the create-commit endpoint, with…
 ledksv/interpreter-hackthebox
HackTheBox Interpreter walkthrough: CVE-2023-43208 Mirth Connect deserialization RCE, PBKDF2 hash cracking, and eval() injection privilege escalation…
 ledksv/cctv
HackTheBox CCTV walkthrough chaining CVE-2024-51482 ZoneMinder SQL injection, bcrypt hash cracking, and CVE-2025-60787 motionEye RCE to obtain root.
 ledksv/devarea
HackTheBox DevArea walkthrough chaining CVE-2022-46364 Apache CXF SSRF, CVE-2025-54123 Hoverfly RCE, and SUID bash hijacking for root escalation.
 ledksv/monitorsfour
HackTheBox MonitorsFour walkthrough covering credential leak, CVE-2025-24367 Cacti RCE, and CVE-2025-9074 Docker Desktop API container escape to root.
 ledksv/pterodactyl
HackTheBox Pterodactyl walkthrough chaining CVE-2025-49132 path traversal, hash cracking, and CVE-2025-6018/6019 PAM and XFS race for root.
 ledksv/wingdata
HackTheBox Wingdata walkthrough covering WingFTP CVE-2025-47812 command injection for initial access and tar path traversal sudo privilege escalation…
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 sajjadsiam/cve-2026-82222-poc
Proof-of-concept and local DDEV lab for CVE-2026-82222, an unauthenticated PHP object injection to RCE in the GiveWP WordPress plugin, with cURL and…
 0xlyvio/cve-2026-85706-poc-exploit-gitlab
PoC exploit and writeup for CVE-2026-85706, an unauthenticated arbitrary local file read in GitLab CE/EE via Workhorse path-encoding bypass.
 infernosalex/cve-2026-33439-python-poc
Python PoC for CVE-2026-33439, an OpenAM pre-authentication RCE via jato.clientSession deserialization
 harshrajsinghania/cotonti-commentswidget-poc
Safe local proof of concept for the Cotonti CommentsWidget PHP object injection vulnerability (CAN-2026-2035973 / CVE-2026-71294).
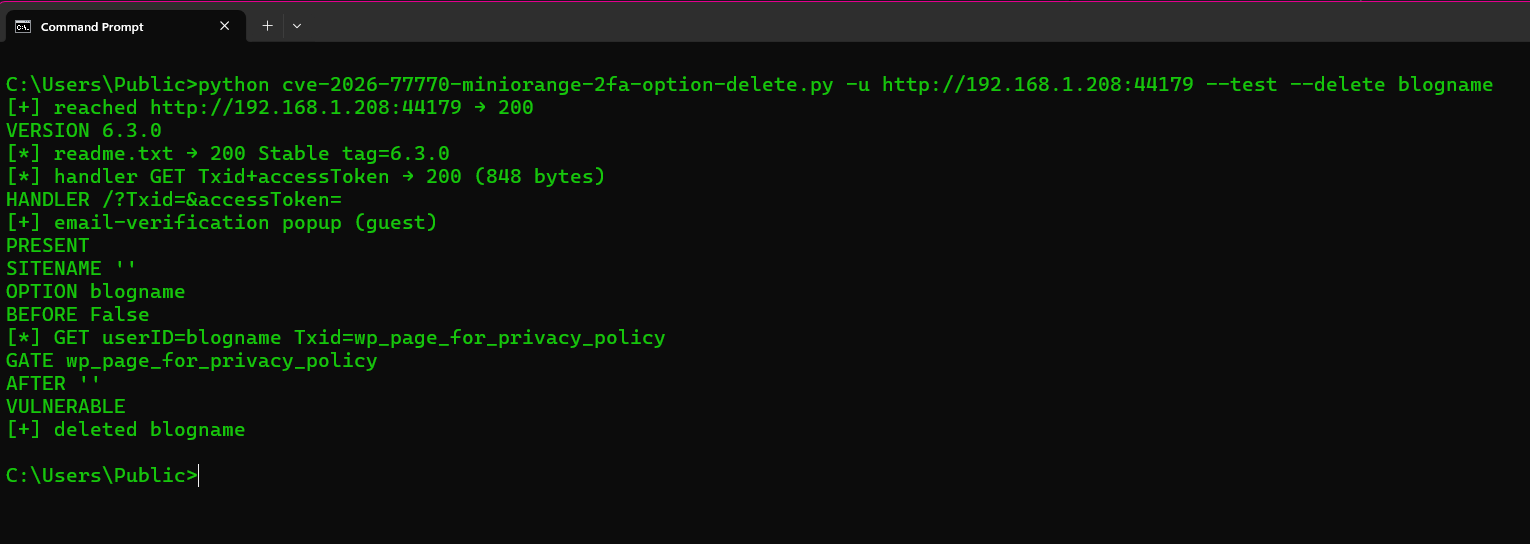 cflowsec/cve-2026-77770
Python PoC for CVE-2026-77770, an unauthenticated arbitrary WordPress option deletion flaw in the miniOrange 2FA plugin (<= 6.3.0) via the…