
openhands-disclosure
 edoardottt/openhands-disclosure
Multiple Command Injection vulnerabilities in openhands <0.62.0 allow an attacker to run arbitrary system commands.
code-analysisstatic-analysisvulnerability-analysis+1
4
edoardottt/openhands-disclosureMultiple Command Injection vulnerabilities in openhands <0.62.0 allow an attacker to run arbitrary system commands.
 oscerd/cve-2026-85313
Runnable Spring Boot proof-of-concept reproducing CVE-2026-85313, where Apache Camel camel-jetty enableCORS reflects any origin with credentials,…
 abraxas/pfsense-bsnmpd-conf
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - bsnmpd syslocation
 abraxas/pfsense-cp-maxprocperip
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Config injection - CP maxprocperip nginx
 abraxas/pfsense-limiter-aqm
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - limiter AQM newline
 abraxas/pfsense-ntp-gps-fudge
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - NTP GPS/PPS fudge
 abraxas/opnsense-ntp-gps-fudge
OPNsense 26.7.6 - High - Remote - Config line injection - NTP GPS fudge
 abraxas/opnsense-tunables-loader
OPNsense 26.7.6 - High - Remote - Config line injection - tunables loader
 abraxas/spark-connect-copy-local
Apache Spark 4.2.0 - High - Remote - File write - Connect session SET copyFromLocalToFs.allowDestLocal
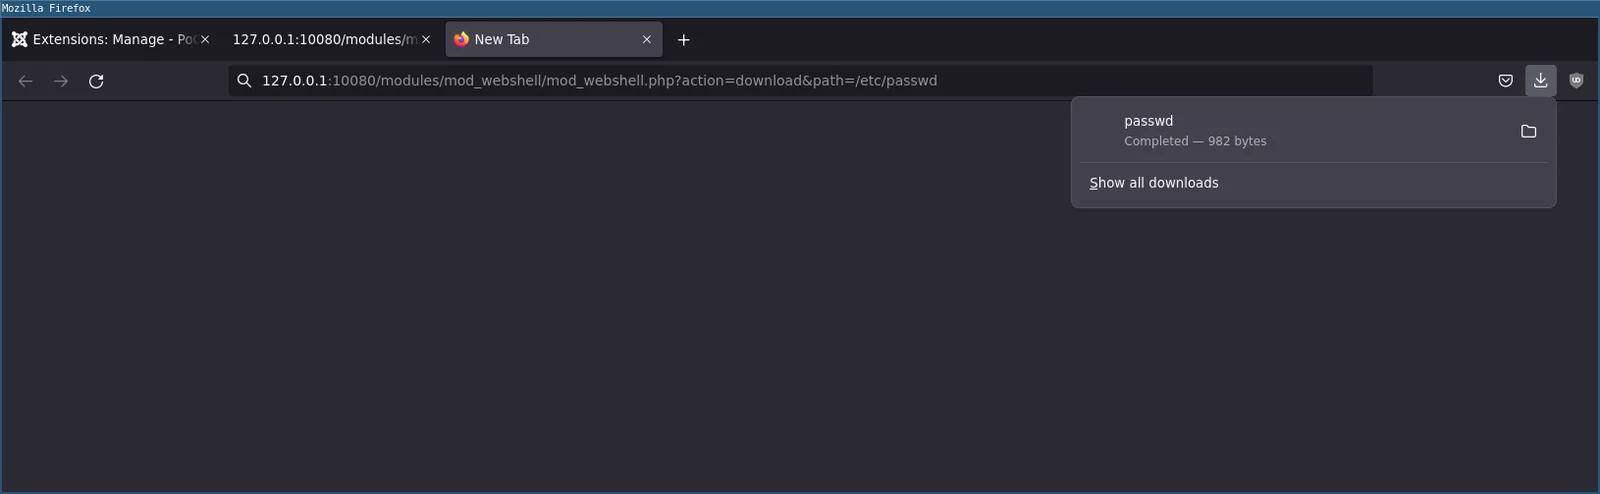 p0dalirius/joomla-webshell-plugin
A webshell plugin and interactive shell for pentesting a Joomla website.
 y198nt/nginx-chain-rift-poolslip
ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…
 yym8538/cve-2026-20896
Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
 svtagan/wp-cve-2026-87902
Read-only PHP diagnostic script that checks WordPress version, core checksums, extra PHP files, and known plugin paths for CVE-2026-87902 exposure…
 g4sp4rcs/cve-2019-11707-from-an-ionmonkey-type-confusion-to-system-
Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 samy4samy/cve-2025-59287-wsus-2
Proof-of-concept exploit for CVE-2025-59287, a remote code execution vulnerability in Microsoft WSUS via unsafe deserialization. Sends crafted SOAP…
 m4rgs/cve-2025-5947_exploit
An mini exploit for the Service Finder -Bookings plugin WP