

CVE-2026-0073
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
android-securityauthenticationcryptography+5
umarrehmansiddiqui/cve-2026-0073Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 horkimhab/cve-2026-109618-619
Proof-of-concept code for CVE-2026-109618 and CVE-2026-109619 (php2shell bypass), packaged for authorized lab reproduction and vulnerability research.
 horkimhab/cve-2026-wordpress
Educational CVE proof-of-concept collection targeting WordPress vulnerabilities, with setup scripts and lab guidance for authorized security research…
 horkimhab/cve-2026-59265
Proof-of-concept and research material for CVE-2026-59265, a LibreOffice and OpenOffice vulnerability, intended for authorized lab testing and…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 isec-tugraz/file-notification-attacks
Research artifacts for file-notification side-channel attacks on Linux, Windows, and macOS, demonstrating inotify/FSEvents leakage, keystroke timing,…
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 horkimhab/cve-2026-19975
Proof-of-concept and research repository for CVE-2026-19975 in Azuriom, with setup instructions and a linked technical writeup for authorized…
 funfactor1/cve-2026-82090-18-years-all-versions-cvss-9.2-critical-the-pocket-forever-day
CVE-2026-82090 · CVSS 9.2 CRITICAL · 0-click stored XSS in Mozilla Pocket — all versions (v0 → v8.33.0.0) · 18-year forever-day · no patch · MITRE…
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 horkimhab/cve-2026-13181-cve-2026-13182-cve-2026-13183-cve-2026-13184
Educational proof-of-concept for Telerik padding oracle vulnerabilities (CVE-2026-13181-184) with scripts for authorized security testing and…
 mobilehackinglab/cve-2026-28576-poc
Educational proof-of-concept demonstrating a SQL injection vulnerability in Android 17's Contacts Provider, allowing a zero-permission app to…
 horkimhab/cve-2023-27350-cve-2023-27351
Educational proof-of-concept for PaperCut pre-auth RCE chain (CVE-2023-27350, CVE-2023-27351) with setup scripts and authorized testing guidance.
 adityatelange/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 jaf0rk/cve-2026-5281-cve-2026-11057-fullchain
Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…
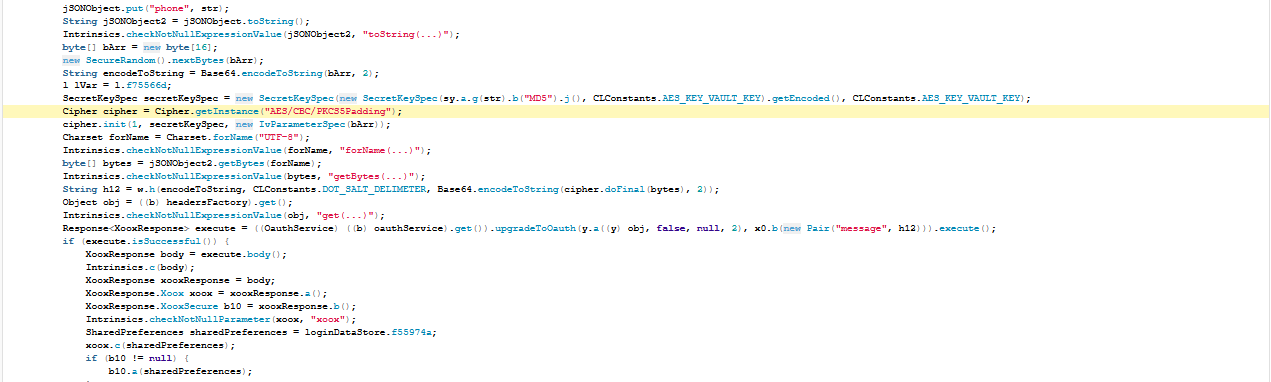 honestcorrupt/meesho-android-improper-encryption-cve-2026-5682
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…