
CVE-2019-9053
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
exploitationpassword-crackingpenetration-testing+3
11
4nner/cve-2019-9053Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 oieua/cve-2026-33017
Bash proof-of-concept exploit for CVE-2026-33017 in Langflow, triggering a reverse shell callback to a netcat listener.
 maximilianomeyer/cve-2026-33017
Proof-of-concept implementation for CVE-2026-33017, demonstrating the vulnerability for authorized security testing and research.
 ac8999/cve-2025-27636-rce-in-apache-camel
Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.
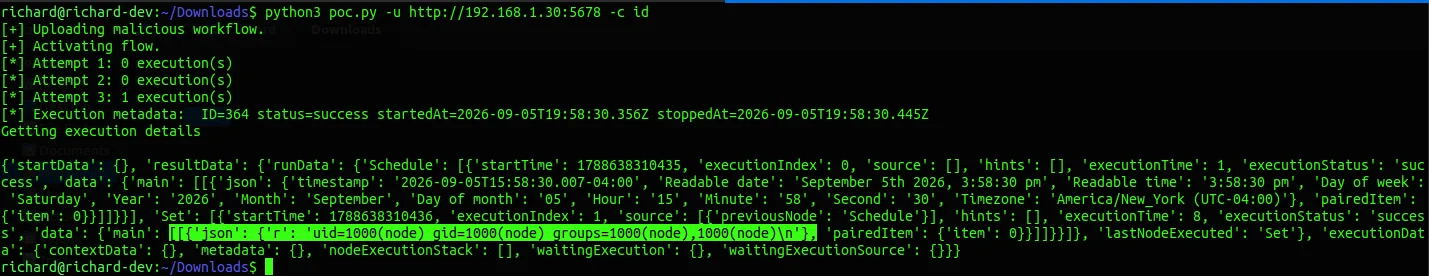 rmhowe425/poc-cve-2025-68613
Proof-of-concept exploit for CVE-2025-68613, an authenticated remote code execution vulnerability in N8N. Executes arbitrary bash commands on…
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
 shubham0d/cve-2021-30853
Proof-of-concept script that demonstrates bypassing macOS Gatekeeper, notarization, and XProtect checks by exploiting CVE-2021-30853, allowing…
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 kanitan/log4j2-web-vulnerable
A vulnerable web app for log4j2 RCE(CVE-2021-44228) exploit test.
 diogolourencodev/middleforce
Simple script to attempt a Bypass on a server possibly vulnerable to CVE-2025-29927 (Next.js Middleware)
 desultory/cve-2026-31431
Demonstrates CVE-2026-31431 by poisoning the cache for a target file with attacker-controlled payload bytes, illustrating a web cache poisoning…
 darkpills/cve-2021-24307-all-in-one-seo-pack-admin-rce
Proof-of-concept exploit for CVE-2021-24307, an authenticated admin RCE in All in One SEO Pack <= 4.1.0.1 via PHP unserialization, enabling arbitrary…
 ctzisme/cve-2026-23744
Proof-of-concept exploit for CVE-2026-23744, demonstrating unauthenticated remote code execution in MCPJam Inspector versions up to 1.4.2 via crafted…
 yunfeige18/cve-2026-1281-cve-2026-1340-ivanti-epmm-rce
A simple demo application that shows how to reproduce the Ivanti EPMM pre-auth RCE vulnerability (CVE-2026-1281 / CVE-2026-1340) for educational and…
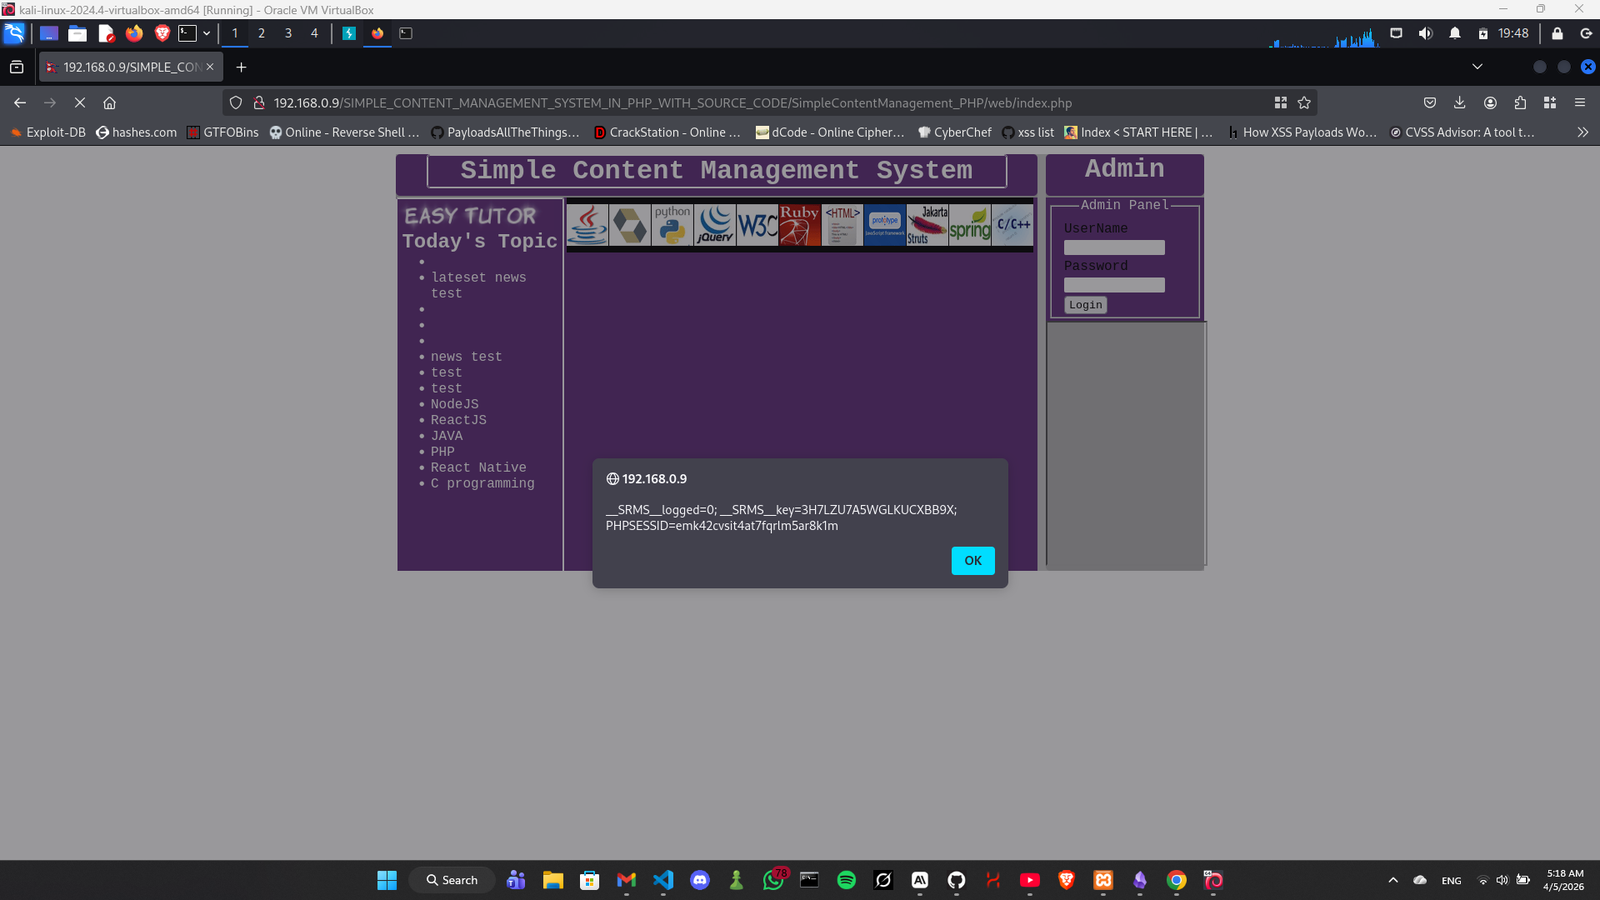 xmyronn/cve-2026-6184-stored-xss
Proof-of-concept for a stored XSS vulnerability in Simple Content Management System PHP, demonstrating session cookie theft via unsanitized News…
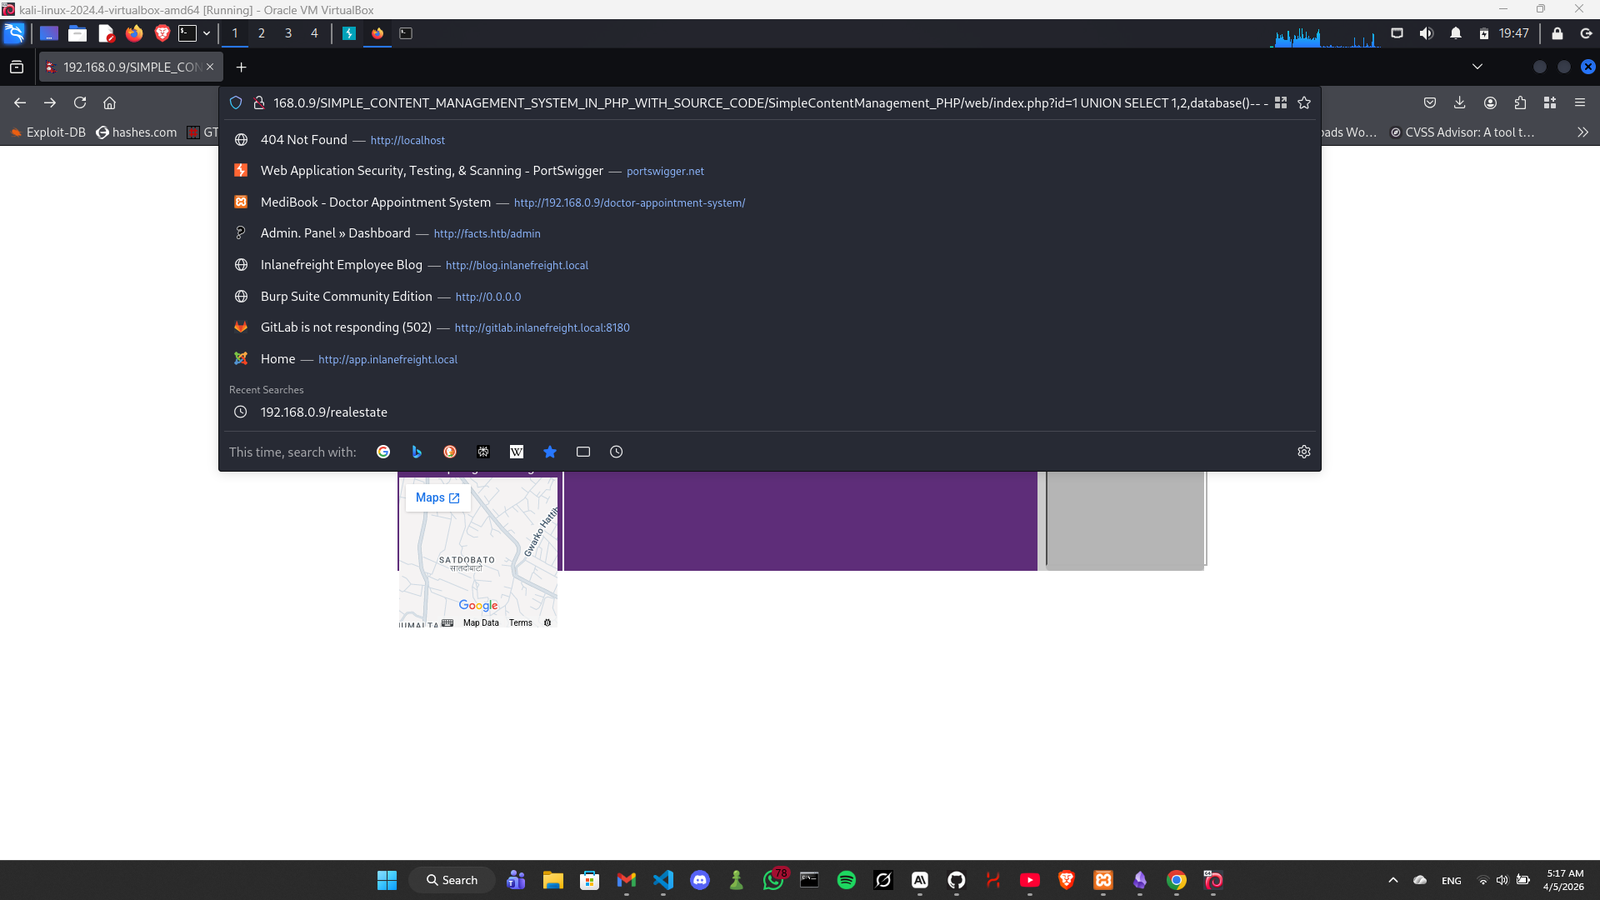 xmyronn/cve-2026-6183-sqli
Proof-of-concept exploit for SQL injection in Simple Content Management System PHP, demonstrating UNION-based data extraction via the id parameter in…
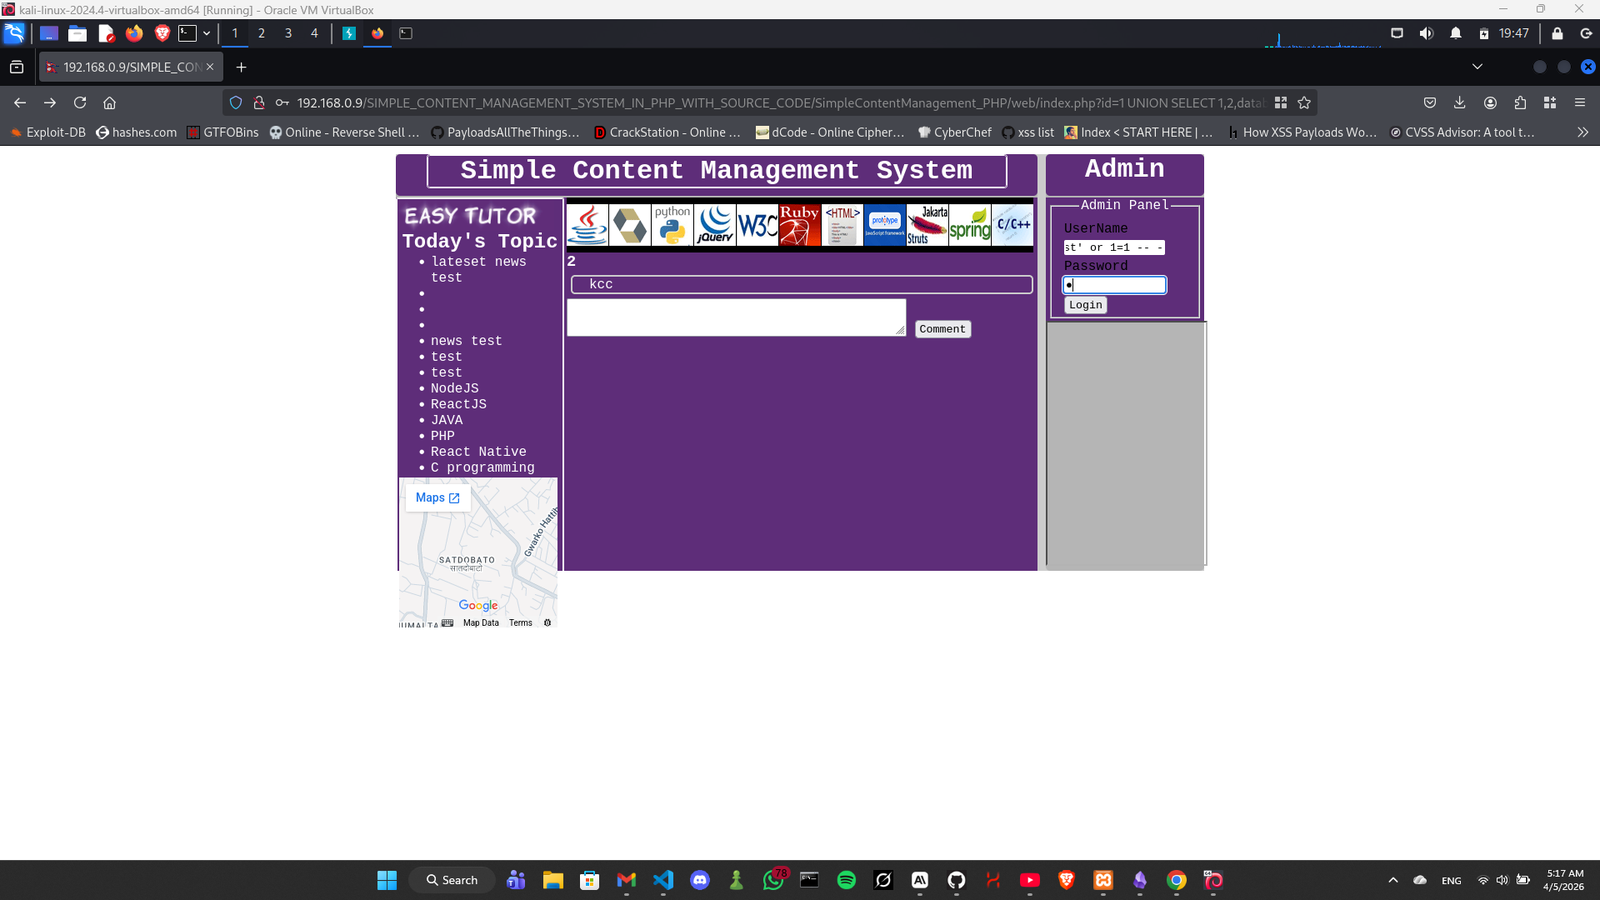 xmyronn/cve-2026-6182-sqli-auth
Proof-of-concept for SQL injection authentication bypass in Simple Content Management System PHP, allowing unauthenticated attackers to gain admin…
 mister-joe/cve-2021-44593
Public disclosure and writeup of CVE-2021-44593, an unauthenticated SQL injection in Simple College Website leading to arbitrary file upload and…