
CVE-2026-19632
 thejesterrrr/cve-2026-19632
Proof-of-concept code and reproduction details for CVE-2026-19632, demonstrating the vulnerability's trigger conditions and impact.
exploitationvulnerability-analysisweb-application-exploitation
thejesterrrr/cve-2026-19632Proof-of-concept code and reproduction details for CVE-2026-19632, demonstrating the vulnerability's trigger conditions and impact.
 foxcornlab/thc-bloodmiami
AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
 infobyte/ai-pentest-agent
Standalone autonomous AI pentest agent with a plan→act→judge loop, generic skills, destructive-action gate, and swappable LLM providers, plus a…
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 abraxas/moodle-grades-gradeitems
Moodle 5.2.3 - High - Remote - IDOR - core_grades_get_gradeitems lists hidden grade items
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 dragonjar/burpia
Extensión de Burp Suite que incorpora detección pasiva de vulnerabilidades mediante inteligencia artificial.
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
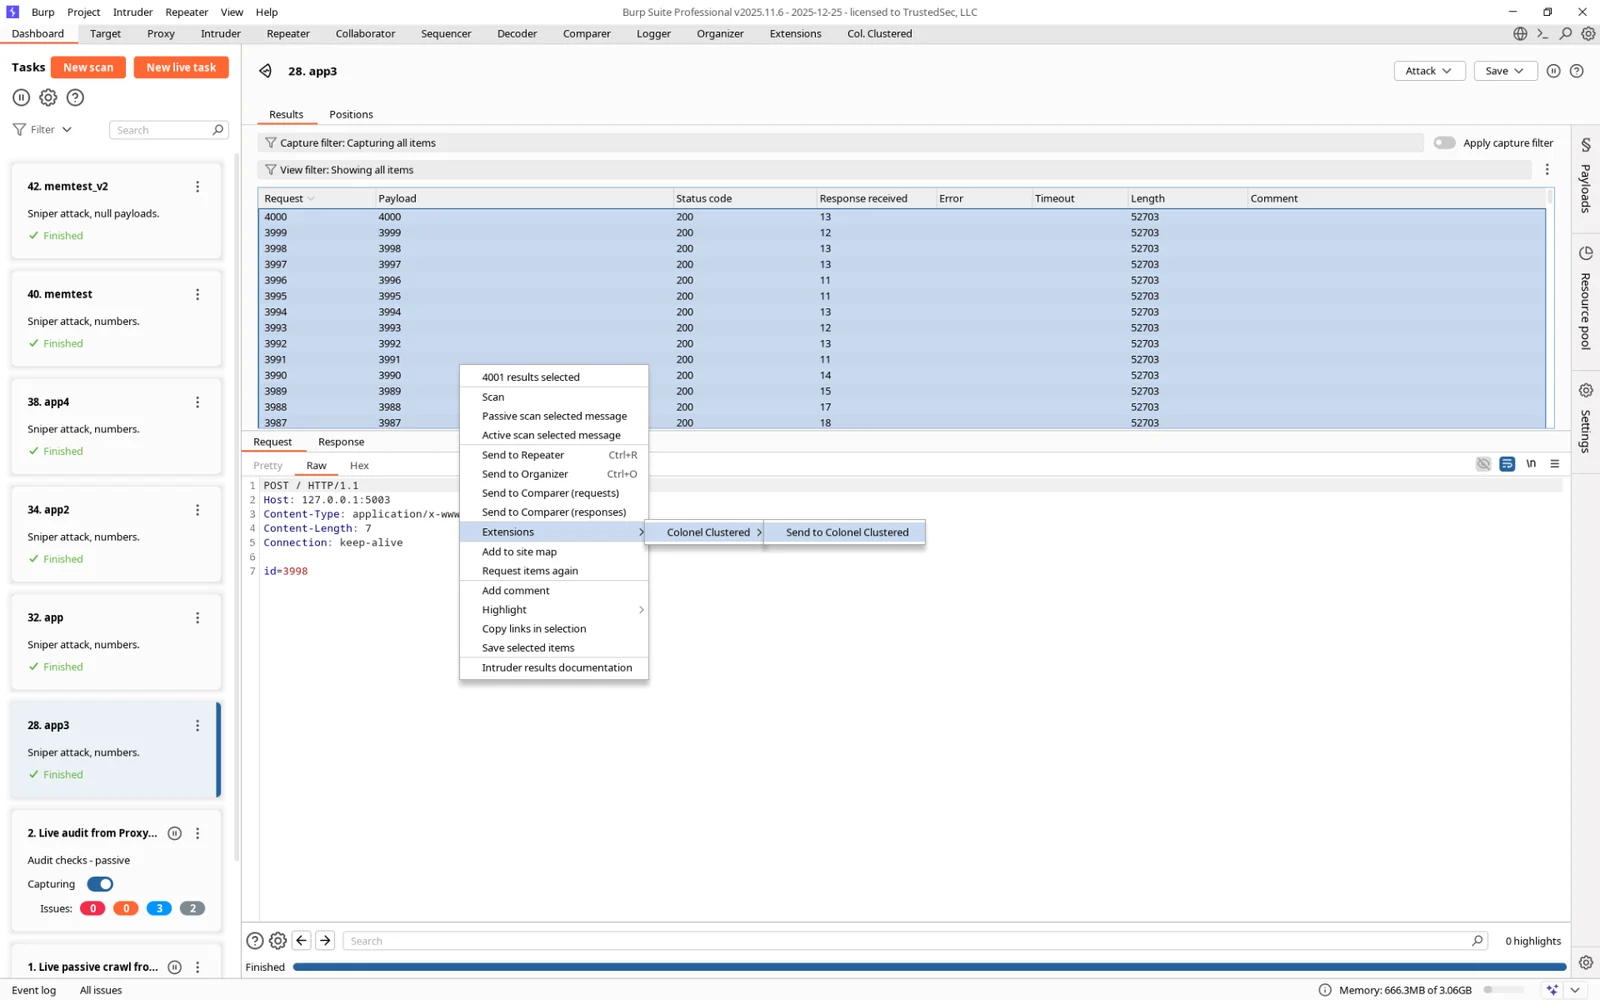 hoodoer/colonelclustered
A Java Burp Plugin that performs text clustering on responses to identify outliers/groups based on the actual content of the server responses, say…
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
 d0ge/xsw
XML Signature Wrapping Burp Suite Extensions
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 bombobombone/cve-2026-103442
Local proof-of-concept and sanitized report for CVE-2026-103442, a PHP object injection in MediaWiki CentralAuth's merge-session handling that can…
 bombobombone/cve-2026-103437
Local proof-of-concept and sanitized report for CVE-2026-103437, a canonical URL XSS in MediaWiki ReadingLists triggered via crafted import links.