
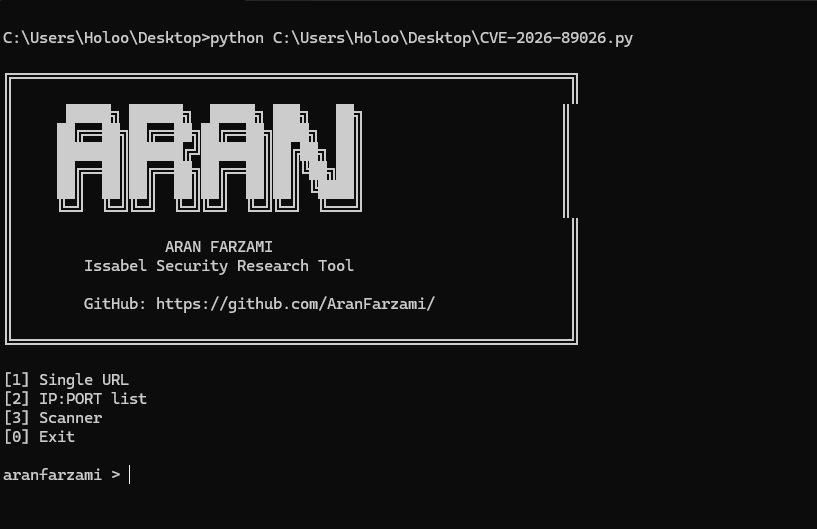
CVE-2026-89026
 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
authenticationexploitationpenetration-testing+5
1
aranfarzami/cve-2026-89026PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 horkimhab/cve-2026-19975
Proof-of-concept and research repository for CVE-2026-19975 in Azuriom, with setup instructions and a linked technical writeup for authorized…
 harshrajsinghania/cotonti-commentswidget-poc
Safe local proof of concept for the Cotonti CommentsWidget PHP object injection vulnerability (CAN-2026-2035973 / CVE-2026-71294).
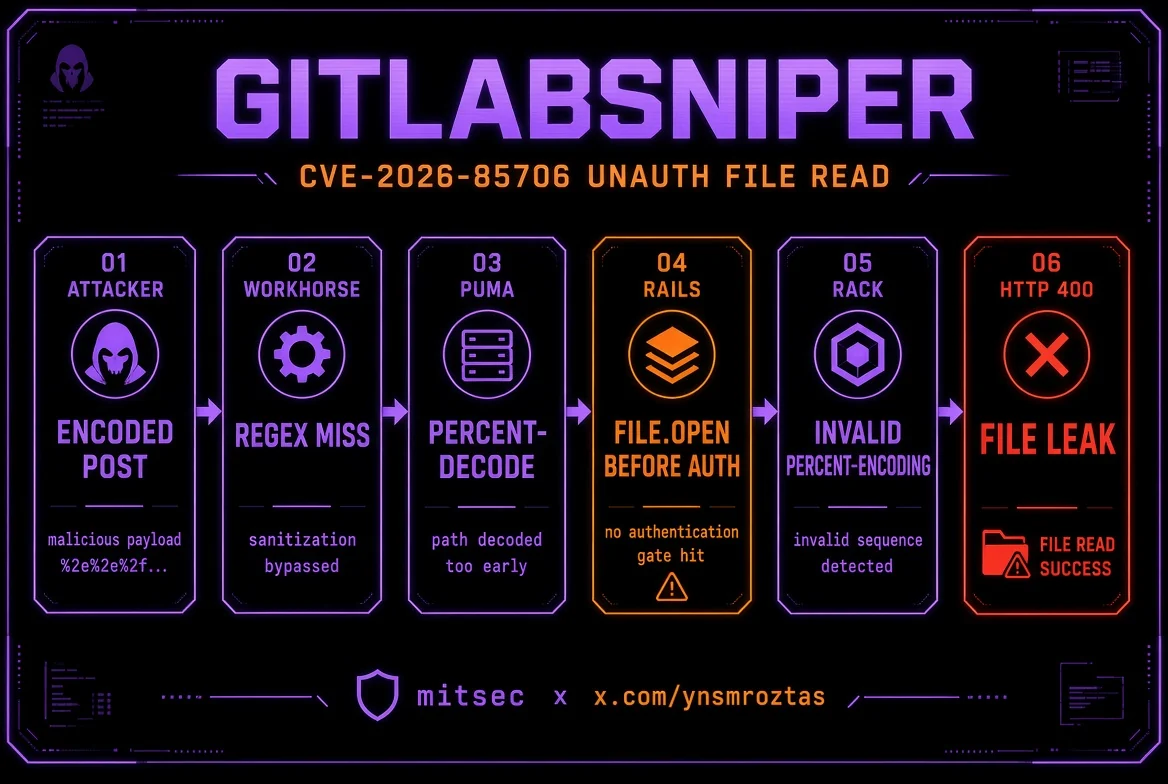 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 squeeze440/code-graph-rag-poc
PoC — symlink following to arbitrary file read/write outside project root in code-graph-rag (GHSA-85gg-2gfq-q95m, CVE-2026-87008, CVSS 7.1).
 horkimhab/cve-2026-13181-cve-2026-13182-cve-2026-13183-cve-2026-13184
Educational proof-of-concept for Telerik padding oracle vulnerabilities (CVE-2026-13181-184) with scripts for authorized security testing and…
 moksh-nfsu/cve-2026-36392
Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…
 horkimhab/cve-chamilo-lms
CVE-2026-61578, CVE-2026-61582, CVE-2026-61583, CVE-2026-61584, CVE-2026-61585, CVE-2026-61587, CVE-2026-61600, CVE-2026-61601, CVE-2026-61602,…
 shihongsu/netsec-cve-2023-4357
Reproduces CVE-2023-4357 in Google Chrome to demonstrate XML/XSLT-based file access bypass, with analysis and proof-of-concept for educational…
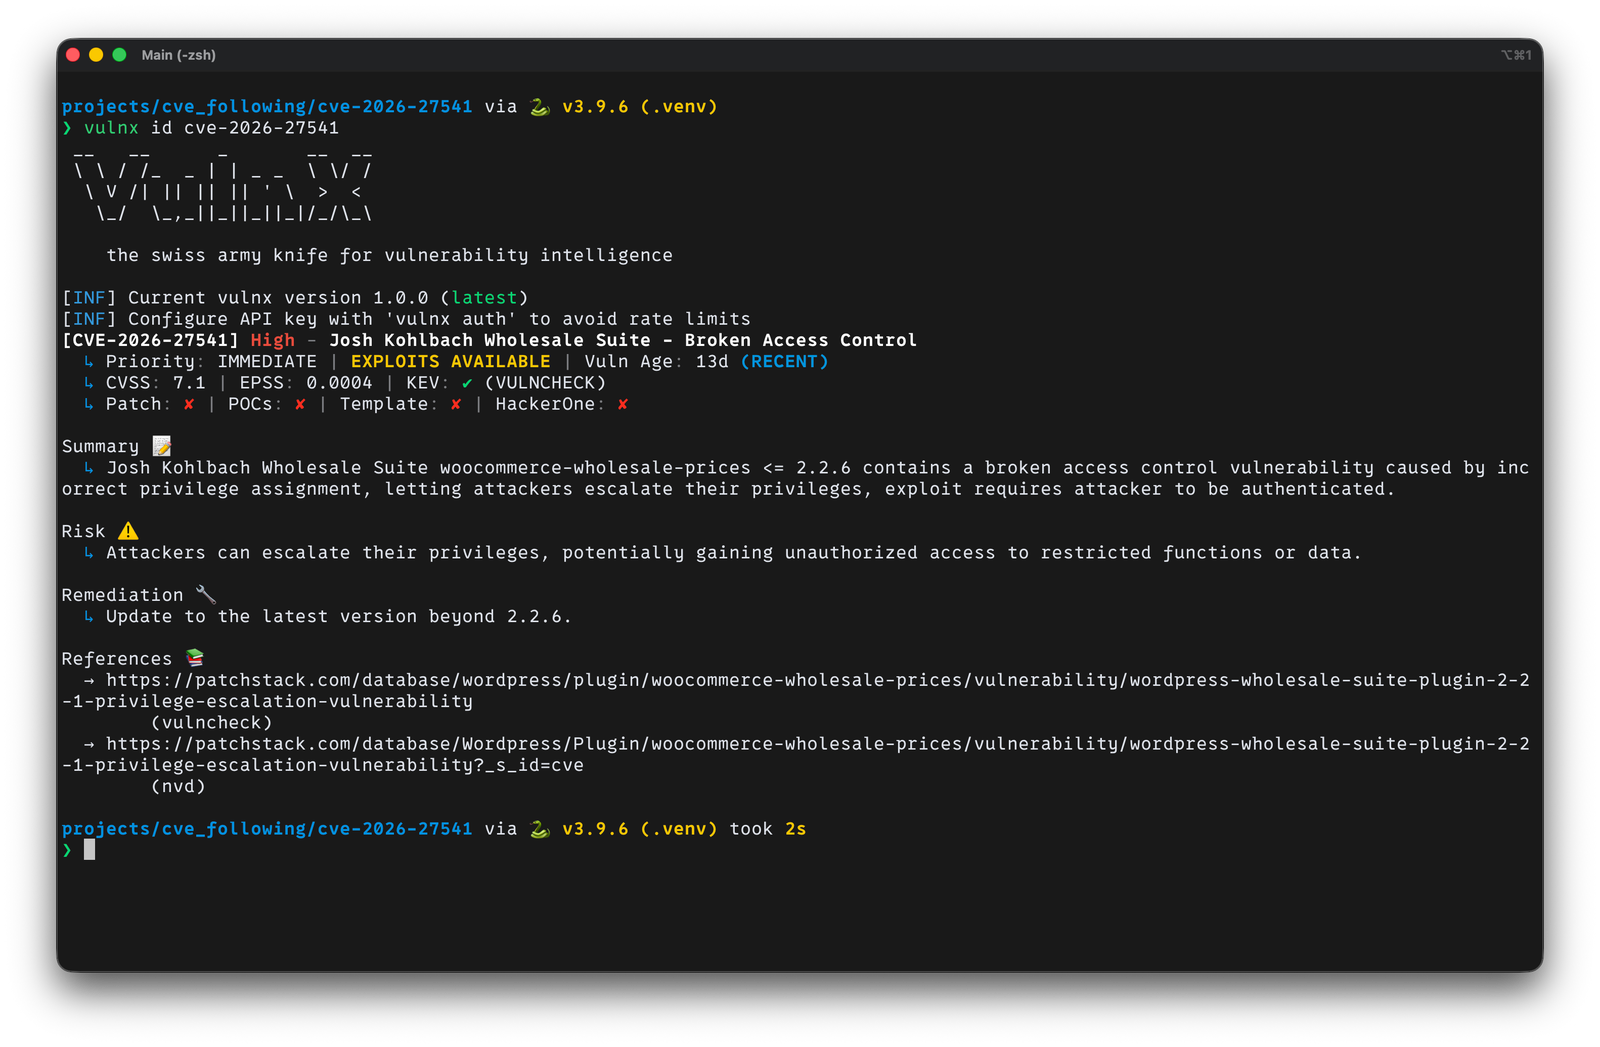 rootdirective-sec/cve-2026-27541-analysis-lab
Docker lab for reproducing CVE-2026-27541, an authenticated privilege escalation in WooCommerce Wholesale Prices. Compares vulnerable and patched…
 horkimhab/cve-2023-27350-cve-2023-27351
Educational proof-of-concept for PaperCut pre-auth RCE chain (CVE-2023-27350, CVE-2023-27351) with setup scripts and authorized testing guidance.
 ipisav/fastjson-cve
Reproduction project for CVE-2026-16723, a critical RCE in fastjson 1.2.68-1.2.83. Demonstrates AutoType bypass, JNDI injection, and TemplatesImpl…
 eqstlab/cve-2026-19478
Proof-of-concept exploit for CVE-2026-19478, an unauthenticated GraphQL injection in GitLab CE/EE allowing arbitrary method invocation and project…
 gh0stuncle/cve-2018-16763_fuel_cms_exploit
A fuel CMS exploit based on Python for RCE mentioned in CVE-2018-16763.
 tansique-17/cve-2025-61456
Public disclosure and proof-of-concept for a reflected XSS vulnerability (CVE-2025-61456) in an e-commerce project, including technical details, CVSS…
 tansique-17/cve-2025-61454
Public disclosure and proof-of-concept for CVE-2025-61454, a reflected XSS vulnerability in E-commerce Project v1.0's search.php, including…