
CVE-2026-97229
 noshadi-sec/cve-2026-97229
Python exploit for CVE-2026-97229, a GitLab CI lint regex RCE. Creates a project, pushes a malicious CI config, triggers the lint endpoint, and…
command-and-controlexploitationpenetration-testing+3
noshadi-sec/cve-2026-97229Python exploit for CVE-2026-97229, a GitLab CI lint regex RCE. Creates a project, pushes a malicious CI config, triggers the lint endpoint, and…
 horkimhab/cve-2026-109618-619
Proof-of-concept code for CVE-2026-109618 and CVE-2026-109619 (php2shell bypass), packaged for authorized lab reproduction and vulnerability research.
 owasp/secretsifter
OWASP Incubator project: detects credentials exposed in browser-delivered content (JavaScript, config responses, live traffic).
 horkimhab/cve-2026-wordpress
Educational CVE proof-of-concept collection targeting WordPress vulnerabilities, with setup scripts and lab guidance for authorized security research…
 horkimhab/cve-2026-59265
Proof-of-concept and research material for CVE-2026-59265, a LibreOffice and OpenOffice vulnerability, intended for authorized lab testing and…
 bombobombone/cve-2026-103437
Local proof-of-concept and sanitized report for CVE-2026-103437, a canonical URL XSS in MediaWiki ReadingLists triggered via crafted import links.
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 horkimhab/cve-2026-81000
Educational CVE-2026-81000 proof-of-concept repository for authorized security research, vulnerability awareness, and controlled lab testing.
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 horkimhab/cve-2026-19975
Proof-of-concept and research repository for CVE-2026-19975 in Azuriom, with setup instructions and a linked technical writeup for authorized…
 harshrajsinghania/cotonti-commentswidget-poc
Safe local proof of concept for the Cotonti CommentsWidget PHP object injection vulnerability (CAN-2026-2035973 / CVE-2026-71294).
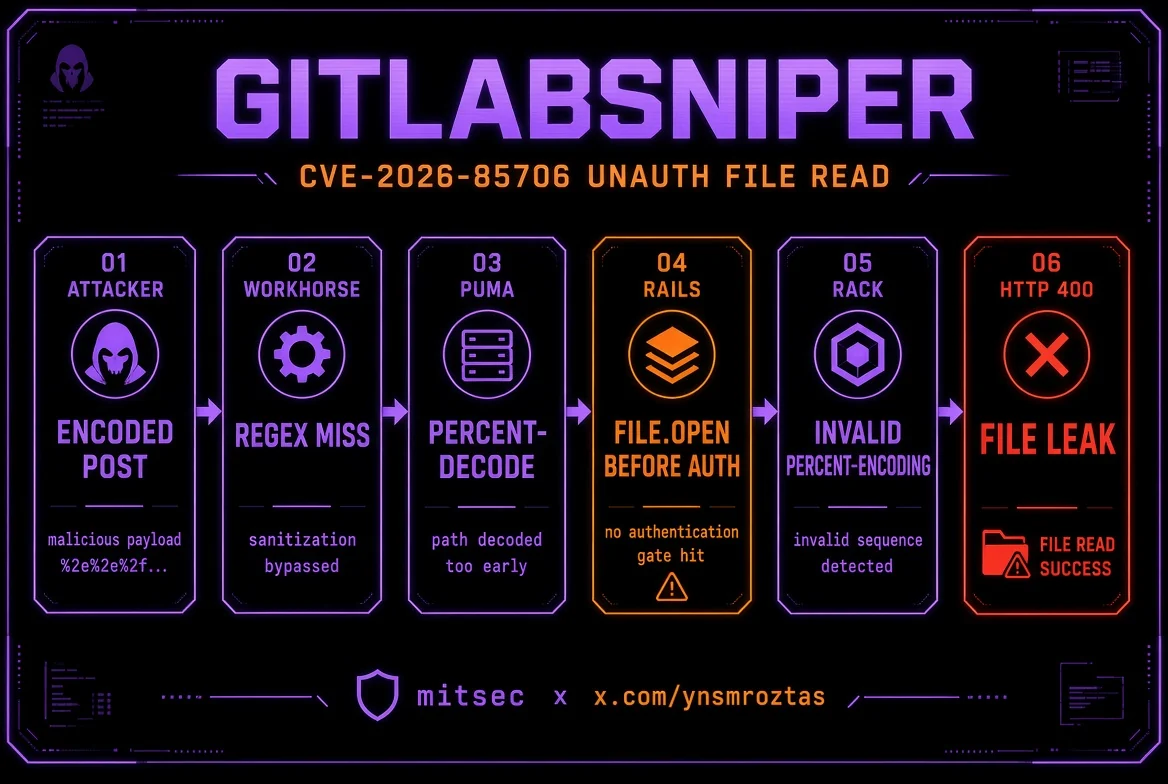 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 squeeze440/code-graph-rag-poc
PoC — symlink following to arbitrary file read/write outside project root in code-graph-rag (GHSA-85gg-2gfq-q95m, CVE-2026-87008, CVSS 7.1).
 horkimhab/cve-2026-13181-cve-2026-13182-cve-2026-13183-cve-2026-13184
Educational proof-of-concept for Telerik padding oracle vulnerabilities (CVE-2026-13181-184) with scripts for authorized security testing and…
 moksh-nfsu/cve-2026-36392
Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…
 horkimhab/cve-chamilo-lms
CVE-2026-61578, CVE-2026-61582, CVE-2026-61583, CVE-2026-61584, CVE-2026-61585, CVE-2026-61587, CVE-2026-61600, CVE-2026-61601, CVE-2026-61602,…
 shihongsu/netsec-cve-2023-4357
Reproduces CVE-2023-4357 in Google Chrome to demonstrate XML/XSLT-based file access bypass, with analysis and proof-of-concept for educational…