Instatic-Stored-XSS-CVE-2026-103931

Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…

Proof-of-concept and analysis of a stored XSS in Instatic's isSafeUrl() URL filter, where leading C0 control characters bypass javascript: scheme…

Zero shot vulnerability discovery using LLMs

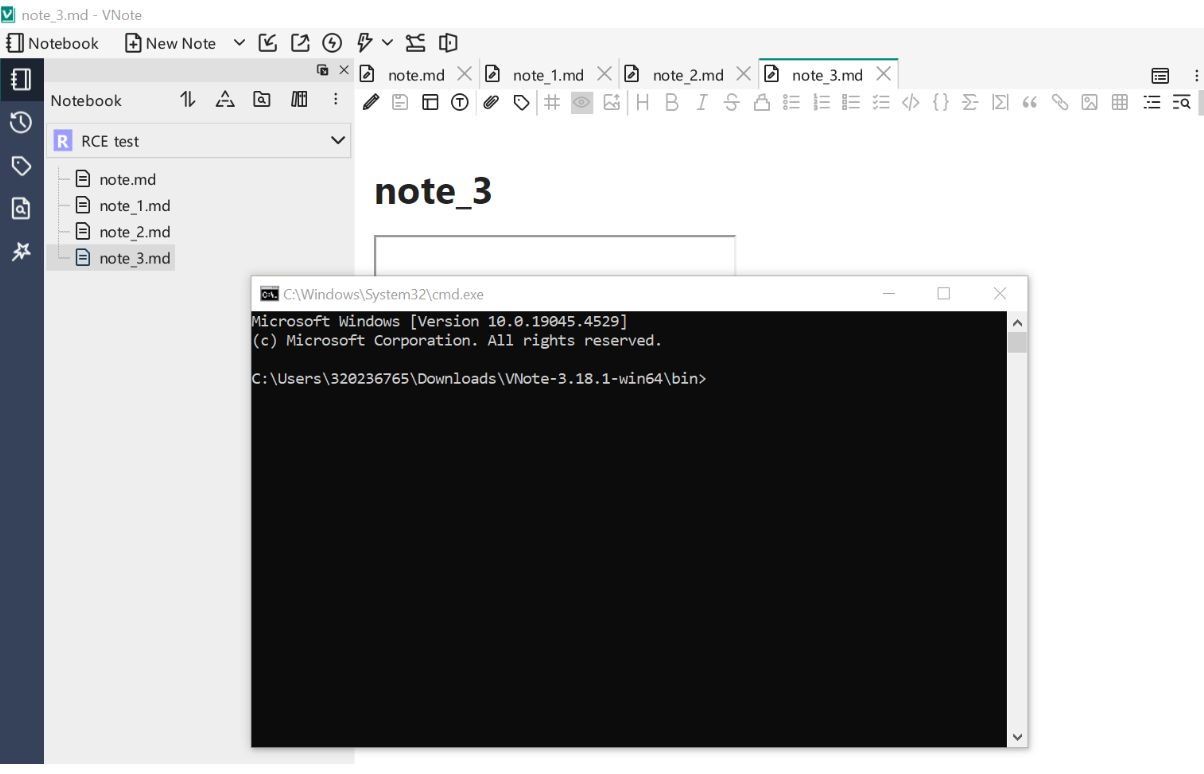
Markdown XSS leads to RCE in VNote version <=3.18.1

Exploit for CVE-2011-4367 targeting Apache MyFaces JSF implementation, demonstrating a remote code execution vulnerability in the Jakarta Faces…

Java XML serialization library with a focus on the CVE-2013-7285 deserialization vulnerability, providing source code, binaries, and documentation…

ReactGuard provides framework- and vulnerability-detection tooling for CVE-2025-55182 (React2Shell)

Apache synapse 反序列化 CVE–2017–15708

Proof-of-concept exploit for CVE-2025-53964: remote file read/write via malicious XDXF dictionary in GoldenDict 1.5.0/1.5.1, leveraging unsanitized…

CVE-2021-46364: YAML Deserialization in Magnolia CMS

Proof-of-concept exploit for CVE-2018-14667, demonstrating Java deserialization combined with EL injection to achieve remote code execution in…


Source code for CVE-2013-2186

Proof-of-concept and technical analysis of CVE-2023-25813, a SQL injection vulnerability in Sequelize ORM versions prior to 6.19.1, including…

Java-based tool to detect Adobe Flex SWF files vulnerable to CVE-2011-2461, usable as a command-line utility or Burp Suite passive scanner plugin.

Proof-of-concept exploit for CVE-2019-5413, a remote code execution vulnerability in Apache NetBeans. Demonstrates exploitation via crafted XML…

Proof-of-concept exploit for CVE-2019-5413 targeting NetBeans IDE, demonstrating remote code execution via crafted project files.

Java library for XML serialization and deserialization, with a focus on CVE-2020-26217 exploitation. Enables converting Java objects to XML and back,…

(CVE-2017-10271)Java反序列化漏洞